

DSE-Patcher
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
binary-exploitationdefensive-toolsexploitation+2
29
gmh5225/dse-patcherWindows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
 wh04m1001/cve-2022-3368
Proof-of-concept for local privilege escalation in Avira Security via arbitrary file move, exploiting junction points to load a malicious DLL into a…
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
 ethanevans92/cve-2025-32463
Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation in sudo. Demonstrates chroot-based NSS manipulation to load a malicious…
 mofarthim/cve-2026-9973-exploit
Proof-of-concept exploit for CVE-2026-9973, a V8 Turboshaft load elimination bug leading to memory corruption, with ongoing sandbox escape research.
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
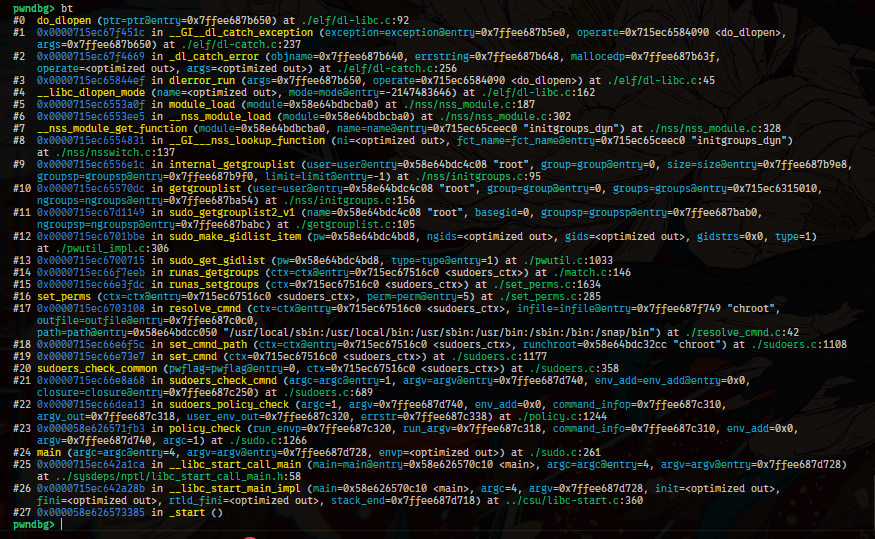 robbert1978/cve-2025-32463_poc
Proof-of-concept exploit for CVE-2025-32463, demonstrating privilege escalation via chroot and nsswitch.conf manipulation to load libnss_systemd.so.2.
 woshimaniubi8/cve-2026-43499-root-kernelsu
基于内核漏洞CVE-2026-43499的本地提权适配,集成嵌入式 KernelSU.CVE-2026-43499+KernelSU越狱模式
 boredpentester/abl_rop
Experimenting with CVE-2022-20120 (Pixel Bootloader / ABL) using Unicorn, derived from eShard's emulator at…
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 eddinos2/cve-2026-78938
Root-cause analysis and working exploit for CVE-2026-78938, a V8 TurboFan type confusion leading to arbitrary read/write within the compressed heap.…
 fusiondrive/cve-2026-43499-a36
Standalone CVE-2026-43499 port for Galaxy A36 5G SM-A366W A366WVLS3AYG1 with KernelSU late-load