
ezwinrar
 ektoplasma/ezwinrar
Python tool exploiting CVE-2018-20250 found by CheckPoint folks
binary-exploitationexploitationpayload-generation+2
2
ektoplasma/ezwinrarPython tool exploiting CVE-2018-20250 found by CheckPoint folks
 shinkirou789/cve-2025-8088-winrar-vulnerability
Python tool that crafts malicious RAR archives to exploit CVE-2025-8088 in WinRAR, enabling path traversal and arbitrary file overwrite via NTFS ADS.…
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 ekomssavior/telnet_scan
scanner/exploiter CVE-2026-24061 & CVE-2026-32746
 anonstorks/cve-2025-0282-full-version
# CVE-2025-0282: Remote Code Execution Vulnerability in [StorkS]
 horizon3ai/cve-2021-44142
Python script to detect and exploit CVE-2021-44142 in Samba servers, dumping heap cookie and pointer via single SMB connection for vulnerability…
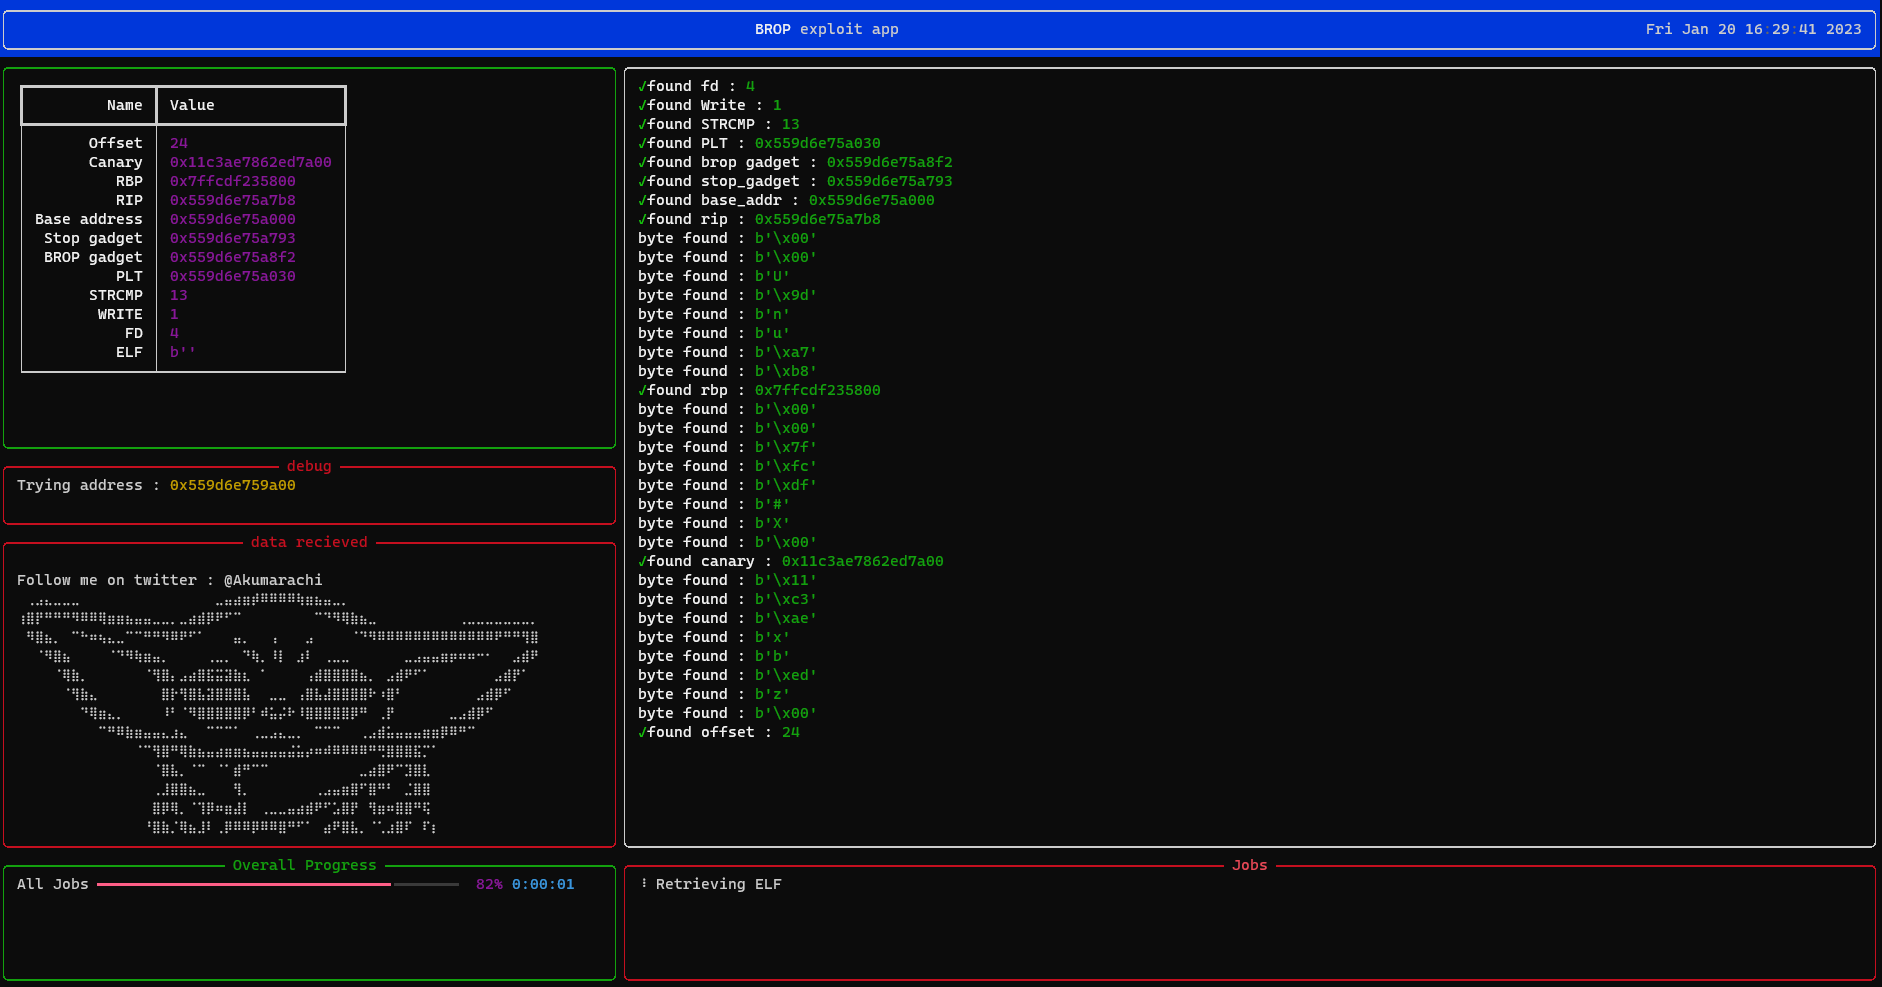 hakumarachi/bropper
An automatic Blind ROP exploitation tool
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 404godd/cve-2026-20841-poc
🛠 Demonstrate remote code execution in Windows Notepad versions below 11.2510 using the CVE-2026-20841 proof of concept.
 kkirsche/cve-2004-2271
Python exploit for Minishare 1.4.1 remote buffer overflow (CVE-2004-2271) with proof-of-concept demonstration.
 toxy4ny/copy-fail
Copy Fail - CVE-2026-31431 - Hardened C implementation for redteam and authorized penetration testing operations. ⚠️ Legal Notice: This tool is…
 cybermads/cve-2011-2523
Python exploit for vsftpd 2.3.4 backdoor vulnerability (CVE-2011-2523) that opens a shell on port 6200 when a smiley is sent in the USER parameter.
 jsantos1990/cve-2025-5548
🚀 Complete analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server 1.0 - NOOP Buffer Overflow) Full methodology: manual tool installation,…
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 tamagaft/cve-2019-17662
Golang implementation of CVE-2019-17662 TinyVNC Arbitrary File Read leading to Authentication Bypass Exploit
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…