
CVE-2025-4517-POC
 azureadtrent/cve-2025-4517-poc
Privilege Escalation script for CVE-2025-4517
binary-exploitationctfeducation+3
97 months ago
azureadtrent/cve-2025-4517-pocPrivilege Escalation script for CVE-2025-4517
 drapl0n/dirtypipe
DirtyPipe: Exploit for a new Linux vulnerability known as 'Dirty Pipe(CVE-2022-0847)' allows local users to gain root privileges. The vulnerability…
 xkaneiki/cve-2022-1011
这个漏洞感觉只能信息泄露?
 aterror2be/cve-2020-14974
A simple POC that demonstrates A vulnerability found in IObitUnlocker 1.1.2 that leverages IOCTL codes found it its vulnerable driver…
 nishanthanand21/cve-2023-4911-poc
Repository containing a Proof of Concept (PoC) demonstrating the impact of CVE-2023-4911, a vulnerability in glibc's ld.so dynamic loader, exposing…
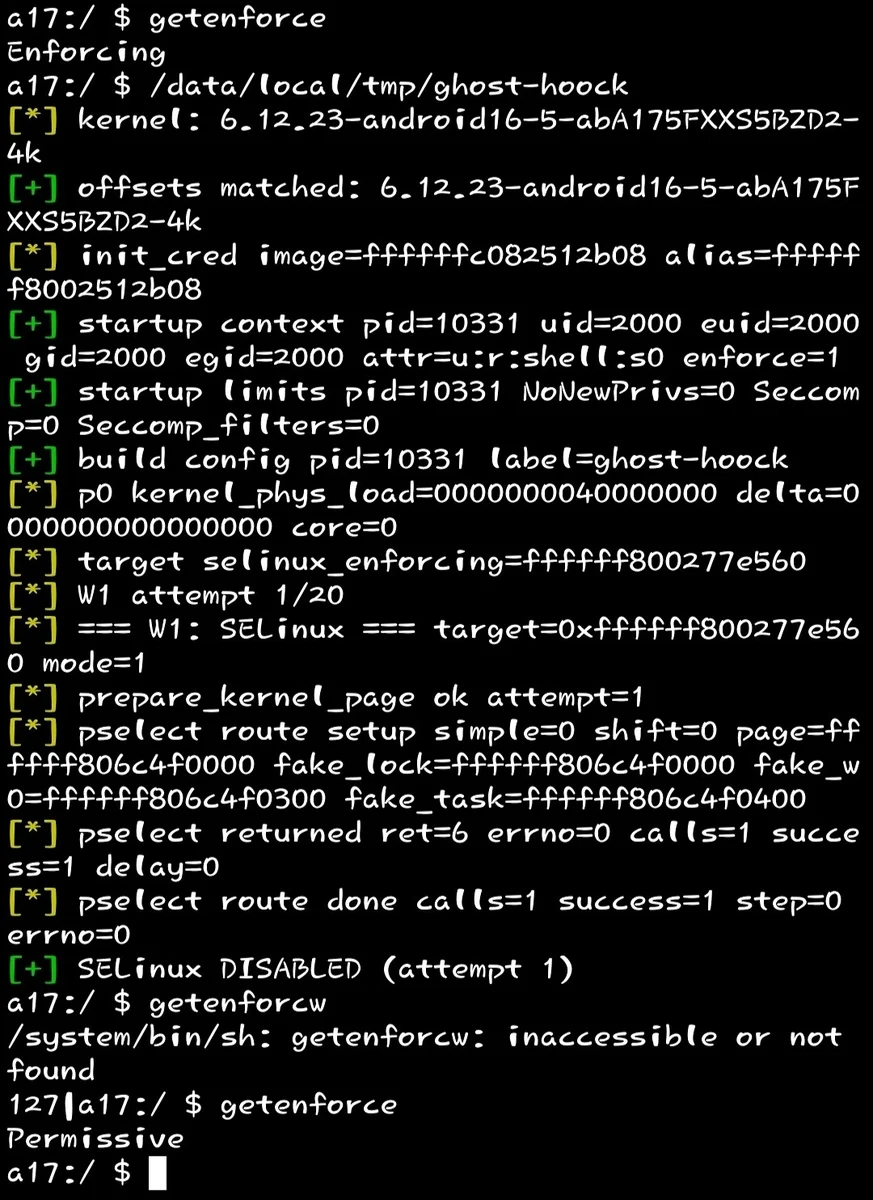 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 jeromeyoung/cve-2021-40154
POC to test the BootROM vulnerability found in LPC55S69 and K82 Series
 satirush/cve-2025-14174-poc
Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…
 davidcarliez/cve-2026-54992-poc
Proof of concept for CVE-2026-54992, an MSMQ remote-read integer overflow
 viai957/webkit-vulnerability
CVE-2016-4657 web-kit vulnerability for ios 9.3, nintendo switch browser vulnerability
 minime794/dirtyfrag
Linux kernel exploit chain (CVE-2026-43284 and CVE-2026-43500) that achieves root via xfrm-ESP and RxRPC page-cache write vulnerabilities.
 bbaranoff/cve-2023-4863
Proof-of-concept exploit for CVE-2023-4863, a heap buffer overflow in libwebp, demonstrating crash trigger and reproduction steps with…
 franklinf25/cve-2026-31431
Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…
 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 k4ntux/cowslip
xfs kernel LPE (CVE-2026-64600), disclosed by Qualys on 22 July 2026
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 crihexe/v8-poc-cve-2026-5865
Minimal JavaScript proof-of-concept for V8 engine vulnerability CVE-2026-5865, with scripts to patch and calibrate the exploit for d8.