
CVE-2016-2434
 jianqiangzhao/cve-2016-2434
Exploit for CVE-2016-2434, a buffer overflow in Android mediaserver enabling arbitrary code execution via crafted media file.
android-securitybinary-exploitationexploitation+2
49
jianqiangzhao/cve-2016-2434Exploit for CVE-2016-2434, a buffer overflow in Android mediaserver enabling arbitrary code execution via crafted media file.
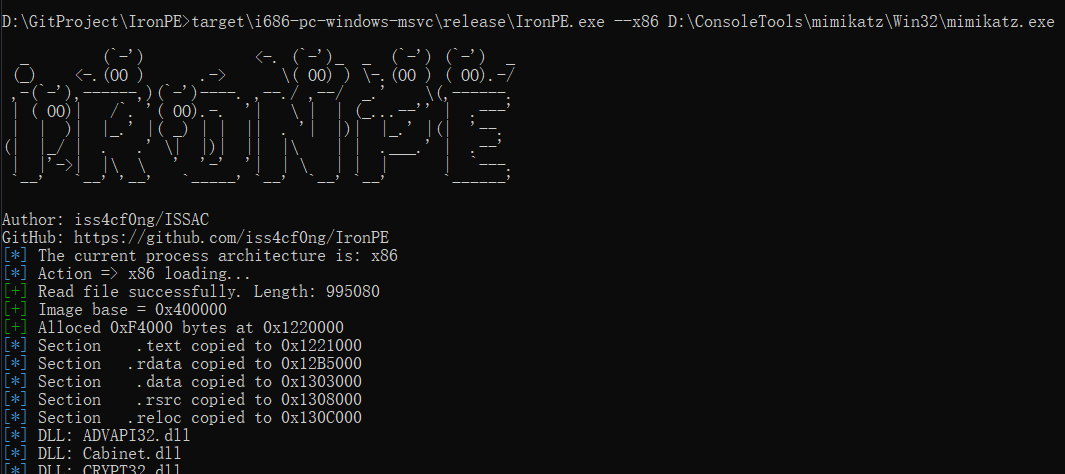 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 geekben/towelroot
Research of CVE-2014-3153 and its famous exploit towelroot on x86
 leommxj/cve-2020-0022
Proof-of-concept exploit for CVE-2020-0022, targeting Android Bluetooth stack to trigger a buffer overflow via crafted L2CAP packets, causing denial…
 cakestwix/android-cve-2026-43499
Android version CVE-2026-43499 tester
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
 thomasking2014/slides
Curated collection of security conference slide decks covering Android rooting, kernel exploitation, browser memory corruption, JIT mitigations, and…
 laginimaineb/cve-2016-2431
Qualcomm TrustZone kernel privilege escalation
 busung-dev/cve-2026-43499-s25u
Standalone CVE-2026-43499 PoC for Galaxy S25 Ultra SM-S938N S938NKSUACZF1
 canyie/transitionplayer
CVE-2026-0091, play with an issue in android window management to perform arbitrary code execution in Launcher process from adb
 colorful-glassblock/duchamp-root
Xiaomi K70e (duchamp) one-click root via CVE-2026-43499 (IonStack) + KernelSU integration
 rasetsuu/vmprotect-research
Generalized VMProtect devirtualizer supporting versions 1.x–3.x. Standalone CLI tool and Ghidra plugin for automated bytecode decoding, handler…
 flankerhqd/cve-2015-6620-poc
POC for CVE-2015-6620, AMessage unmarshal arbitrary write
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 nanoturtle1145/root-my-s24
Using CVE-2026-43499 to root your Galaxy S24 Series(SM-S92X0 ,(China / Hong Kong SAR / Taiwan))
 p2p3p/ghostlock-for-oneplus
(CVE-2026-43499)内核漏洞利用程序,适用于未解锁 Bootloader 的一加设备。
 kasnria001/pwnage24mtk
Cert exploit for MTK devices.There is a logic flaw in MTK cert verification process.Similar to CVE-2023-20696.