
LiveCTF-DEFCON30
 live-ctf/livectf-defcon30
Collection of DEF CON 30 CTF challenge binaries, build scripts, and solve scripts for practicing binary exploitation and reverse engineering.
binary-exploitationctfexploitation+2
114
live-ctf/livectf-defcon30Collection of DEF CON 30 CTF challenge binaries, build scripts, and solve scripts for practicing binary exploitation and reverse engineering.
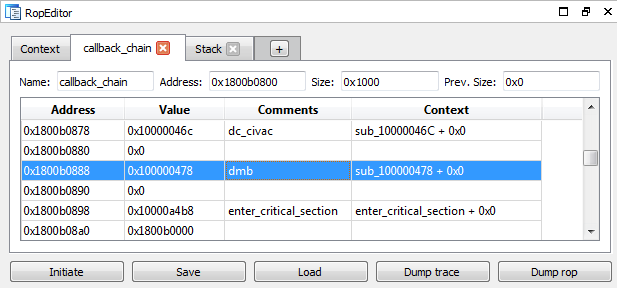 dsecurity/crauemu
crauEmu is an uEmu extension for developing and analyzing payloads for code-reuse attacks
 ze0r/cve-2018-8639-exp
Windows kernel exploit for CVE-2018-8639 targeting Windows 2008 and 2008 R2 systems with privilege escalation capabilities.
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 thetorjancaptain/cve-2025-49144_poc
CVE-2025-49144 PoC for security researchers to test and try.
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 mistymntncop/cve-2023-3079
Proof-of-concept exploit for CVE-2023-3079, a Chrome V8 type confusion vulnerability, with curated writeups and root cause analysis resources.
 0neb1n/cve-2020-16947
Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…
 fortra/cve-2024-30051
Detailed technical analysis and proof-of-concept exploit for CVE-2024-30051, a heap-based buffer overflow in the Windows DWM Core Library enabling…
 cbwang505/cve-2020-1066-exp
Local privilege escalation exploit for CVE-2020-1066 targeting Windows 7 and Server 2008 R2. Leverages arbitrary file replacement via Windows…
 tandasat/cve-2023-36427
Report and exploit of CVE-2023-36427
 bytev0rtex/cve-2026-65343
Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…
 genericcoding/pois0nsword
A demonstration of read write using cve-2025-43529 and userland PAC bypass on iOS 26.1
 y3a/cve-2023-28229
Proof-of-concept exploit for Windows CNG KeyIso RPC elevation of privilege and sandbox escape, demonstrating exploitation of CVE-2023-28229.
 bttea/cve-2026-20841-poc
Proof-of-concept exploit for CVE-2026-20841 demonstrating remote code execution in Windows Notepad before version 11.2510, intended for vulnerability…
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 jhftss/cve-2022-22639
Exploit for CVE-2022-22639, a macOS Monterey root privilege escalation vulnerability, with Objective-C source code and compilation instructions.