

Learning-Linux-Binary-Analysis
 packtpublishing/learning-linux-binary-analysis
Learning Linux Binary Analysis, published by Packt
binary-analysisbinary-exploitationdebuggers+7
89
packtpublishing/learning-linux-binary-analysisLearning Linux Binary Analysis, published by Packt
 4d4j/objdump-out-of-bounds-write
Proof of Concept (PoC) demonstrating the CVE-2026-18220, an out-of-bounds (OOB) write vulnerability in the DLX ELF backend of GNU binutils…
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 brucetg/dirtycow-exp
编译好的脏牛漏洞(CVE-2016-5195)EXP
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 retme7/cve-2014-4322_poc
Gain privileges:system -> root,as a part of https://github.com/retme7/CVE-2014-7911_poc
 quarkslab/cve-2020-0069_poc
Proof-of-concept exploit for CVE-2020-0069 on Mediatek Android devices, enabling kernel memory read/write and syscall hooking for privilege…
 vulnerabilityresearchcentre/patch-diffing-in-the-dark
Leveraging patch diffing to discover new vulnerabilities
 j4nn/cve-2020-0041
Local privilege escalation exploit for Android kernel vulnerability CVE-2020-0041, with portability across devices and kernel versions.
 pwnipc/badparcel
CVE-2023-20963 PoC (Android WorkSource parcel/unparcel logic mismatch)
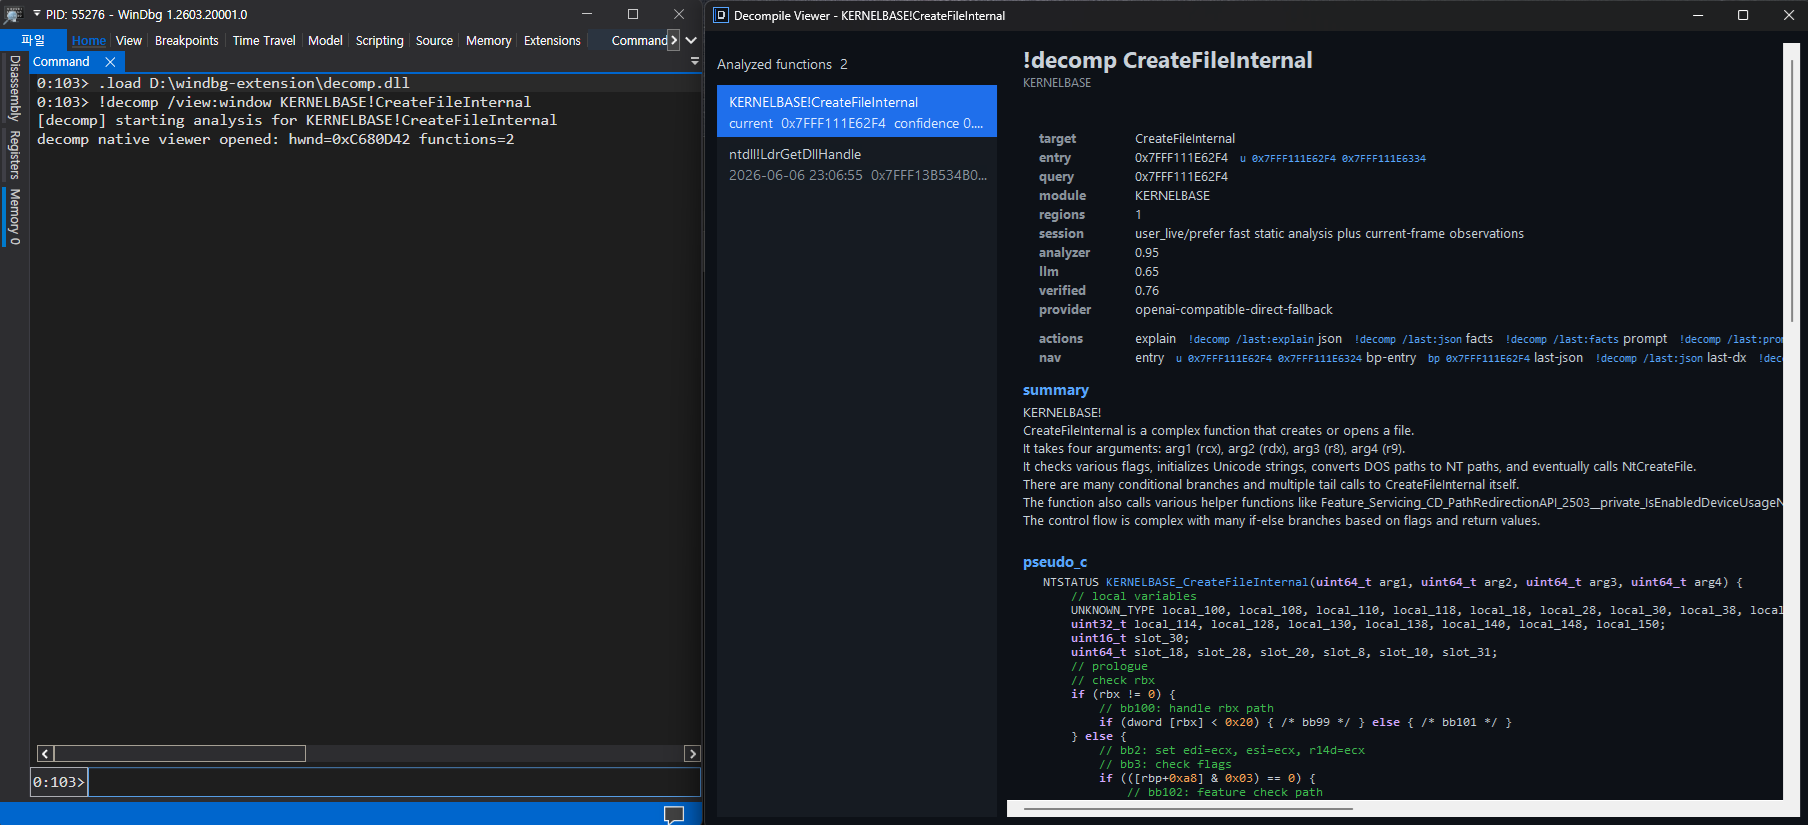 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 timwr/cve-2019-2215
Android kernel privilege escalation exploit for CVE-2019-2215, providing a proof-of-concept to achieve root access via a use-after-free vulnerability…
 android-rooting-tools/libpingpong_exploit
CVE-2015-3636 exploit
 laginimaineb/cve-2014-7920-7921
Exploit code for CVE-2014-7920 and CVE-2014-7921 - code-exec in mediaserver up to Android 5.1
 villager1314/cve-2026-64560-analysis
Linux kernel UAF analysis for CVE-2026-64560 with race-triggering PoC, patch review, affected LTS/Android version matrix, and self-check for patched…
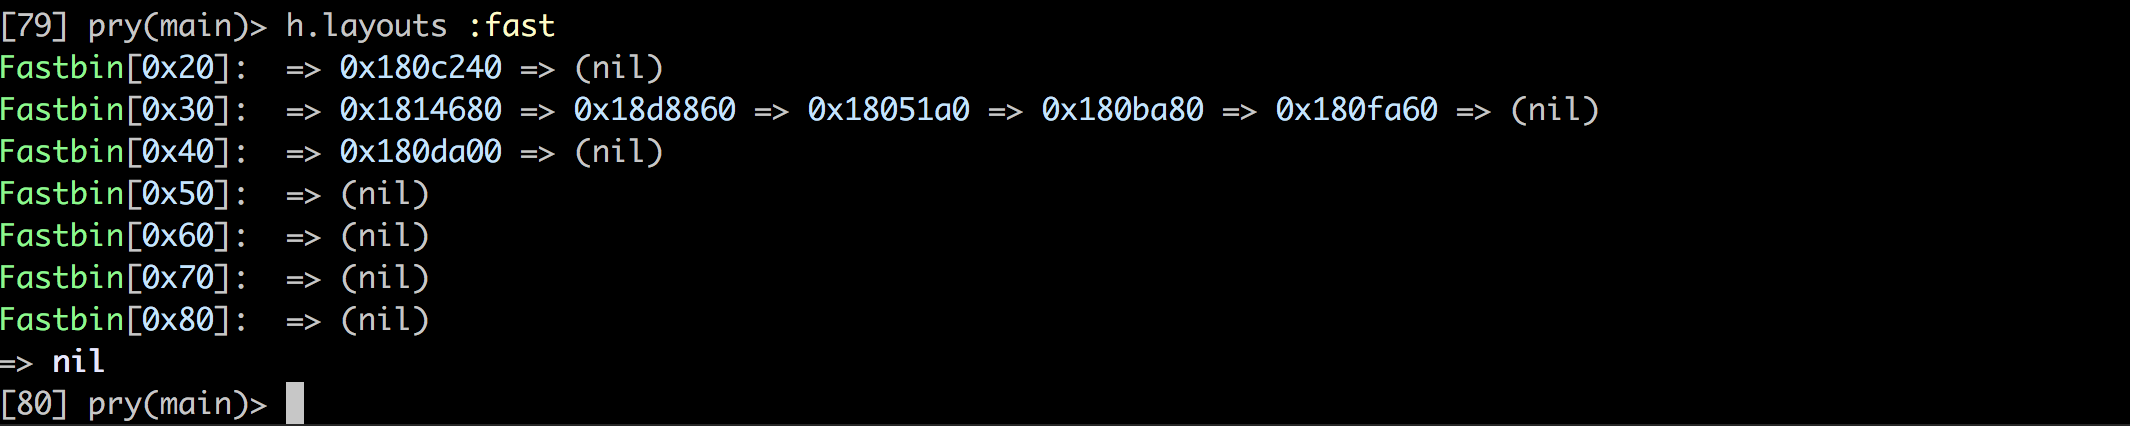 david942j/heapinfo
An interactive memory info for pwning / exploiting
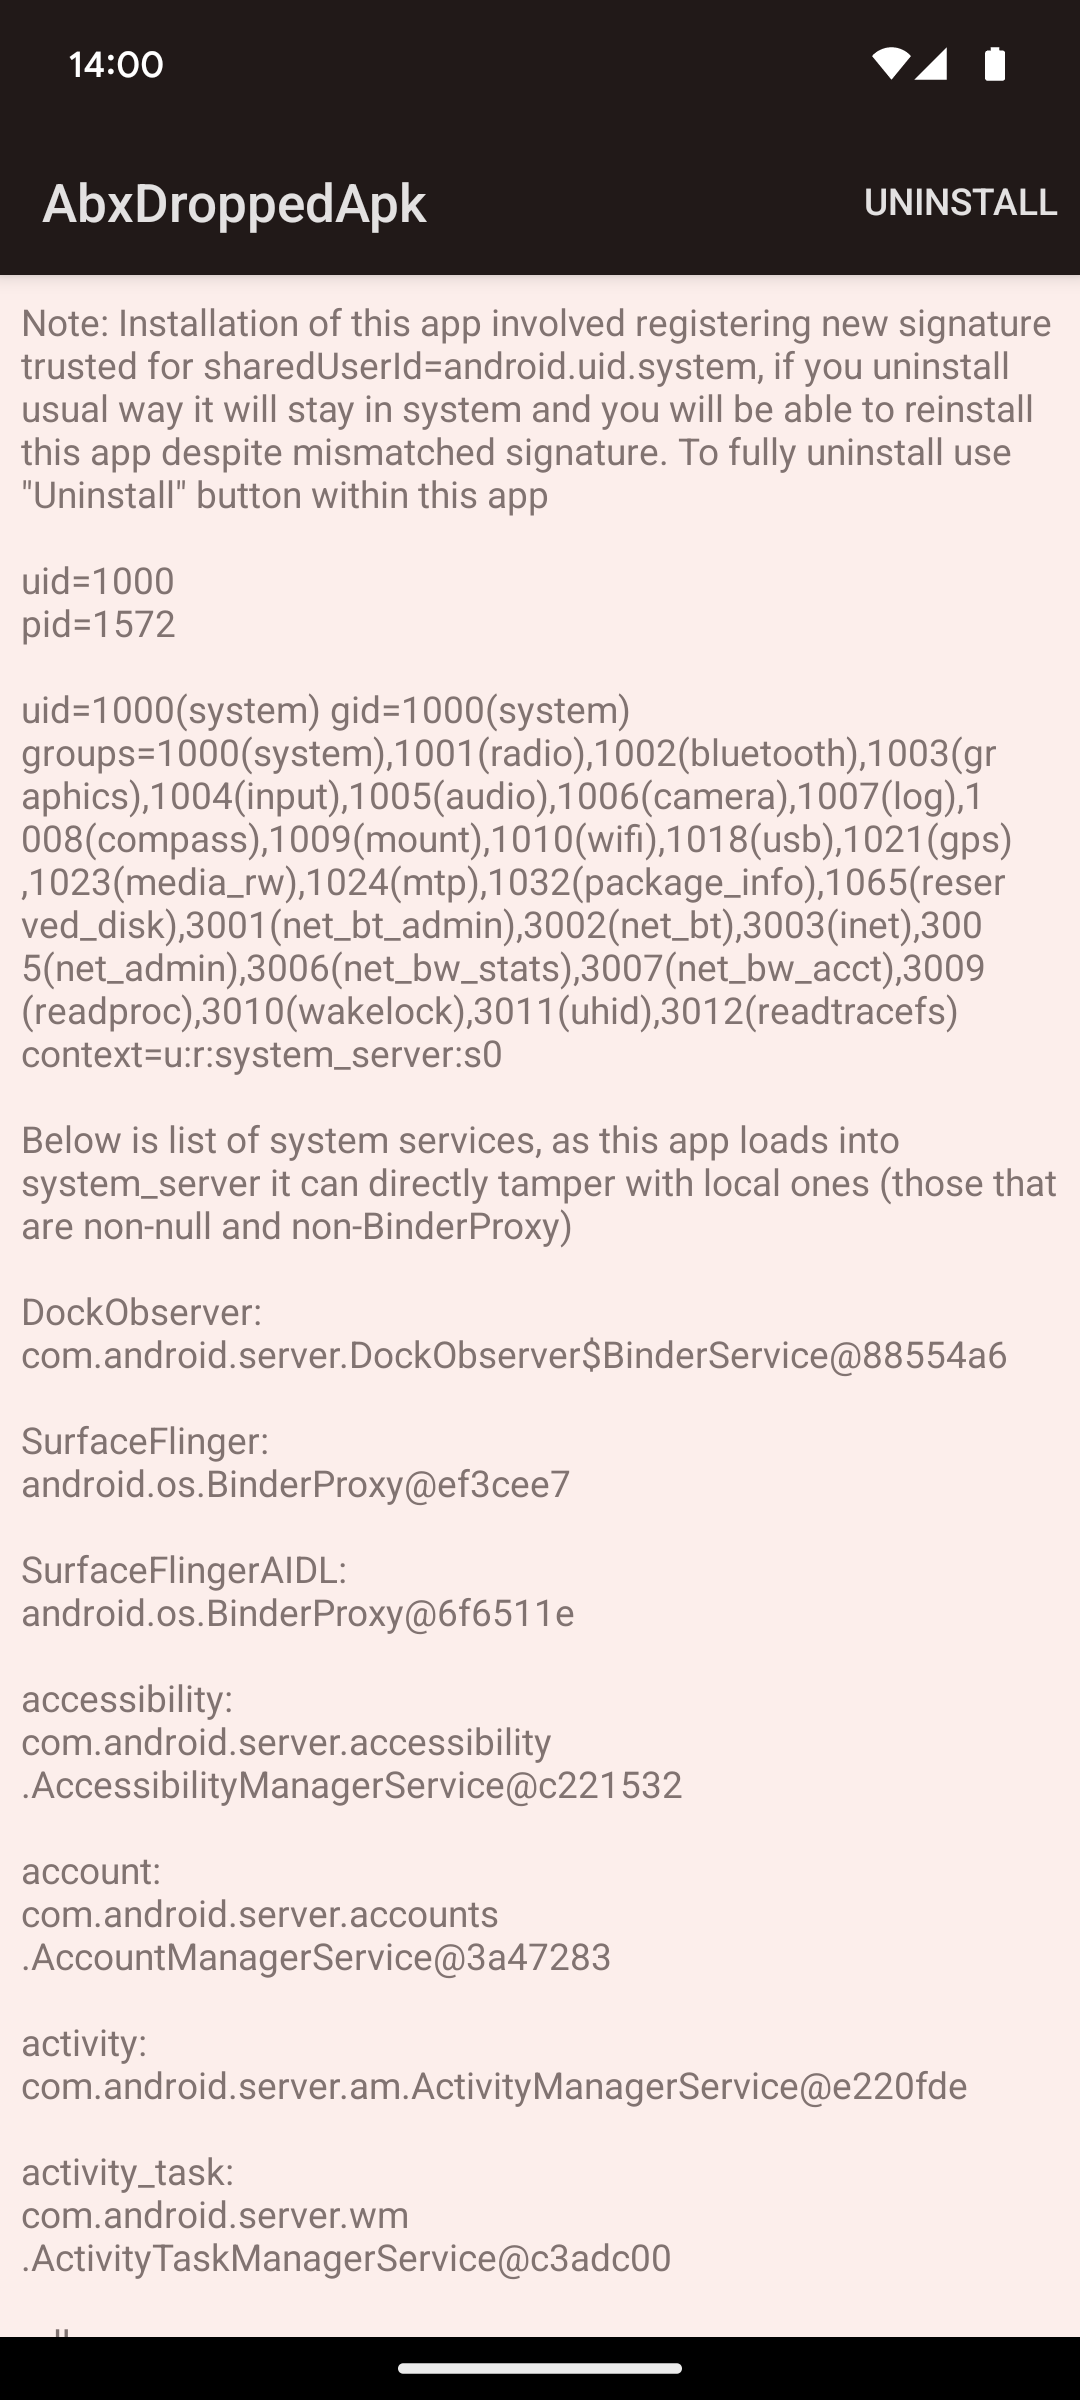 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…