
dnSpy
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.1k
dnspyex/dnspyUnofficial revival of the well known .NET debugger and assembly editor, dnSpy
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 jonathansalwan/ropgadget
Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 timwr/cve-2016-5195
CVE-2016-5195 (dirtycow/dirtyc0w) proof of concept for Android
 danigargu/heap-viewer
IDA Pro plugin to examine the glibc heap, focused on exploit development
 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader
 hasherezade/exe_to_dll
Converts a EXE into DLL
 laginimaineb/extractkeymaster
Exploit that extracts Qualcomm's KeyMaster keys using CVE-2015-6639 and CVE-2016-2431
 northbit/metaphor
Metaphor - Stagefright with ASLR bypass

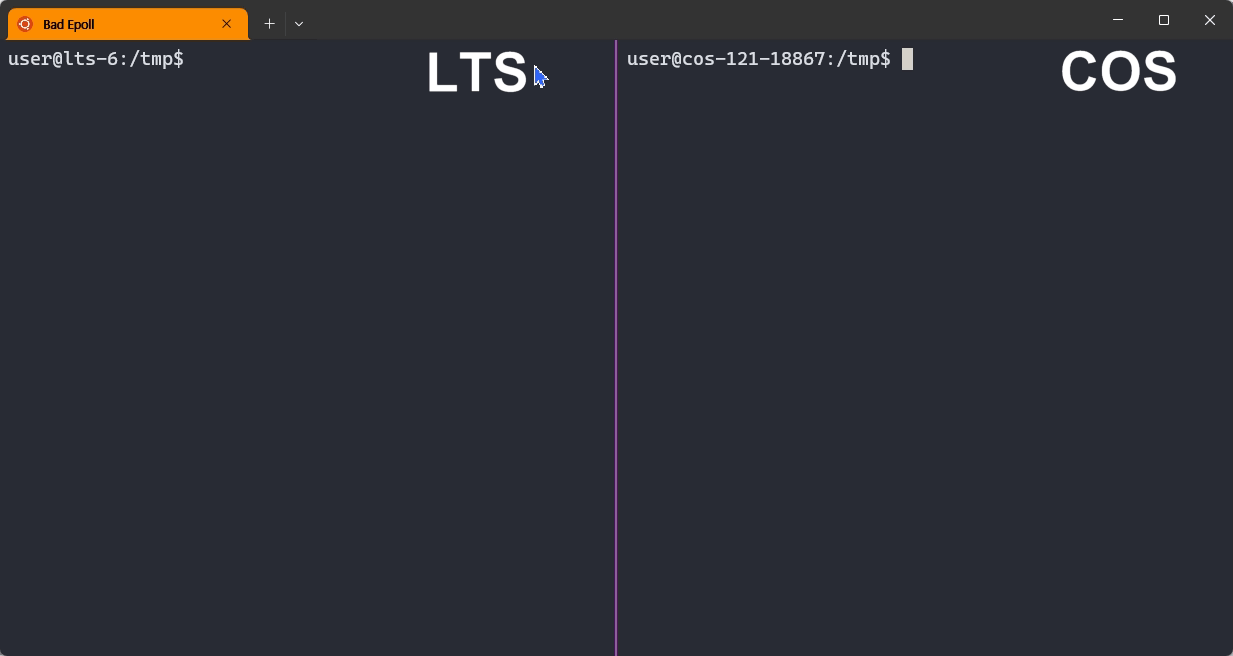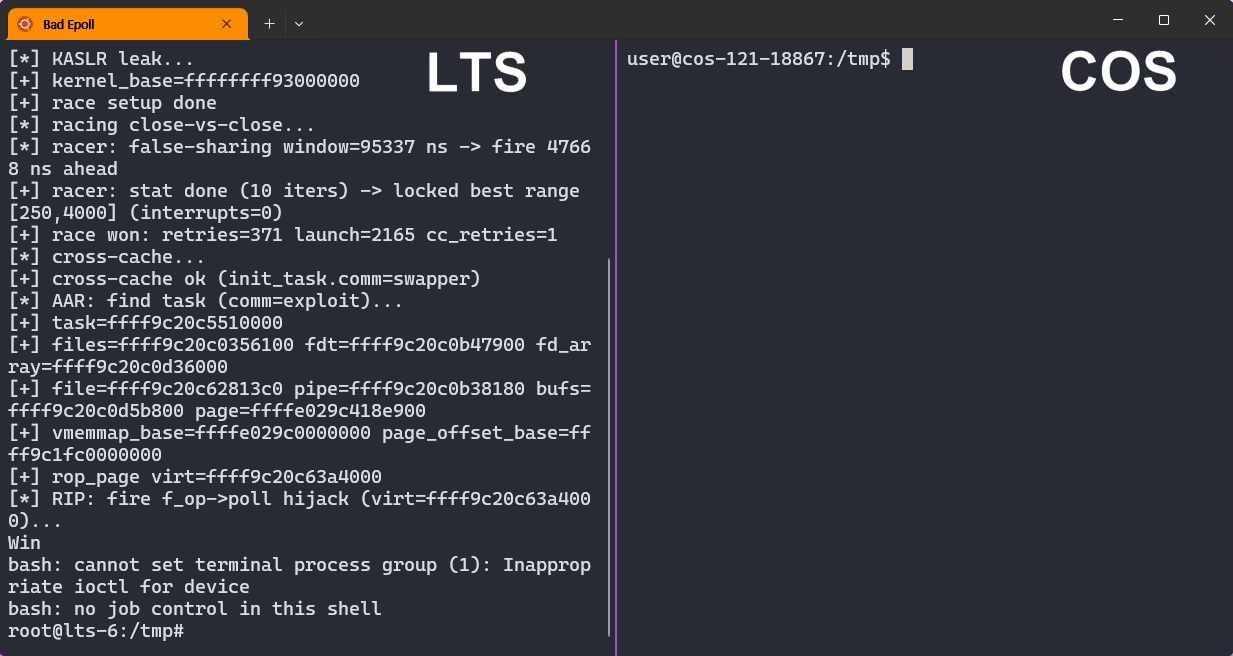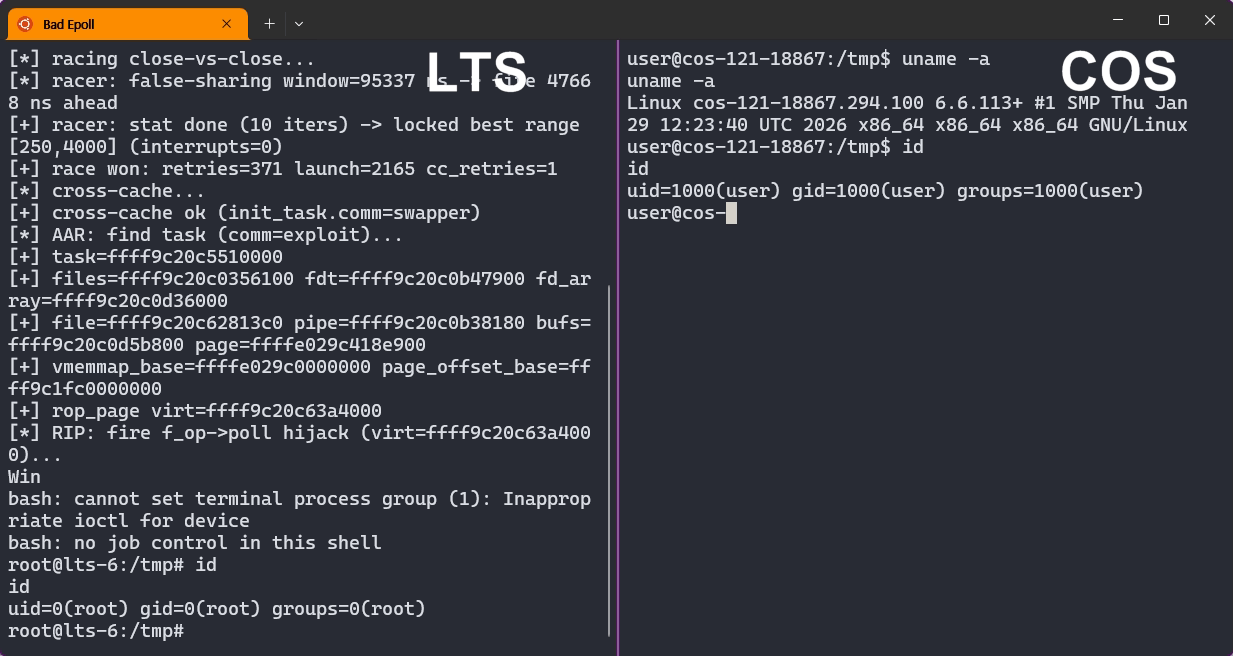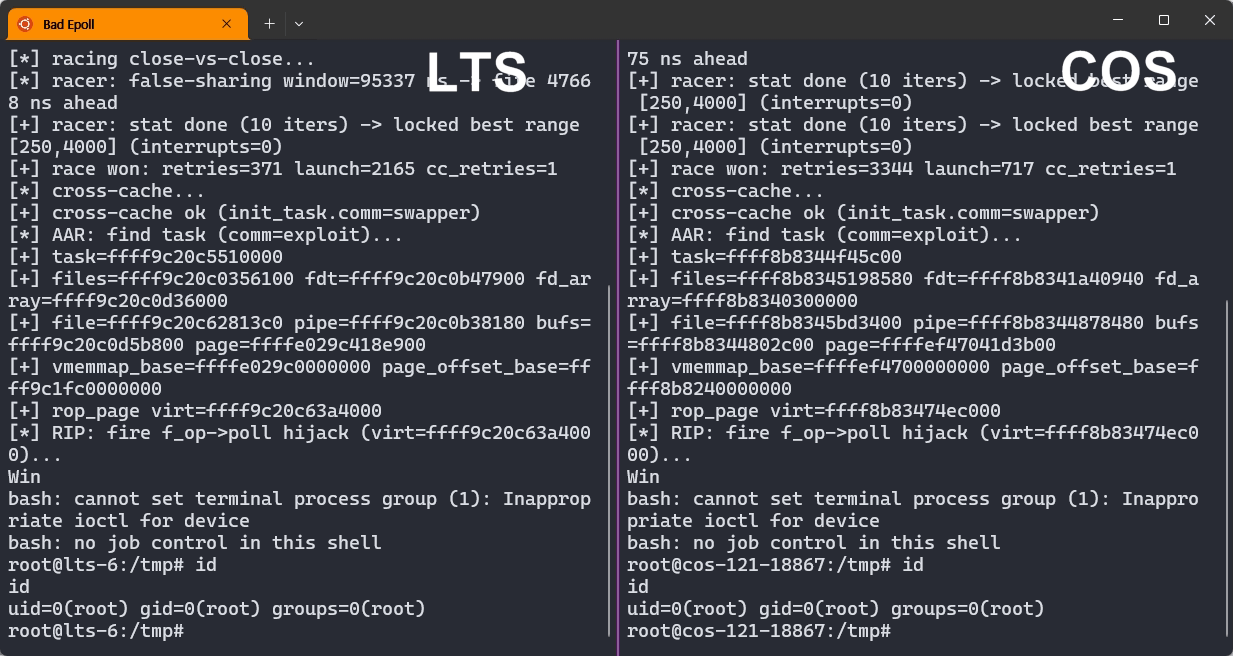 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 t00sh/rop-tool
A tool to help you write binary exploits
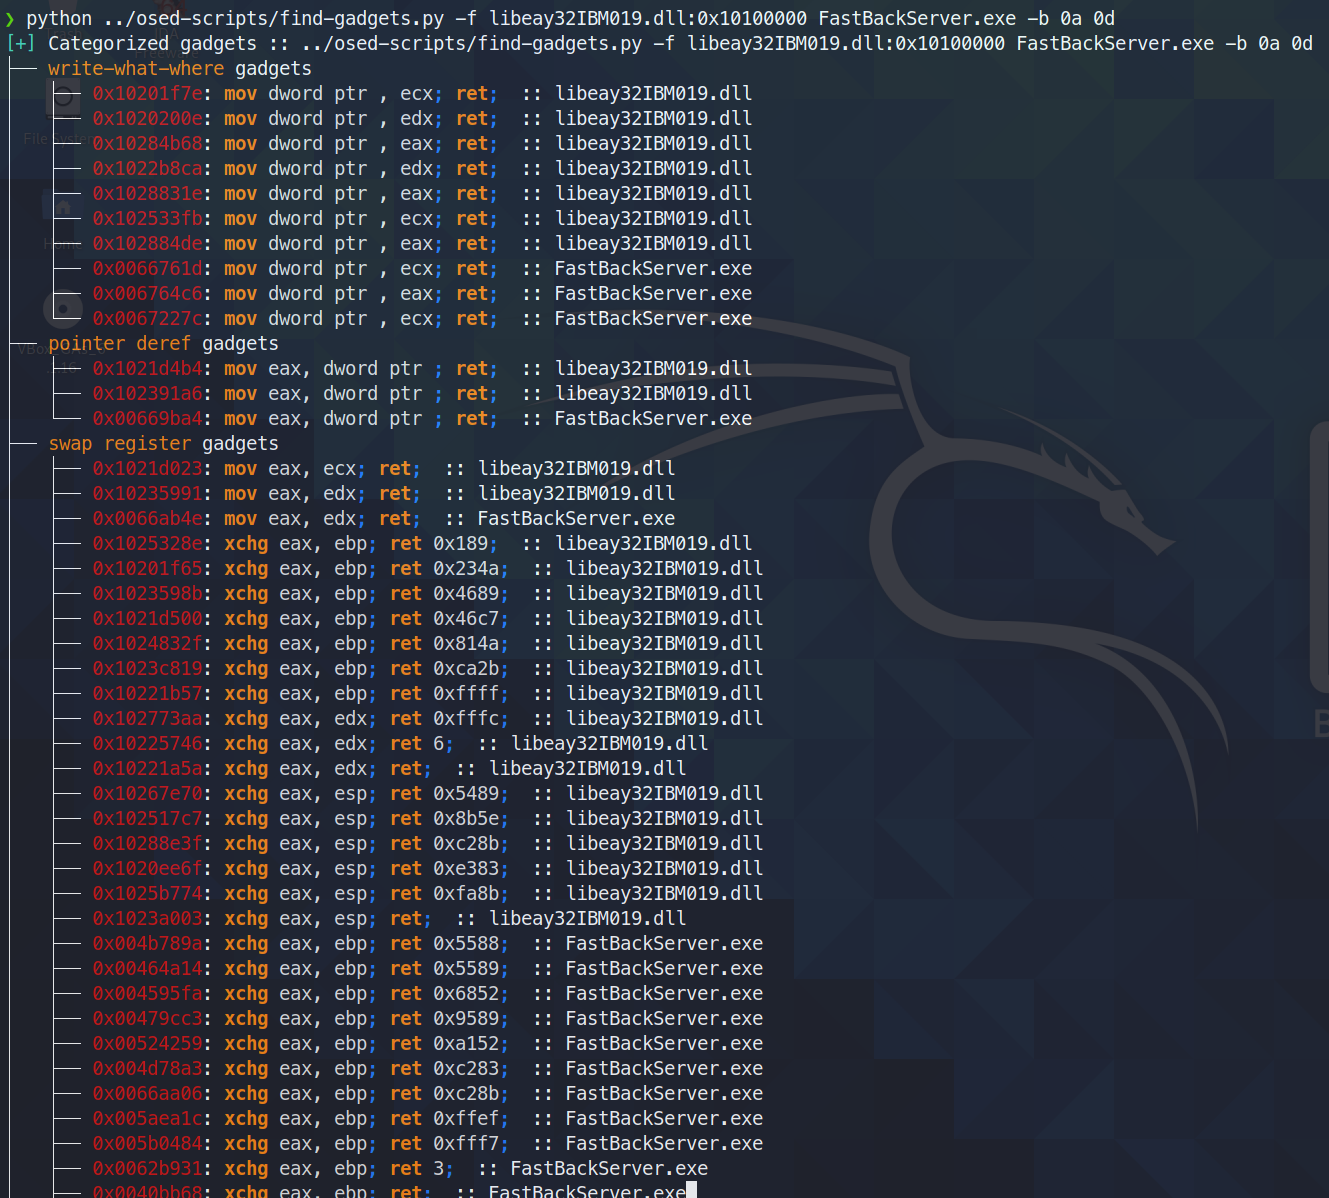 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 externalist/exploit_playground
Analysis of public exploits or my 1day exploits