
cve-2026-64560-a16
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
android-securitybinary-exploitationexploitation+8
1
become-illusory/cve-2026-64560-a16CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 walidpyh/cve-2025-8088
Proof-of-concept demonstrating Alternate Data Stream (ADS) payload delivery via crafted WinRAR archives for educational research and controlled lab…
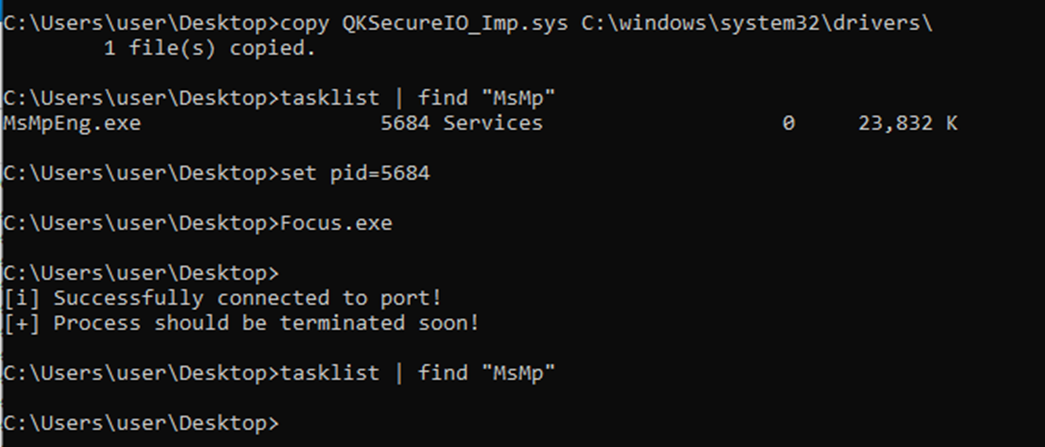 cwjchoi01/cve-2026-3796
Proof-of-concept exploit for CVE-2026-3796, demonstrating arbitrary process termination via a vulnerable QAX driver. Includes usage instructions and…
 razureink/cve-2025-0282-ivanti_rce_reproduction
Reproduction of cve-2025-0282-ivanti_rce_reproduction
 razureink/cve-2025-2783-chrome_sandbox_escape_reproduction
CVE Reproduction: cve-2025-2783-chrome_sandbox_escape_reproduction
 razureink/cve-2026-21509-office_security_bypass_reproduction
CVE Reproduction: cve-2026-21509-office_security_bypass_reproduction

 dnlid/cve-2026-43499
CVE-2026-43499: Linux kernel futex PI use-after-free research package
 gmh5225/cheat-engine-undetectable
Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).
 sudoand3rs0n/cve-2025-5548
Educational repository documenting the analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server buffer overflow). Includes a reusable…
 lucabarile/cve-2022-38604
Exploits and reports for CVE-2022-38604
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 chrxstxqn/cve-2025-6218-winrar-rce-poc
Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier
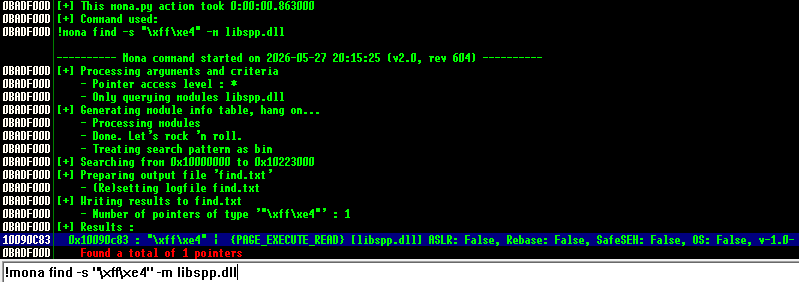 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 tna0y/cve-2018-1000802-poc
Python CVE-2018-1000802 Proof-of-Concept
 admin9961/cve-2024-30088
Questa repository contiene una replica (tentativo di replica) scritto in Python per CVE-2024-30088.
 apexpredator-infosec/forti_shield
A combined POC for CVE-2021-31955, CVE-2015-4077, and CVE-2015-5736
 h3raklez/cve-2025-14321
Proof-of-concept demonstrating a Use-After-Free vulnerability in Firefox's RTCEncodedFrameBase via WebRTC Encoded Transforms, enabling heap…