
DrayTek-Exploit
 symbolexe/draytek-exploit
CVE-2022-23093 FreeBSD Stack-Based Overflow
binary-exploitationexploitationpayload-development+3
symbolexe/draytek-exploitCVE-2022-23093 FreeBSD Stack-Based Overflow
 colaoo123/cve-2022-22555
Exploit for CVE-2022-22555, a Linux kernel heap buffer overflow vulnerability enabling local privilege escalation. Includes proof-of-concept code and…
 natleoj/cve-2019-11933
Heap corruption in WhatsApp's media picker
 day6reak/cve-2014-4140
Technical notes and debugger analysis for CVE-2014-4140, a use-after-free vulnerability in MSHTML's CHtmRootParseCtx::AddText leading to remote code…
 beraphin/cve-2017-16943
Technical analysis and proof-of-concept for CVE-2017-16943, a use-after-free in Exim's receive_msg function, demonstrating heap manipulation and RIP…
 redhatkaty/-cve-2010-3904-report
Exploit for CVE-2010-3904, a Linux kernel privilege escalation vulnerability. Provides a proof-of-concept implementation for local privilege…
 bl4ck5un/cve-2013-2072
Buffer overflow in the Python bindings for the xc_vcpu_setaffinity call in Xen
 nipund513/exploiting-uaf-by-ret2bpf-in-android-kernel-cve-2021-0399-
 tagatac/linux-cve-2006-4814
A deadlock on the mmap semaphore ‘mmap sem’ in the CentOS 3.9 kernel, that is triggered by a specific interleaving of concurrent threads, one calling…
 tuankiethkt020/phat-hien-cve-2017-8464
 soteria-research/cve-2015-4843-type-confusion-phrack
Demonstrates type confusion and heap overflow exploits for CVE-2015-4843 in Java, with demos for aarch64 and Morello, highlighting CHERI capability…
 0vercl0k/cve-2022-21971
PoC for CVE-2022-21971 "Windows Runtime Remote Code Execution Vulnerability"
 itm4n/ppldump
Dump the memory of a PPL with a userland exploit
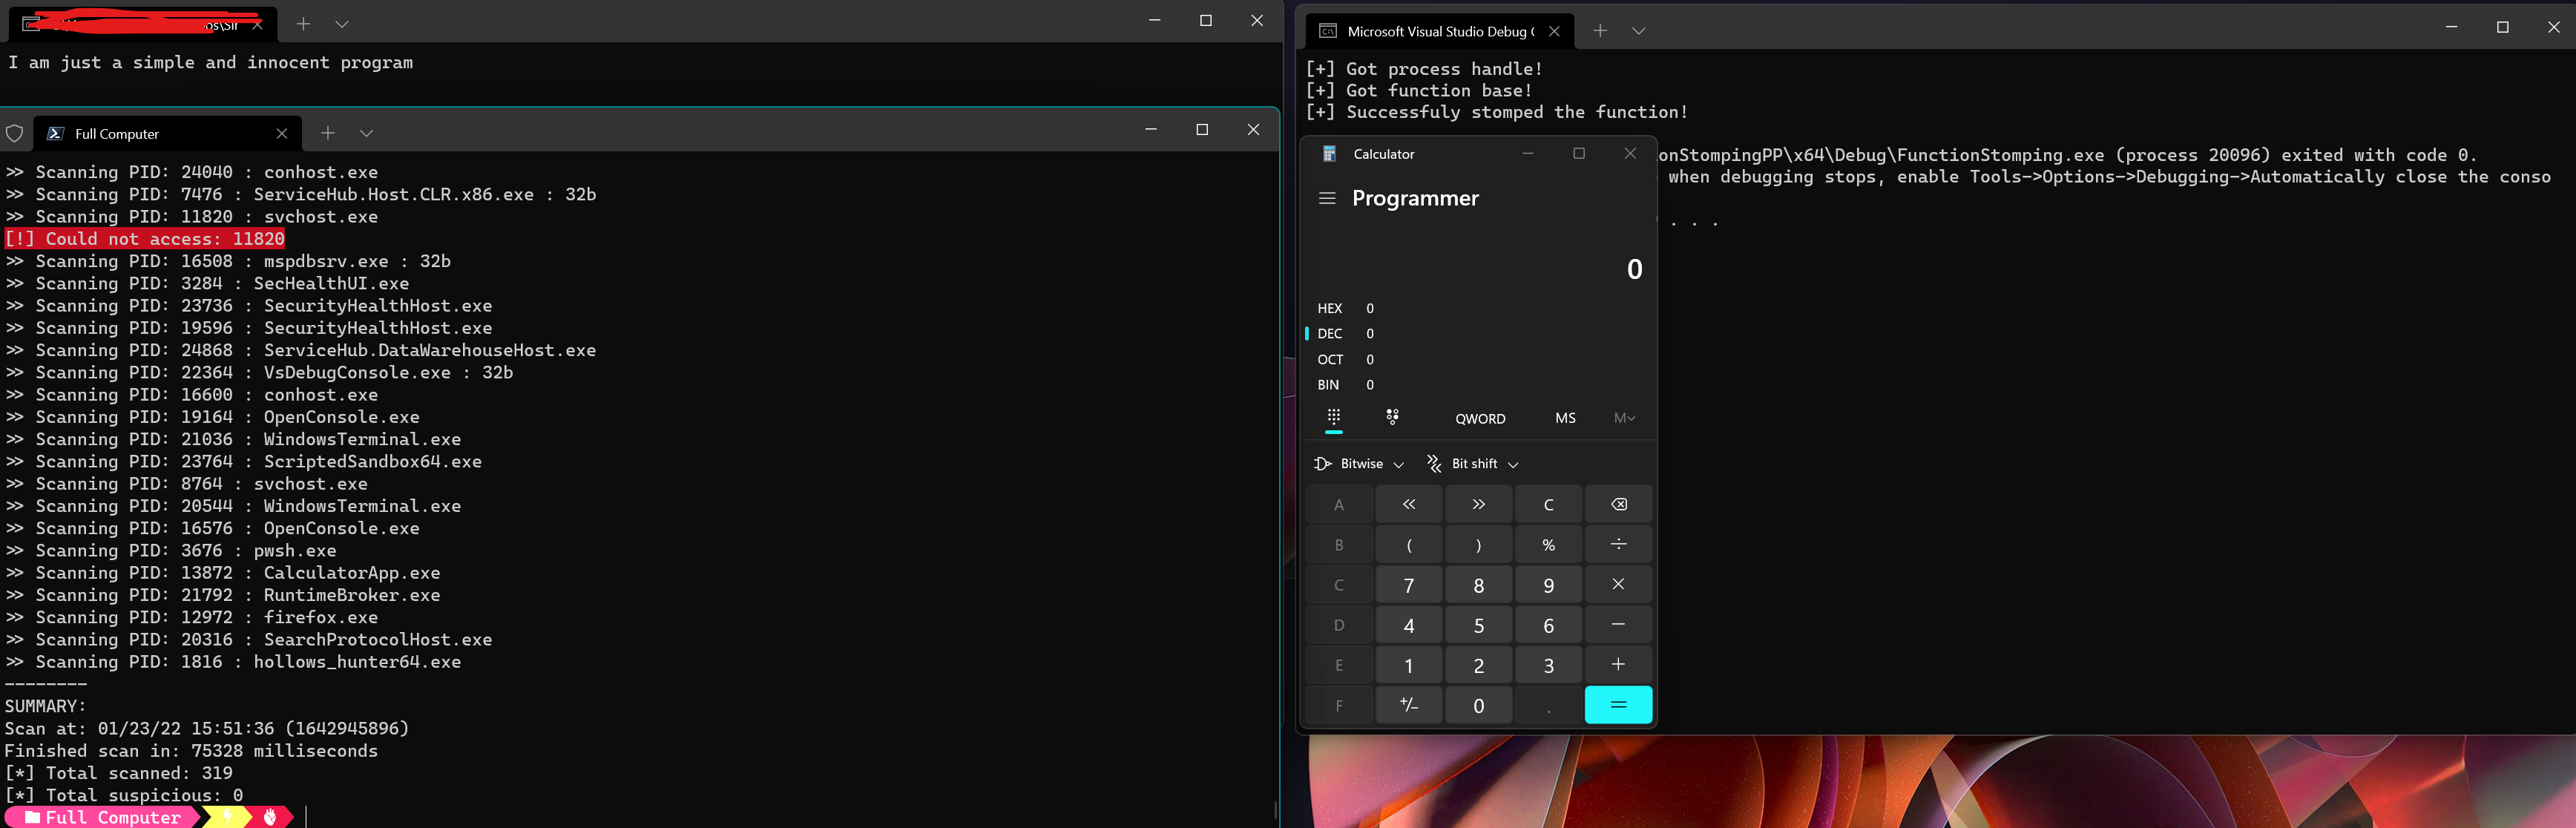 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
 isec-tugraz/meltdown
Proof-of-concept demos and libkdump library demonstrating the Meltdown microarchitectural attack, leaking kernel and physical memory on vulnerable…
 y198nt/nginx-chain-rift-poolslip
ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…
 0vercl0k/cve-2021-32537
PoC for CVE-2021-32537: an out-of-bounds memory access that leads to pool corruption in the Windows kernel.