
CVE-2026-54107
 pravin761/cve-2026-54107
Root-cause analysis of CVE-2026-54107: a use-after-free in Windows win32kfull.sys with race condition debugging, static analysis, MSRC triage…
binary-exploitationdebuggerseducation+5
1
pravin761/cve-2026-54107Root-cause analysis of CVE-2026-54107: a use-after-free in Windows win32kfull.sys with race condition debugging, static analysis, MSRC triage…
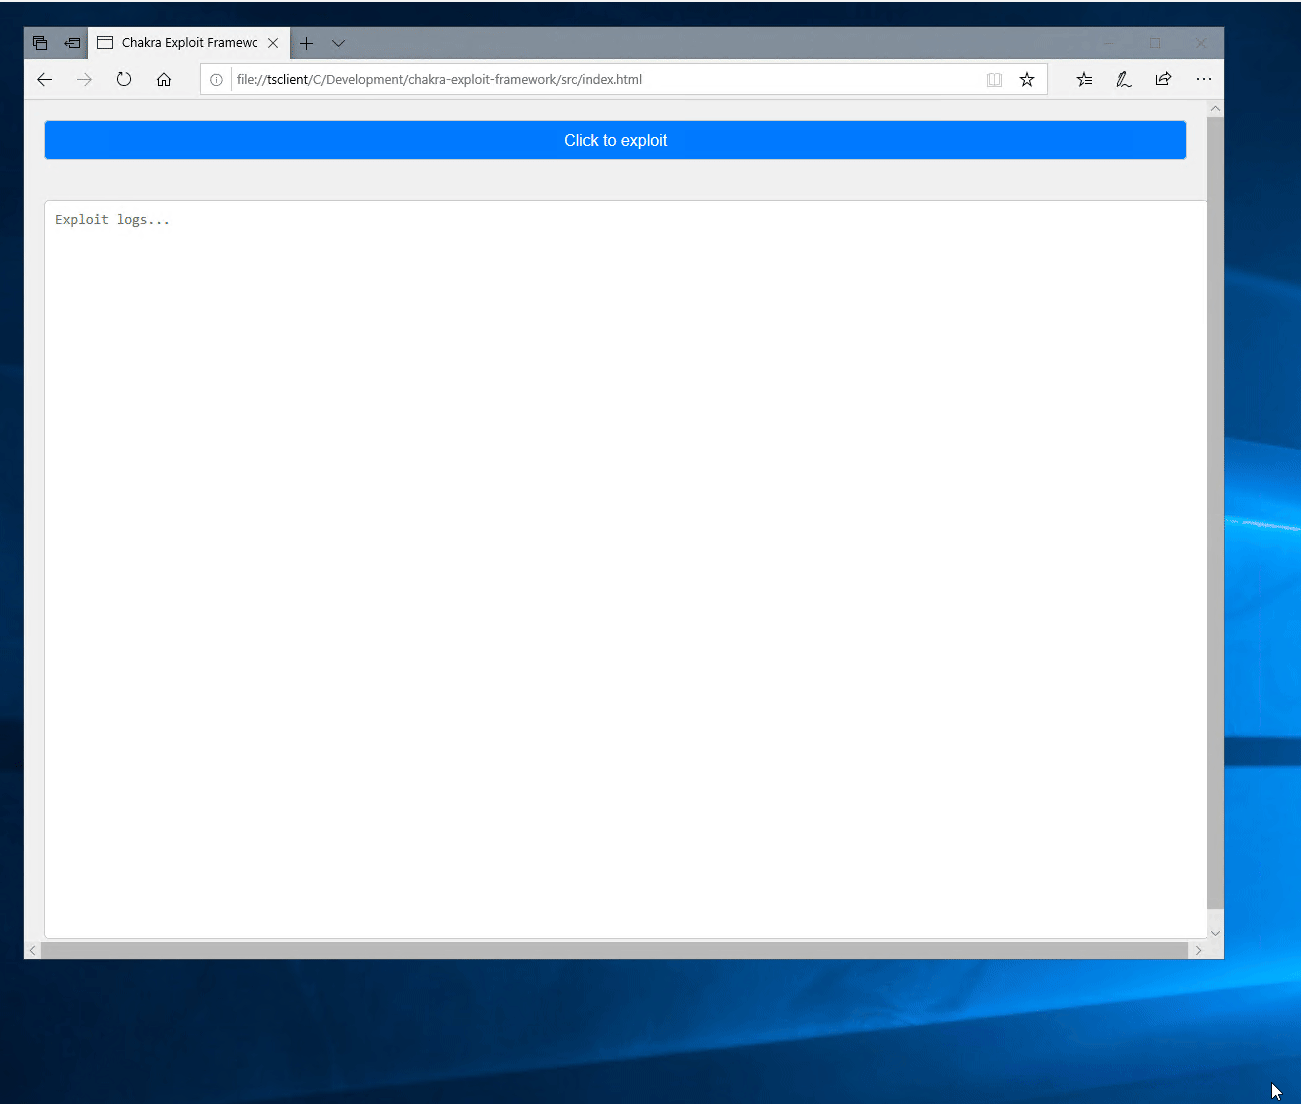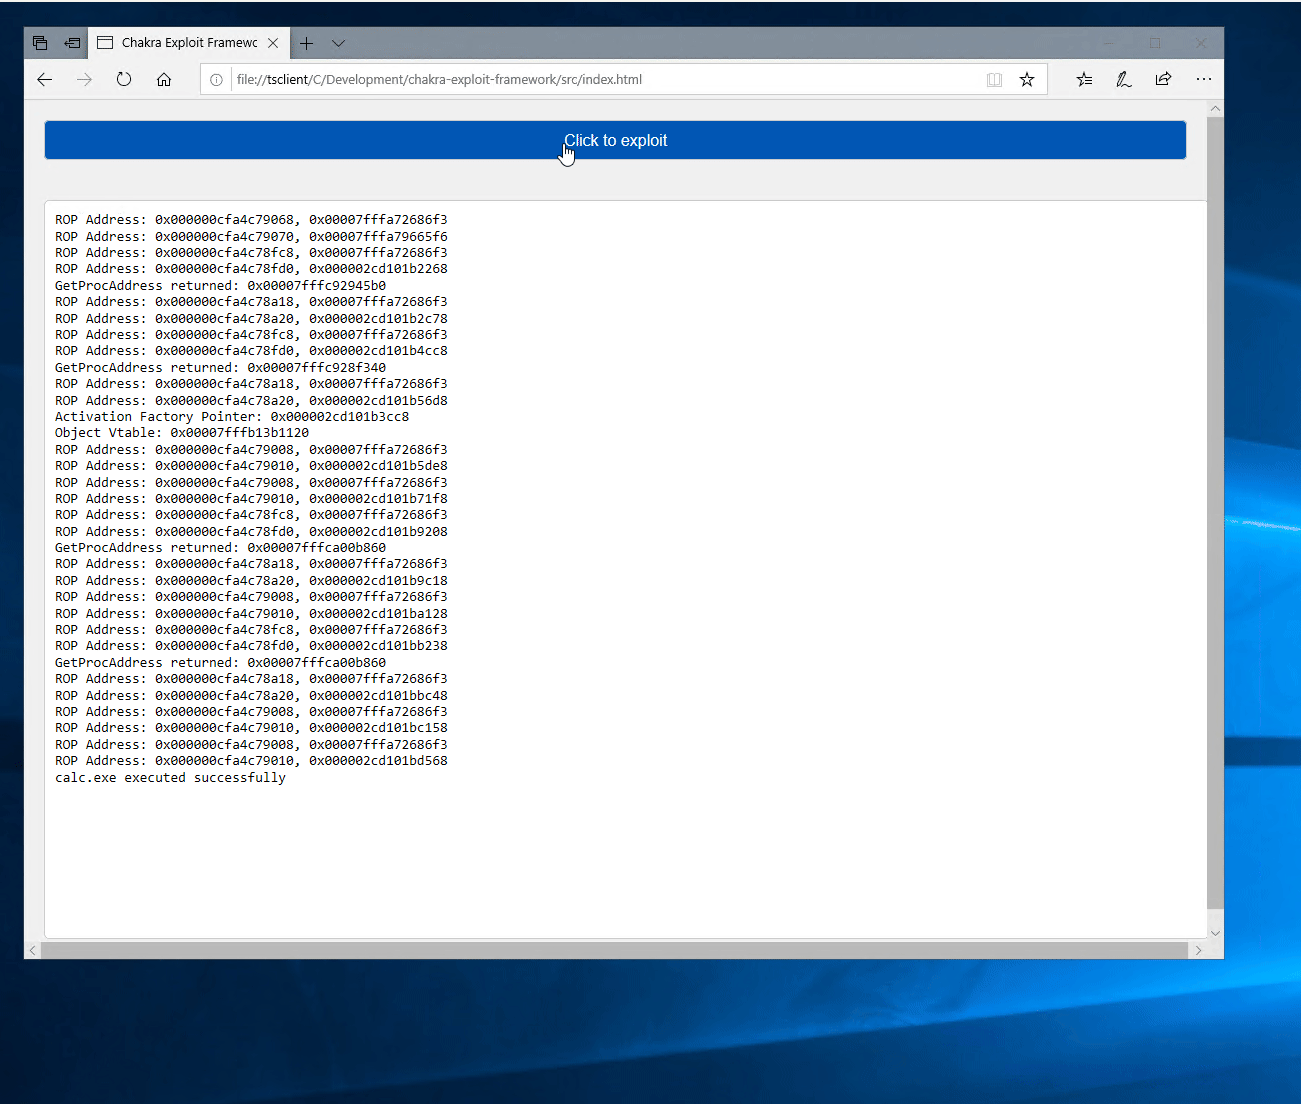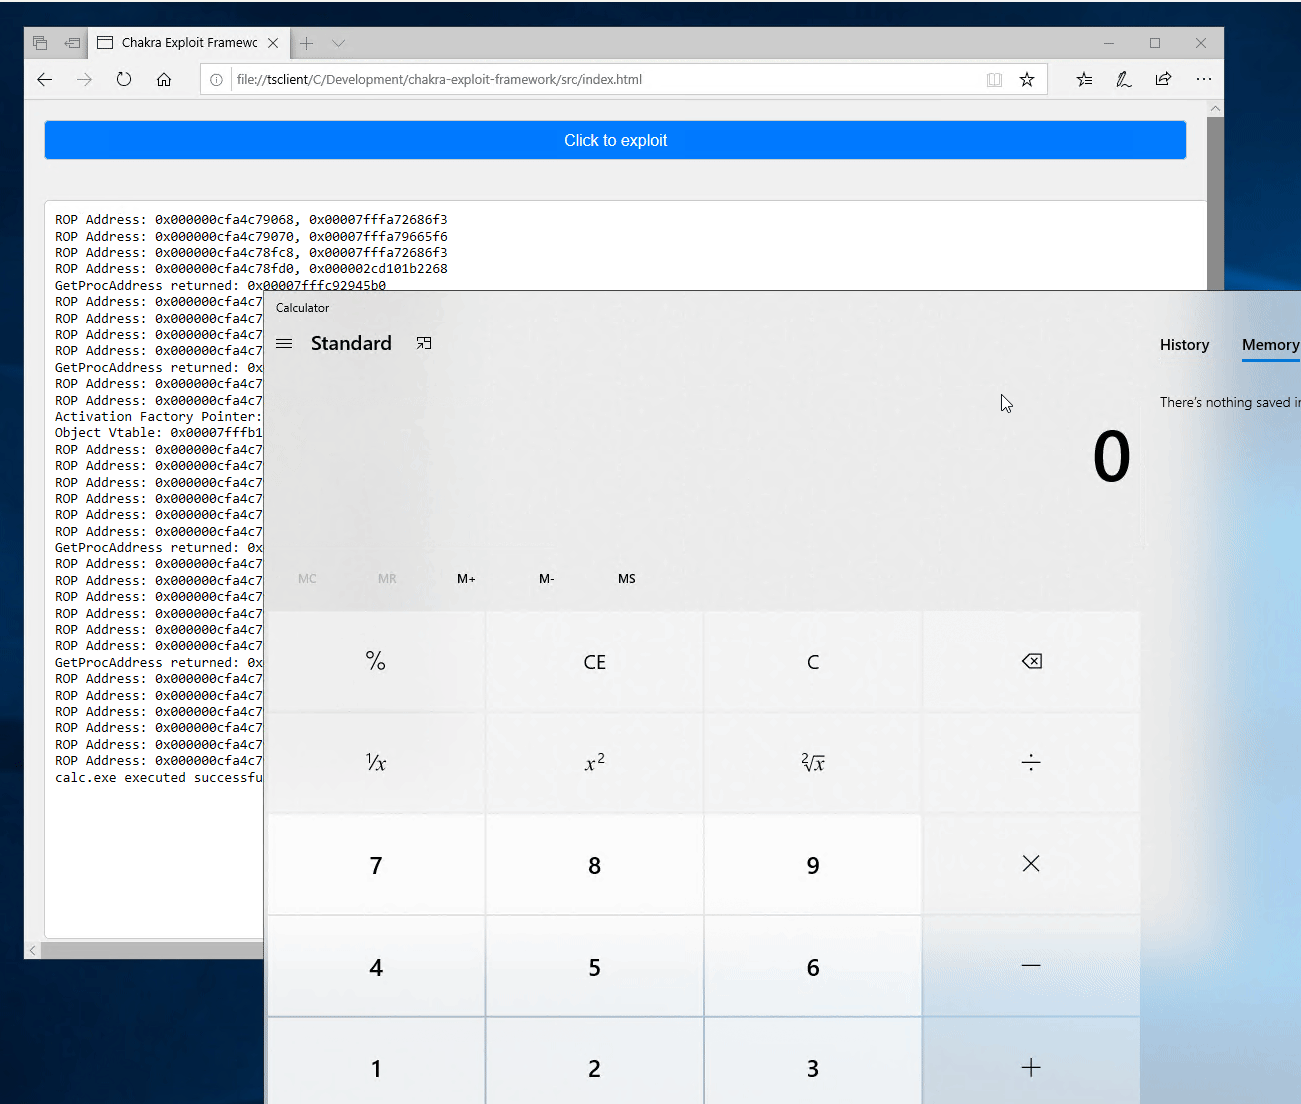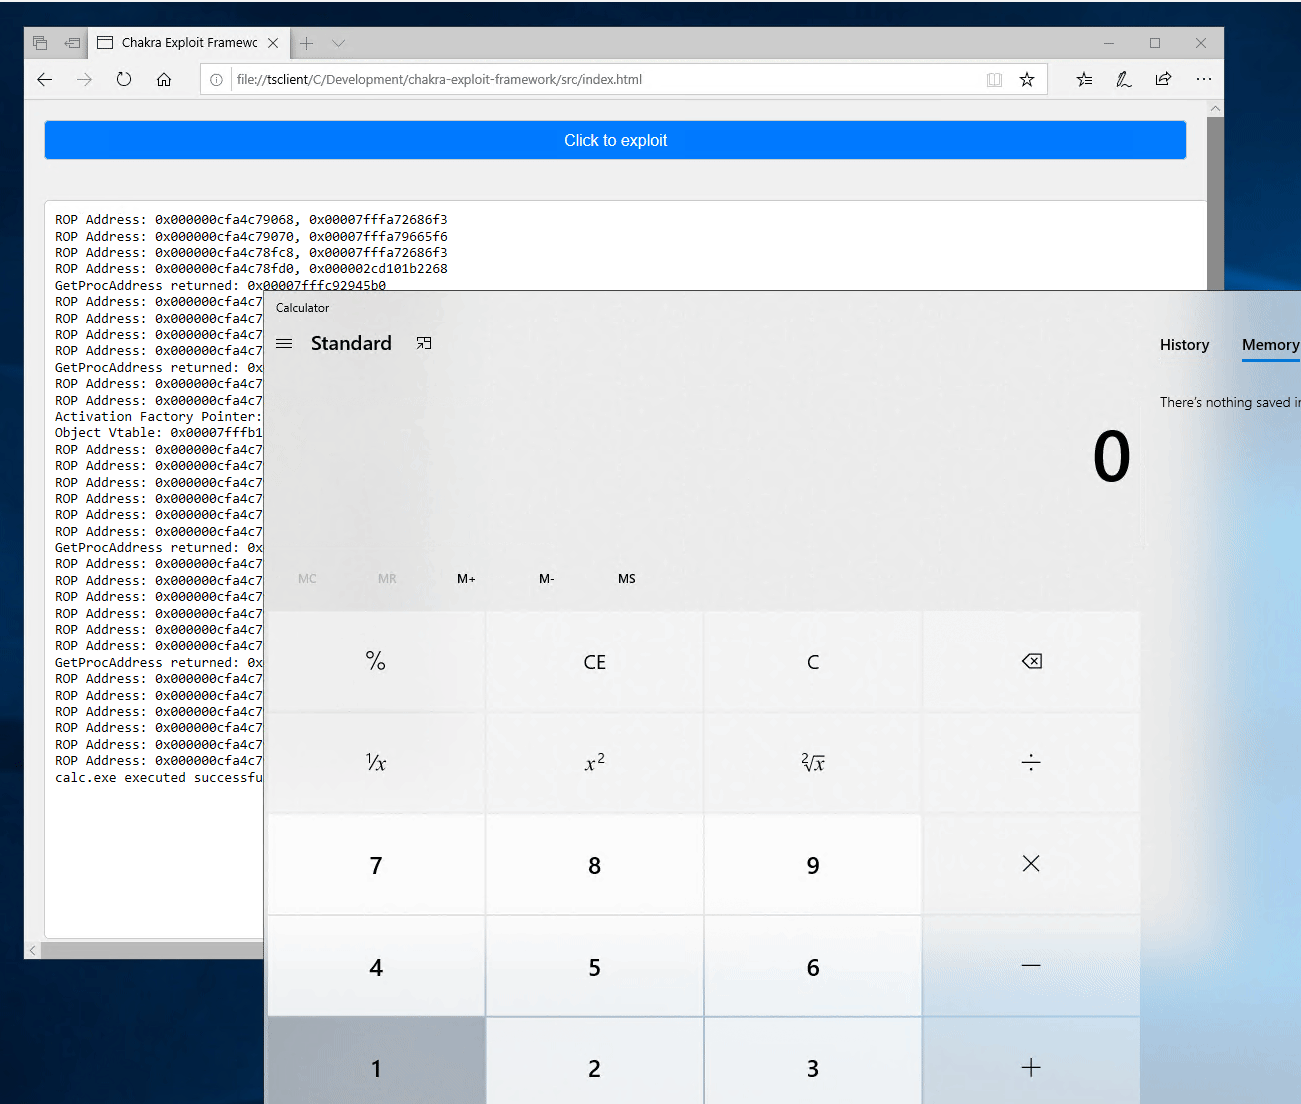 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 alexlee820/cve-2025-63946-tencent-pc-manager-eop
Proof-of-concept exploit for CVE-2025-63946, a local privilege escalation in Tencent PC Manager via symlink attacks on temporary directories,…
 s1d6point7bugcrowd/cve-2024-6387-race-condition-in-signal-handling-for-openssh
Technical analysis and proof-of-concept for CVE-2024-6387, a race condition in OpenSSH signal handling enabling unauthenticated remote code execution…
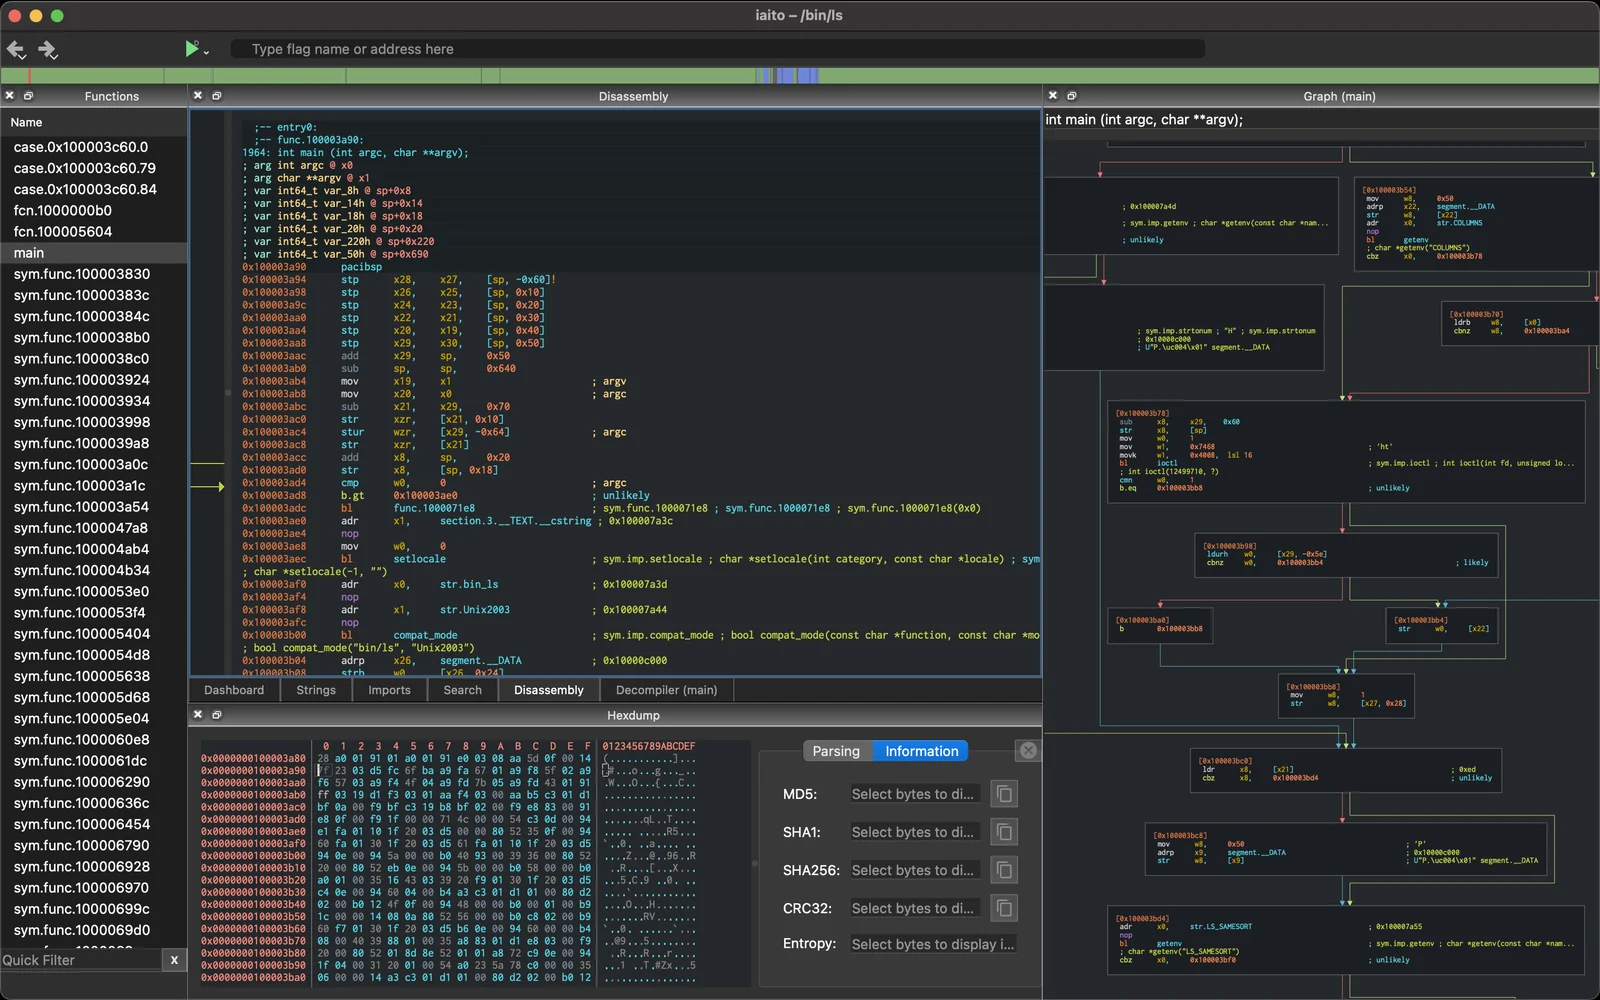 radareorg/iaito
Qt-based graphical interface for the radare2 reverse engineering framework, providing disassembly, binary analysis, debugging, patching and forensics…
 x86rc/unthemidator
An automated Themida / Code Virtualizer / WinLicense (v3.0-v4) unpacker and dump fixer tool
 d4rkks/cve-2025-7771-vulnerability-exploration
Escalating privilege in the system from unsigned driver using throttlestop vulnerability
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 sneakynachos/cve-2026-2796-and-cve-2026-2768-escape-the-wasm-box
Full Firefox chain: CVE-2026-2796 wasm type confusion -> content-process RCE, plus CVE-2026-2768 parent-process escape analysis (both fixed in…
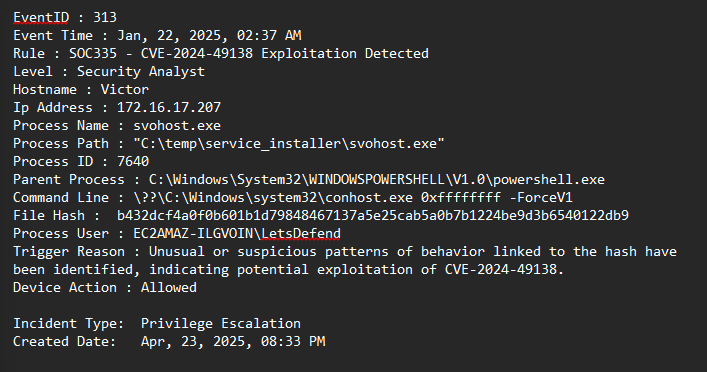 cyprianatsyor/letsdefend-cve-2024-49138-investigation
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.
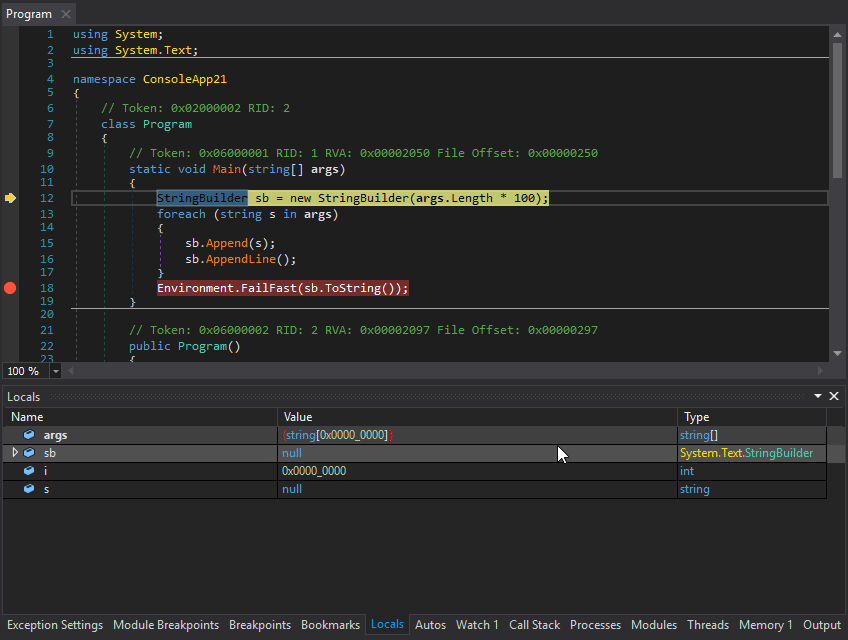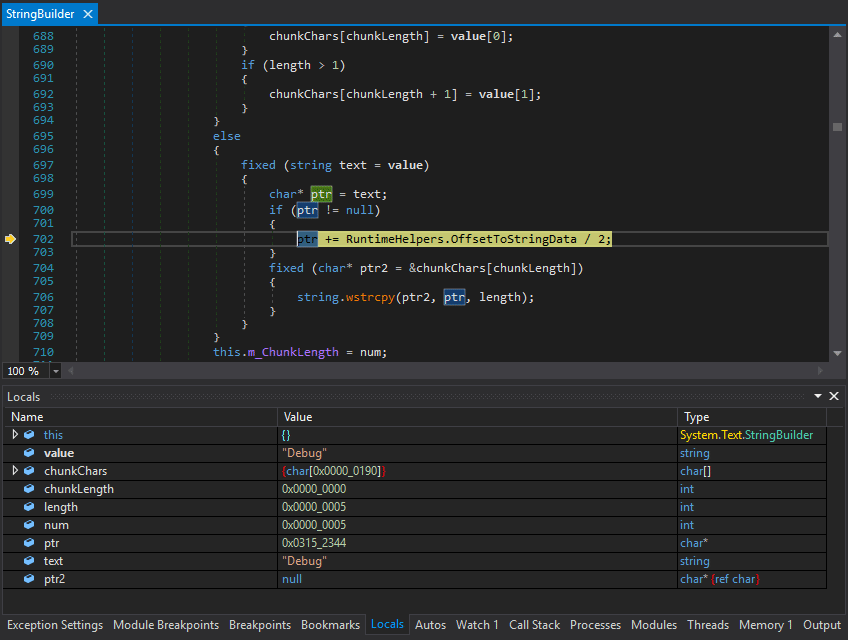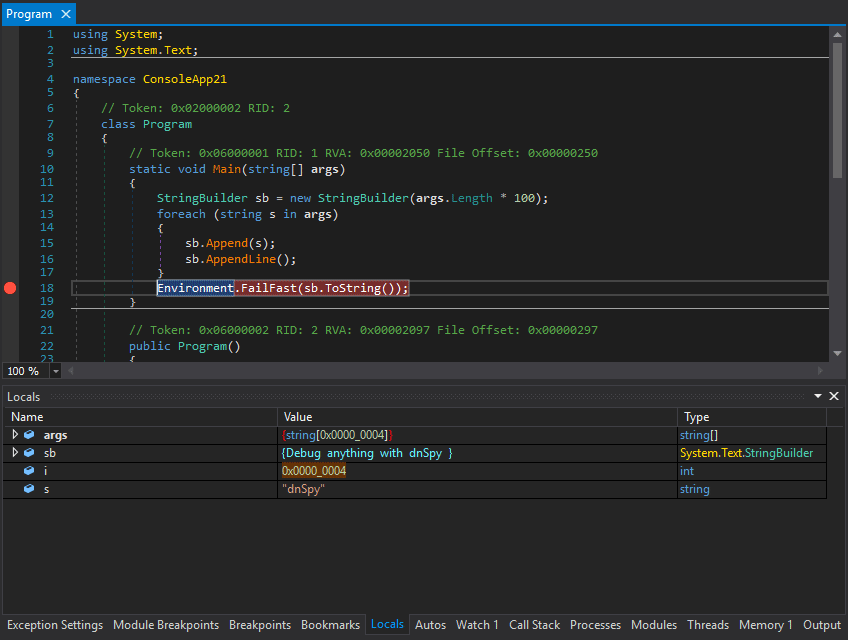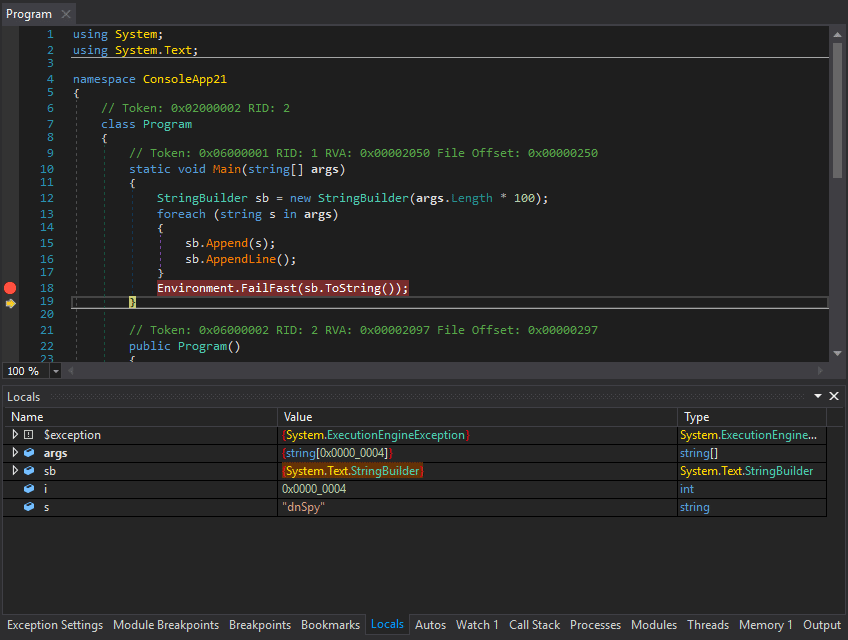
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
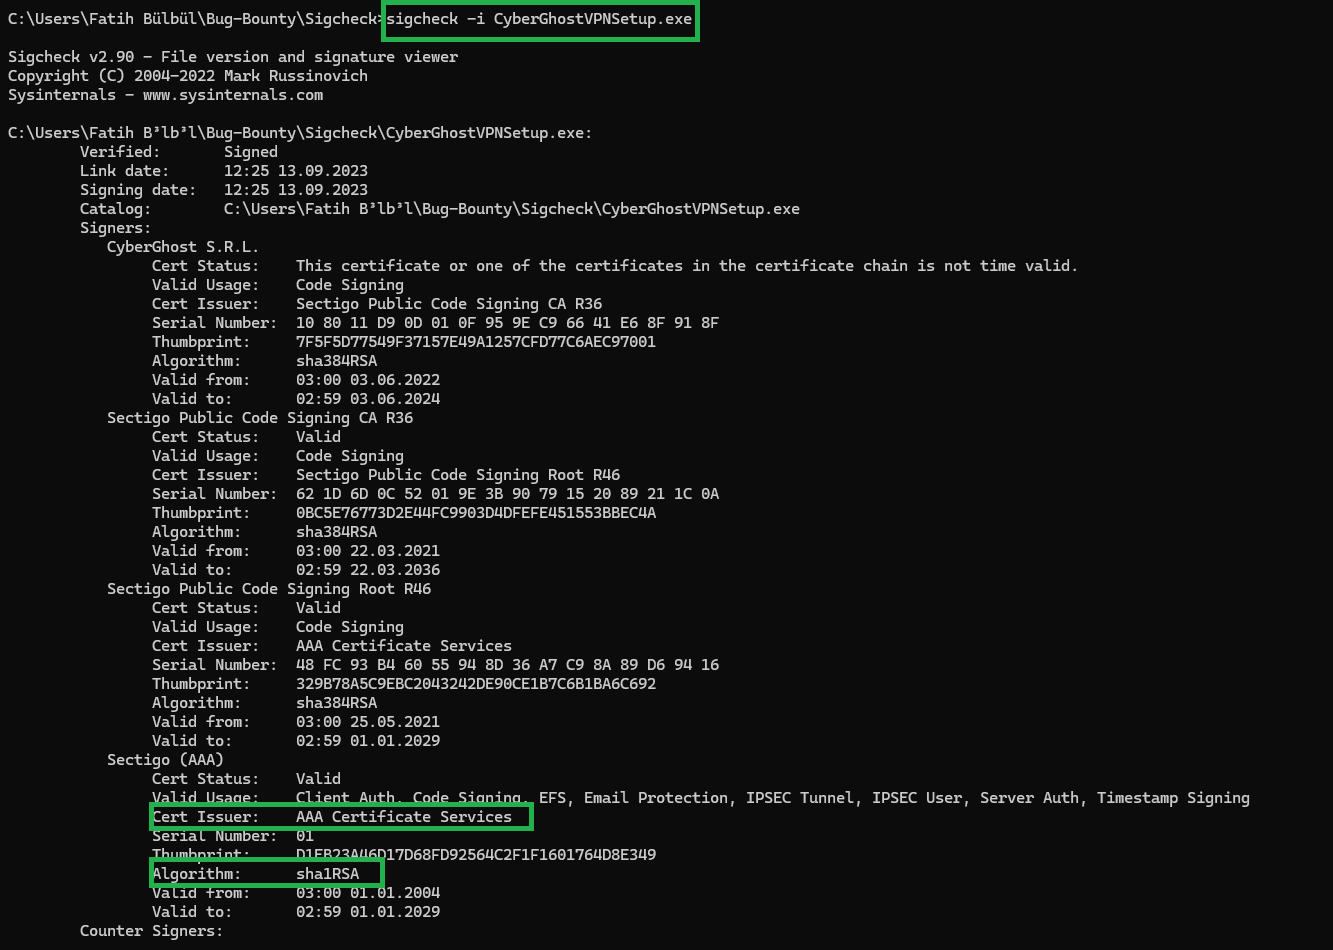 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…