
copy-fail-tiny-elf-CVE-2026-31431
 crihexe/copy-fail-tiny-elf-cve-2026-31431
Minimal no-libc Linux x86_64 ELF PoC build for Copy Fail (CVE-2026-31431)
binary-exploitationexploitationexploit-frameworks+1
crihexe/copy-fail-tiny-elf-cve-2026-31431Minimal no-libc Linux x86_64 ELF PoC build for Copy Fail (CVE-2026-31431)
 embedi/dir8xx_poc
Proof-of-Concept exploits for D-Link DIR8xx routers
 longofo/apache-dubbo-hessian2-cve-2021-43297
Demonstrates a proof-of-concept exploit for CVE-2021-43297, a deserialization vulnerability in Apache Dubbo's Hessian2 protocol, with provider and…
 tacnetsol/cve-2019-10999
Full exploit for D-Link DCS-5020L, POC crash for others that are vulnerable as well.
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
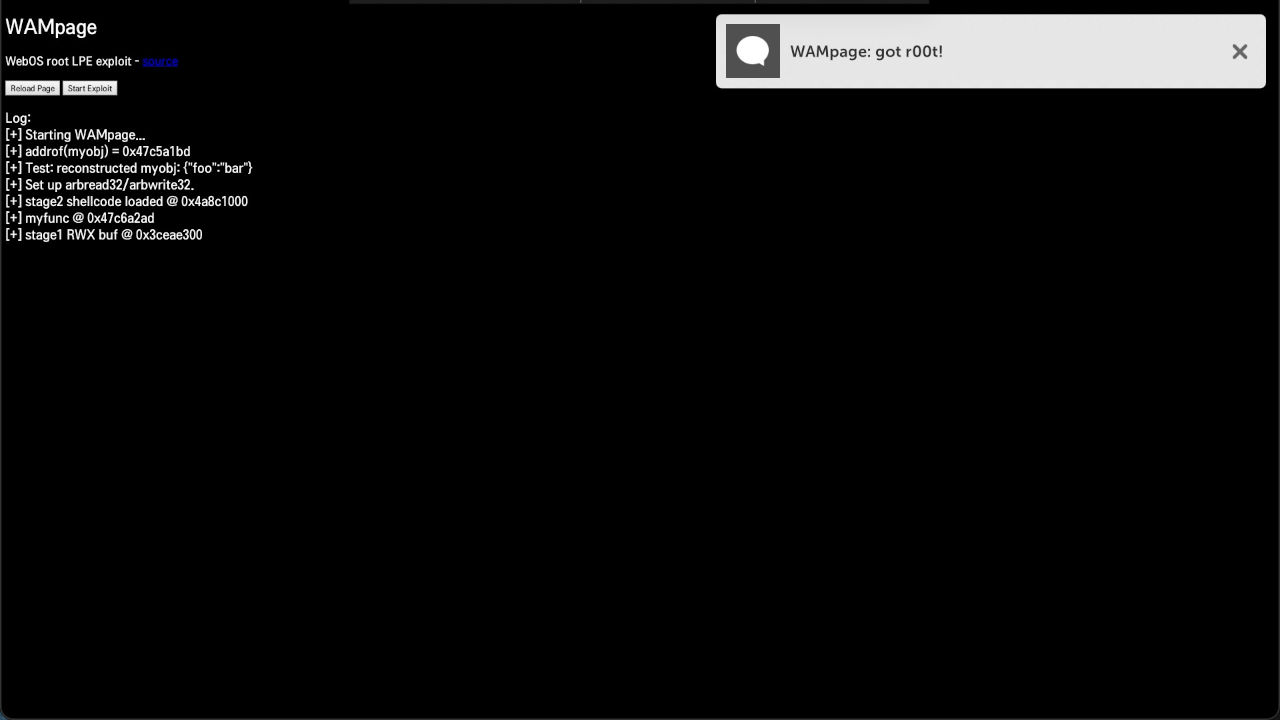 davidbuchanan314/wampage
WAMpage - A WebOS root LPE exploit chain (CVE-2022-23731)
 ck00004/cve-2021-4034
Exploit for CVE-2021-4034 (pkexec) targeting CentOS 8, allowing custom command execution via modified pwnkit-dry-run.c. Includes compilation and…
 f1tz/cve-2020-0796-lpe-exp
Compiled Windows SMBv3 local privilege escalation exploit targeting CVE-2020-0796 (SMBGhost). Tested on x64 Win10 1909.
 fi01/libmsm_acdb_exploit
Exploit for CVE-2013-2597, a stack-based buffer overflow in the Qualcomm ACDB audio driver, enabling privilege escalation on affected Android devices.
 zoemurmure/cve-2023-21768-afd-for-winsock-eop-exploit
Local privilege escalation exploit for Windows Ancillary Function Driver (afd.sys) targeting CVE-2023-21768, with post-exploitation cleanup code.…
 crackercat/cve-2024-35250
PoC for the Untrusted Pointer Dereference in the ks.sys driver
 go-spider/cve-2018-3252
Exploit for CVE-2018-3252 targeting WebLogic deserialization vulnerability. Includes payload generation with ysoserial and a Python proof-of-concept…
 mellow-hype/cve-2023-33476
Exploits for a heap overflow in MiniDLNA <=1.3.2 (CVE-2023-33476)
 askyeye/cve-2022-21894-payload
Example payload for CVE-2022-21894
 rva3/cve-2026-40003
Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
 otsmane-ahmed/cve-2025-2620-poc
Proof-of-concept exploit for CVE-2025-2620, a critical stack-based buffer overflow in D-Link DAP-1620 routers enabling unauthenticated remote code…
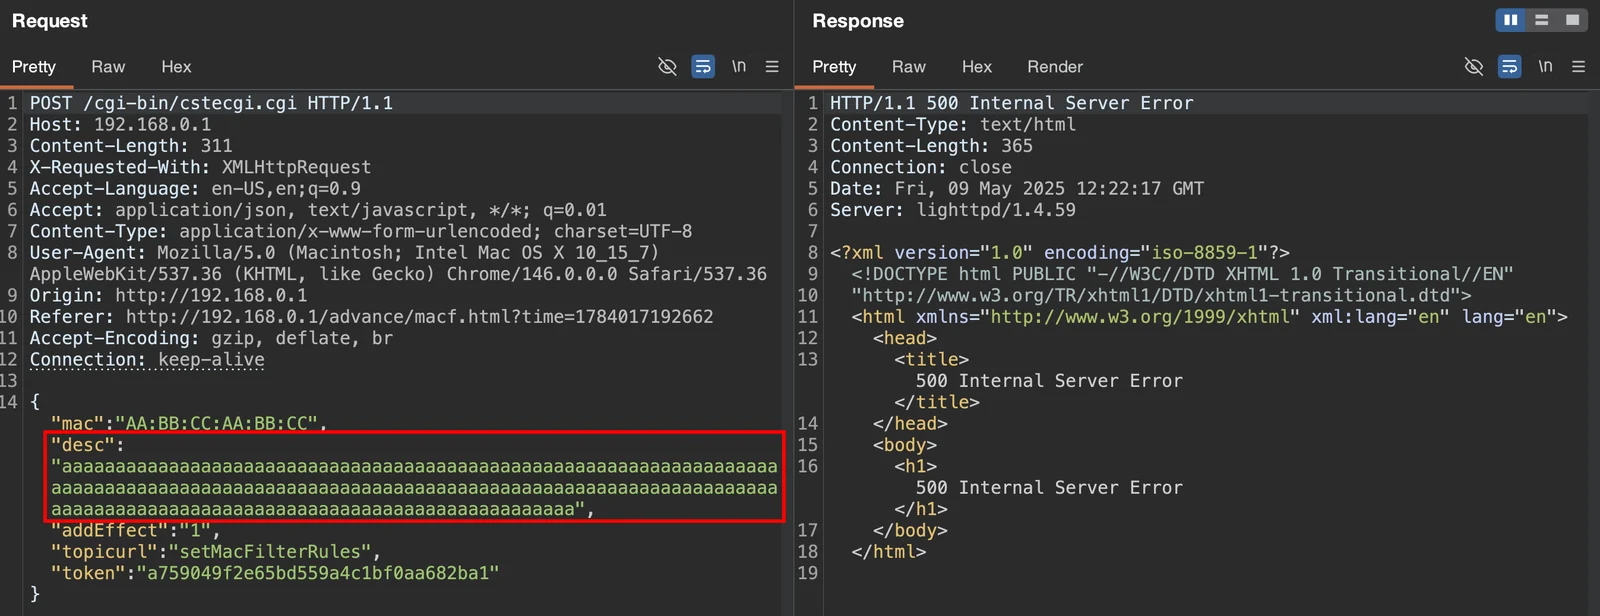 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 fortra/cve-2024-7479
Python proof-of-concept exploit for CVE-2024-7479, demonstrating privilege escalation via BYOVDKit driver abuse against TeamViewer on Windows.