
CVE-2021-22555-Poc
 spydomain/cve-2021-22555-poc
Heap overflow exploit for CVE-2021-22555 achieving local privilege escalation to root on Ubuntu 20.04 with kernel 5.8.0-48.
binary-exploitationexploitationinformation-gathering+3
1
spydomain/cve-2021-22555-pocHeap overflow exploit for CVE-2021-22555 achieving local privilege escalation to root on Ubuntu 20.04 with kernel 5.8.0-48.
 cyberkimathi/py3-cve-2017-0785
Proof-of-concept exploit for CVE-2017-0785, an Android Bluetooth stack remote code execution vulnerability. Enables testing and verification of the…
 lukinneberg/cve-2023-2636
Python-based proof-of-concept exploit for CVE-2023-2636, demonstrating a specific vulnerability with code for testing and verification in controlled…
 t1v0h/cve-2018-4415
Proof-of-concept exploit for CVE-2018-4415, a memory corruption vulnerability in Apple's macOS, demonstrating exploitation techniques.
 dothanthitiendiettiende/cve-2019-6207
Exploit for CVE-2019-6207: kernel heap information leak in getdirentriesattr on macOS <=10.14.4 and iOS <12.2, triggerable from sandbox.
 hyunjungg/cve-2023-21688
Exploit for CVE-2023-21688 combining a side-channel information leak with a use-after-free (UAF) chain for kernel privilege escalation.
 otsutez/cve-2024-12085
Exploit for CVE-2024-12085 Infoleak
 mouftan/cve-2022-44268
Python-based exploit for CVE-2022-44268, an arbitrary file read vulnerability in ImageMagick. Poisons PNG images to read sensitive files from…
 datntsec/cve-2020-1206
Technical analysis of CVE-2020-1206 (SMBleed) kernel information disclosure vulnerability in Windows SMBv3, including unauthenticated memory leak…
 abdurahmon3236/cve-2024-44947
Proof-of-concept exploit for Linux kernel FUSE information leak (CVE-2024-44947), demonstrating beyond-EOF memory disclosure via mmap and including…
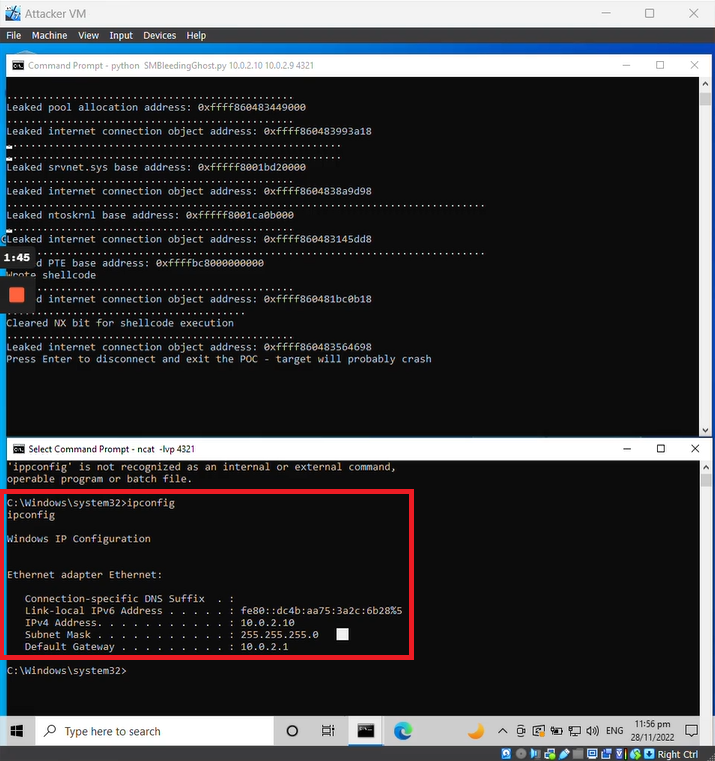 tdevworks/cve-2020-0796-smbghost-exploit-demo
Educational proof-of-concept exploit for CVE-2020-0796 (SMBGhost) demonstrating pre-auth RCE on Windows SMBv3. Includes step-by-step lab setup,…
 ieee0824/cve-2017-1000117-sl
Proof-of-concept exploit for CVE-2017-1000117, demonstrating a remote code execution vulnerability in Git's submodule handling.
 redhatkaty/-cve-2010-3904-report
Exploit for CVE-2010-3904, a Linux kernel privilege escalation vulnerability. Provides a proof-of-concept implementation for local privilege…
 exploits-forsale/prefetch-tool
Windows KASLR bypass using prefetch side-channel
 worawit/cve-2019-0708
CVE-2019-0708 (BlueKeep)
 idov31/etwleakkernel
Leaking kernel addresses from ETW consumers. Requires Administrator privileges.
 bazad/xpc-string-leak
CVE-2018-4248: Out-of-bounds read in libxpc during string serialization.
 niklasb/libc-database
Build a database of libc offsets to simplify exploitation