
CVE-2025-62215_analysis
 uky007/cve-2025-62215_analysis
CVE-2025-62215 exploit development using Claude Code Agent Team
binary-exploitationeducationexploitation+4
uky007/cve-2025-62215_analysisCVE-2025-62215 exploit development using Claude Code Agent Team
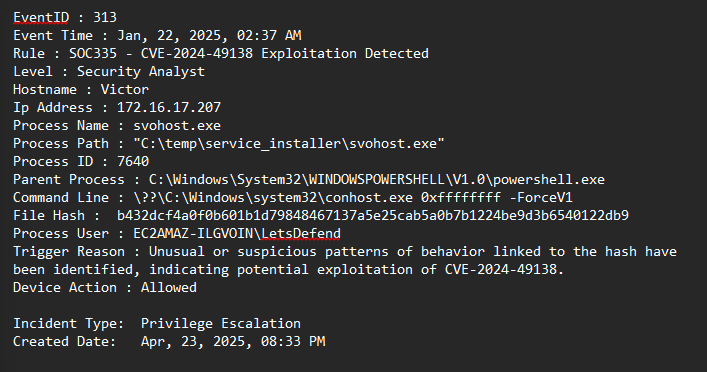 cyprianatsyor/letsdefend-cve-2024-49138-investigation
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 ustayready/wnfexec
WNF Code Execution Library Using C#
 samueltulach/voidmap
Using CVE-2021-40449 to manual map kernel mode driver
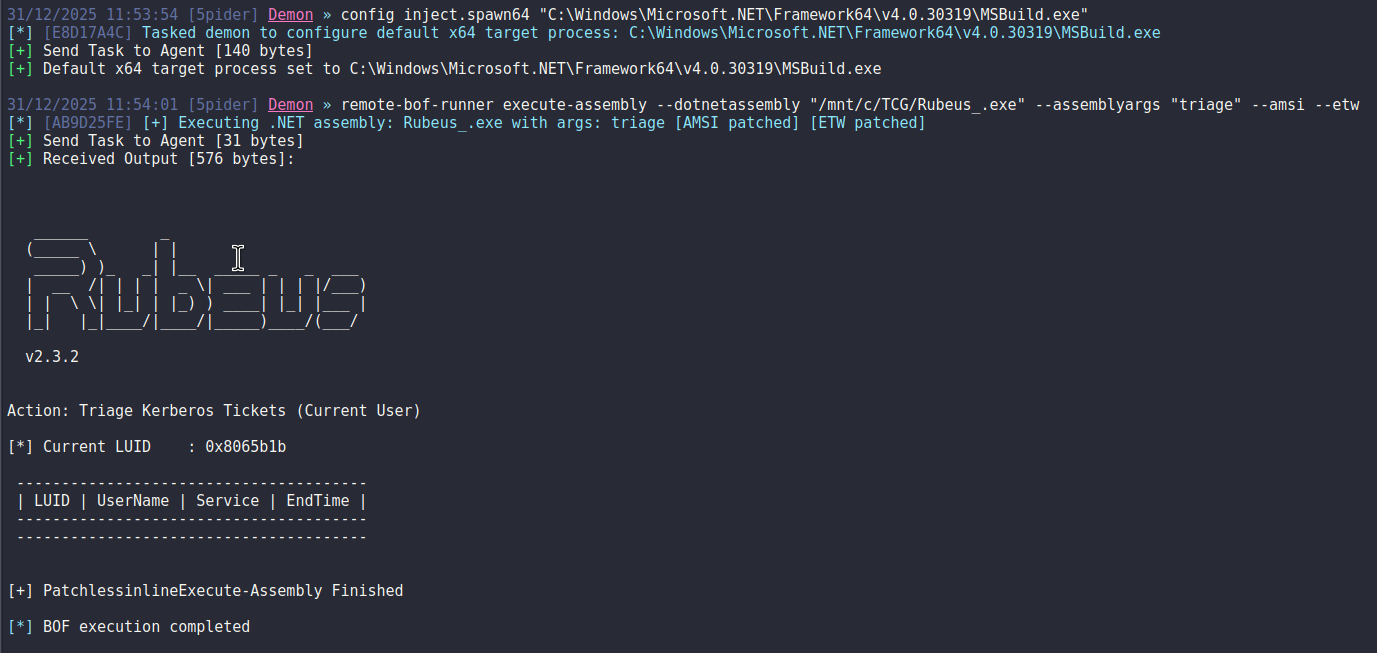 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 siberas/cve-2016-3309_reloaded
Exploits for the win32kfull!bFill vulnerability on Win10 x64 RS2 using Bitmap or Palette techniques
 pentestfunctions/cve-2025-8088-multi-document
Exploit systems using older WinRAR without knowing their username (unlike other projects)
 diego-tella/cve-2025-1055-poc
PoC for CVE-2025-1055 and CVE-2025-52915 using K7RKScan.sys
 d4rkks/cve-2025-7771-vulnerability-exploration
Escalating privilege in the system from unsigned driver using throttlestop vulnerability
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 pentestfunctions/best-cve-2025-8088
Winrar CVE exploitation before 7.13 using multiple ADS streams on a single file (Custom PDF implementation)
 iiictech/-cve-2020-0601-ecc---exploit
CurveBall (CVE-2020-0601) - PoC CVE-2020-0601, or commonly referred to as CurveBall, is a vulnerability in which the signature of certificates using…
 mr-bv/copy-fail-cve-2026-31431-exploit-in-c
C exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability in the AF_ALG AEAD path, using splice() to influence cached file…
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 sourceincite/cve-2018-8440
CVE-2018-8440 standalone exploit