
ROPgadget
 jonathansalwan/ropgadget
Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
binary-analysisbinary-exploitationctf+3
4.5k
jonathansalwan/ropgadgetSearch for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 ashemery/exploitation-course
Offensive Software Exploitation Course
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 fabiobaroni/awesome-exploit-development
A curated list of resources (books, tutorials, courses, tools and vulnerable applications) for learning about Exploit Development
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
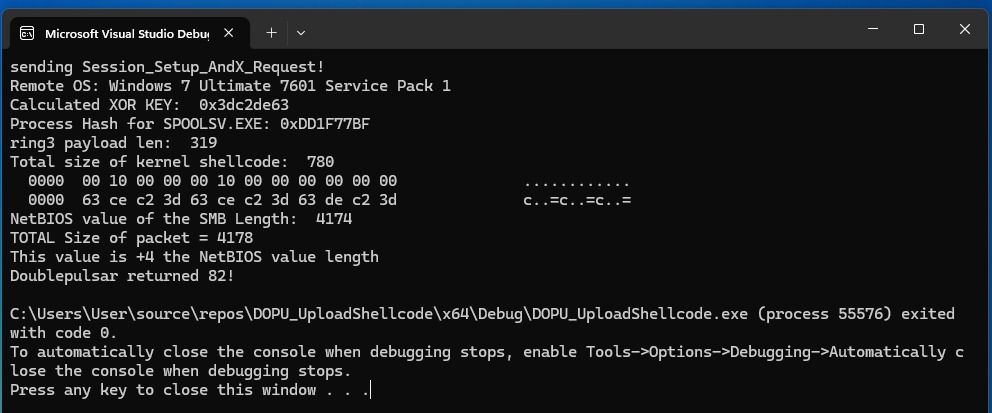 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 xairy/vmware-exploitation
A collection of links related to VMware escape exploits
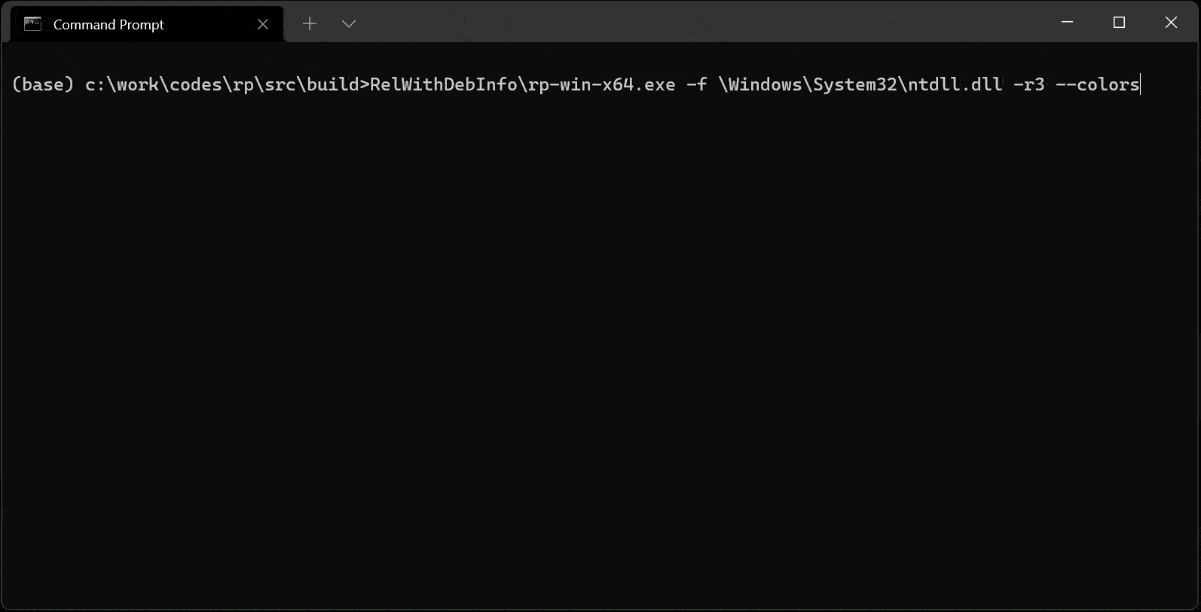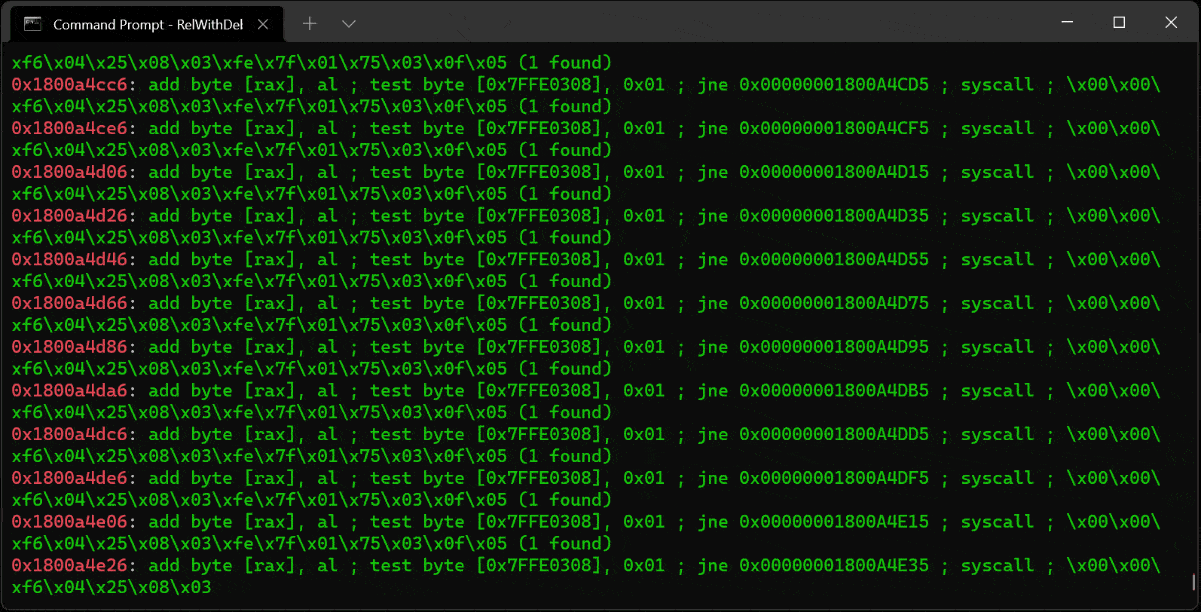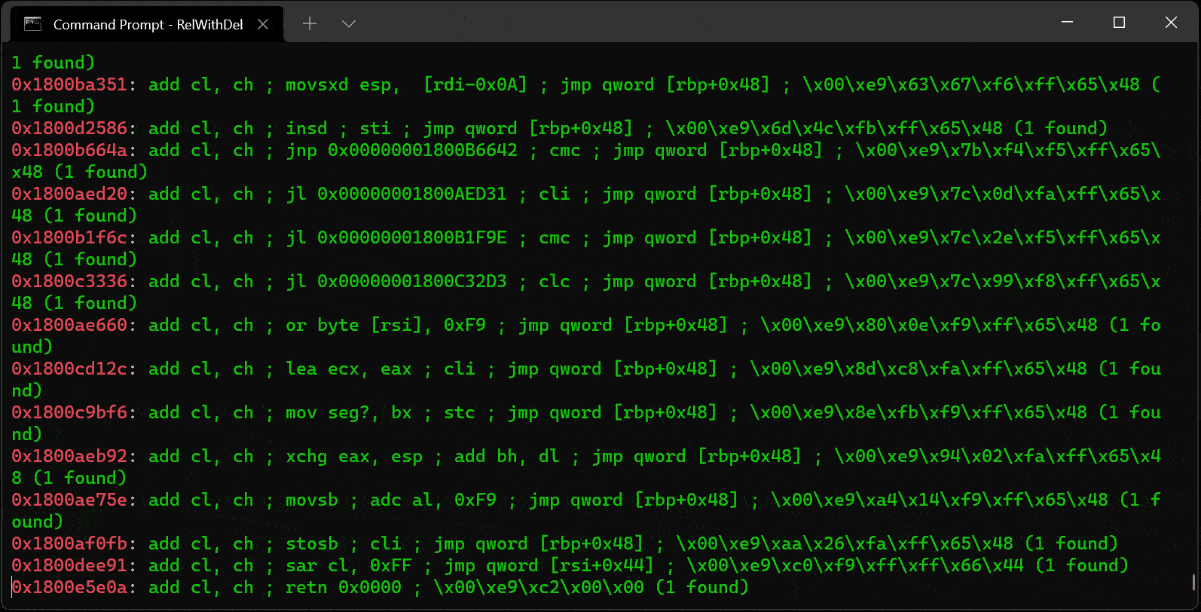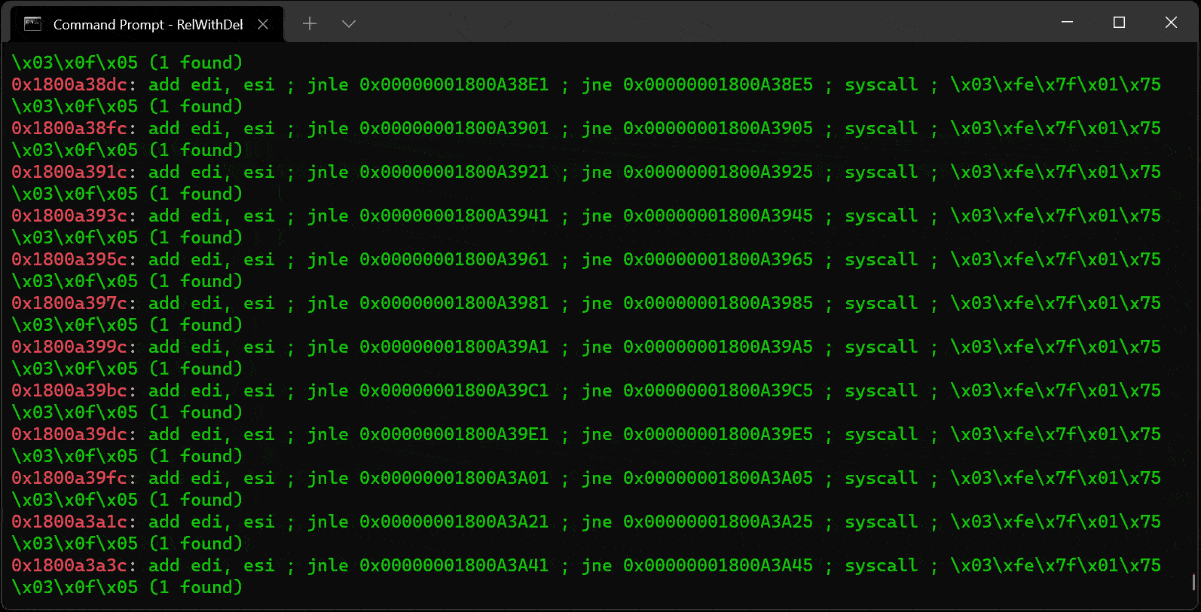 0vercl0k/rp
Fast C++ ROP gadget finder for PE/ELF/Mach-O binaries across x86/x64/ARM/ARM64 architectures, enabling efficient return-oriented programming chain…
 califio/publications
Curated collection of security research papers, CVE exploit writeups, reverse-engineering analyses of Apple internals, and commissioned security…
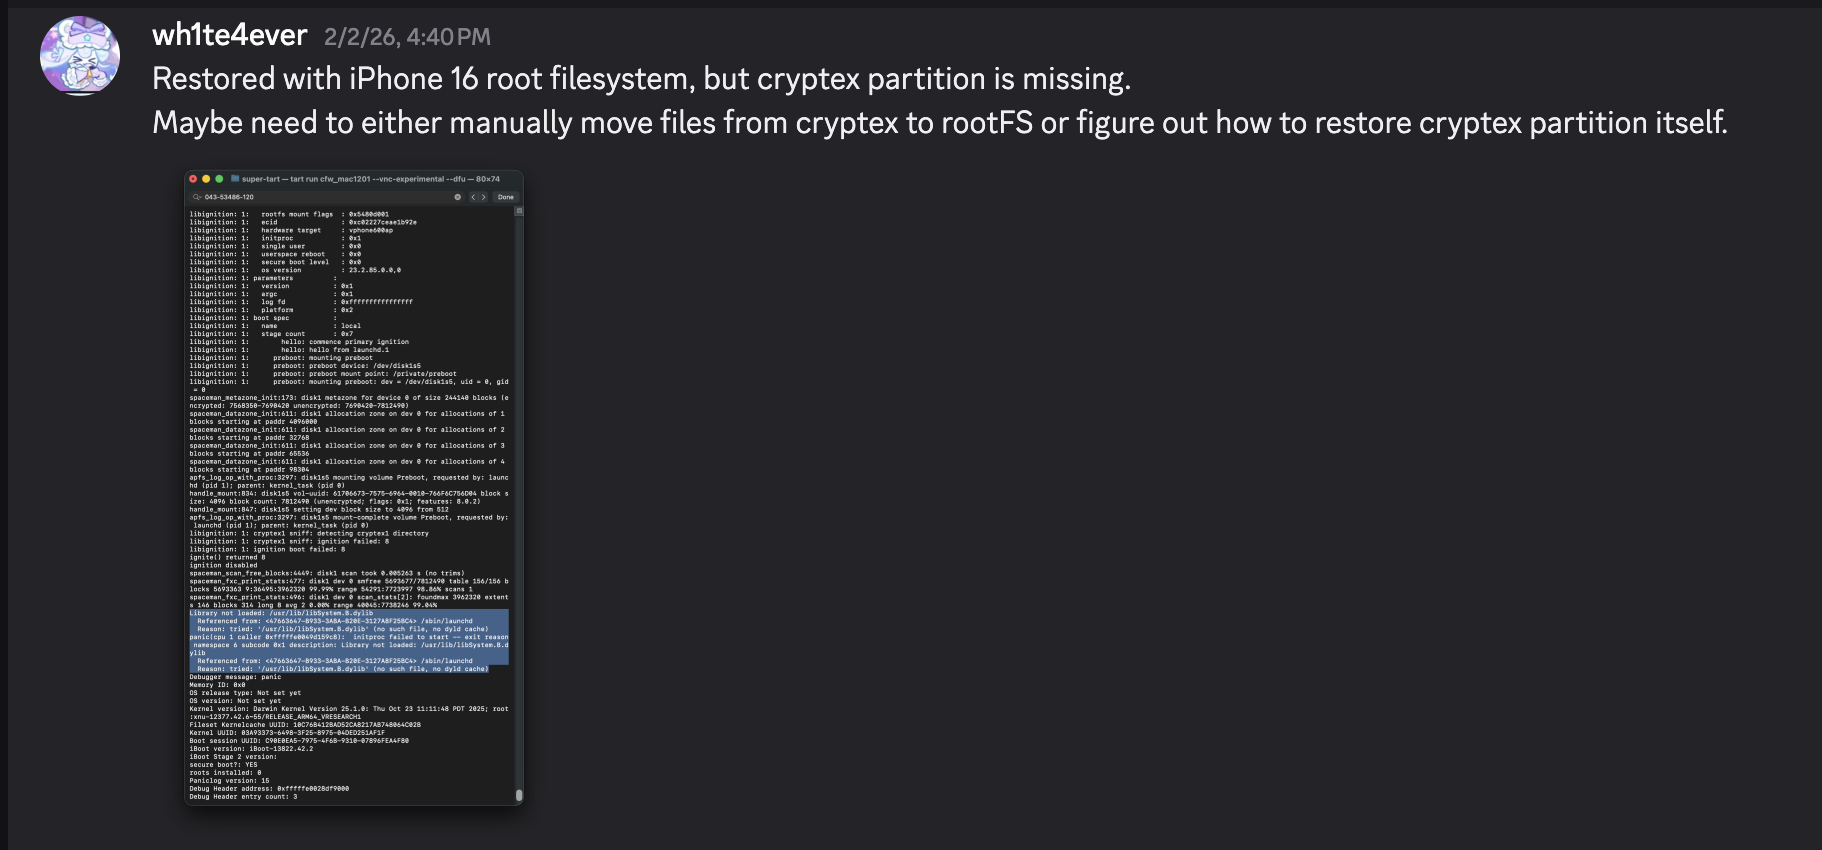 wh1te4ever/super-tart-vphone-writeup
Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…
 paboldin/meltdown-exploit
Meltdown Exploit PoC
 gjduck/e9patch
A powerful static binary rewriting tool
 eugnis/spectre-attack
Example of using revealed "Spectre" exploit (CVE-2017-5753 and CVE-2017-5715)
 egebalci/amber
Reflective PE packer.
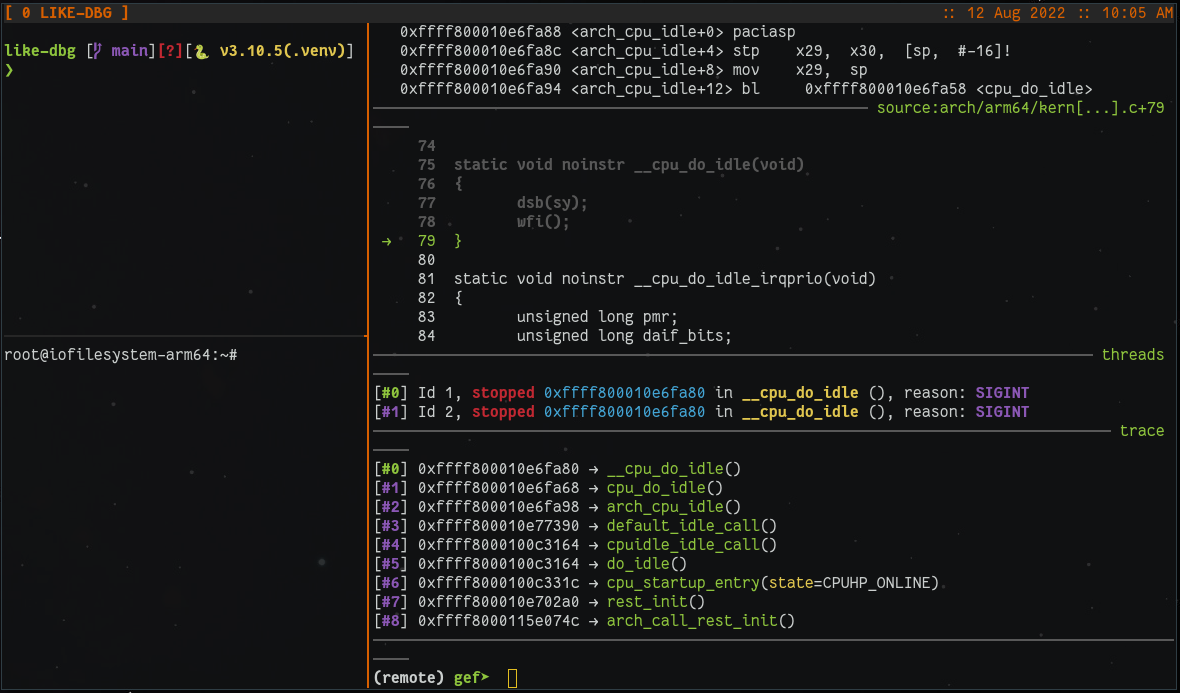 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment