

CVE-2026-42533
 jelasin/cve-2026-42533
Proof-of-concept reproduction of an nginx heap overflow and info leak (CVE-2026-42533) with two attack surfaces, debug analysis, and a full RCE chain.
binary-exploitationcode-analysisdebuggers+4
jelasin/cve-2026-42533Proof-of-concept reproduction of an nginx heap overflow and info leak (CVE-2026-42533) with two attack surfaces, debug analysis, and a full RCE chain.
 vett3x/smb-linux-cve-2025-37899
Technical analysis of CVE-2025-37899: a use-after-free vulnerability in Linux kernel's ksmbd SMB module enabling remote code execution. Includes…
 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
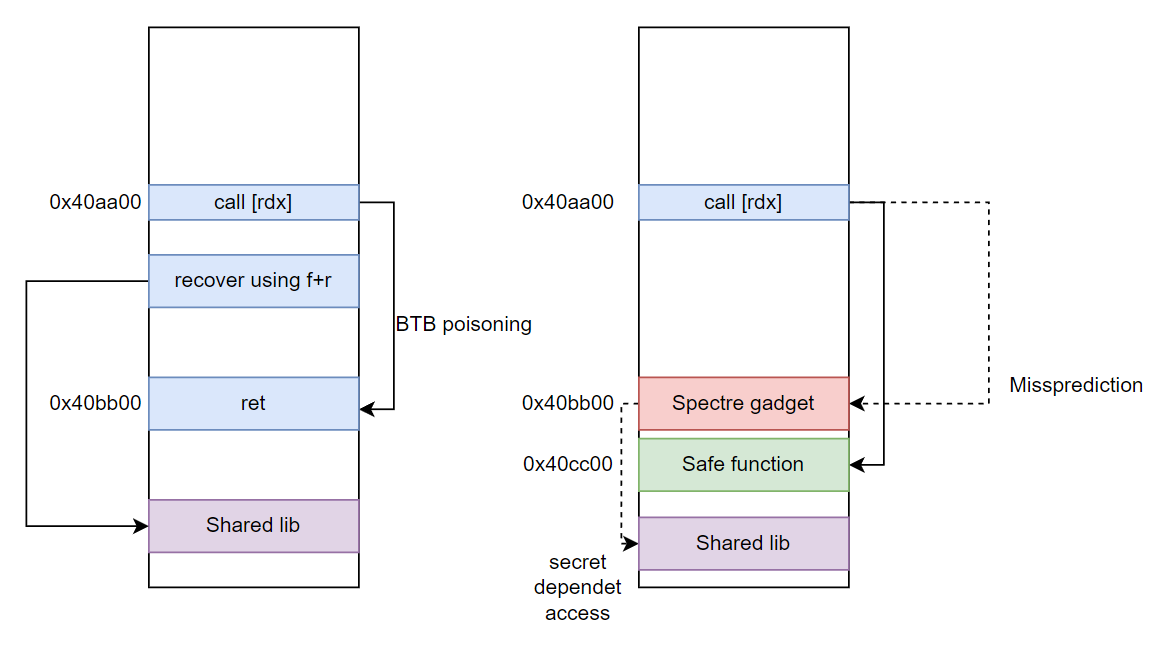 es0j/execaslr-ekoparty
Proof-of-concept exploit that bypasses ASLR on Intel CPUs by abusing branch target buffer and speculative execution to leak randomized addresses via…
 spiralbl0ck/rowhammer-exploit
RowHammer Based-Exploit
 bitdefender/swapgs-attack-poc
This repository contains the sources and documentation for the SWAPGS attack PoC (CVE-2019-1125)
 lakshan-sameera/cve-2025-32462-and-cve-2025-32463---critical-sudo-vulnerabilities
Proof-of-concept exploit code for critical sudo vulnerabilities CVE-2025-32462 and CVE-2025-32463, demonstrating privilege escalation attack vectors.
 teawater/cve-2017-5123
Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…
 mk017-hk/cve-2025-5548
Security research and technical analysis of CVE-2025-5548, a buffer overflow vulnerability affecting FreeFloat FTP Server 1.0. This repository…
 mbanyamer/rtos-f-16-exploit---cve-2019-7711
Proof-of-concept exploit for CVE-2019-7711, a format string vulnerability in Green Hills INTEGRITY RTOS. Demonstrates a full attack chain with memory…
 bitdefender/lvi-lfb-attack-poc
This repository contains the sources and documentation for the LVI-LFB Control Flow Hijacking attack PoC (CVE-2020-0551)
 abdul-kalam2000/retbleed-speculative-execution-poc
Reproduction of the Retbleed (CVE-2022-29900/29901) micro-architectural attack in gem5. RSB underflow, Flush+Reload side-channel leak, and a verified…
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
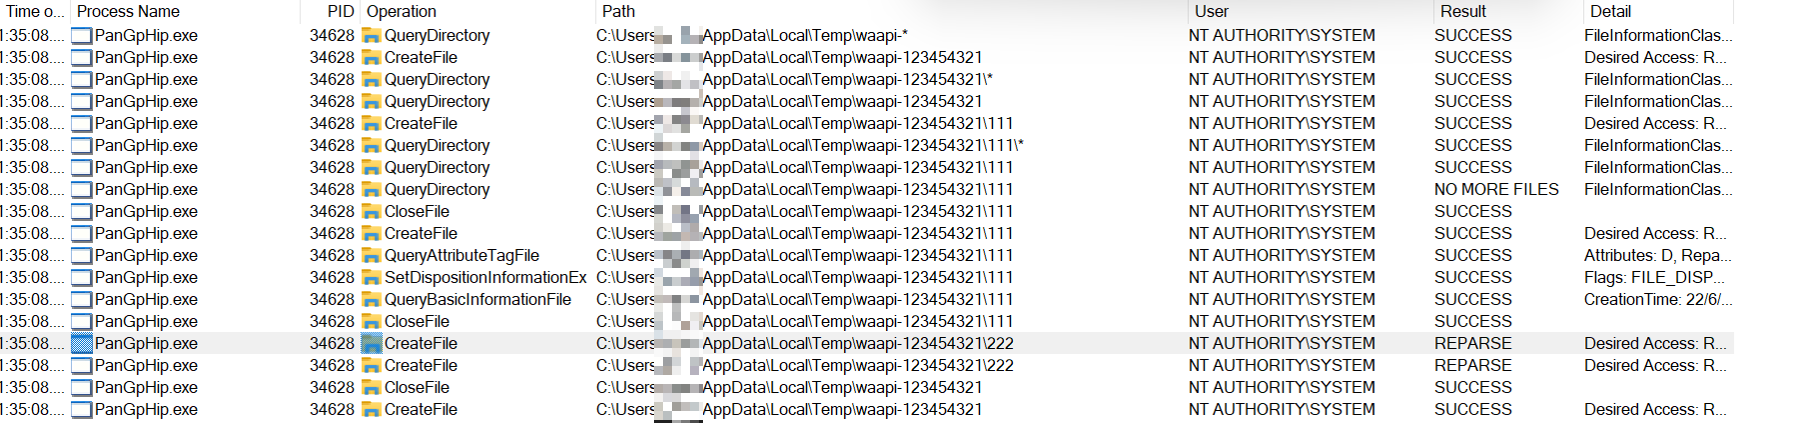 hagrid29/cve-2024-2432-paloalto-globalprotect-eop
Proof-of-concept exploit for CVE-2024-2432 demonstrating local privilege escalation on Windows via arbitrary file delete through symbolic link attack…
 spiralbl0ck/cve-2024-40431-cve-2022-25479-eop-chain
CVE-2024-40431+CVE-2022-25479 chain for EOP(DATA ONLY ATTACK)
 mbanyamer/cve-2025-24076
Python exploit for CVE-2025-24076, a Windows Cross Device Service privilege escalation vulnerability. Replaces a DLL to achieve SYSTEM privileges via…
 101010zyl/cve-2024-0582-dataonly
Data-only local privilege escalation exploit for Linux kernel io_uring CVE-2024-0582, using sprayed file structures and ext4_file_operations hooks to…
 0xblackash/cve-2026-12485
CVE-2026-12485