
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
822 results
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…

binary-exploitationexploitationmalware-analysis+6
126
9 months ago
globalprotect-ca-cert-ipc preview

globalprotect-ca-cert-ipc

GitHubs3c/globalprotect-ca-cert-ipc

Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.

binary-exploitationexploitationmalware-analysis+3
1 year ago
IAT-Hook preview

IAT-Hook

GitHubgmh5225/iat-hook

C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…

binary-exploitationcode-analysismalware-analysis+4
4 years ago
Silverseal preview

Silverseal

GitHubidov31/silverseal

Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…

binary-exploitationexploitationmalware-analysis+4
16625 days ago
themida-unmutate preview

themida-unmutate

GitHubergrelet/themida-unmutate

Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.

binary-analysisbinary-exploitationmalware-analysis+3
3952 years ago
WinRAR-CVE-2025-8088-Path-Traversal-PoC preview

WinRAR-CVE-2025-8088-Path-Traversal-PoC

GitHubpexlexity/winrar-cve-2025-8088-path-traversal-poc

Proof-of-Concept for CVE-2025-8088 vulnerability in WinRAR (path traversal via ADS)

binary-exploitationexploitationmalware-analysis+3
21 year ago
CVE-2025-55891 preview

CVE-2025-55891

GitHubterribledactyl/cve-2025-55891

Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…

binary-exploitationexploitationfuzzing+3
1 year ago
KillChain preview

KillChain

GitHuboxfemale/killchain

Kernel Process Termination Tool ( CVE-2026-0828 exploit)

binary-exploitationexploitationmalware-analysis+3
366 months ago
CVE-2025-56799 preview

CVE-2025-56799

GitHubshinycolumn/cve-2025-56799

OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application

binary-exploitationexploitationmalware-analysis+3
111 months ago
CVE-2024-27518 preview

CVE-2024-27518

GitHubsecunnix/cve-2024-27518

SUPERAntiSpyware Professional X <=10.0.1264 LPE Vulnerability PoC

binary-exploitationexploitationmalware-analysis+2
2 years ago
CVE-2025-51726 preview

CVE-2025-51726

GitHubmeisterlos/cve-2025-51726

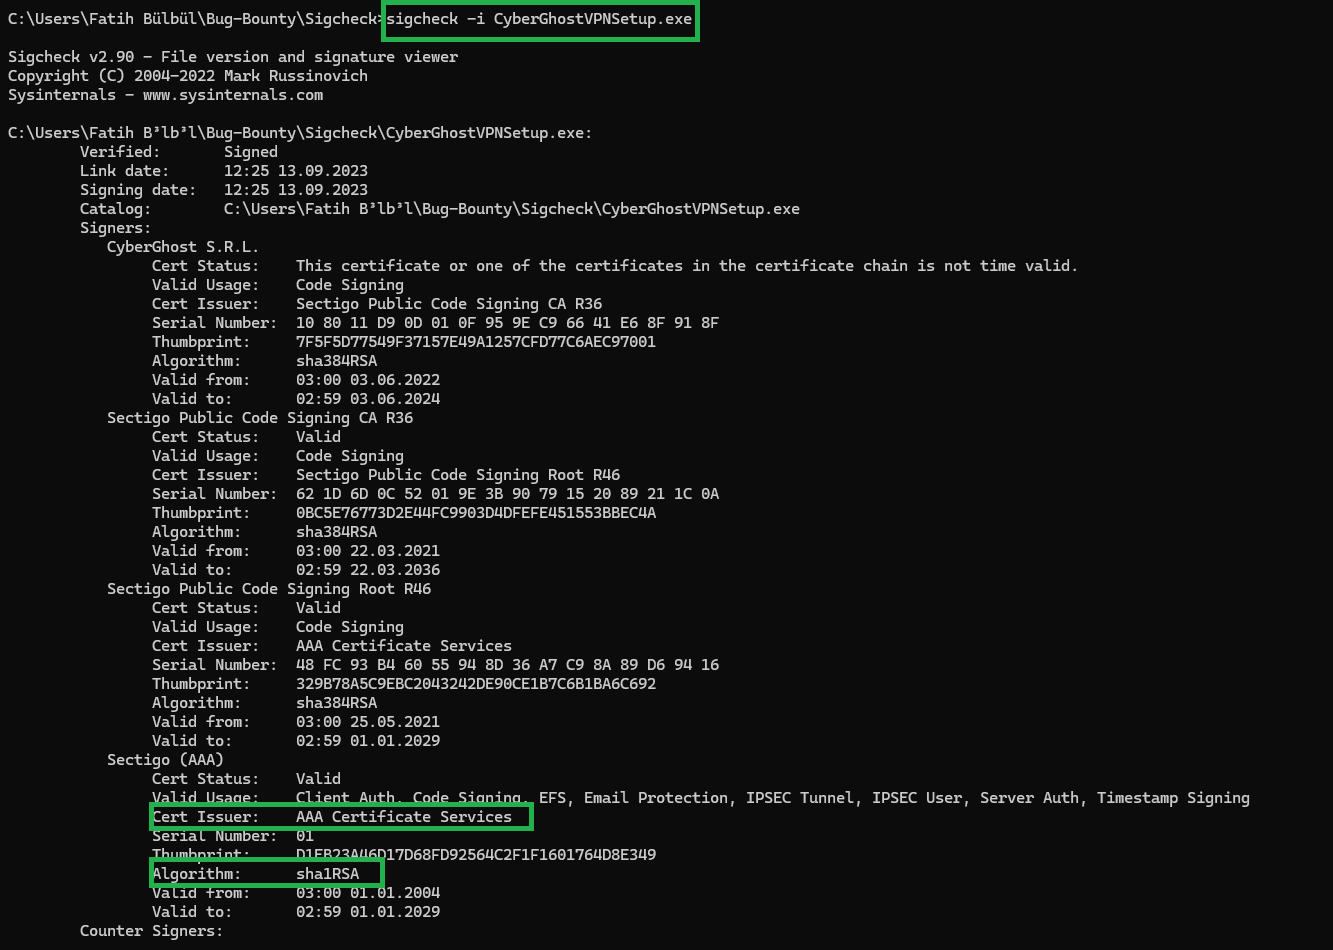
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…

binary-exploitationexploitationmalware-analysis+4
1 year ago
CVE-2026-54424 preview

CVE-2026-54424

GitHubtomadimitrie/cve-2026-54424

Exploiting Parsec for Windows to gain SYSTEM privileges

binary-exploitationcommand-and-controlexploitation+5
3 months ago
Ivanti-Pulse_VPN-Client_Exploit-CVE-2023-35080_Privilege-escalation preview

Ivanti-Pulse_VPN-Client_Exploit-CVE-2023-35080_Privilege-escalation

GitHubhophouse/ivanti-pulse_vpn-client_exploit-cve-2023-35080_privilege-escalation

Exploit for CVE-2023-35080 leveraging a write primitive in the Ivanti/Pulse VPN client kernel driver on Windows to achieve privilege escalation.

binary-exploitationexploitationexploit-frameworks+2
12 years ago
CVE-2020-0753-and-CVE-2020-0754 preview

CVE-2020-0753-and-CVE-2020-0754

GitHubafang5472/cve-2020-0753-and-cve-2020-0754

Writeup and POC for CVE-2020-0753, CVE-2020-0754 and six fixed Window DOS Vulnerabilities.

binary-exploitationeducationexploitation+3
146 years ago
CVE-2020-0753-and-CVE-2020-0754 preview

CVE-2020-0753-and-CVE-2020-0754

GitHubvikasvarshney/cve-2020-0753-and-cve-2020-0754

Writeup and POC for CVE-2020-0753, CVE-2020-0754 and six unfixed Window DOS Vulnerabilities.

binary-exploitationeducationexploitation+3
66 years ago
FUD-UUID-Shellcode preview

FUD-UUID-Shellcode

GitHubbl4ckm1rror/fud-uuid-shellcode

C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…

binary-exploitationdefensive-toolsexploitation+6
3343 years ago
exch_CVE-2021-42321 preview

exch_CVE-2021-42321

GitHub7bitsteam/exch_cve-2021-42321

Modified .NET deserialization payload for CVE-2021-42321, based on ysoserial.net, that writes files and bypasses Windows Defender to target Microsoft…

binary-exploitationexploitationpayload-development+3
103 years ago
cve-2026-62737-lab preview

cve-2026-62737-lab

GitHubdavidcarliez/cve-2026-62737-lab

Elevates a low-privilege Windows process to SYSTEM via a gdb-assisted ROP token-swap chain, demonstrating CVE-2026-62737 in a lab-only QEMU…

binary-exploitationdebuggersexploitation+2
21 month ago
Previous123…46Next