
CVE-2025-5548
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
binary-exploitationdebuggersexploitation+5
vsvalinx/cve-2025-5548Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 canomer/cve-2026-36980-kernel-bsod-dos-poc
Project Date : Feb 2026 / Discovered a buffer overflow vulnerability in the IOCTL handler of the kernel driver. The vulnerability allows an…
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 alfa8sa/cve-2025-5548
Heap Buffer Overflow in CVE-2025-5548
 elrajiii/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0
 iamescri/cve-2025-5548-freefloat-ftp-buffer-overflow
Laboratorio de análisis y explotación de la vulnerabilidad CVE-2025-5548 en FreeFloat FTP Server 1.0
 javyan05/cve-2025-5548
Entorno y explotación de la vulnerabilidad CVE-2025-5548
 anasrami12/cve-2025-5548
Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…
 ptresearch/inteltxe-poc
Intel Management Engine JTAG Proof of Concept
 nazeeh111/capsulith
Run preserved ARM64 code in Node or a browser; inspect decoded image pixels and initialized memory.
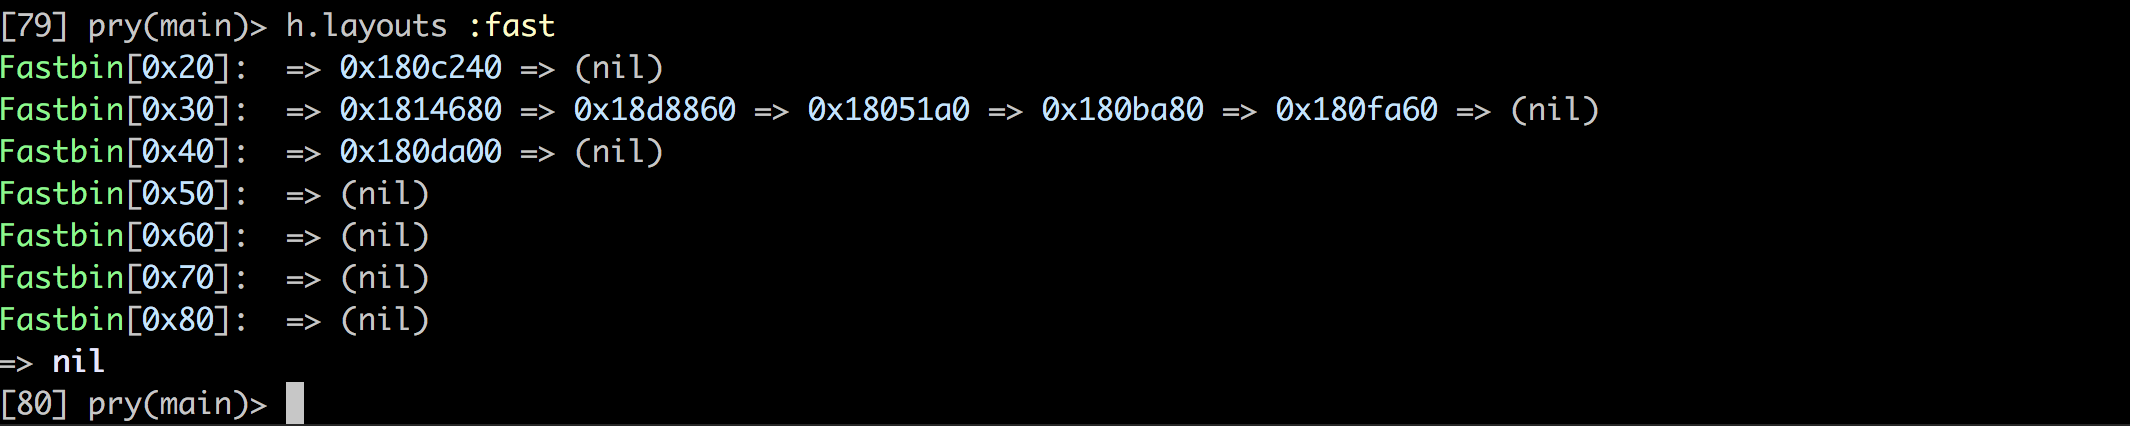 david942j/heapinfo
An interactive memory info for pwning / exploiting