
CVE-2025-5548
 jsantos1990/cve-2025-5548
🚀 Complete analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server 1.0 - NOOP Buffer Overflow) Full methodology: manual tool installation,…
binary-exploitationeducationexploitation+6
jsantos1990/cve-2025-5548🚀 Complete analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server 1.0 - NOOP Buffer Overflow) Full methodology: manual tool installation,…
 devianntsec/cve-2021-4034
Master's thesis research on CVE-2021-4034 (PwnKit) local privilege escalation. Multi-payload Python exploit with 7 modes including interactive shell,…
 kaleth4/cve-2026-4747-
Remote kernel exploit for FreeBSD CVE-2026-4747, leveraging a stack buffer overflow in kgssapi.ko to achieve RCE with a reverse shell. Includes…
 redcrazyghost/cve-2026-42945
Go-based exploit tool for CVE-2026-42945 (nginx HTTP/2) with detection, crash probing, command execution, and reverse shell capabilities for…
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
 lipeozyy/cve-2010-1872-blazedvd-seh-exploit
Proof-of-concept SEH buffer overflow exploit for BlazeDVD 5.0 via crafted .plf playlist file, generating a reverse shell payload with msfvenom for…
 kylvgoi/cve-2019-1663
Educational exploit for CVE-2019-1663 targeting a stack-based buffer overflow in Cisco RV routers. Includes a Python exploit script, reverse shell…
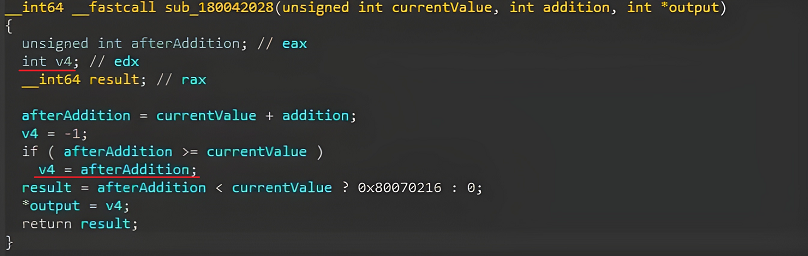 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 charlyrr/cve-2025-5548
Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
 incredible1yu/cve-2017-7494
C exploit for CVE-2017-7494 (Samba is_known_pipename) with custom shared object compilation and reverse shell payload generation.
 androidteacher/cve-2026-24061-poc-telnetd
Proof-of-concept exploit for CVE-2026-24061, an unauthenticated remote root privilege escalation in inetutils-telnetd via USER environment variable…
 foudadev/cve-2007-2447
Educational exploit implementation for CVE-2007-2447 Samba 3.0.20-3.0.25rc username map script command execution vulnerability with Python SMB client…
 victoriousknight/cve-2023-38831_exploit
Python script that generates a malicious RAR file exploiting CVE-2023-38831 to execute a reverse shell payload, intended for educational and ethical…
 h-wookie/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, demonstrating Docker container escape via runC vulnerability with reverse shell payload injection.
 monjheta/cve-2020-0796
Proof-of-concept remote code execution exploit for CVE-2020-0796 (SMBGhost) targeting unpatched Windows 10 1903/1909. Delivers a reverse shell via…
 caioprince/cve-2019-11395
Python exploit for CVE-2019-11395, a buffer overflow in MailCarrier 2.51 POP3 service. Generates a reverse shell payload via msfvenom and achieves…
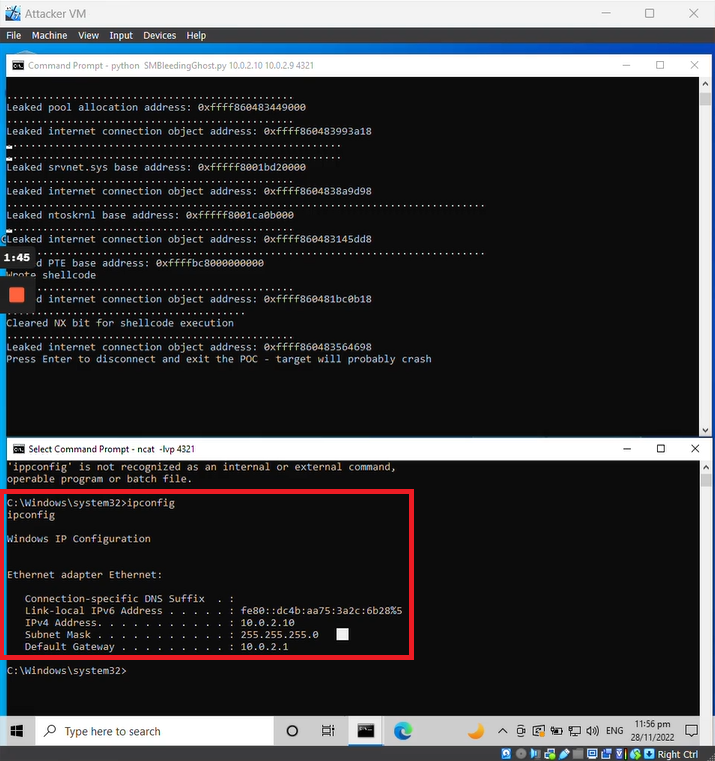 tdevworks/cve-2020-0796-smbghost-exploit-demo
Educational proof-of-concept exploit for CVE-2020-0796 (SMBGhost) demonstrating pre-auth RCE on Windows SMBv3. Includes step-by-step lab setup,…