
REx-skill
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
ai-assisted-reversingbinary-analysisbinary-exploitation+8
99
tihanyin/rex-skillREx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 sharif-dev/androidkernelvulnerability
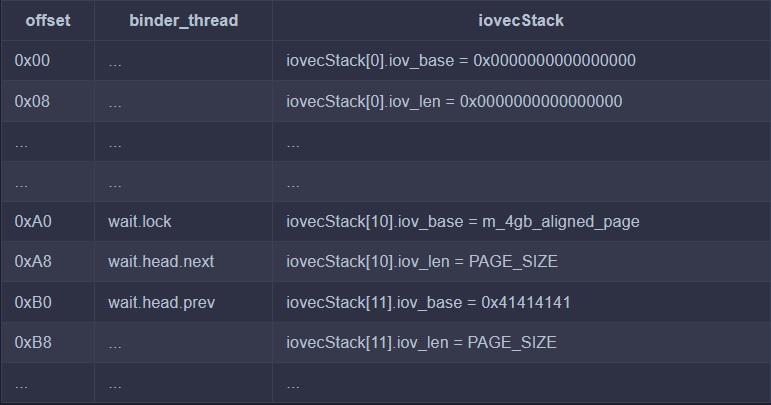
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
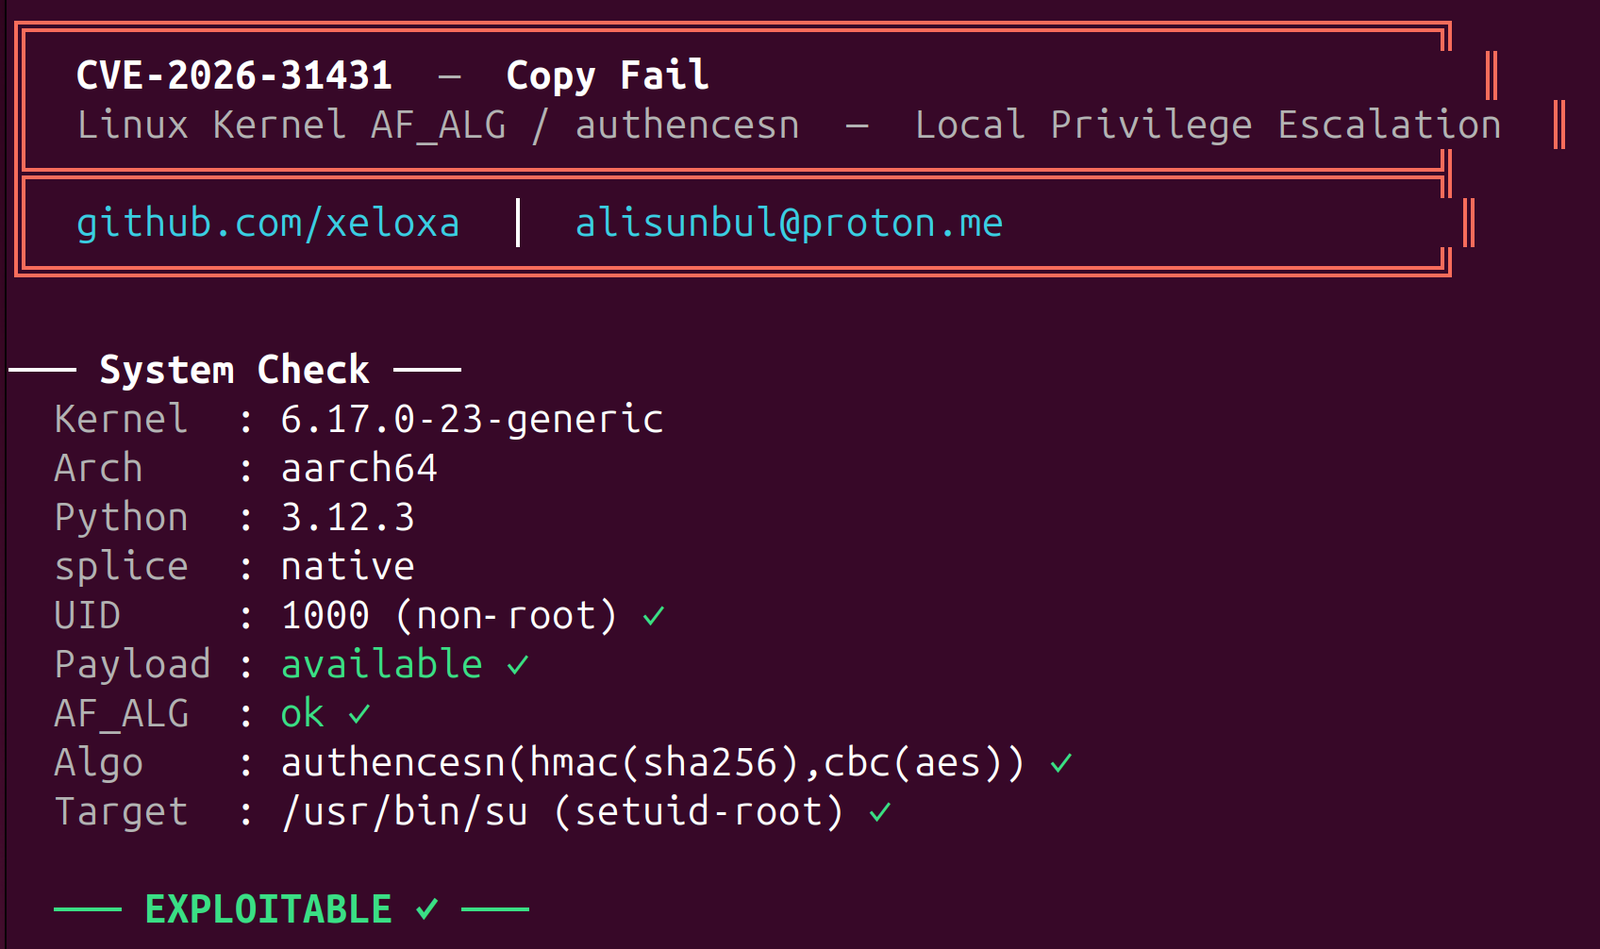 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
 hrtowii/cve-2024-23208-test
Proof-of-concept exploit for CVE-2024-23208, targeting a specific vulnerability in Apple platforms. Provides a test case for security researchers and…
 mrk336/cve-2025-26686-the-tcp-ip-flaw-that-opens-the-gates
A critical RCE vulnerability in Windows TCP/IP stack (CVE-2025-26686) leaves sensitive memory unlocked, allowing remote attackers to hijack systems.…
 freeide/cve-2021-31955-poc
Proof-of-concept exploit for CVE-2021-31955, a Windows kernel information disclosure vulnerability. Demonstrates exploitation on 64-bit systems to…
 d4rkks/cve-2025-7771-vulnerability-exploration
Escalating privilege in the system from unsigned driver using throttlestop vulnerability
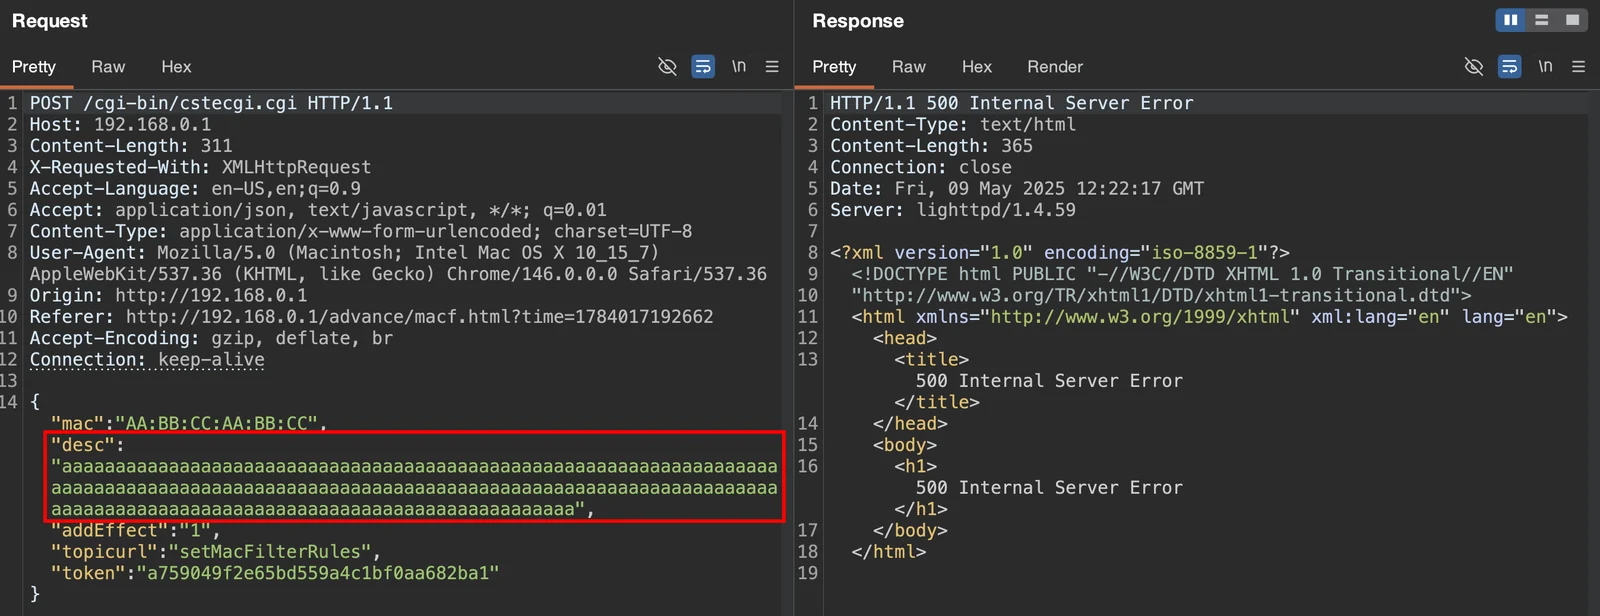 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 0xkol/ripple20-digi-connect-exploit
RCE exploit for CVE-2020-11896 (Ripple20 IP-in-IP Heap Overflow Vulnerability) targeting Digi Connect ME 9210
 dest-3/cve-2023-46012
LINKSYS AC1900 EA7500v3 IGD UPnP Stack Buffer Overflow Remote Code Execution Vulnerability
 dylvie/cve-2024-9570_d-link-dir-619l-bof
Remote buffer overflow exploit for D-Link DIR-619L router (CVE-2024-9570) targeting the formEasySetTimezone function for penetration testing and…
 keyuraghao/cve-2025-20260
Python-based exploit for CVE-2025-20260 that generates a malicious PDF file and includes core dump analysis capabilities for vulnerability…
 discordianfish/cve-2022-0185-crash-poc
Docker container that runs a crash proof-of-concept for CVE-2022-0185, a Linux kernel vulnerability. Designed for unprivileged execution to test…
 seregonwar/uaf-2023-28205
PoC CVE-2023-28205: Apple WebKit Use-After-Free Vulnerability
 eduquintanilha/cve-2022-0847-dirtypipe-exploits
C exploit collection for Linux Dirty Pipe (CVE-2022-0847) local privilege escalation, including read-only file overwriting and SUID binary hijacking,…