
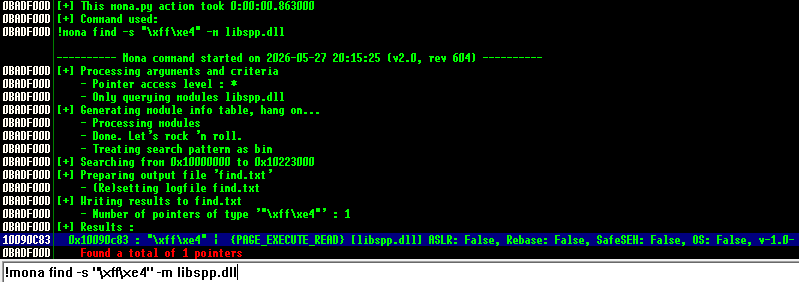
CVE-2017-14980
 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
binary-exploitationdebuggerseducation+5
1
godoy-sec/cve-2017-14980Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 sprushed/cve-2022-30292
Technical documentation and analysis of CVE-2022-30292, a heap-based buffer overflow in Squirrel 3.2 leading to denial of service, sandbox escape,…
 lsw29475/cve-2020-17057
Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.
 hunt-benito/lwip-snmpv3-stack-overflow-cve-2026-8836-critical-embedded-rce
CVE-2026-8836 — lwIP SNMPv3 stack-based buffer overflow PoC (CVSS 9.8)
 uname1able/cve-2025-21333
Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…
 fengjixuchui/cve-2009-4049
Heap-based buffer overflow in aswRdr.sys (aka the TDI RDR driver) in avast! Home and Professional 4.8.1356.0 allows local users to cause a denial of…
 0xkol/freebsd-dhclient-poc
Reproducer PoC for FreeBSD dhclient heap-based buffer overflow vulnerability when parsing DHCP option 119 (CVE-2020-7461)
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 grimmmbo/ros2_cve-2024-28231
Demonstrating the usage of Fastrtps-DDS vulnerability CVE-2024-28231 within Ros2
 trone-ux/cve-2025-22457
PoC CVE-2025-22457
 rana-ali93/cve-2021-3156-sudo-buffer-overflow-linux
Red Team exploitation of CVE-2021-3156 (Baron Samedit) – Heap Buffer Overflow in Sudo leading to Local Privilege Escalation on Ubuntu 20.04
 fengjixuchui/cve-2003-0358
By passing an overly large string when invoking nethack, it is possible to corrupt memory. jnethack and falconseye are also prone to this…
 fath0218/cve-2016-2233
Step-by-step guide to exploiting a stack-based buffer overflow in HexChat (CVE-2016-2233) with a malicious IRC server, including a patch to fix the…
 aaroncaiii/cve-2020-0796-poc
CVE-2020-0796-POC