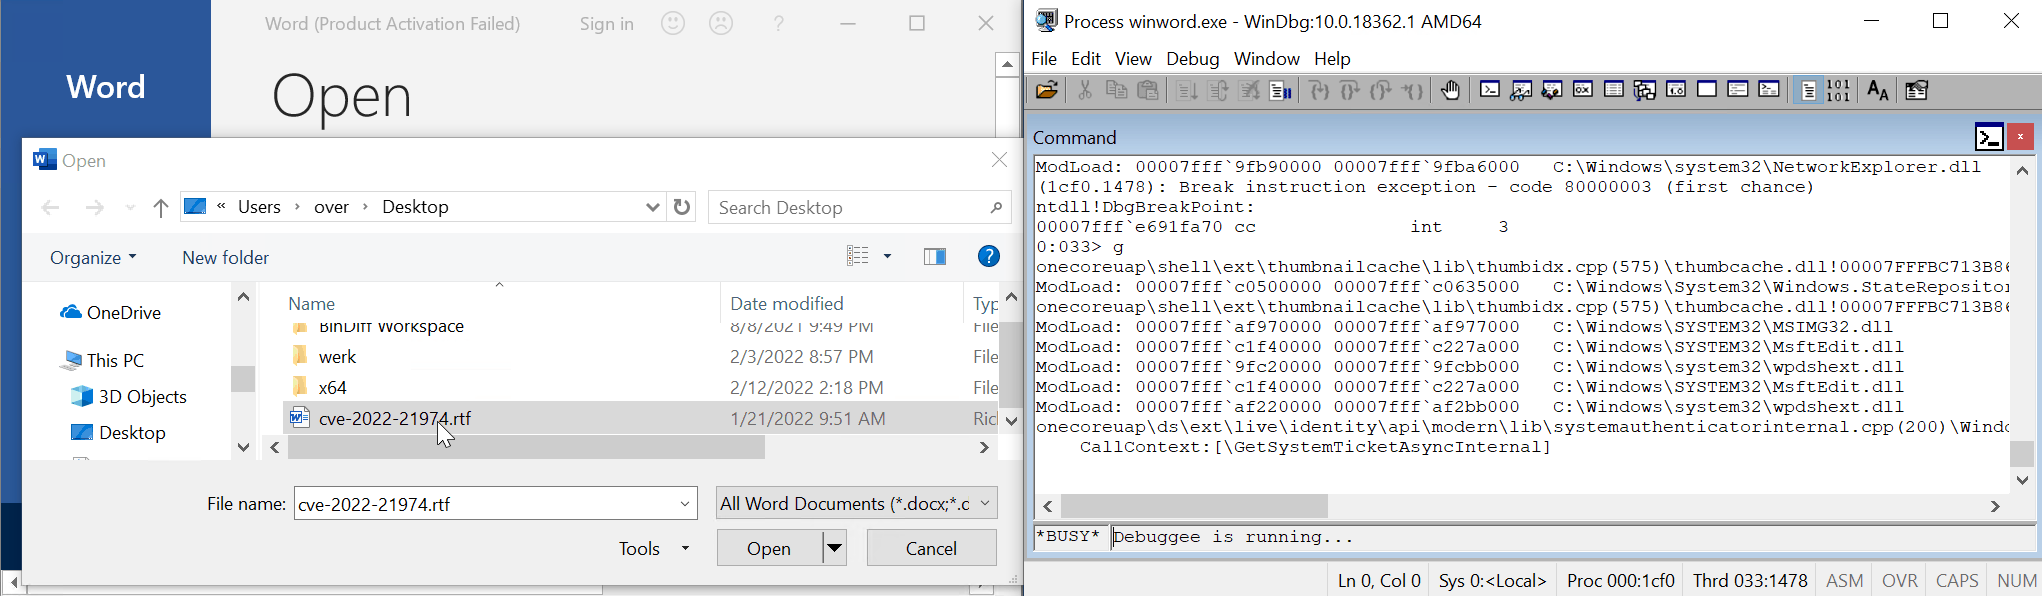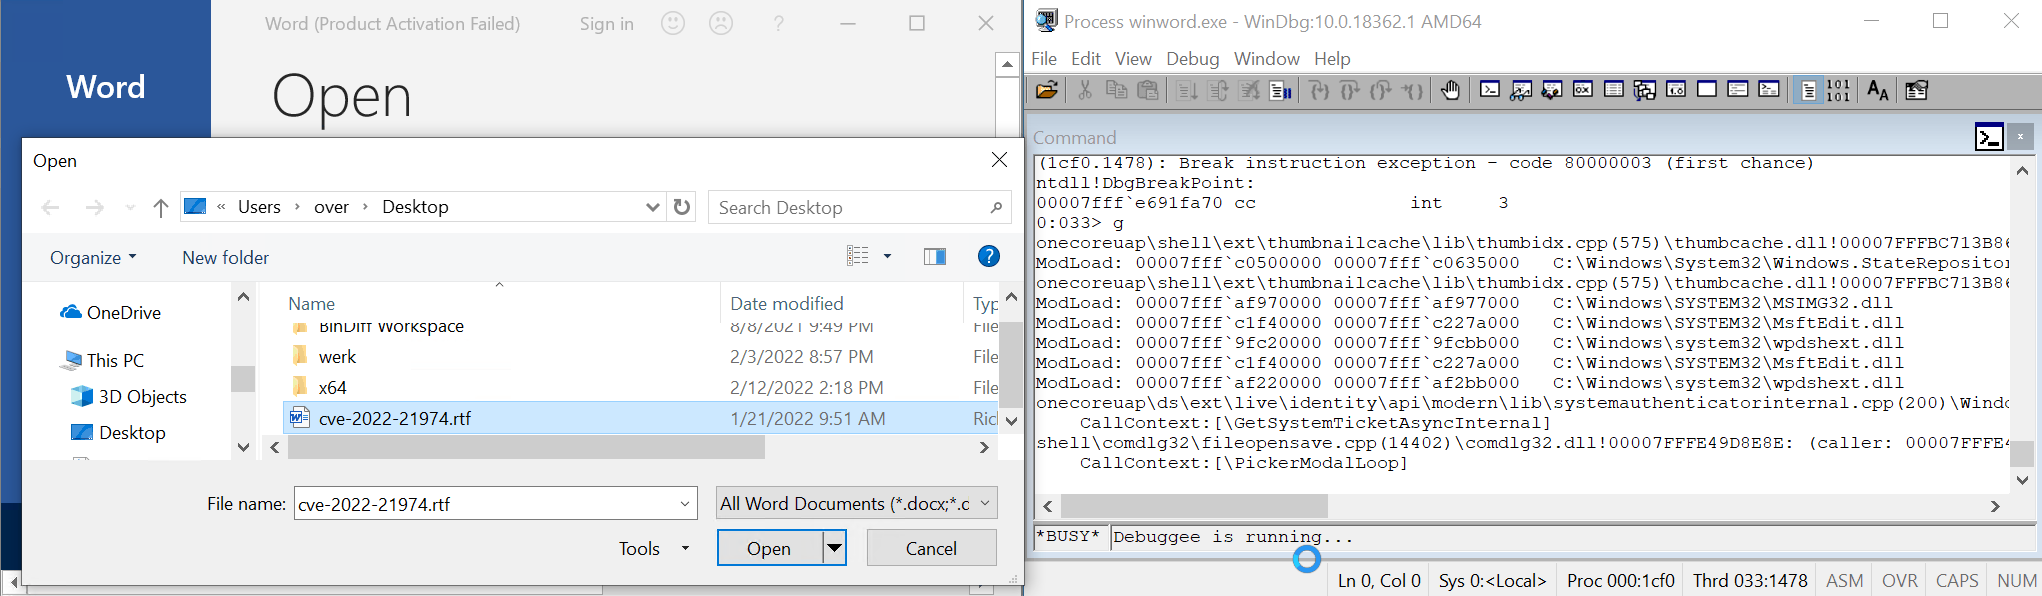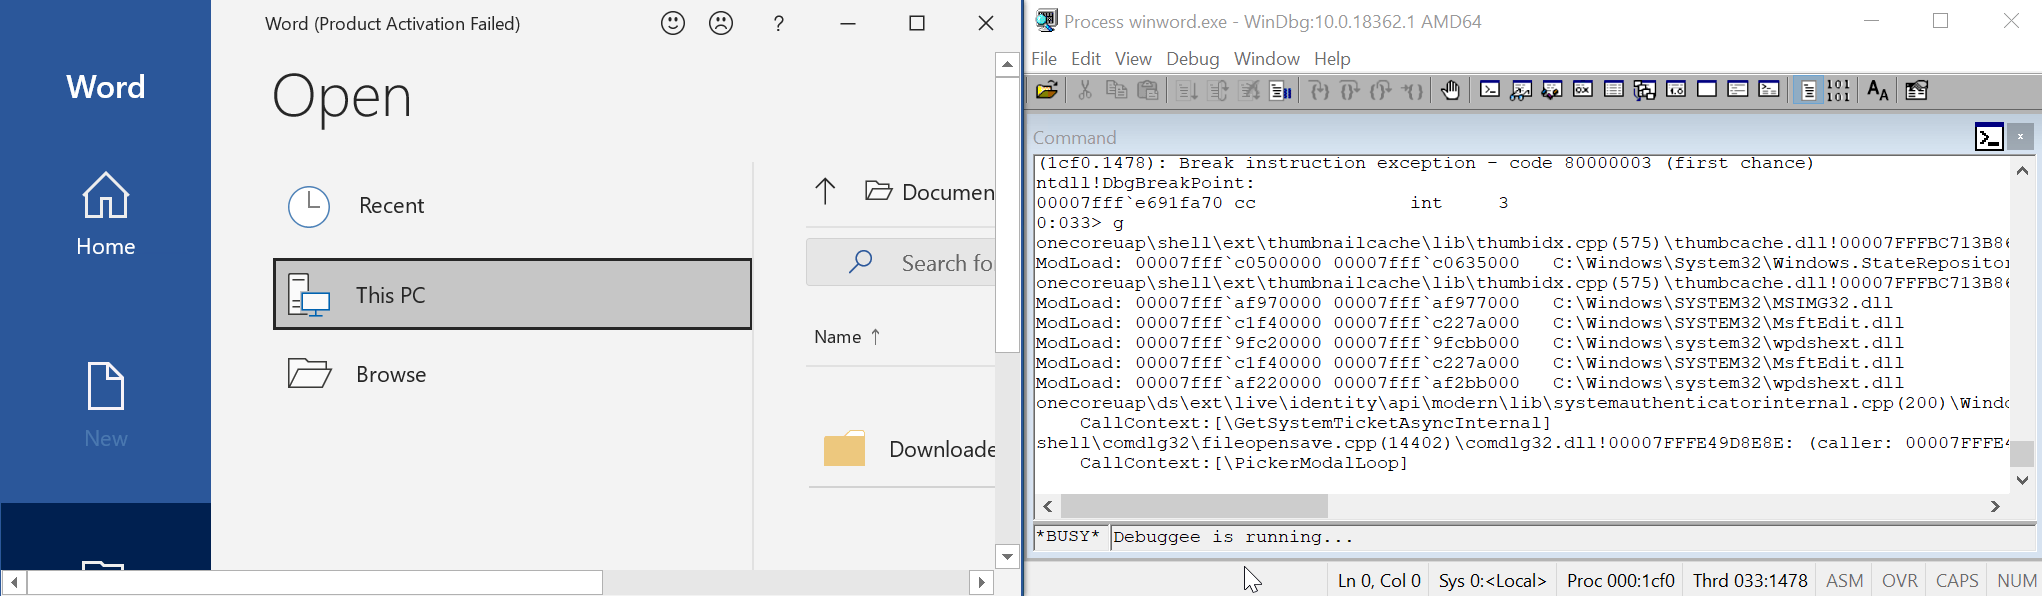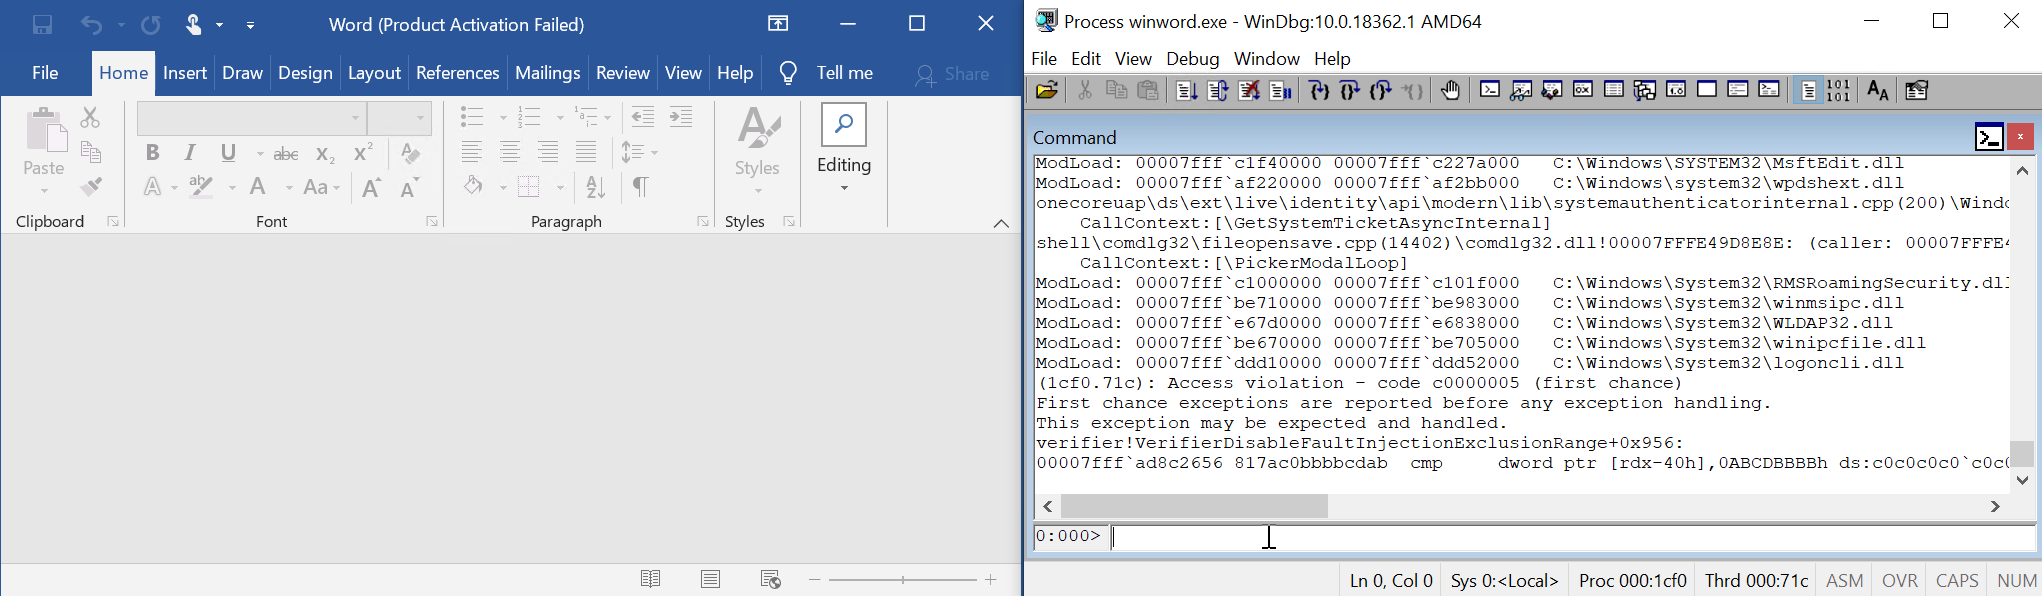
CVE-2022-21971-Windows-Runtime-RCE

Proof-of-concept exploit for CVE-2022-21971, an uninitialized pointer free vulnerability in Windows Runtime's prauthproviders.dll, triggered via…

Proof-of-concept exploit for CVE-2022-21971, an uninitialized pointer free vulnerability in Windows Runtime's prauthproviders.dll, triggered via…

CVE-2025-62215: Windows Kernel Race Condition + Double-Free EoP

Root-cause analysis of CVE-2026-54107: a use-after-free in Windows win32kfull.sys with race condition debugging, static analysis, MSRC triage…

Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.

In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…

Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…

Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…

Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…

Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…

Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…


PoC for CVE-2022-21971 "Windows Runtime Remote Code Execution Vulnerability"

PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"

Free and Open Source Reverse Engineering Platform powered by rizin

Laboratorio de análisis y explotación de la vulnerabilidad CVE-2025-5548 en FreeFloat FTP Server 1.0

Intel Management Engine JTAG Proof of Concept

IDA Pro plugin to examine the glibc heap, focused on exploit development