CVE-2026-32223-USBPrint-Exploit

Proof-of-concept exploit for CVE-2026-32223, a heap-based buffer overflow in Windows USB print driver (usbprint.sys), achieving local privilege…

Proof-of-concept exploit for CVE-2026-32223, a heap-based buffer overflow in Windows USB print driver (usbprint.sys), achieving local privilege…

CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver

Proof-of-concept exploit for CVE-2023-41993, demonstrating a WebKit vulnerability with post-exploitation techniques and binary exploitation…

CVE-2026-46331 and CVE-2026-43503

Analysis and exploitation of an use-after-free in ProFTPd

Proof-of-concept exploit for CVE-2013-2730, demonstrating a memory corruption vulnerability with a C-based implementation for security research and…

BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…

Proof-of-concept exploit for OpenSSL buffer overflow vulnerabilities CVE-2022-3602 and CVE-2022-3786, demonstrating remote code execution via crafted…

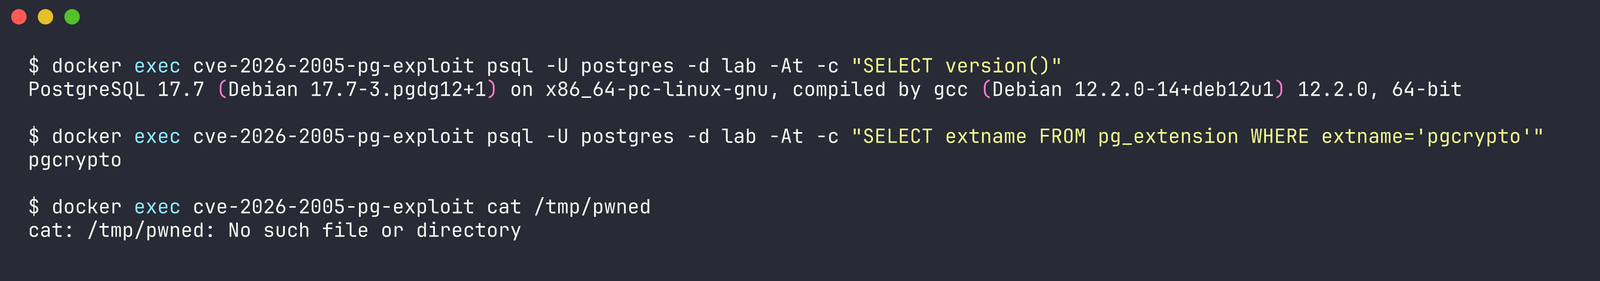
Exploit for CVE-2026-2005, a heap overflow in PostgreSQL's pgcrypto extension leading to remote code execution. Includes PoC generators, Docker lab,…

Local privilege escalation exploit for CVE-2026-3888 targeting snap-confine and systemd-tmpfiles on Ubuntu, providing SUID and capabilities variants…

Exploit for CVE-2018-3252 targeting WebLogic deserialization vulnerability. Includes payload generation with ysoserial and a Python proof-of-concept…

Proof-of-concept exploit for CVE-2020-16152: LFI-to-RCE in Aerohive/Extreme Networks HiveOS via PHP string truncation and log poisoning, enabling…

Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…

Proof-of-concept exploit for Android kernel privilege escalation vulnerability CVE-2015-6640, demonstrating the flaw and providing a reference for…

Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…

Technical analysis and proof-of-concept demonstrating a bypass of Linux kernel Spectre-BTI user-space mitigations via prctl and seccomp, with…

Educational examples porting Linux kernel vulnerabilities to Rust, featuring intentionally vulnerable code and exploits for learning kernel security…

PoC demonstrating dyld as a PAC signing oracle via hand-crafted Mach-O chained fixups on arm64e, achieving controlled PAC-valid pointer writes and…