
CVE-2020-3433
 goichot/cve-2020-3433
PoCs and technical analysis for three Cisco AnyConnect Windows vulnerabilities: local privilege escalation (CVE-2020-3433), denial of service…
binary-exploitationexploitationpayload-development+2
41
goichot/cve-2020-3433PoCs and technical analysis for three Cisco AnyConnect Windows vulnerabilities: local privilege escalation (CVE-2020-3433), denial of service…
 jjensn/cve-2024-36877
Proof-of-concept exploit for CVE-2024-36877 targeting firmware vulnerabilities, with detailed write-up and binary exploitation techniques.
 zeusbox/cve-2021-21017
Proof-of-concept exploit for Adobe Reader type confusion leading to heap overflow, with detailed root-cause analysis and detection guidance.
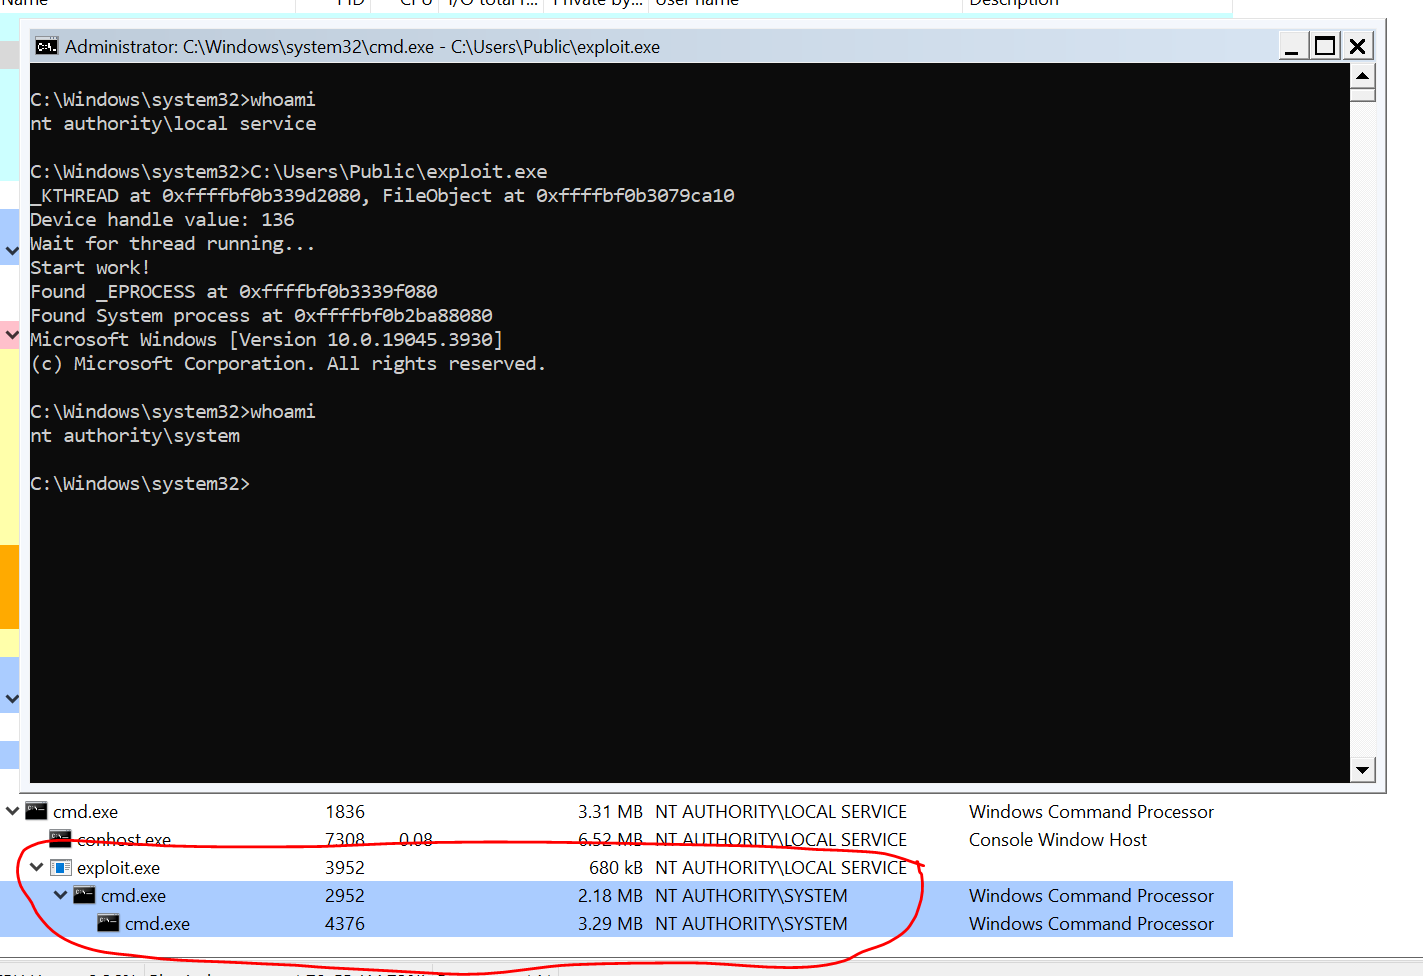 tykawaii98/cve-2024-21338_poc
Proof-of-concept exploit for CVE-2024-21338, a kernel vulnerability. Demonstrates exploitation technique for security research and vulnerability…
 uoftctf/uoftctf-2025-chals-public
Challenge handouts, source code, and solutions for UofTCTF 2025
 sam-b/hacksysdriverexploits
Windows kernel driver exploits for HackSys Extreme Vulnerable Driver, demonstrating binary exploitation and privilege escalation for security…
 es0j/execaslr-ekoparty
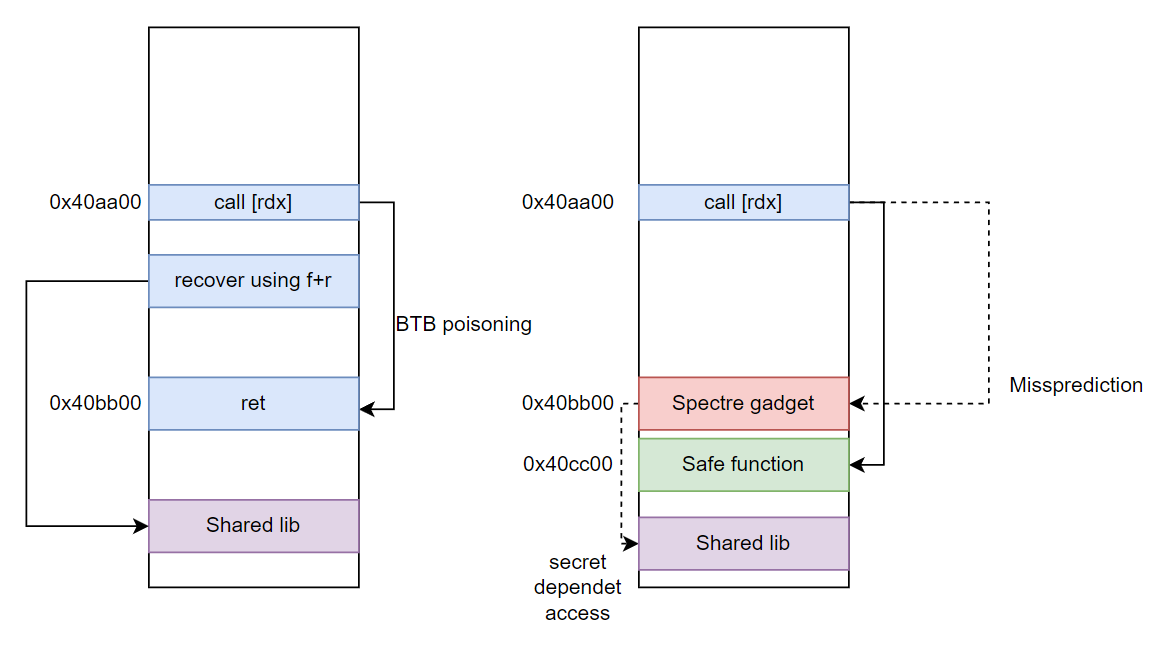
Proof-of-concept exploit that bypasses ASLR on Intel CPUs by abusing branch target buffer and speculative execution to leak randomized addresses via…
 jas502n/cve-2020-17008
Proof-of-concept exploit for CVE-2020-17008, demonstrating splWOW64 elevation of privilege via heap manipulation on Windows 10 and Server.
 knight0x07/winrar-code-execution-vulnerability-cve-2023-38831
Educational analysis of WinRAR code execution vulnerability CVE-2023-38831, covering exploitation mechanics and mitigation strategies through…
 kleiton0x00/rtlhijack
Alternative Read and Write primitives using Rtl* functions the unintended way.
 exploitblizzard/windows-privilege-escalation-cve-2021-1732
C++ exploit for CVE-2021-1732 targeting Windows privilege escalation on Win10 1803-20H2 and Server 2019/2004. Provides kernel-level elevation of…
 mistymntncop/cve-2022-4262
Exploit for CVE-2022-4262, a Chromium browser vulnerability. Includes references to official bug report, in-the-wild exploit analysis, and root cause…
 0xshe/cve-2026-31431
Kernel privilege escalation exploit for CVE-2026-31431, abusing AF_ALG interface to overwrite /bin/su and spawn a root shell. Includes C…
 thoxy67/zig-pe
Reflective PE loader written in Zig. Loads and executes native and .NET PE files directly from memory.
 bitdefender/swapgs-attack-poc
This repository contains the sources and documentation for the SWAPGS attack PoC (CVE-2019-1125)
 apkc/cve-2024-26229-bof
BOF implementations of CVE-2024-26229 for Cobalt Strike and BruteRatel
 imbas007/cve-2026-42533
Exploit for nginx heap buffer overflow (CVE-2026-42533) providing pre-auth RCE via two-pass capture clobbering. Includes info leak, heap spray, and…
 chenaotian/cve-2022-0185
CVE-2022-0185 POC and Docker and Analysis write up