
cve-2014-7920-7921
 laginimaineb/cve-2014-7920-7921
Exploit code for CVE-2014-7920 and CVE-2014-7921 - code-exec in mediaserver up to Android 5.1
android-securitybinary-exploitationexploitation+2
76
laginimaineb/cve-2014-7920-7921Exploit code for CVE-2014-7920 and CVE-2014-7921 - code-exec in mediaserver up to Android 5.1
 villager1314/cve-2026-64560-analysis
Linux kernel UAF analysis for CVE-2026-64560 with race-triggering PoC, patch review, affected LTS/Android version matrix, and self-check for patched…
 nhh9905/cve-2026-62735
Proof-of-concept for CVE-2026-62735, an integer overflow in http.sys leading to heap overflow and SYSTEM shell. Includes crash log and stack trace…
 dinosn/mariadb-13-rce-lab
MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…
 giancarlolelli/quantum
This repository contains the code and submission detail for the QDay prize challenge by https://www.projecteleven.com/
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
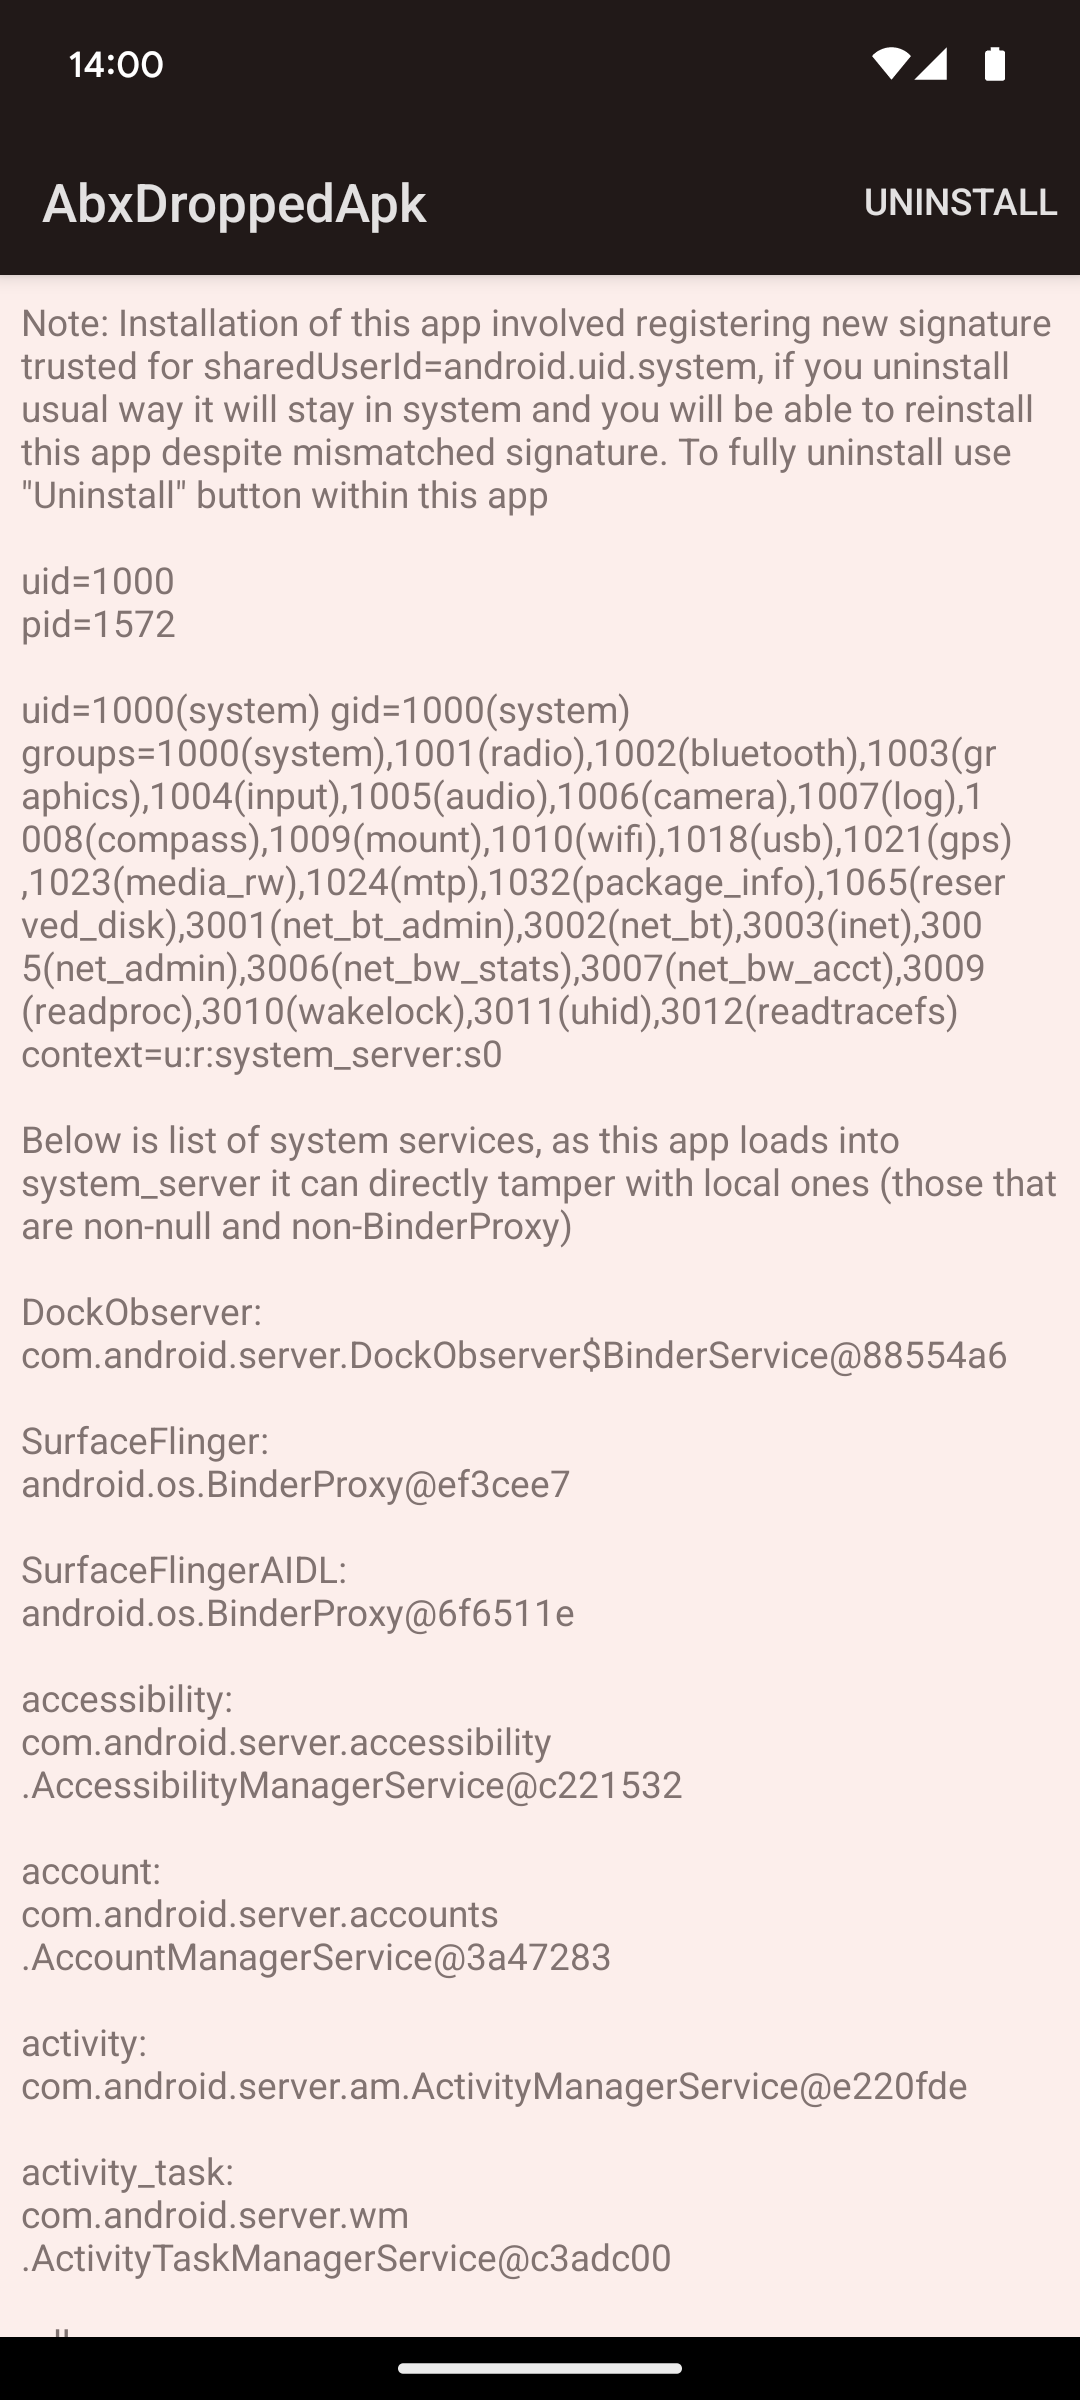 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 febinrev/dirtypipez-exploit
Local privilege escalation exploit for Linux kernel vulnerability CVE-2022-0847 (Dirty Pipe), allowing non-privileged users to overwrite data in…
 kiks7/cve-2022-2602-kernel-exploit
C exploit for CVE-2022-2602, a use-after-free in the Linux kernel's io_uring subsystem, enabling local privilege escalation through file descriptor…
 yuanlink/cve-2022-26809
PoC and analysis for CVE-2022-26809, a Windows RPC runtime integer overflow vulnerability. Includes trigger scripts using PetitPotam-style UNC path…
 flankerhqd/mediacodecoob
Infoleak and PC control poc for CVE-2015-6620 (24445127), I'll add after conference
 crixpwn/cve-2026-8389
Technical analysis and proof-of-concept exploit for CVE-2026-8389, a SpiderMonkey BaselineJIT type confusion vulnerability in Firefox, demonstrated…
 gamesarchive/cve-2025-48543
Proof-of-concept exploit for CVE-2025-48543, written in C++. Demonstrates exploitation of a specific vulnerability for security testing and research…
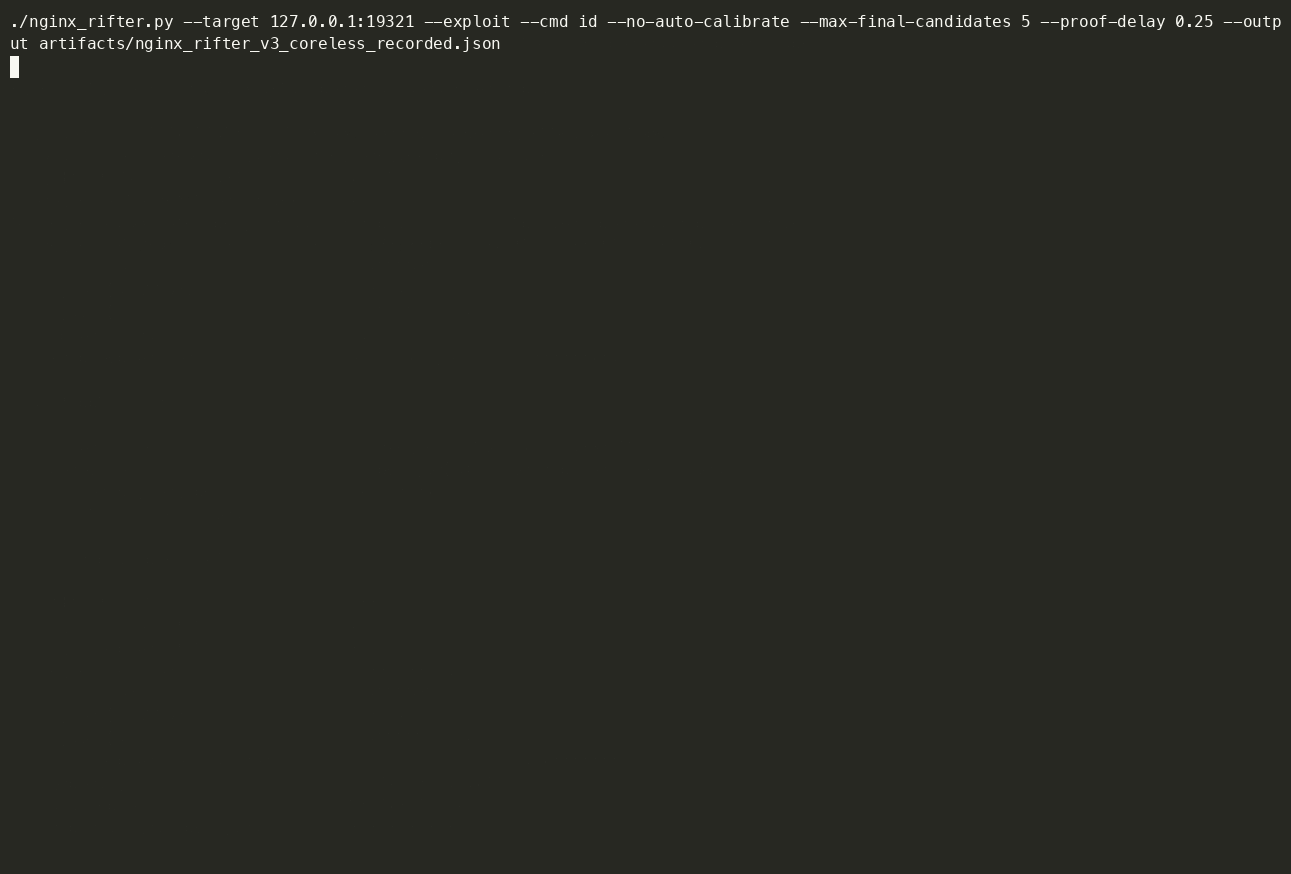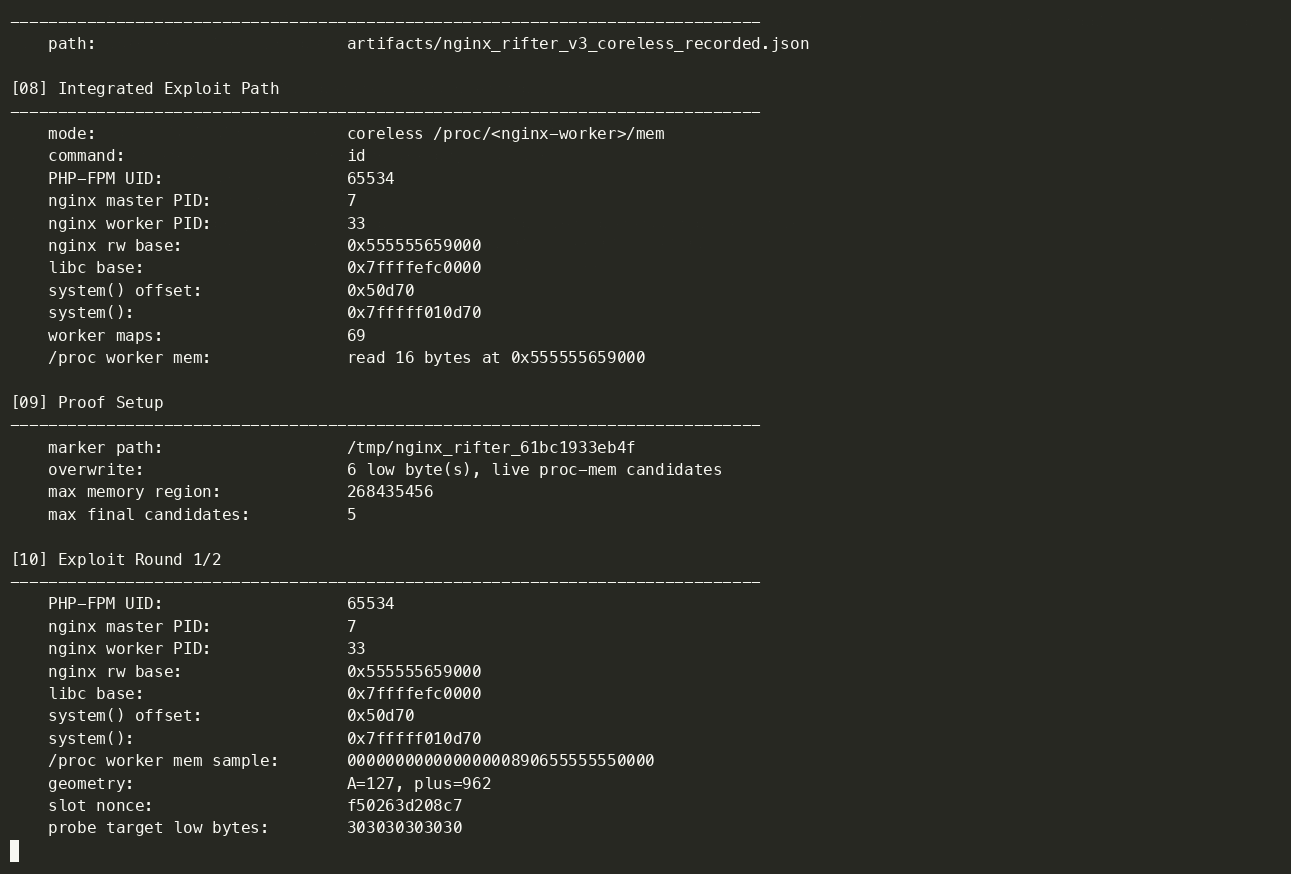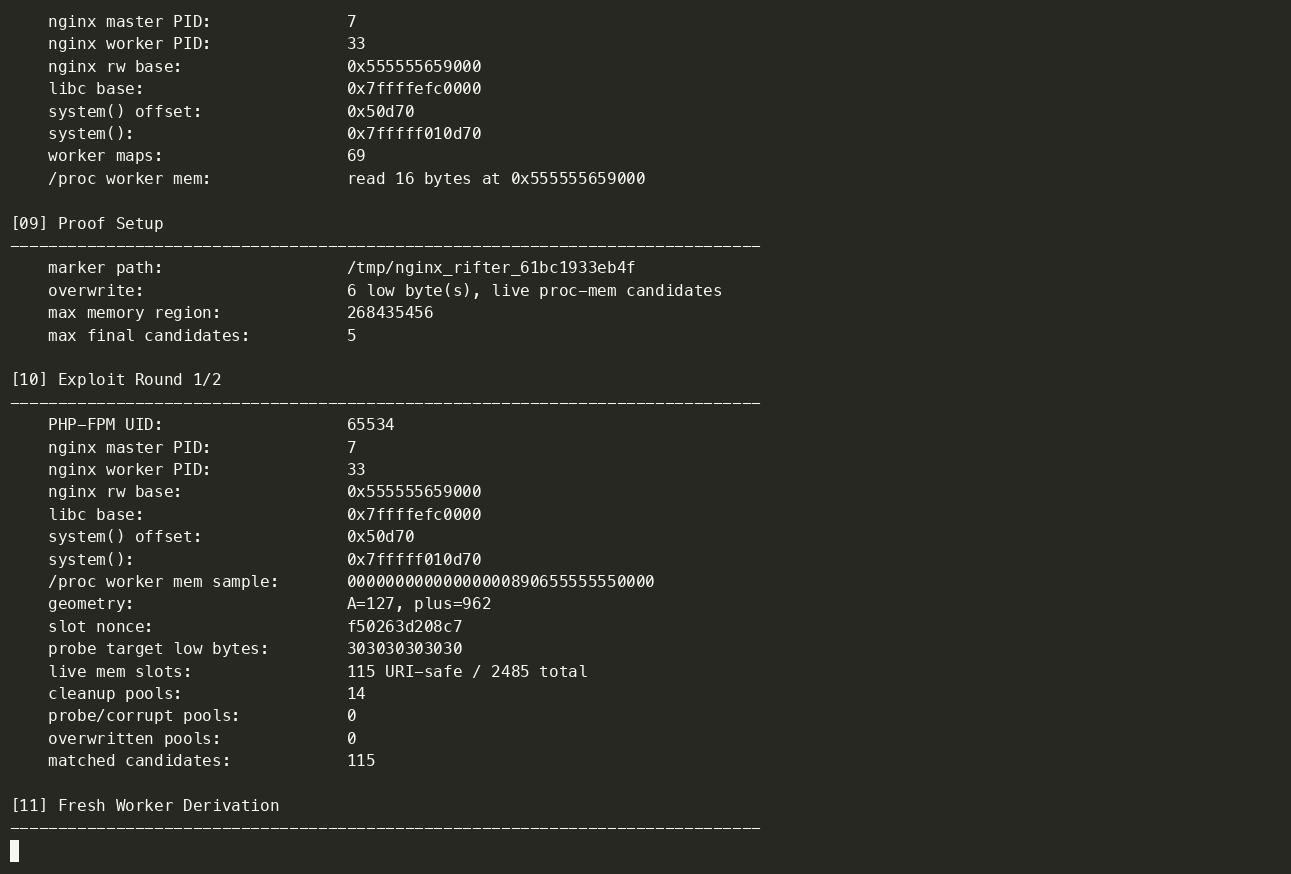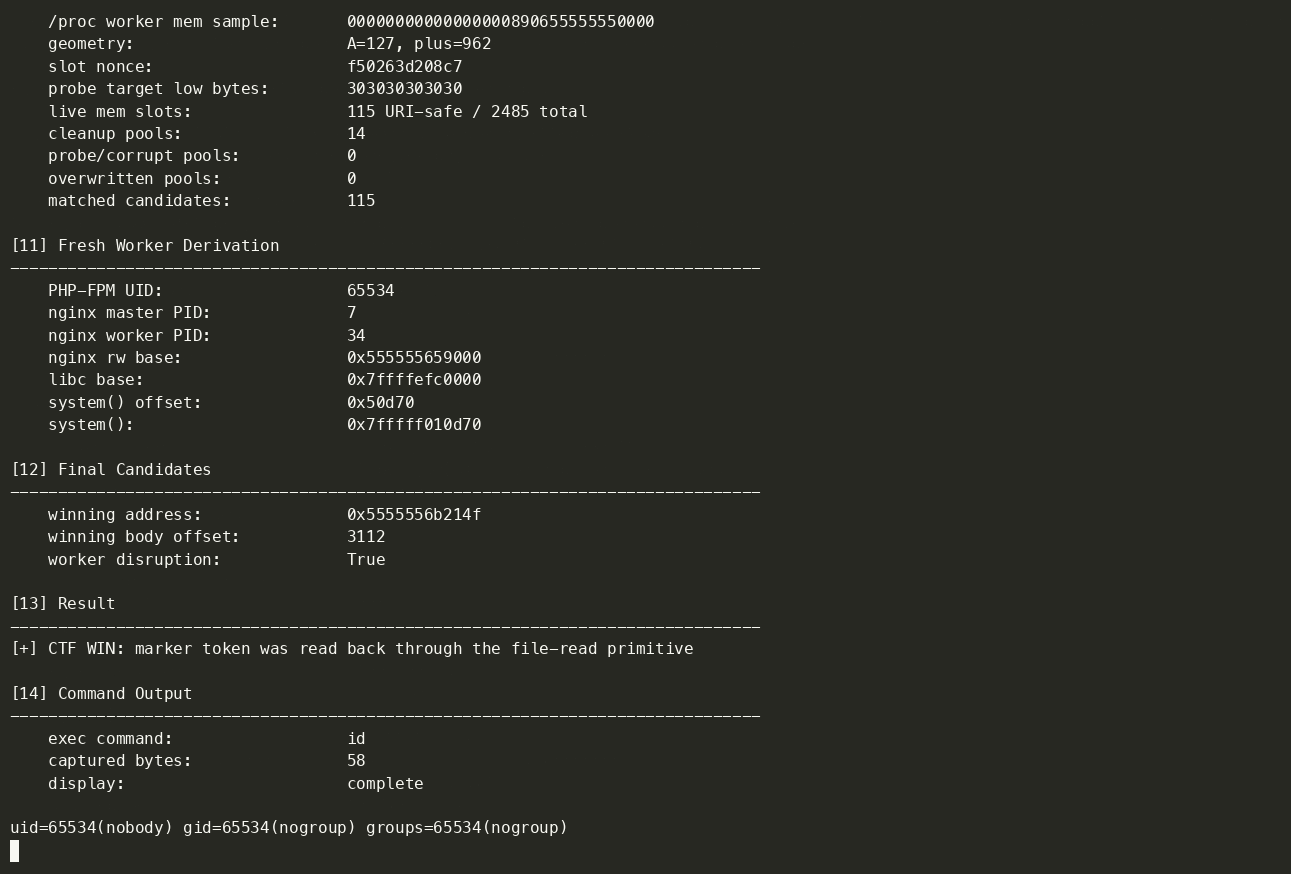 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 exploits-forsale/cve-2024-26218
Proof-of-concept exploit for CVE-2024-26218, demonstrating a specific vulnerability for security research and testing.
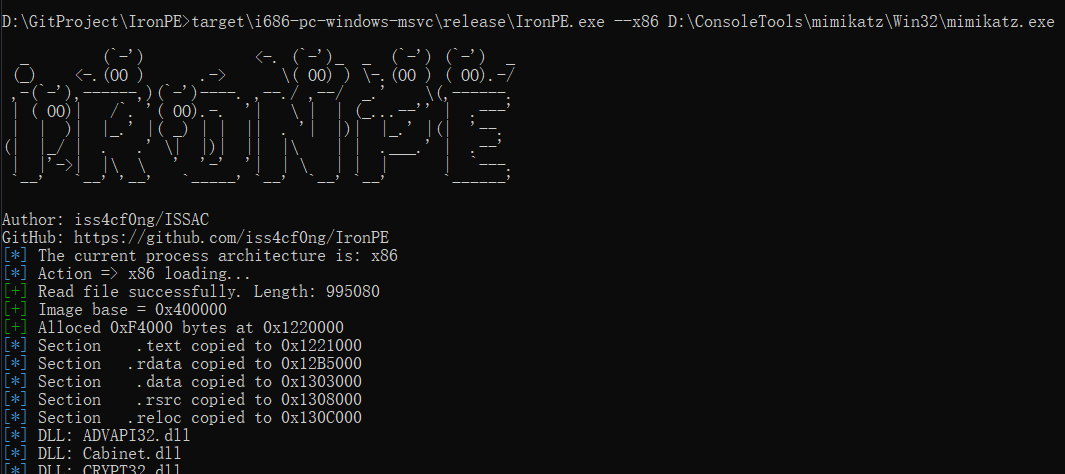 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 geekben/towelroot
Research of CVE-2014-3153 and its famous exploit towelroot on x86
 3gstudent/cve-2017-8464-exp
Support x86 and x64