
vucsa
 warxim/vucsa
Deliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…
binary-exploitationctfeducation+3
102
warxim/vucsaDeliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…
 petergabaldon/cve-2024-7479_cve-2024-7481
TeamViewer User to Kernel Elevation of Privilege PoC. CVE-2024-7479 and CVE-2024-7481. ZDI-24-1289 and ZDI-24-1290. TV-2024-1006.
 realtalk/cve-2013-2094
original cve-2013-2094 exploit and a rewritten version for educational purposes
 renorobert/virtualbox-cve-2018-2844
C-based proof-of-concept exploit for VirtualBox CVE-2018-2844, demonstrating a heap overflow vulnerability in the hypervisor's network driver for…
 chenaotian/cve-2023-0386
Local privilege escalation exploit for CVE-2023-0386 targeting Linux kernel overlayfs. Includes detailed vulnerability analysis, PoC code, and…
 quarkslab/cve-2020-0069_poc
Proof-of-concept exploit for CVE-2020-0069 on Mediatek Android devices, enabling kernel memory read/write and syscall hooking for privilege…
 rlarabee/exploits
C-language exploit code collection focused on vulnerability research, proof-of-concept development, and offensive security testing.
 gdbinit/mach_race
Local privilege escalation exploit for macOS (CVE-2016-1757) using Mach IPC race condition to bypass SIP and SUID protections, targeting multiple OS…
 j4nn/cve-2020-0041
Local privilege escalation exploit for Android kernel vulnerability CVE-2020-0041, with portability across devices and kernel versions.
 0xeb-bp/cve-2020-1054
Rust implementation of a Windows 7 x64 local privilege escalation exploit for CVE-2020-1054; compiles via Cargo and executes to elevate privileges.
 fortra/cve-2024-6769
Technical writeup and PoC for CVE-2024-6769, chaining DLL hijacking with activation cache poisoning to escalate from medium to high integrity on…
 binarygolf/bggp
Annual small file competition repository with binary golf challenges across themes like polyglots, crashes, self-replication, and downloads,…
 exploits-forsale/cve-2024-21345
Proof-of-concept exploit for CVE-2024-21345, demonstrating a specific vulnerability with functional code for security testing and validation.
 bw3ll/jop_rocket
This framework enables user to discover JOP gagdets and can automate building a complete JOP chain to bypass DEP. JOP ROCKET is the ultimate solution…
 s1ckb017/poc-cve-2022-26809
PoC for CVE-2022-26809, analisys and considerations are shown in the github.io.
 anyaschukin/override
Binary Exploitation and Reverse-Engineering (from assembly into C)
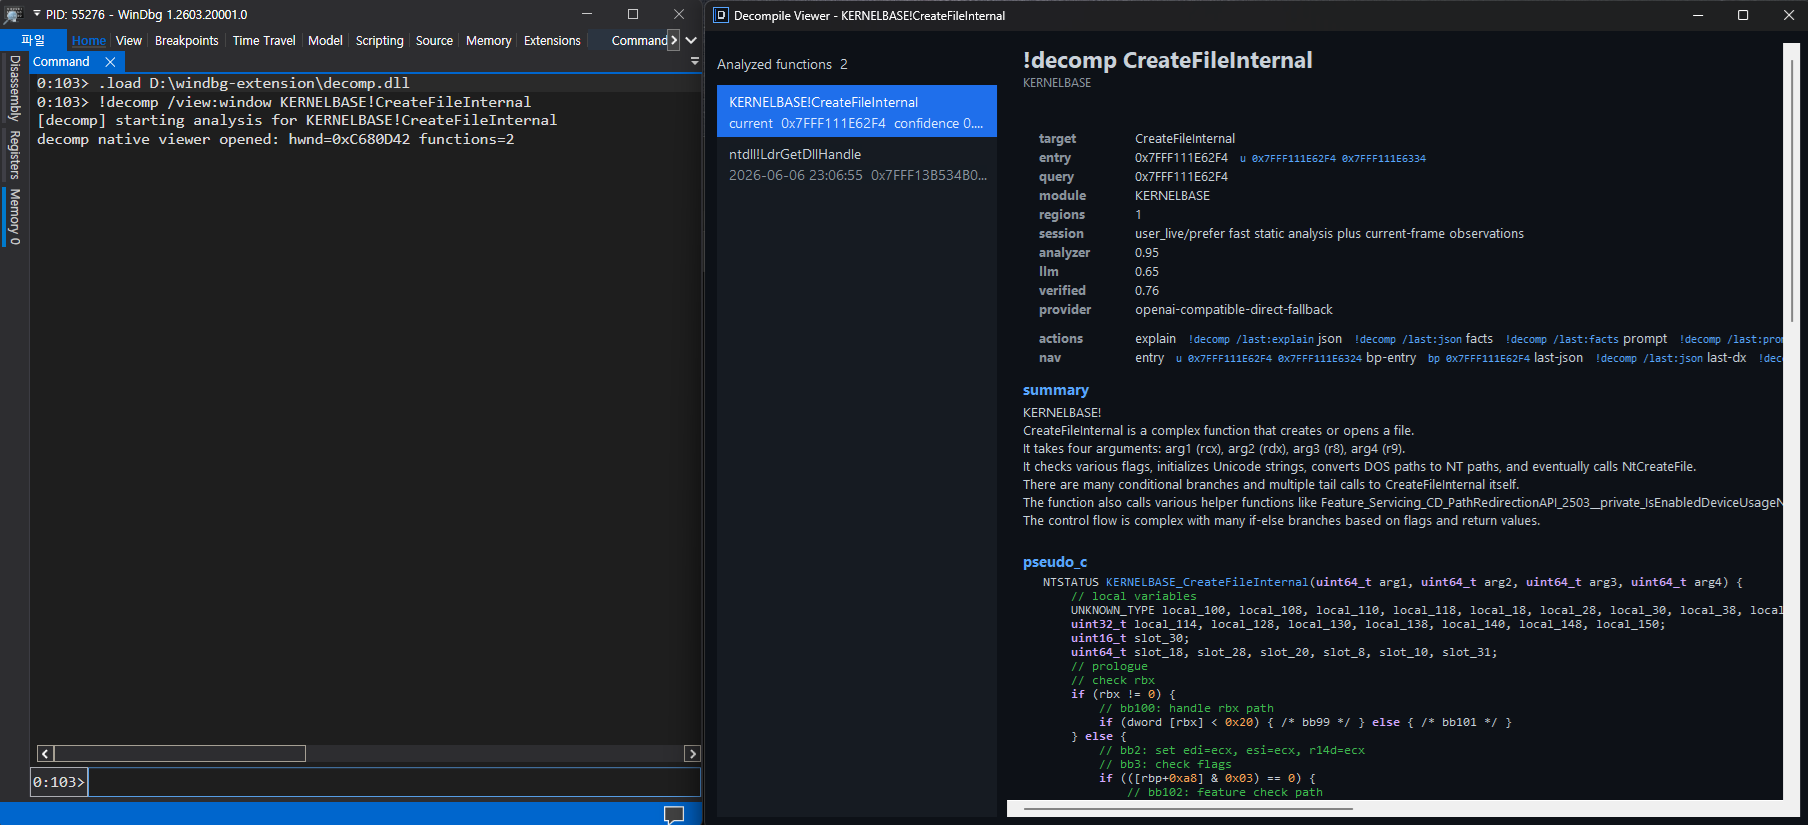 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…