
CVE-2022-22715
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
binary-exploitationexploitationpapers-research+2
vportal/cve-2022-22715Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 dbgbgtf1/cve-2026-40369-exploit
Exploit for CVE-2026-40369 that leverages kernel address leak and token forging to achieve privilege escalation in a browser sandbox environment.
 davidcarliez/cve-2026-66804-crossdevice-lpe
Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…
 uname1able/cve-2025-21333
Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…
 mein-0/cve-2026-0828
Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
 0xgunrunner/cve-2024-26229-bof
CVE-2024-26229 Beacon Object File version
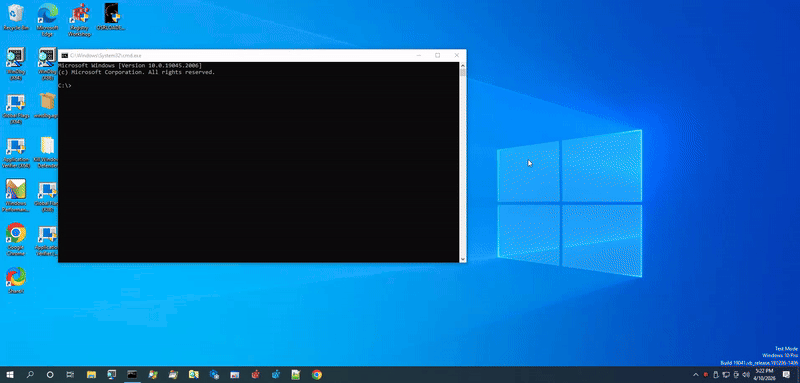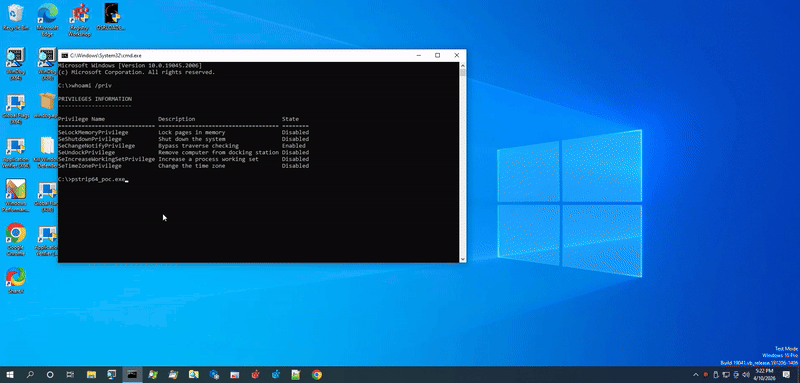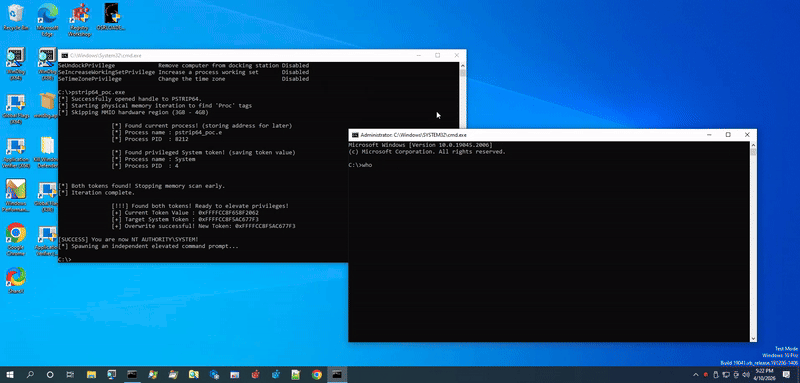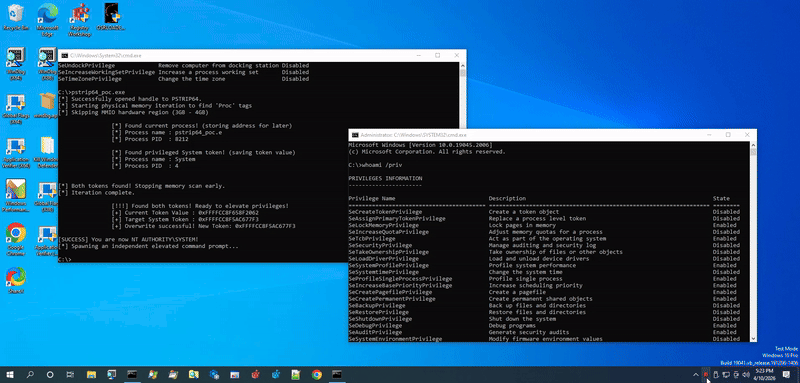 athenasec16/cve-2026-29923
Proof-of-concept exploit for CVE-2026-29923, a BYOVD privilege escalation in pstrip64.sys. Demonstrates physical memory read/write via IOCTL to steal…
 xvalegendary/hvcipwned
CVE-2024-35250 demonstrates that HVCI is not a defense against data-only kernel exploits. As long as a driver bug provides an arbitrary R/W…
 cwjchoi01/cve-2025-65264
Proof-of-concept exploit for CVE-2025-65264 demonstrating arbitrary kernel memory read via IOCTL in CPU-Z driver, enabling token theft and potential…
 ethanedits/iqvw64e-privilege-escalation
Educational proof-of-concept for CVE-2015-2291 local privilege escalation via Intel Ethernet driver IOCTL abuse, demonstrating arbitrary kernel…
 teodor1231241/demo-proof-of-concept-temporal-memory-inconsistency-in-cldflt.sys-cve-2025-62221
Proof-of-concept demonstrating a use-after-free in cldflt.sys (CVE-2025-62221) that enables local privilege escalation to SYSTEM via kernel pool…
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 avielzecharia/cve-2015-5736
PoC for CVE-2015-5736
 bananoname/cve-2024-49138-poc
Proof-of-concept exploit for CVE-2024-49138 in Windows CLFS.sys, achieving local privilege escalation to system shell via token manipulation.
 apeppels/cve-2022-37017
Bypass for Symantec Endpoint Protection's Client User Interface Password
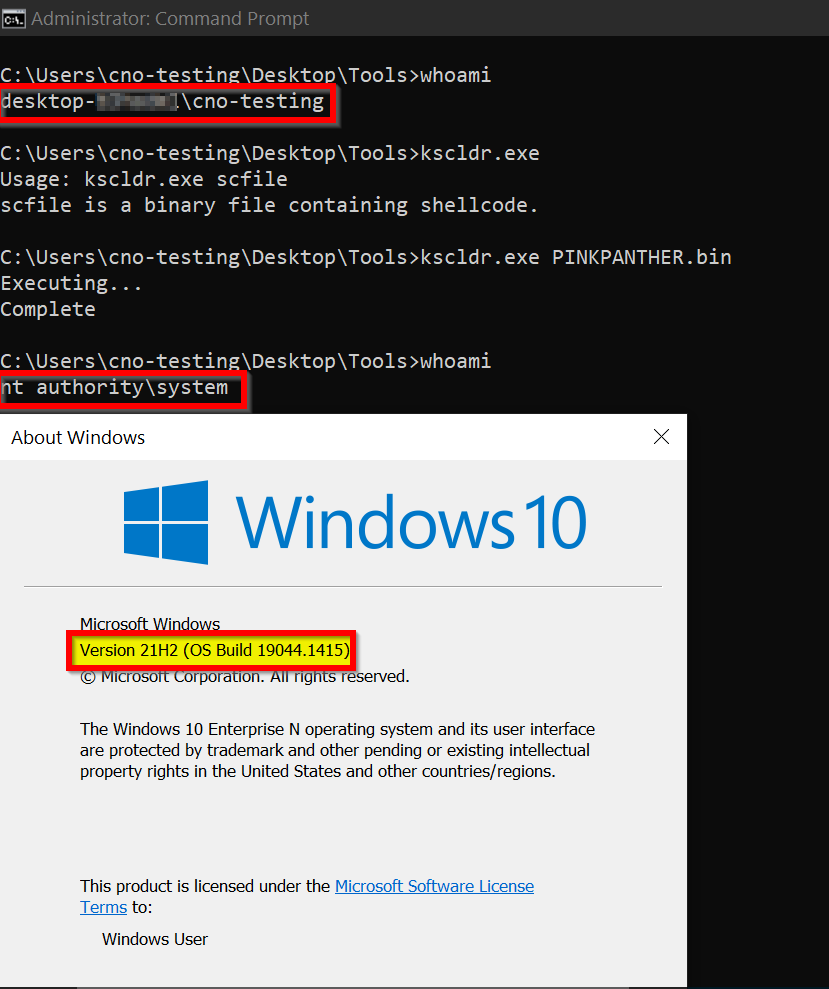 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 threedr3am/learnjavabug
Java安全相关的漏洞和技术demo,原生Java、Fastjson、Jackson、Hessian2、XML反序列化漏洞利用和Spring、Dubbo、Shiro、CAS、Tomcat、RMI、Nexus等框架\中间件\功能的exploits以及Java Security…