
CVE-2026-2005
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
binary-analysisbinary-exploitationdatabase-security+4
open-flaw/cve-2026-2005PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
 califio/publications
Curated collection of security research papers, CVE exploit writeups, reverse-engineering analyses of Apple internals, and commissioned security…
 george0papasotiriou/cve-2026-2222-mqtt-broker-connect-packet-heap-overflow
Demonstrates CVE-2026-2222 heap overflow in MQTT CONNECT packet handling with a simulated vulnerable broker and proof-of-concept exploit code for…
 jelasin/cve-2026-41089
Pre-auth PoC for CVE-2026-41089 Netlogon CLDAP stack overflow via UDP/389, triggering LSASS crash/DC reboot. Includes exploit script, root-cause…
 0xabcd01/cve-2026-41089
CVE-2026-41089 PoC — Netlogon CLDAP stack buffer overflow (CVSS 9.8 CRITICAL)
 vital-information-resource-under-siege/cve-2026-38698-and-cve-2026-38699
Technical details and publication about CVE-2026-38698 and CVE-2026-38699
 damariion/cve-2018-6537.rce
A buffer overflow vulnerability in the control protocol of Flexense SyncBreeze Enterprise v10.4.18 allows remote attackers to execute arbitrary code…
 mrk336/cve-2025-27480
CVE-2025-27480 exposes a buffer overflow in OpenSSH 8.9p1 via a malformed SSH_USERAUTH packet. Attackers can inject shellcode and gain SYSTEM-level…
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 yaldobaoth/cve-2015-1578-poc
This is a proof-of-concept exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation leads to remote…
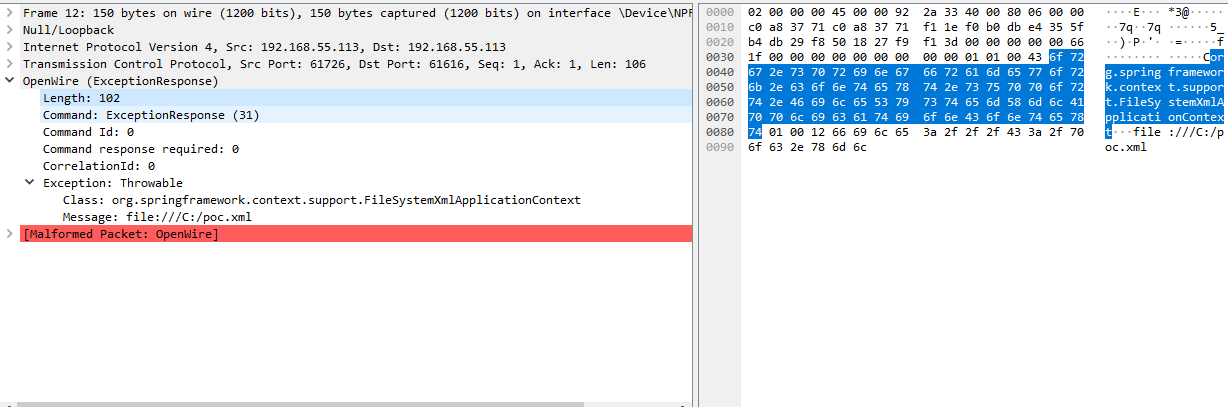 skrkcb2/cve-2023-46604
In-depth technical analysis of CVE-2023-46604, an RCE vulnerability in Apache ActiveMQ's OpenWire protocol, including packet structure breakdown and…
 ownouwa/cve-2024-23113-poc
CVE-2024-23113 是一个在 Linux Kernel 中被发现的漏洞,它属于 任意代码执行漏洞,影响了 bpf (Berkeley Packet Filter) 子系统。具体来说,这个漏洞影响了 bpf 程序的 bpf_prog 类型的对象,并且可以允许攻击者通过构造恶意的 BPF…
 jfrog/jfrog-cve-2023-25136-openssh_double-free
Proof-of-concept exploit triggering a double-free vulnerability (CVE-2023-25136) in OpenSSH 9.1p1, causing a denial-of-service crash via pre-auth…
 anldori/cve-2017-7308
CVE-2017-7308 POC
 szymonh/rndis-co
CVE-2022-25375 - Demo exploit of RNDIS USB Gadget
 foxtrot/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a Wi-Fi vulnerability, leveraging libwifi for packet parsing and crafted for educational purposes.