

pwndbg
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
ai-assisted-reversingbinary-analysisbinary-exploitation+12
pwndbg/pwndbgExploit Development and Reverse Engineering with GDB & LLDB Made Easy
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.
 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
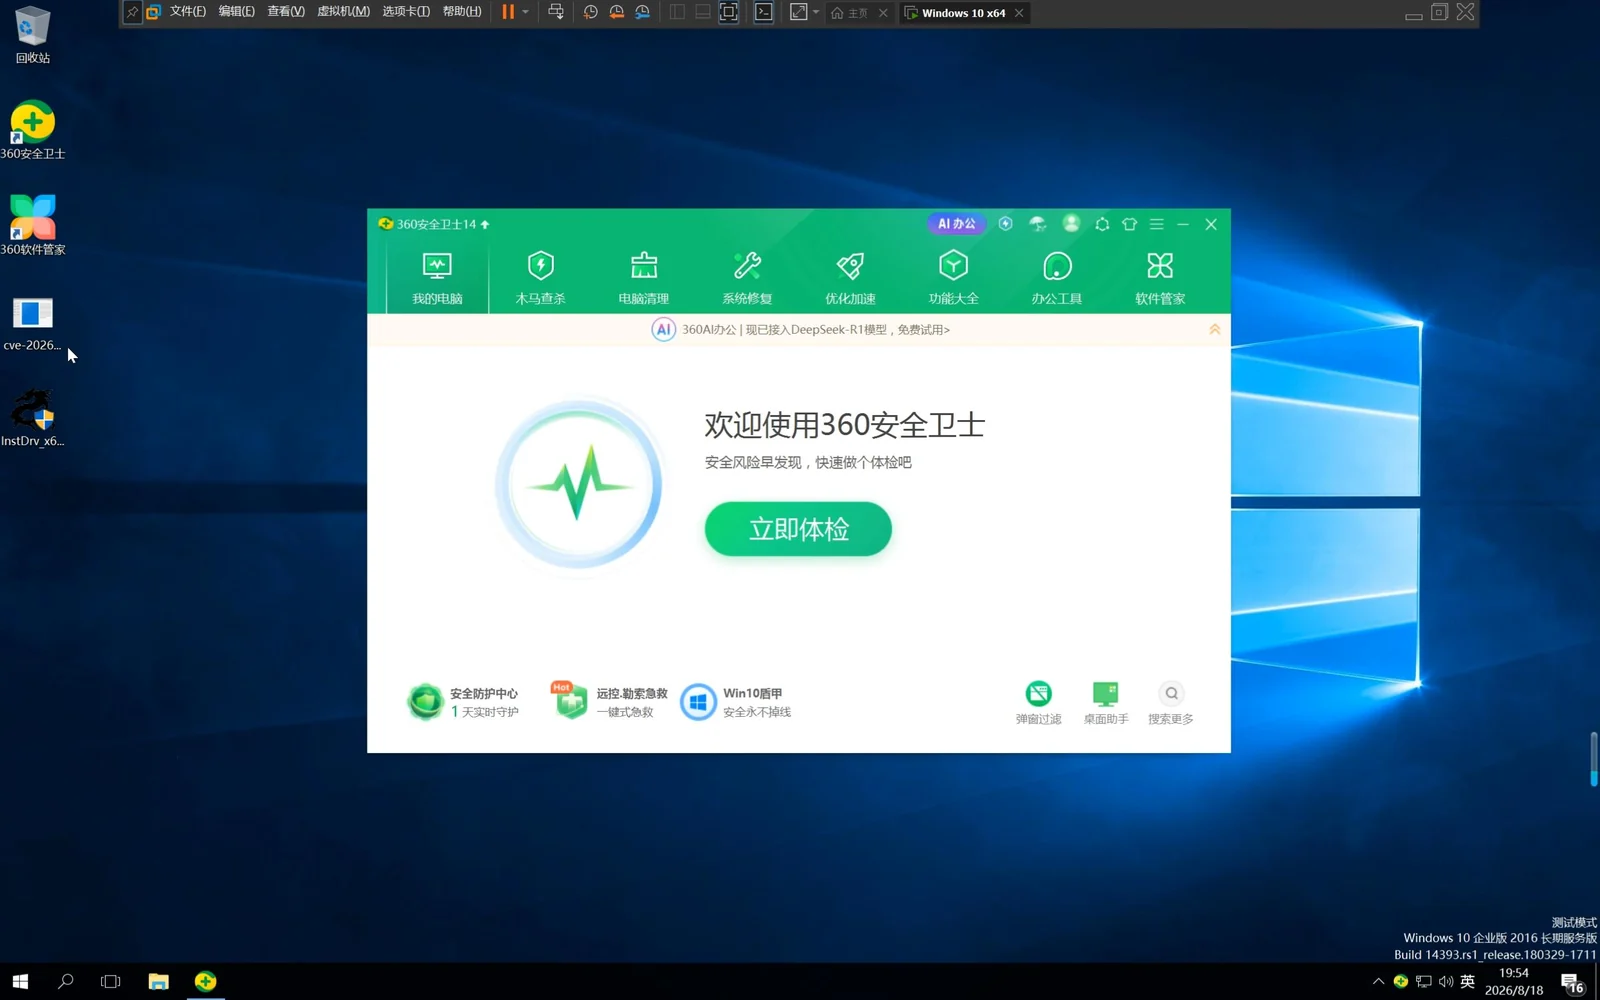 gongchuang1089/edrkiller
Use cve-2026-36425 killer edr,360 can killer
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
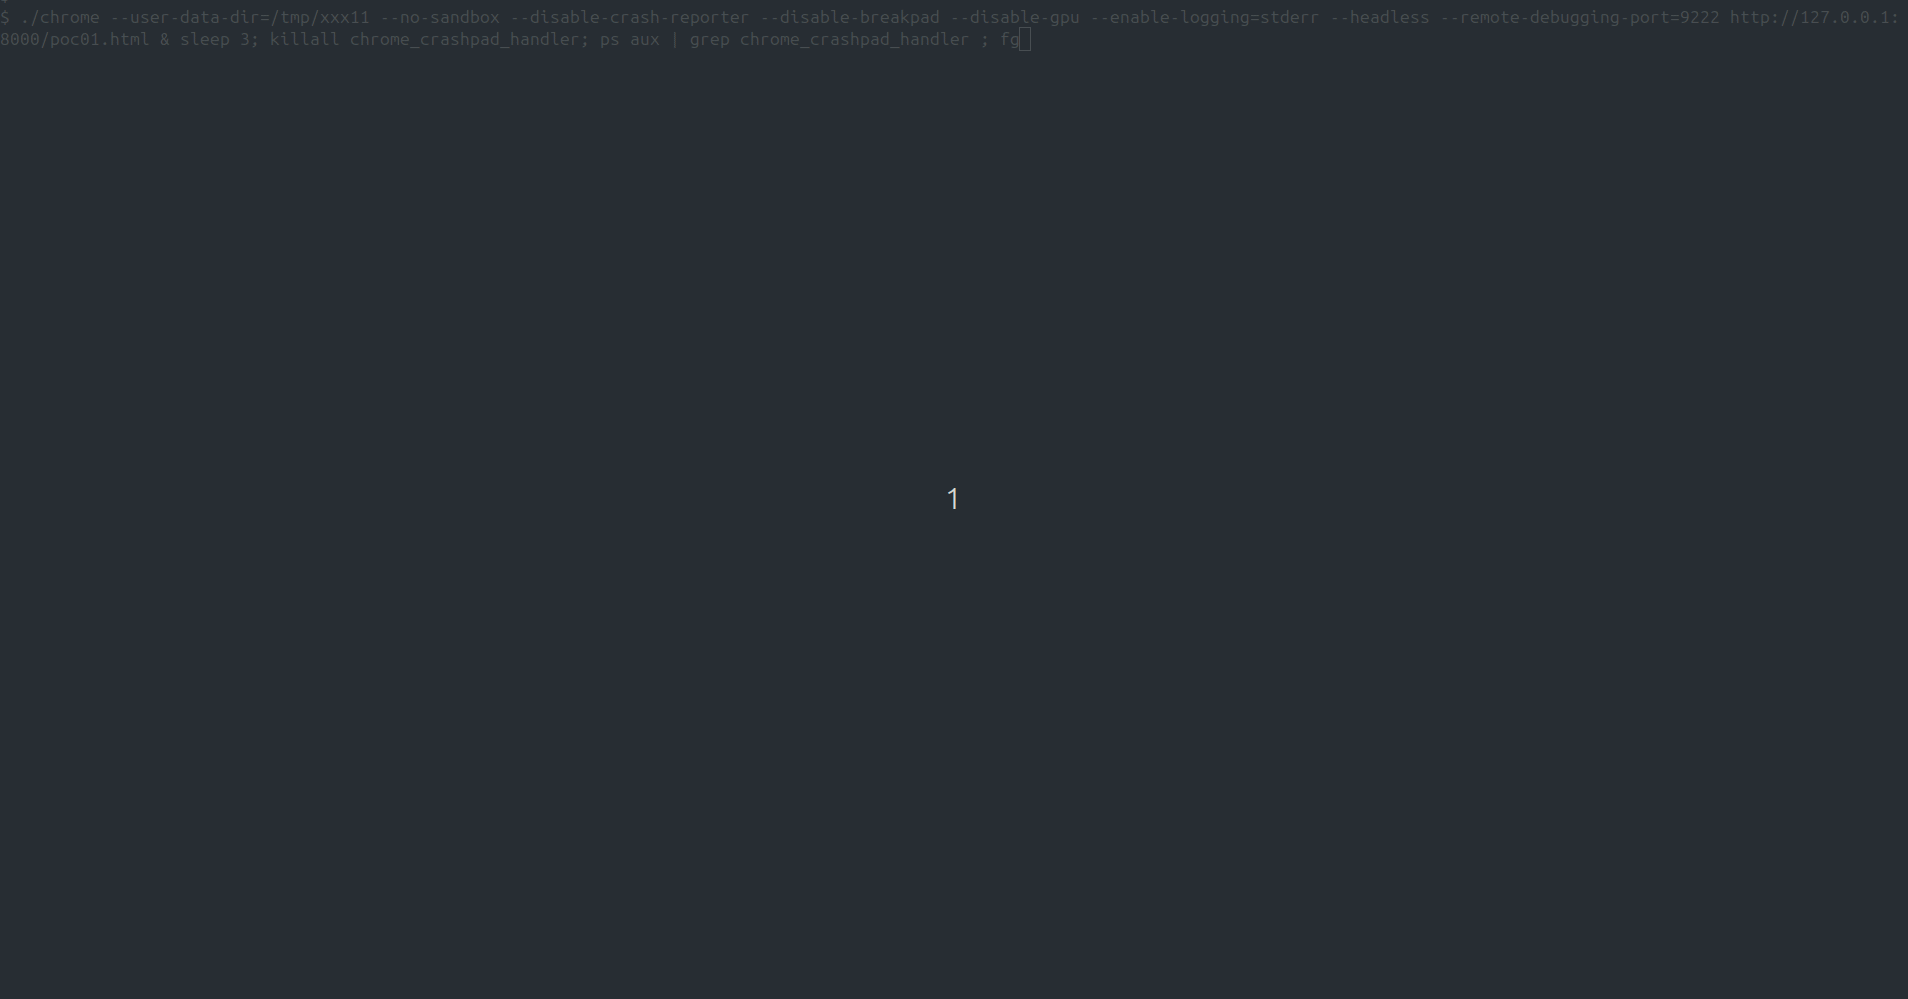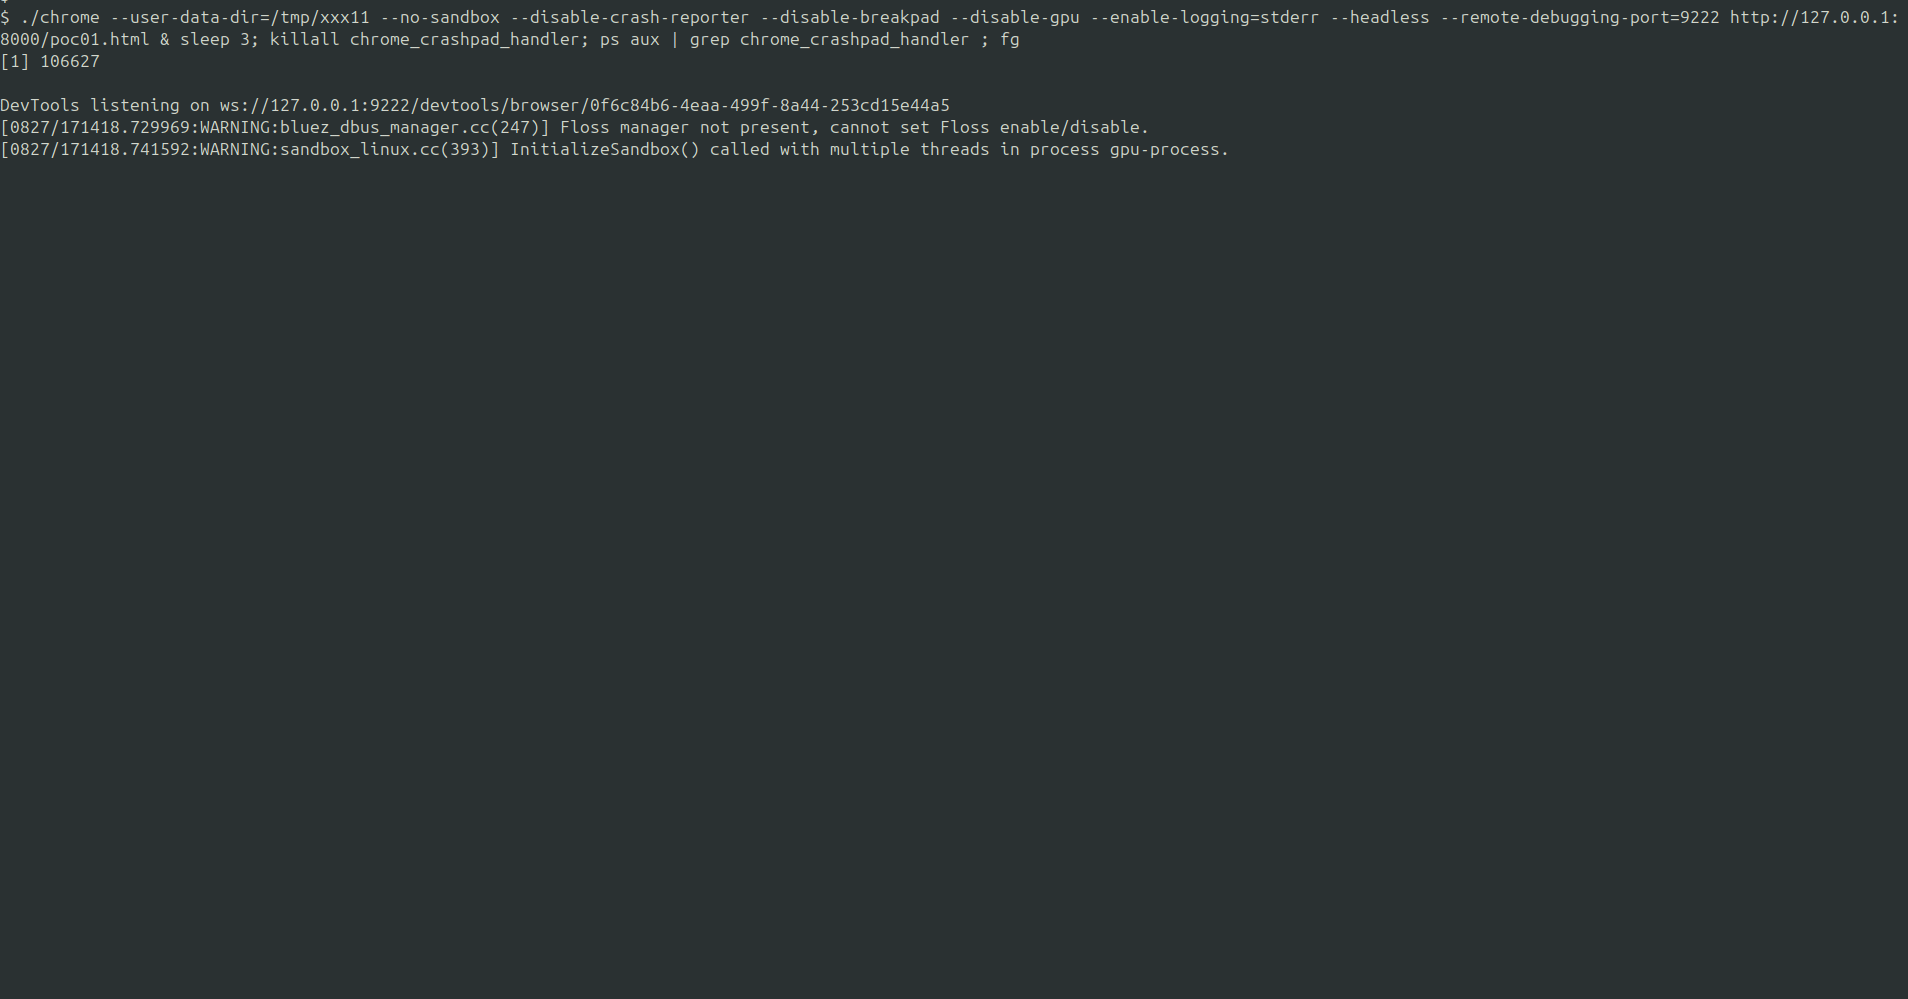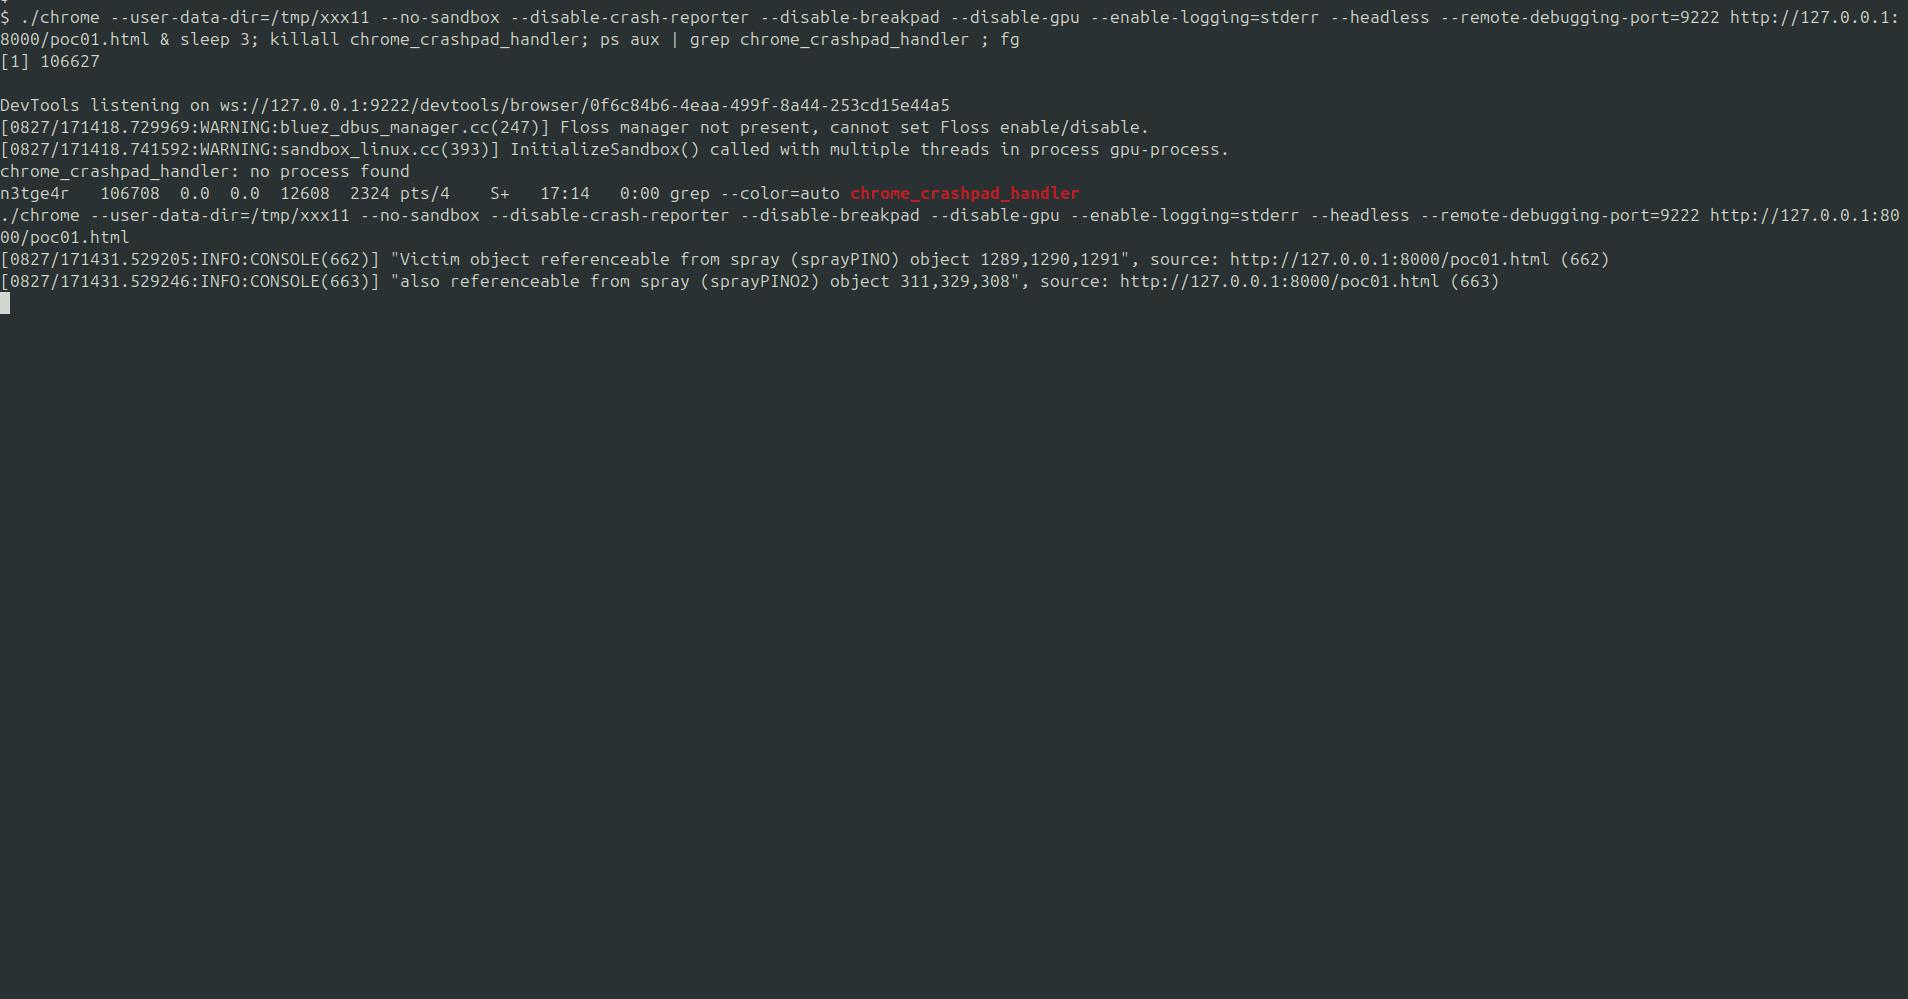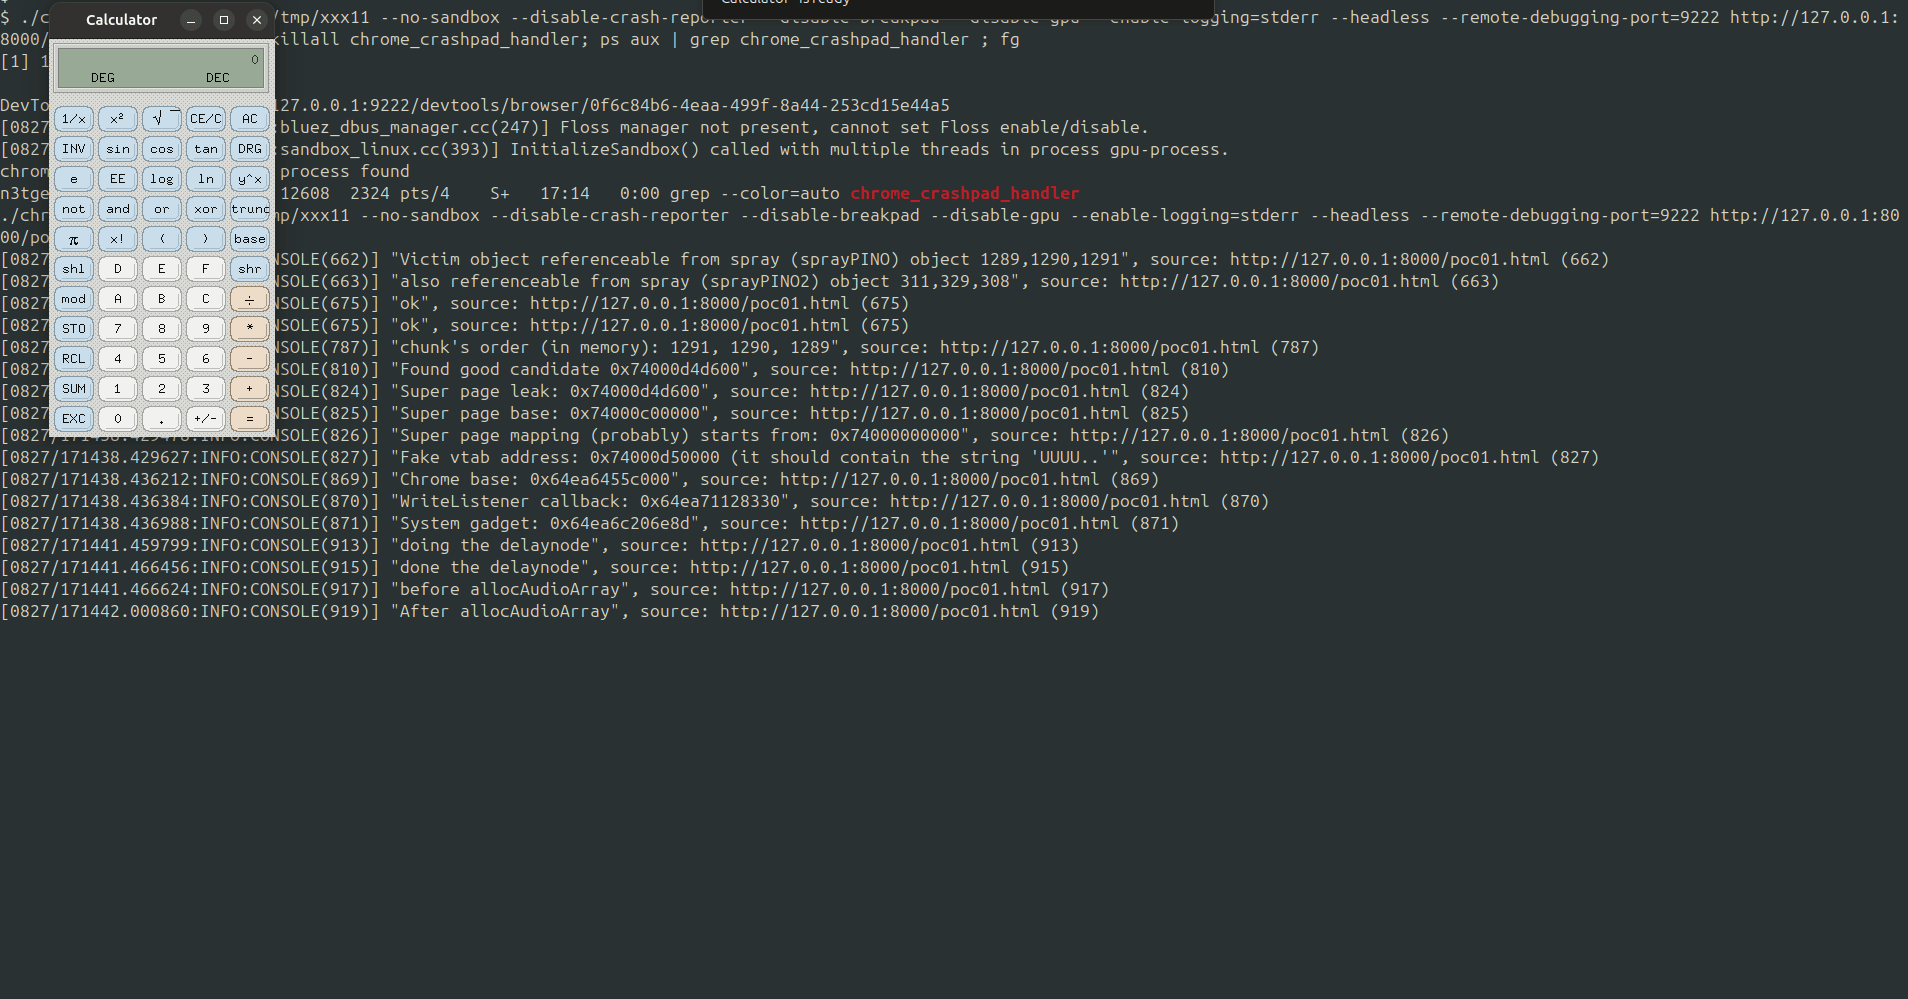 tin-z/cve-2025-27363
Integer overflow in FreeType software, which also affects Chrome
 dasokkk/cve-2026-14459-14460-pardus-software
Pardus Software Local Privilege Escalation PoC - affected from <= 1.0.4
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 alex-acero-security/cve-2025-20260-poc
Proof-of-concept exploit for CVE-2025-20260, a buffer overflow in ClamAV's PDF scanning. Includes a Python script to generate a malicious PDF and…
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
 anilkashyap01/binary-exploitation-and-kernel-escalation
Secured root-level access by identifying and exploiting misconfigurations and outdated software. Buffer overflow vulnerability in an outdated version…
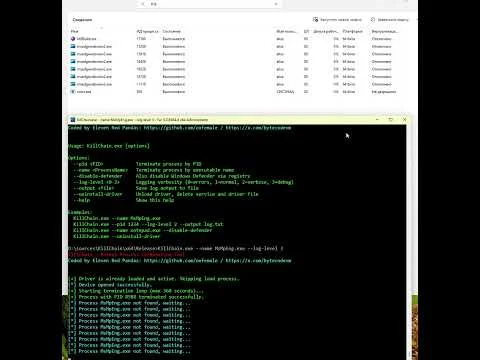 oxfemale/killchain
Kernel Process Termination Tool ( CVE-2026-0828 exploit)
 nasawyer7/iobitmalwarefighterdll
(0 day) CVE-2026-37333 LPE I found in IObit Malware Fighter v. 13.2.0.