
cve-writeups-and-pocs
 suruurism/cve-writeups-and-pocs
CVE-2026-80724 PoC + full write-up — Linux kernel ptp/vmclock read-only mapping becomes writable (VM_MAYWRITE). Discovered, reported & fixed by…
binary-exploitationeducationexploitation+2
1
suruurism/cve-writeups-and-pocsCVE-2026-80724 PoC + full write-up — Linux kernel ptp/vmclock read-only mapping becomes writable (VM_MAYWRITE). Discovered, reported & fixed by…
 404godd/cve-2026-20841-poc
🛠 Demonstrate remote code execution in Windows Notepad versions below 11.2510 using the CVE-2026-20841 proof of concept.
 learningdisordercapital35/cve_2025_24257----not-mine
Demonstrate CVE-2025-24257 with a public PoC for IOGPUFamily kernel heap OOB read/write and panic analysis
 zhangutah/security-research
Proof-of-concept C code and writeups for disclosed Linux kernel vulnerabilities, including per-CVE exploit sources and technical analysis.
 tangrs/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668.
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 do4choo/cve-2026-53694-nomachine-lpe
Proof-of-concept exploit and write-up for CVE-2026-53694, a local privilege escalation in NoMachine for Linux via argument injection in nxchmod.sh,…
 fortbridge-uk/libheif-grid-nextjs-rce
Private Fortbridge PoC for the CVE-2026-32740 Next.js/sharp leak-to-memcpy-GOT RCE chain
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 petermalone/cve-2026-43682
Proof-of-concept disk-image generator that crafts a malformed HFS+ attributes B-tree key to trigger the CVE-2026-43682 kernel heap overflow on macOS.
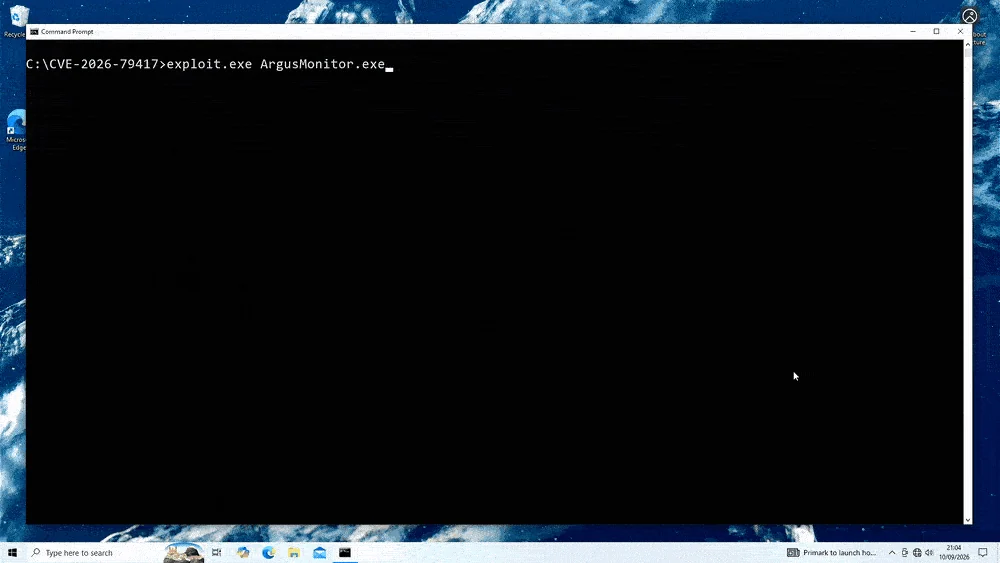 connorjaydunn/cve-2026-79417
Proof-of-concept exploit for CVE-2026-79417, a local denial-of-service vulnerability in Argus Monitor <= 7.4.02, triggered via a signed binary path.
 se1ims/pixelsmash
Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
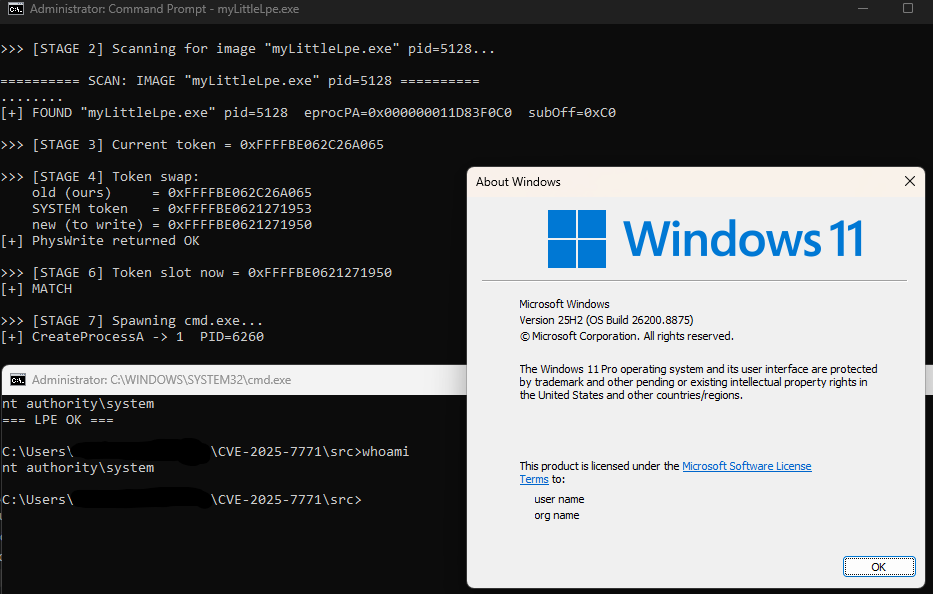 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
 petermalone/cve-2026-84543
Proof-of-concept and technical disclosure for CVE-2026-84543, a macOS SMB kernel vulnerability that triggers kernel panic via crafted SMB1 responses.
 gagaltotal/cve-2026-68376-ubuntu-7.0.0-30-poc
Proof-of-concept exploit for CVE-2026-68376 in Ubuntu kernel 7.0.0-30, leveraging SCTP chunk handling and PTE manipulation to escalate privileges to…
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499
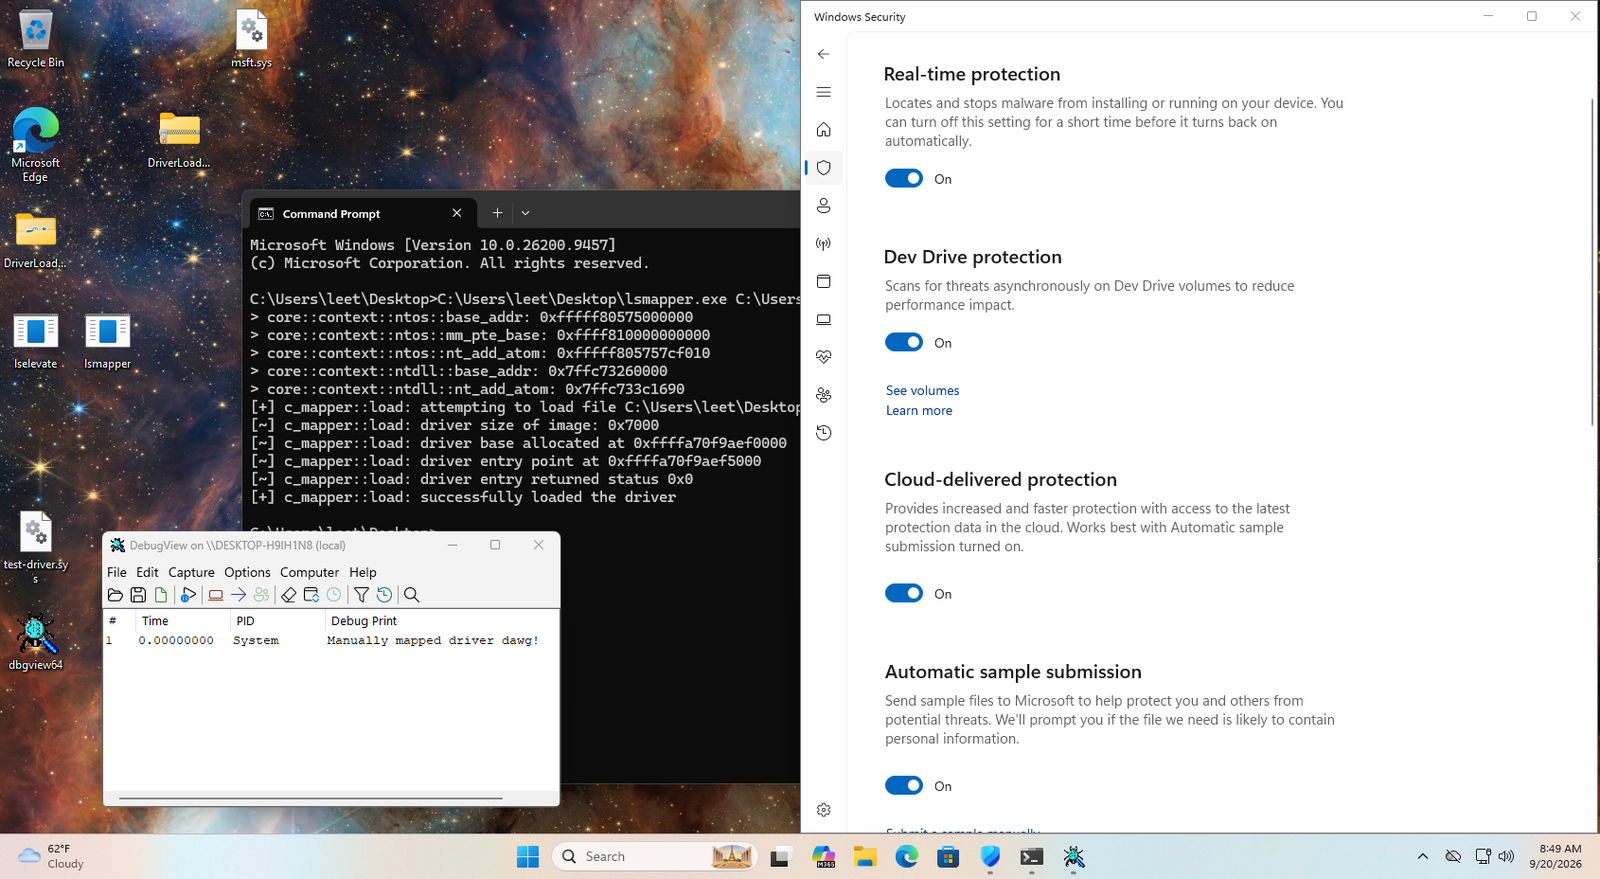 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.