
ghostlock-app
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
android-securitybinary-analysisbinary-exploitation+8
ariyanpegu/ghostlock-appGhostLock One-Tap Execution App (CVE-2026-43499)
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 jaf0rk/cve-2026-5281-cve-2026-11057-fullchain
Full-chain exploit for Android Chromium combining CVE-2026-11057 info leak and CVE-2026-5281 use-after-free to achieve vtable hijack and arbitrary…
 aemmitt-ns/skeleton
Zero-click remote code execution exploit for CVE-2021-0326 targeting Android devices, including the Peloton Bike, with a proof-of-concept requiring…
 snothin/ghostlock-s26
GhostLock (CVE-2026-43499) for the Galaxy S26
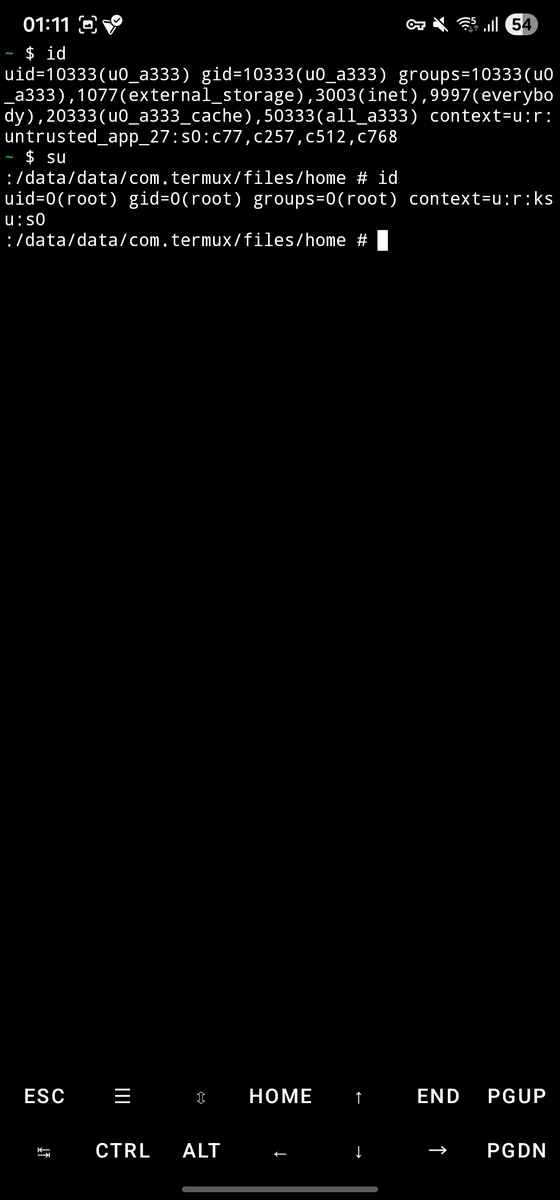 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
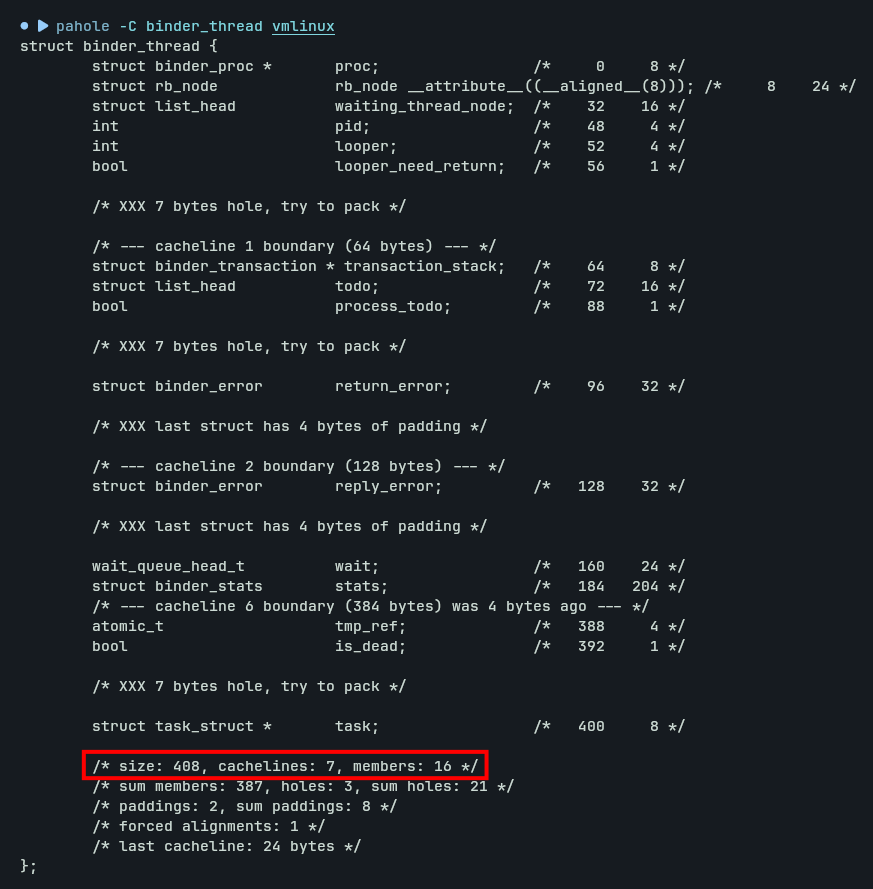 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 mobilehackinglab/ghostlock-a17
Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
 camsshaft/ionstack-s22-cve-2026-43499
Android kernel exploit for Samsung Galaxy S22 that gains kernel-domain root via CVE-2026-43499, with SELinux permissive, device-specific kallsyms,…
 xiaohj233/ghostlock-x200-root
GhostLock-X200 v1.0 - temporary root toolchain for vivo X200 (PD2415 / b57 kernel) based on CVE-2026-43499. For authorized security research only.
 flankerhqd/vendor-android-cves
Collections of my POCs for android vendor CVEs
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
 externalist/exploit_playground
Analysis of public exploits or my 1day exploits
 kudima/exploit_playground
Analysis of public exploits or my 1day exploits
 grant-h/qu1ckr00t
A PoC application demonstrating the power of an Android kernel arbitrary R/W.
 camsshaft/selinux-permissive-only-cve-2025-21479
This is an SELinux permissive version of the Cheese exploit also known as CVE-2025-21479 which affected the adreno kgsl on many devices including…
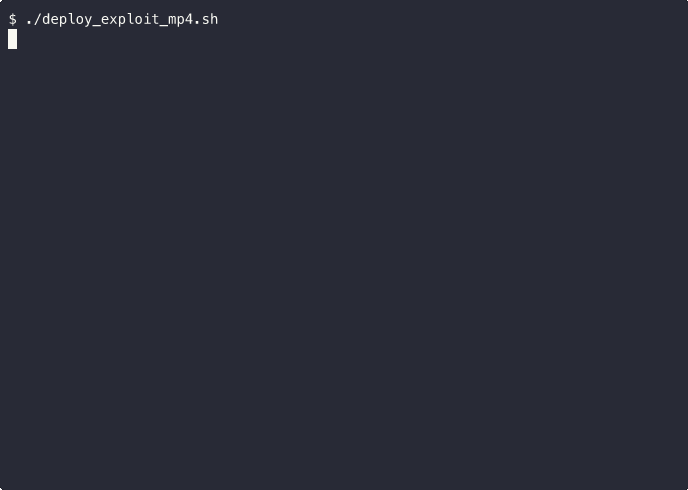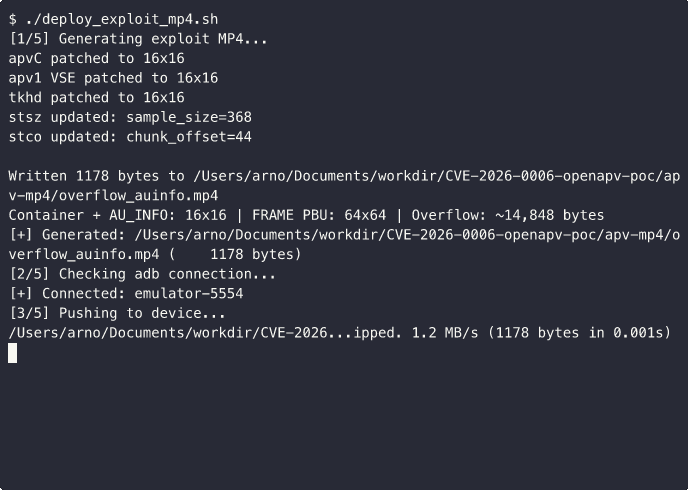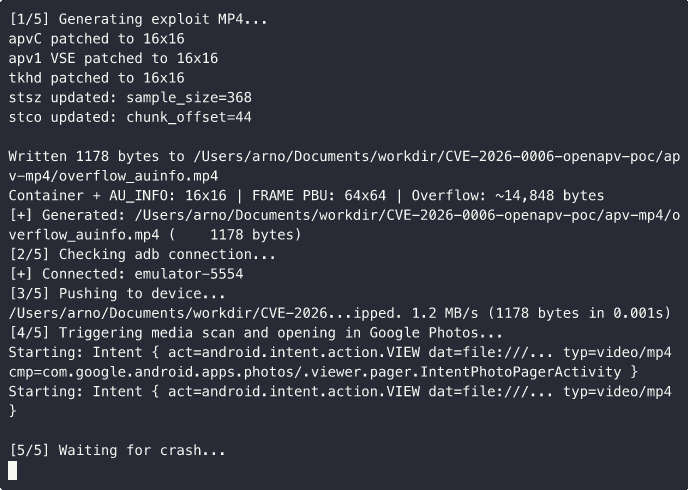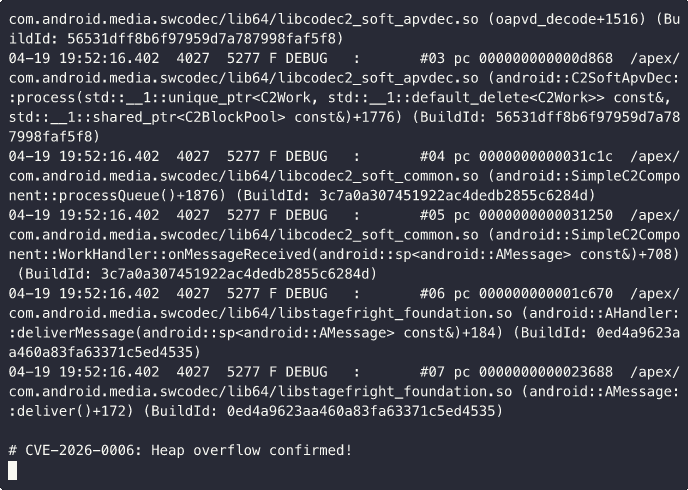 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8