

VectorFreed
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
binary-exploitationexploitationinformation-gathering+4
8
rafabd1/vectorfreedDocuments the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 exploits-forsale/prefetch-tool
Windows KASLR bypass using prefetch side-channel
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 xairy/kernel-exploits
My proof-of-concept exploits for the Linux kernel
 0xdea/exploits
Public exploit repository covering local privilege escalation, buffer overflows, and database exploits across Linux, Solaris, AIX, OpenBSD, Zyxel,…
 spiralbl0ck/linux-kernel-infoleak-6.12.-leveraged-to-do-cross-container-info-leak.-
POC shows how to leak postgresql stuff cause hugefile sub-system. Based on https://x.com/spendergrsec/status/1993794163880718700?s=20
 mcw0/poc
Issues has been disabled for these PoC's, as they are simply PoC, Public Domain and unsupported.
 axi0mx/ipwndfu
open-source jailbreaking tool for many iOS devices
 sandraschi/copy-fail-mcp
CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP
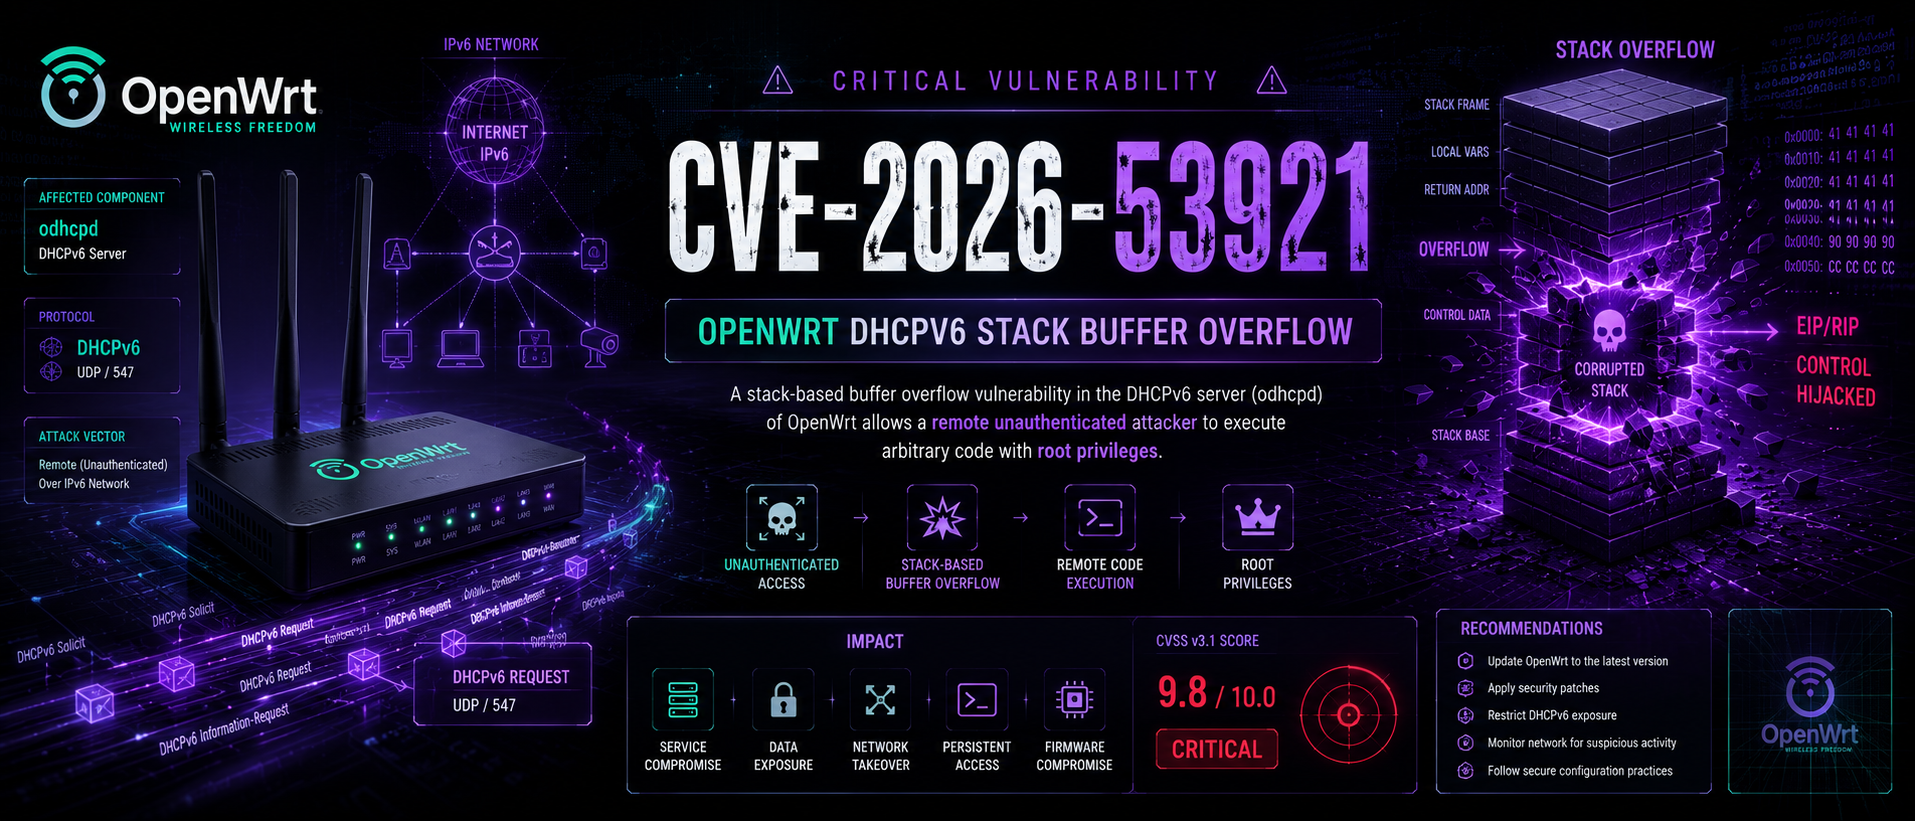 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 imbas007/cve-2026-42533
Exploit for nginx heap buffer overflow (CVE-2026-42533) providing pre-auth RCE via two-pass capture clobbering. Includes info leak, heap spray, and…
 mobilehackinglab/cve-2026-0047-poc
CVE-2026-0047: Missing permission check in ActivityManagerService.dumpBitmapsProto() — steal UI bitmaps from every running app with zero permissions…
 peterpan0927/cve-2017-2370
on Mac 10.12.2
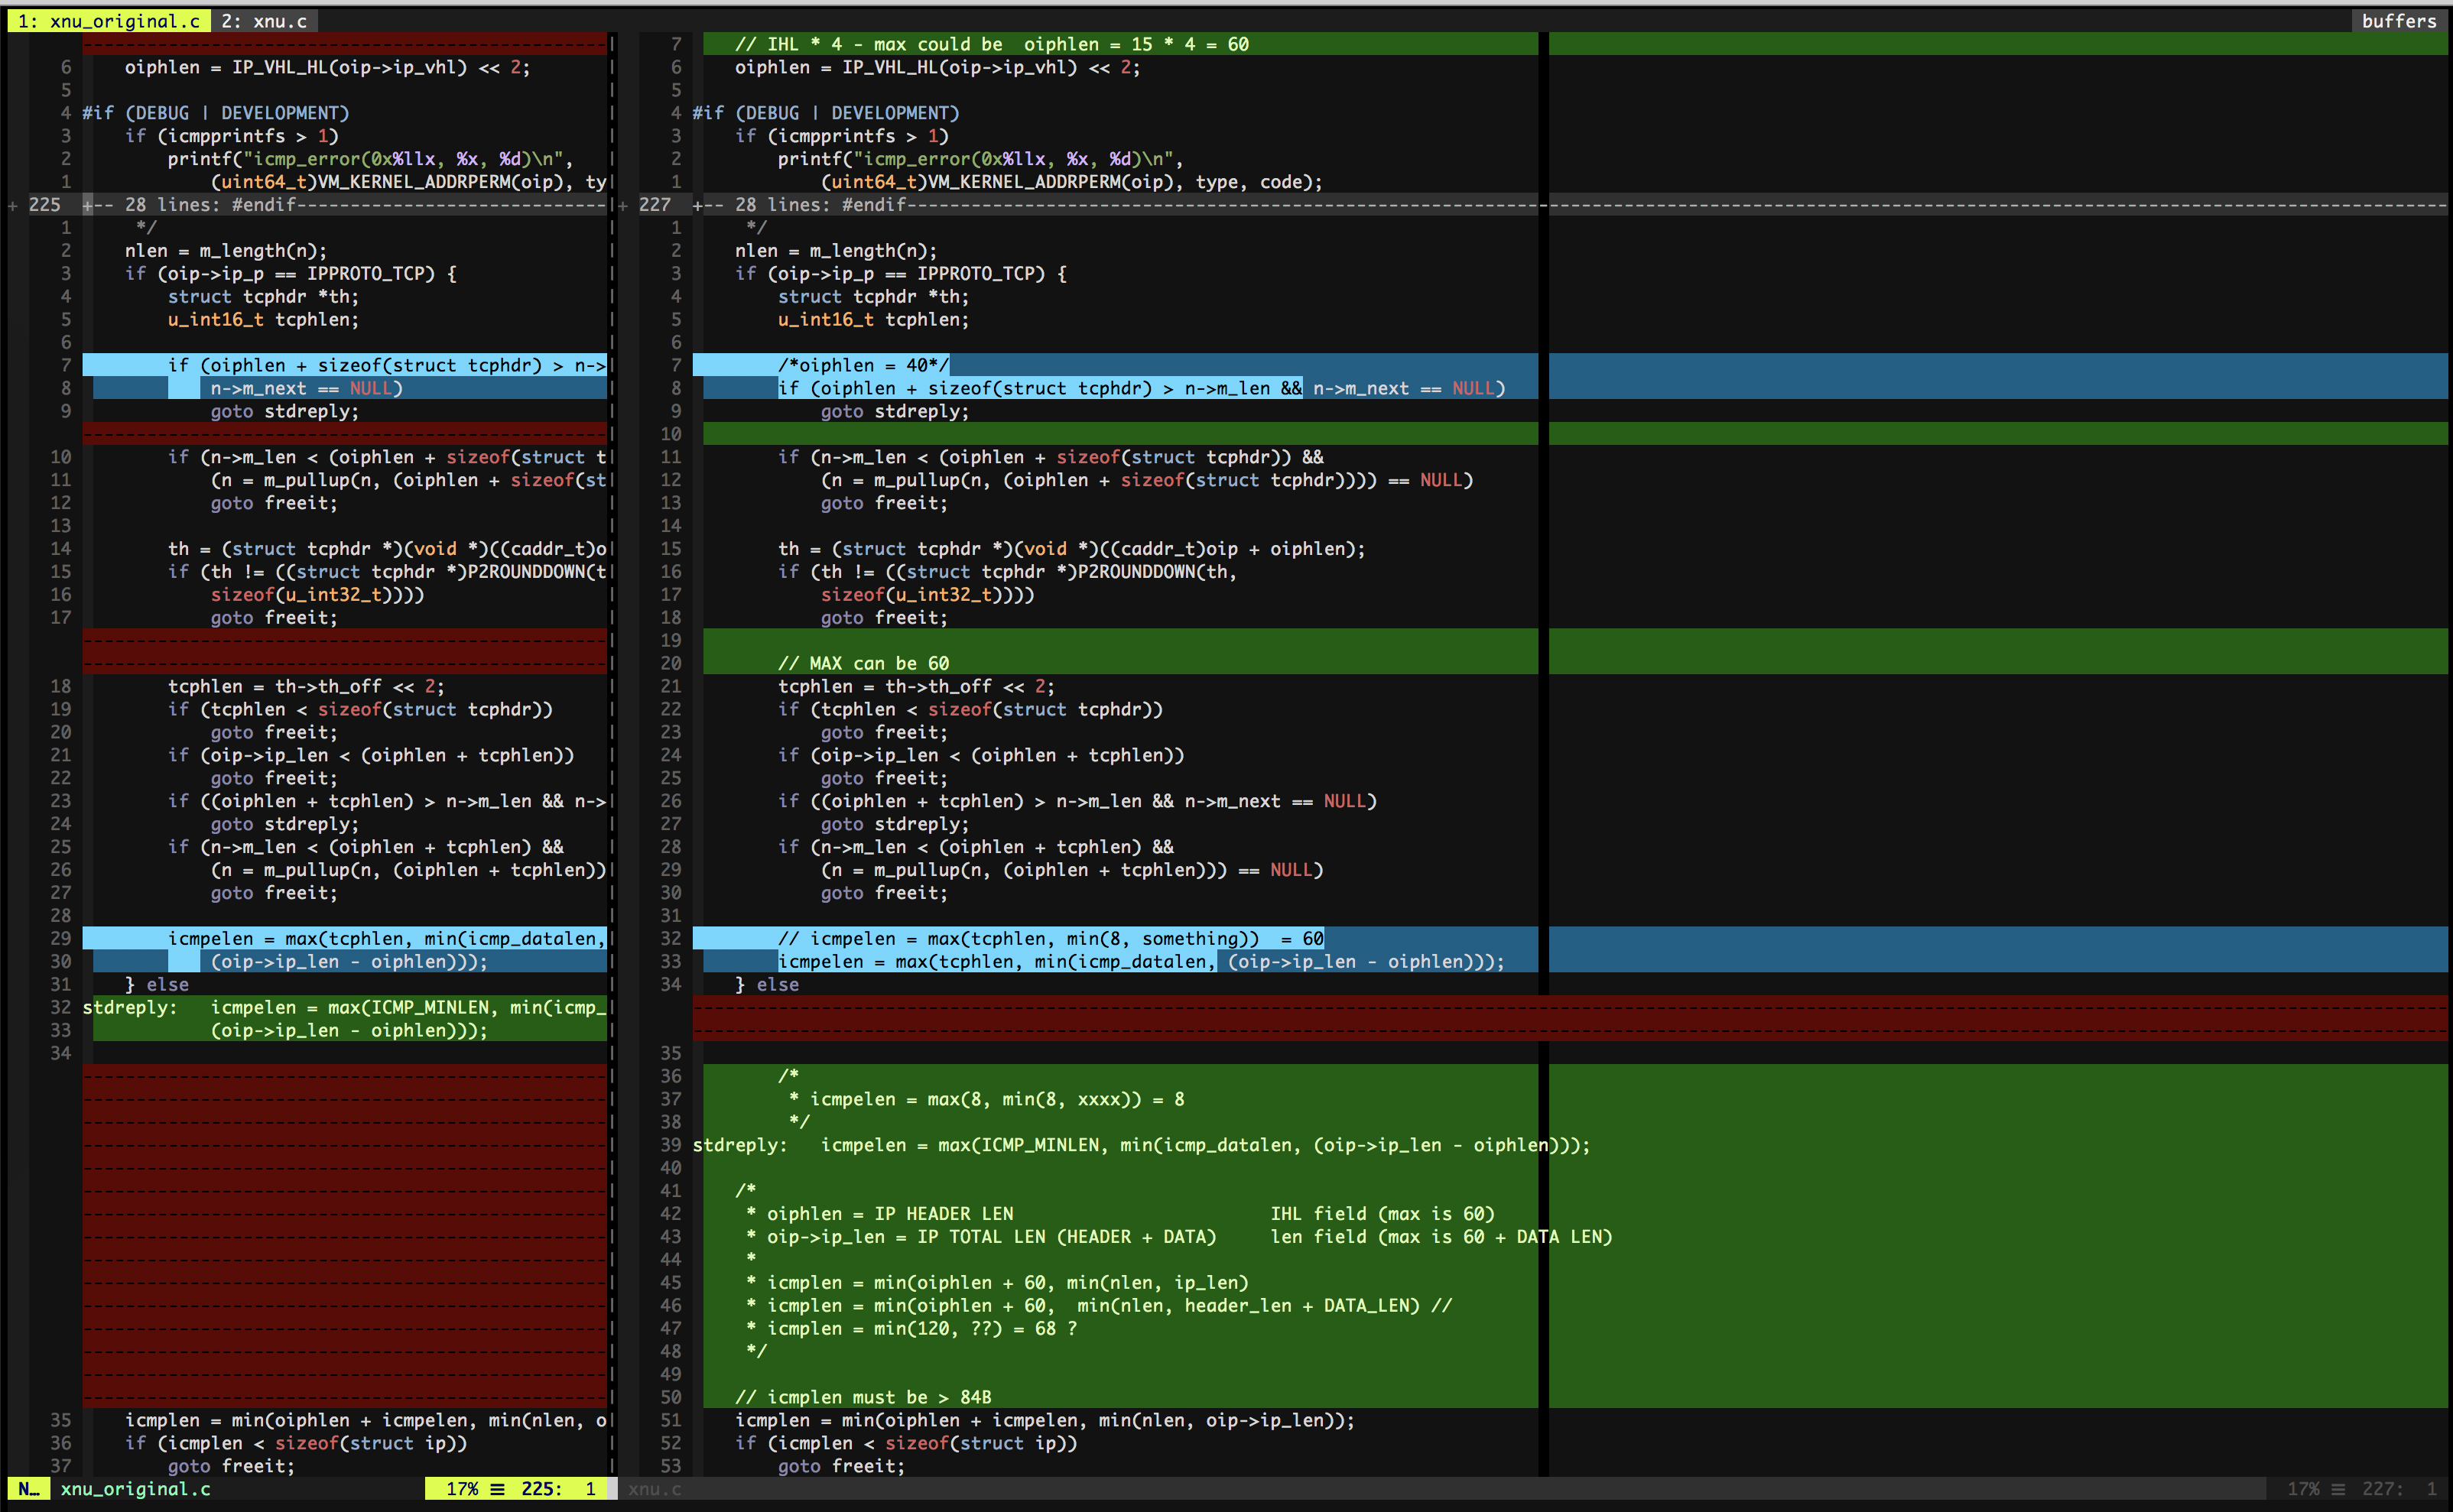 lucagiovagnoli/cve-2018-4407
A buffer overflow vulnerability in the XNU kernel's ICMP error code causes IOS devices to crash (laptops and mobiles).
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used