

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
57 results
MSRKit preview

MSRKit

GitHubrurixis/msrkit

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
binary-exploitationexploitationpayload-development+5
9
4 days ago
K50G-POCOF4GT-CVE-2026-43499-PoC preview

K50G-POCOF4GT-CVE-2026-43499-PoC

GitHubcxyofficial/k50g-pocof4gt-cve-2026-43499-poc

Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
android-securitybinary-exploitationexploitation+5
23 days ago
Copy-fail-CVE-2026-31431-Exploit-in-C preview

Copy-fail-CVE-2026-31431-Exploit-in-C

GitHubmr-bv/copy-fail-cve-2026-31431-exploit-in-c

C exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability in the AF_ALG AEAD path, using splice() to influence cached file…
binary-exploitationexploitationexploit-frameworks+1
4 months ago
CVE-2026-36981-Kernel-EoP-PoC preview

CVE-2026-36981-Kernel-EoP-PoC

GitHubcanomer/cve-2026-36981-kernel-eop-poc

Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
binary-exploitationdebuggersexploitation+4
24 months ago
voidmap preview

voidmap

GitHubsamueltulach/voidmap

Using CVE-2021-40449 to manual map kernel mode driver

binary-exploitationexploitationexploit-frameworks+2
1054 years ago
cve-2018-8611 preview

cve-2018-8611

GitHubahm3dgg/cve-2018-8611

Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
binary-exploitationexploitationpost-exploitation+1
11 month ago
CVE-2026-66804-CrossDevice-LPE preview

CVE-2026-66804-CrossDevice-LPE

GitHubdavidcarliez/cve-2026-66804-crossdevice-lpe

Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…

binary-exploitationexploitationprivilege-escalation+1
141 month ago
prefetch-tool preview

prefetch-tool

GitHubexploits-forsale/prefetch-tool

Windows KASLR bypass using prefetch side-channel
binary-exploitationexploitationinformation-gathering+4
2132 years ago
QuestStack preview

QuestStack

GitHubstarseed12345/queststack

Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
android-securitybinary-exploitationembedded-systems-security+5
20528 days ago
IoRingReadWritePrimitive preview

IoRingReadWritePrimitive

GitHubyardenshafir/ioringreadwriteprimitive

Post exploitation technique to turn arbitrary kernel write / increment into full read/write primitive on Windows 11 22H2
binary-exploitationexploitationpenetration-testing+3
2584 years ago
Windows-kernel-SegmentHeap-Aligned-Chunk-Confusion preview

Windows-kernel-SegmentHeap-Aligned-Chunk-Confusion

GitHubsynacktiv/windows-kernel-segmentheap-aligned-chunk-confusion

PoC exploiting Aligned Chunk Confusion on Windows kernel Segment Heap

binary-exploitationexploitationpapers-research+2
2126 years ago
CVE-2020-17057 preview

CVE-2020-17057

GitHublsw29475/cve-2020-17057

Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.
binary-exploitationexploitationmemory-forensics+1
25 years ago
wnfexec preview

wnfexec

GitHubustayready/wnfexec

WNF Code Execution Library Using C#
binary-exploitationexploitationpayload-development+4
1106 years ago
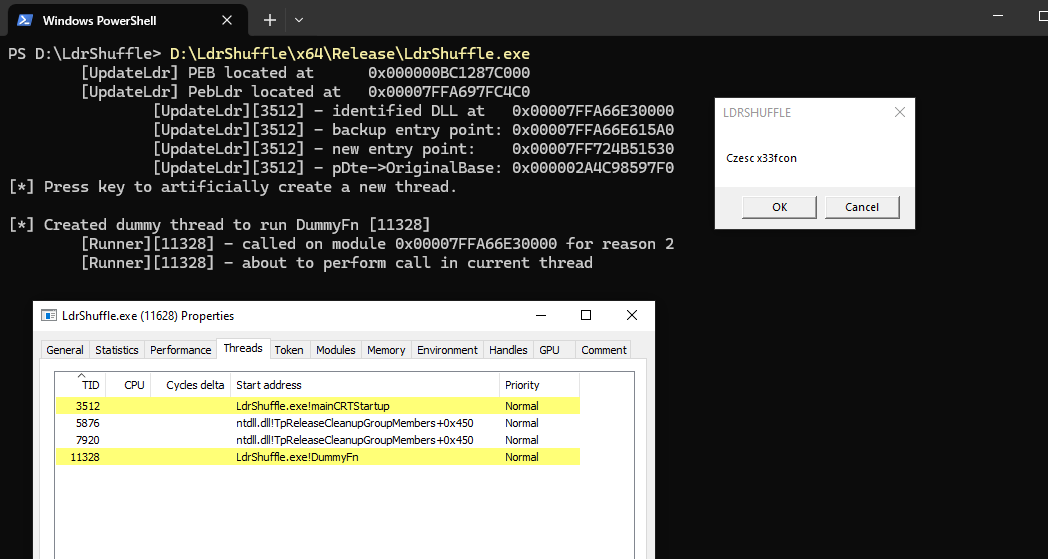
LdrShuffle preview

LdrShuffle

GitHubrwxstoned/ldrshuffle

Code execution/injection technique using DLL PEB module structure manipulation
binary-exploitationcode-analysisexploitation+6
2871 year ago
Cve-2022-26809 preview

Cve-2022-26809

GitHubmichealadams30/cve-2022-26809

Proof-of-concept exploit for CVE-2022-26809, a Windows RPC runtime integer overflow vulnerability. Includes trigger scripts using PetitPotam-style…

binary-exploitationexploitationpayload-development+2
3 years ago
CVE-2025-8088-Multi-Document preview

CVE-2025-8088-Multi-Document

GitHubpentestfunctions/cve-2025-8088-multi-document

Exploit systems using older WinRAR without knowing their username (unlike other projects)

binary-exploitationeducationexploitation+4
351 year ago
CVE-2019-0708-Exploit preview

CVE-2019-0708-Exploit

GitHubrockmelodies/cve-2019-0708-exploit

Using CVE-2019-0708 to Locally Promote Privileges in Windows 10 System

binary-exploitationexploitationprivilege-escalation+1
317 years ago
CVE-2022-26809 preview

CVE-2022-26809

GitHubyuanlink/cve-2022-26809

PoC and analysis for CVE-2022-26809, a Windows RPC runtime integer overflow vulnerability. Includes trigger scripts using PetitPotam-style UNC path…

binary-exploitationexploitationpayload-development+2
614 years ago
Previous1234Next