
EXPLOIT-CVE-2024-7804
 joaovicdev/exploit-cve-2024-7804
Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
binary-exploitationeducationexploitation+2
joaovicdev/exploit-cve-2024-7804Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
 hibanitt/cve-2024-38063
In-depth technical analysis and proof-of-concept for CVE-2024-38063, a critical Windows IPv6 kernel RCE. Includes root-cause breakdown, Scapy-based…
 ownouwa/cve-2024-23113-poc
CVE-2024-23113 是一个在 Linux Kernel 中被发现的漏洞,它属于 任意代码执行漏洞,影响了 bpf (Berkeley Packet Filter) 子系统。具体来说,这个漏洞影响了 bpf 程序的 bpf_prog 类型的对象,并且可以允许攻击者通过构造恶意的 BPF…
 l1m3syc/cve-2024-4947-poc
Educational proof-of-concept for CVE-2024-4947, a V8 Maglev type confusion, demonstrating a full chain from trigger to arbitrary code execution on a…
 sneakynachos/cve-2024-29943-but-with-wasm
CVE-2024-29943, but with wasm
 murdok1982/exploit-poc-para-cve-2024-30085
Exploit en Python diseñado para aprovechar la vulnerabilidad de elevación de privilegios CVE-2024-30085
 horizon3ai/cve-2026-22200
CVE-2026-22200: Arbitrary file read + CNEXT RCE in osTicket
 razureink/cve-2024-49113-ldap_nightmare_reproduction
Reproduction of cve-2024-49113-ldap_nightmare_reproduction
 shinspace92/cve-2024-26229
Nim touch up of CVE 2024 26229
 razureink/cve-2024-38077-madlicense_reproduction
CVE Reproduction: cve-2024-38077-madlicense_reproduction
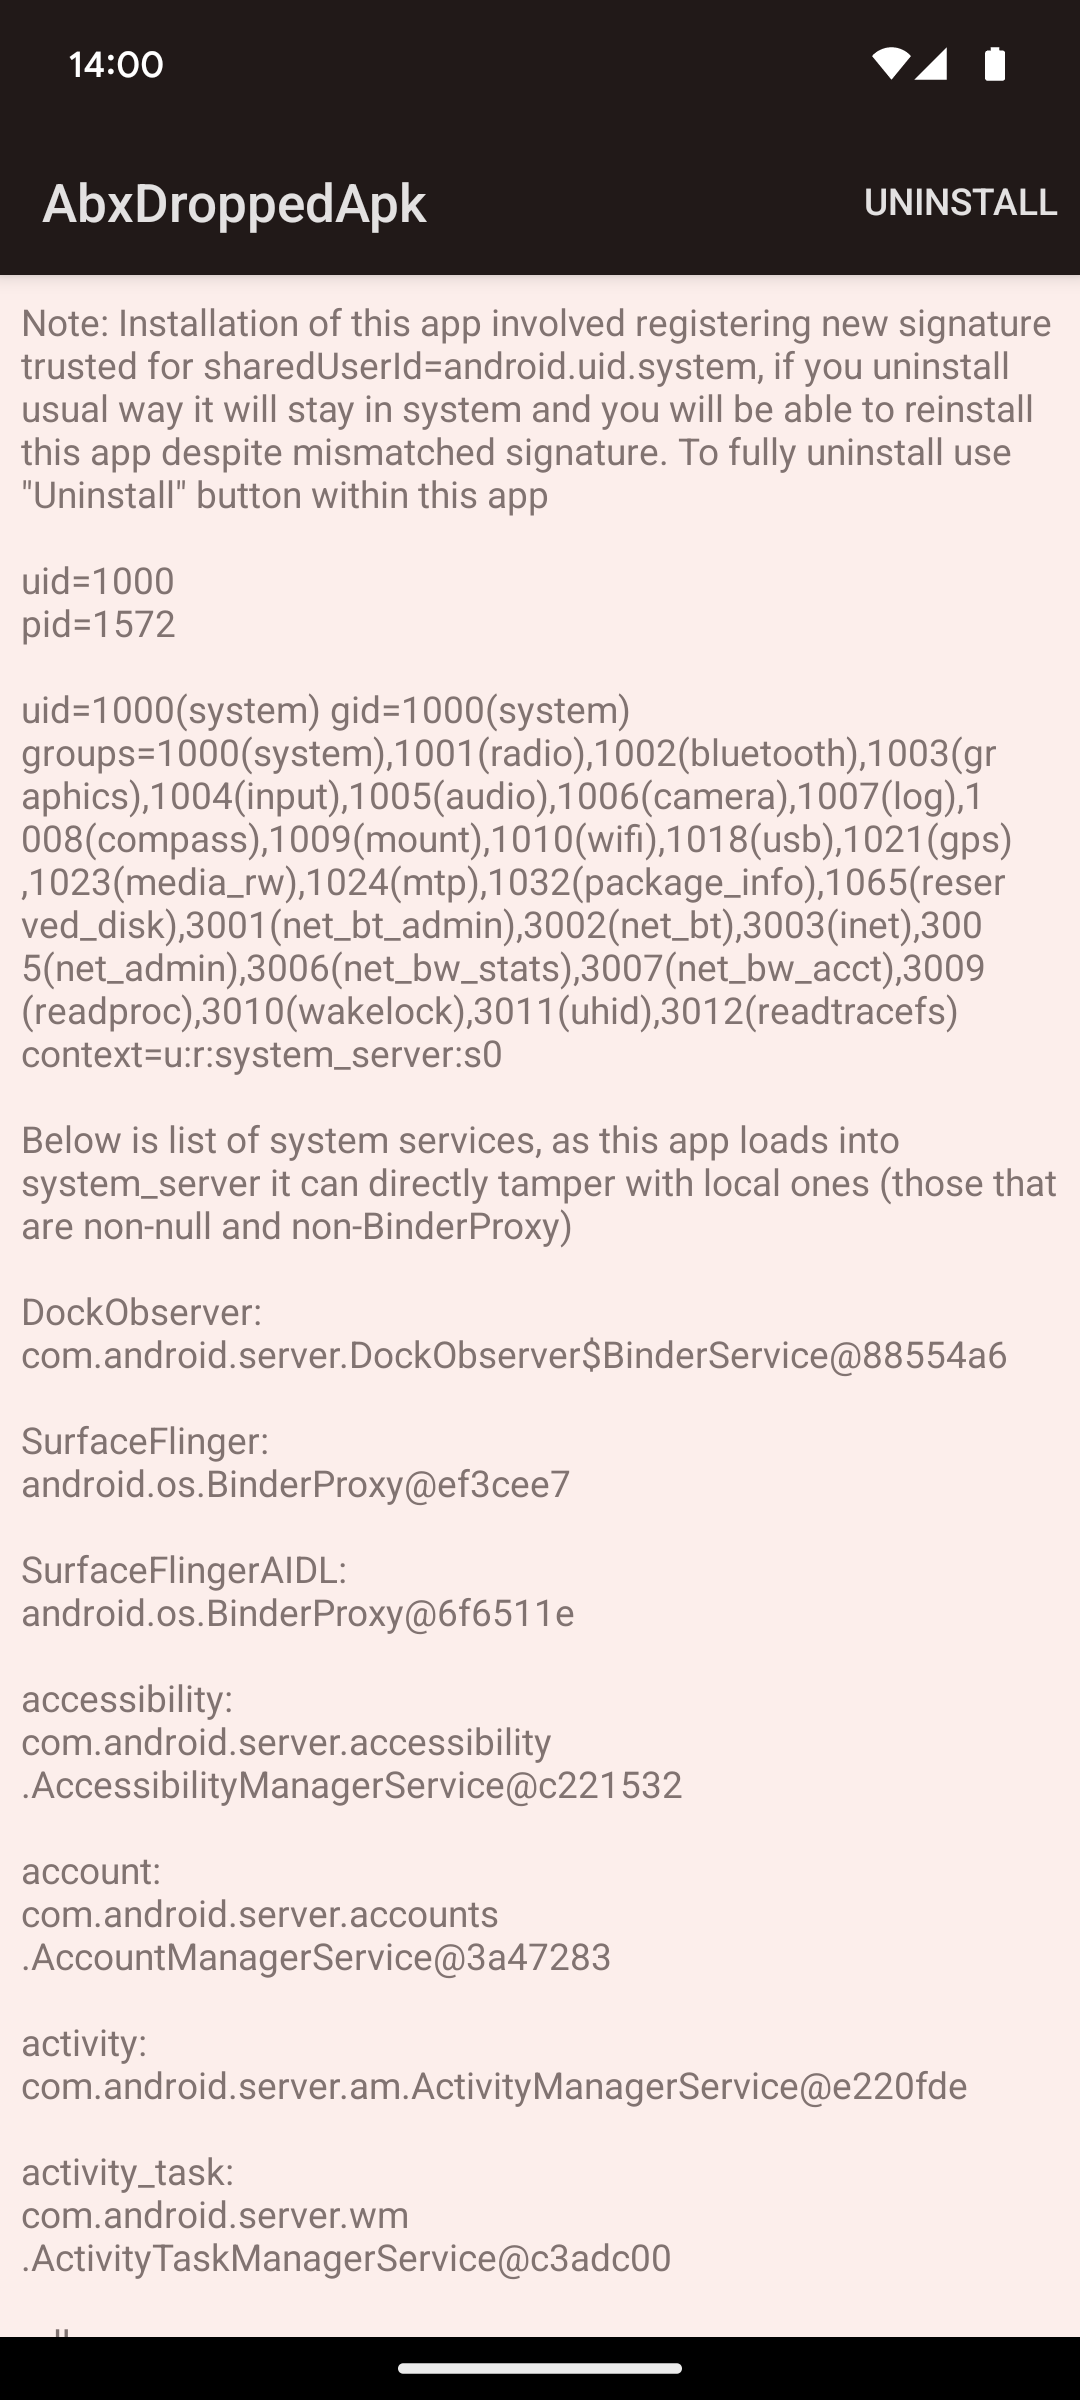 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
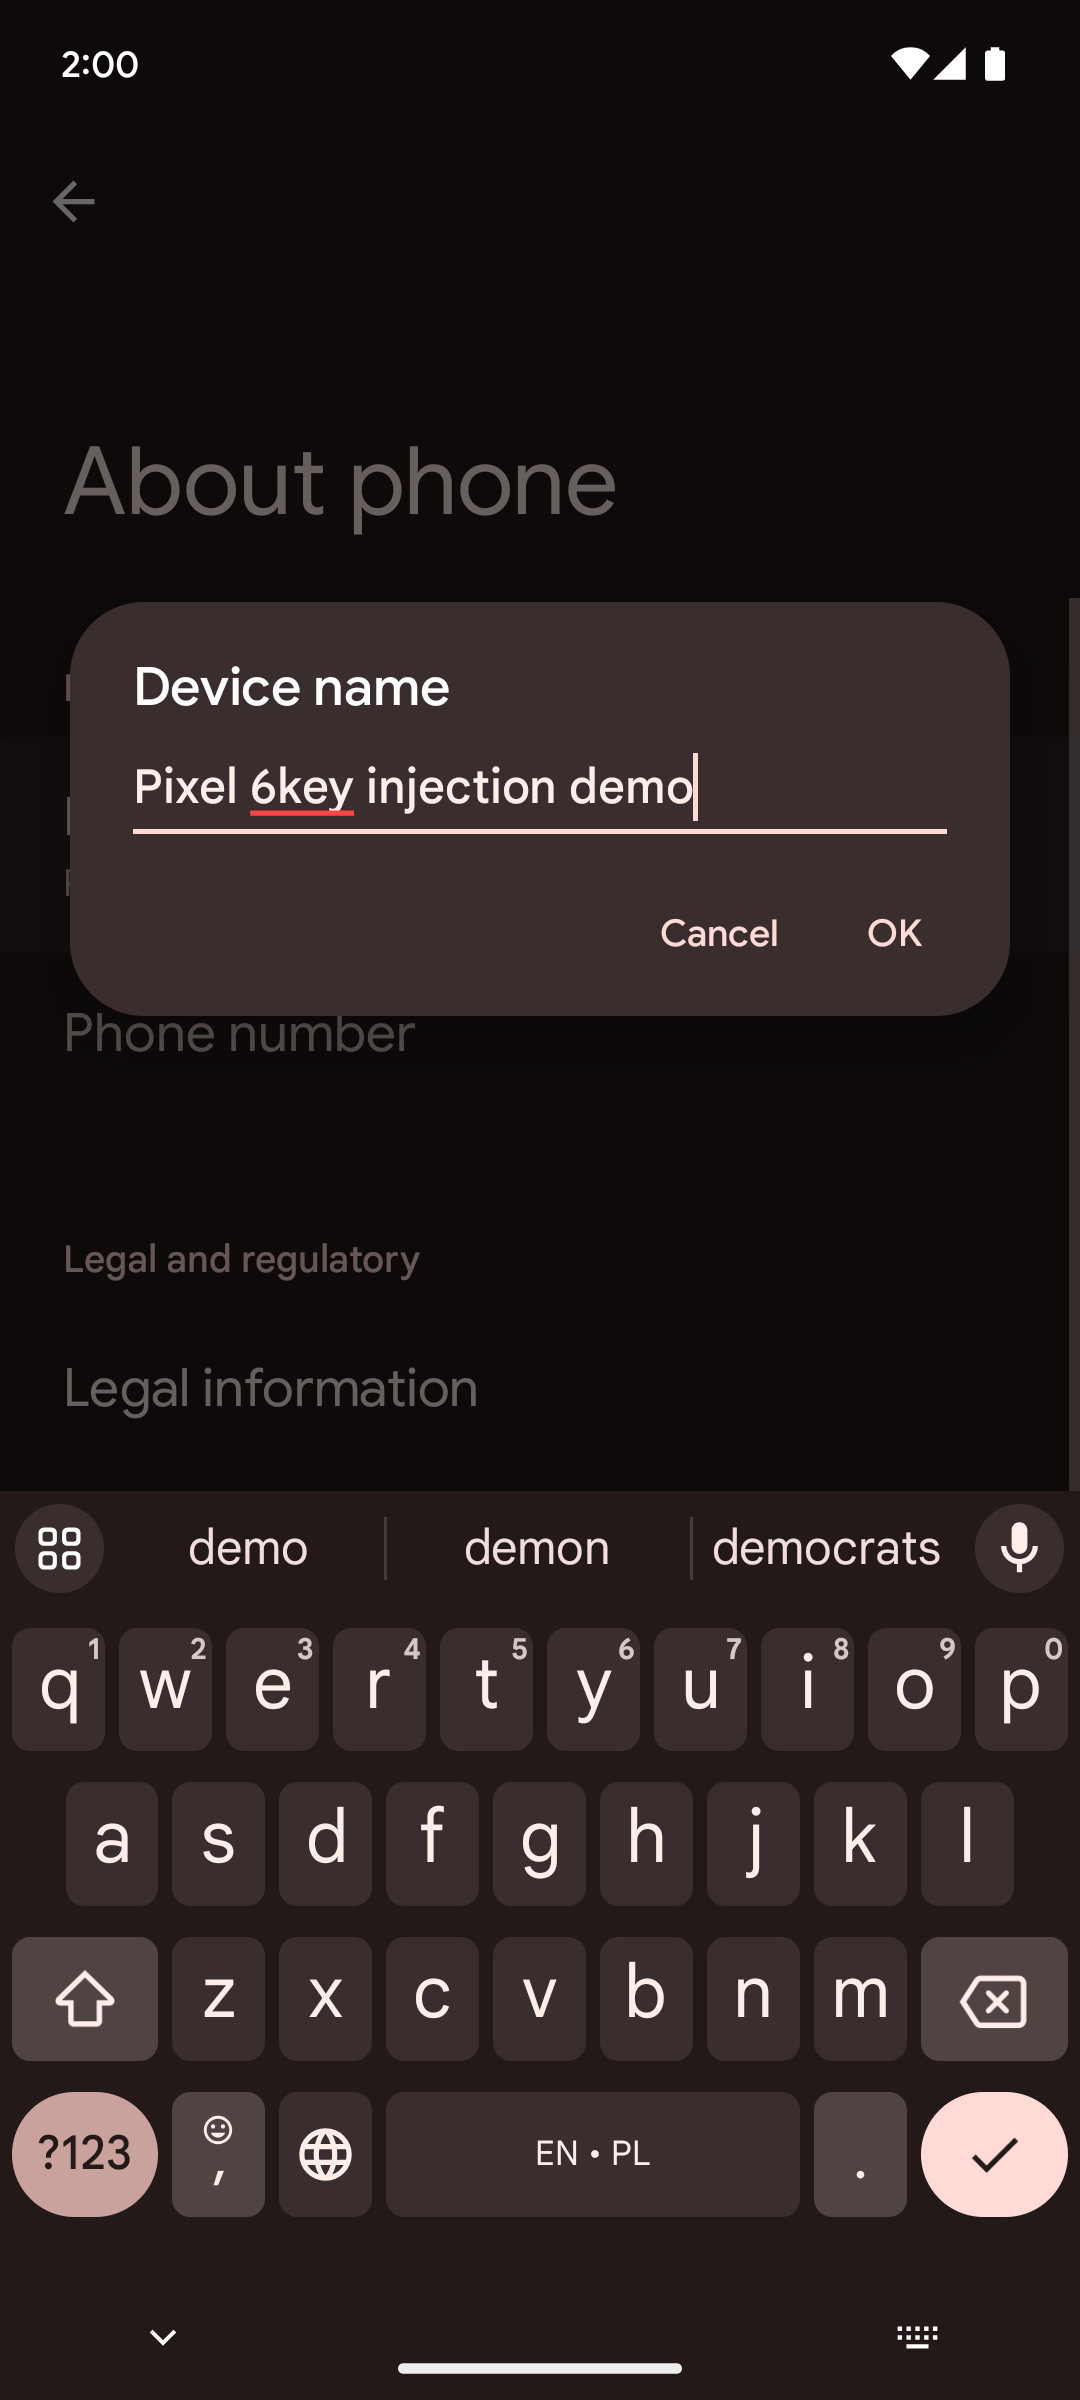 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
 michredteam/cve-2024-4761
High CVE-2024-4761 Exploit
 patchpoint/cve-2024-38063
Proof-of-concept exploit for CVE-2024-38063, a Windows TCP/IP remote code execution vulnerability triggered by sending two crafted IPv6 packets with…
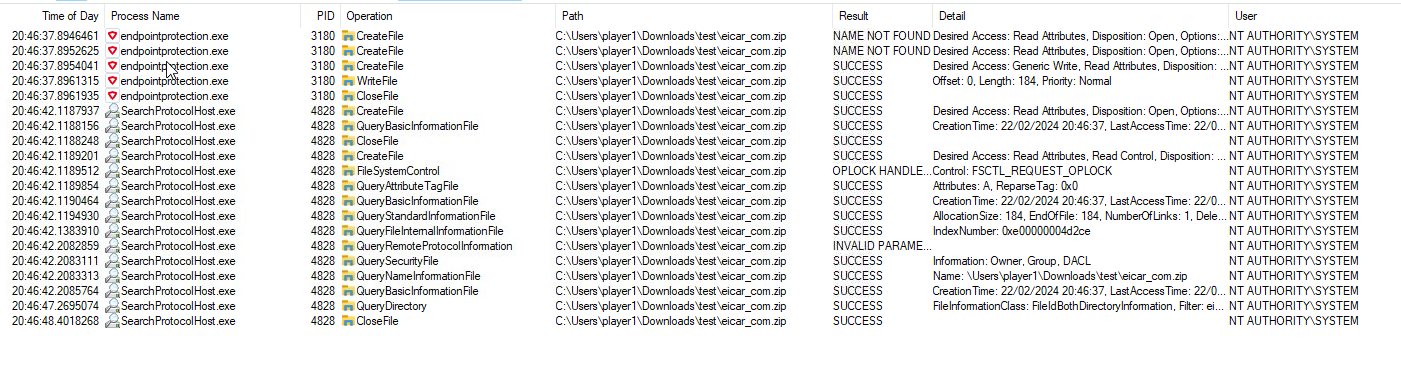 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
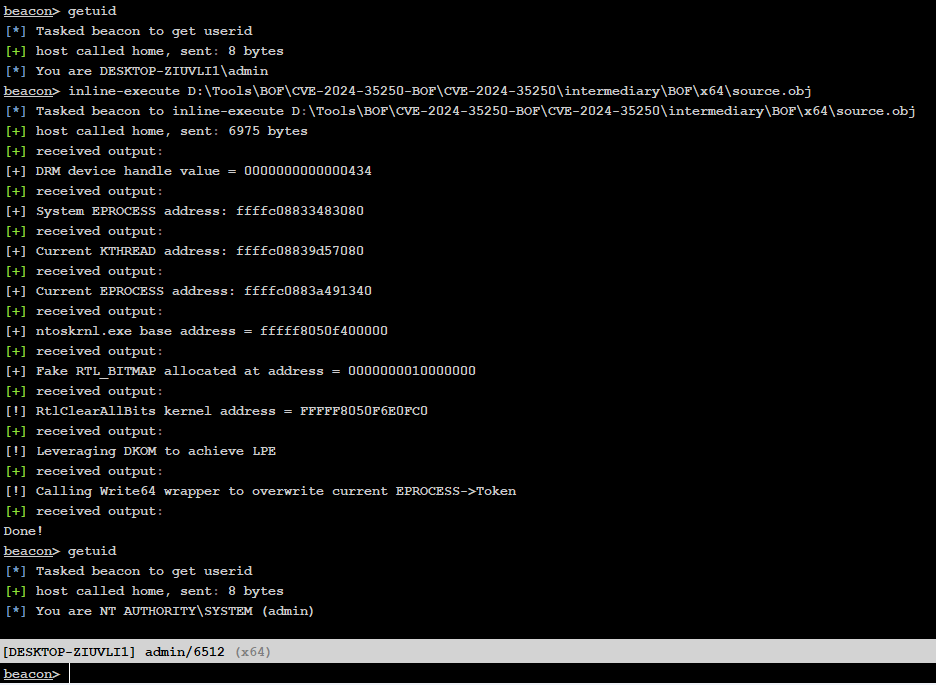 ro0tmylove/cve-2024-35250-bof
Cobalt Strike 的 CVE-2024-35250 的 BOF。(请给我加个星,谢谢。)
 rvzsec/cve-2024-2961
CVE-2024–2961 Security Issue Mitigation Script
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…