
PHP2shell
 0xgh057r3c0n/php2shell
One-click exploit PoC for CVE-2026-109618 and CVE-2026-109619 against vulnerable PHP + Apache mod_php (prefork) targets.
binary-exploitationexploitationpayload-development+4
0xgh057r3c0n/php2shellOne-click exploit PoC for CVE-2026-109618 and CVE-2026-109619 against vulnerable PHP + Apache mod_php (prefork) targets.
 c4psu13/mali-pagecache-root
TCL 50C721 (RTD1319 / Mali-G31) root toolkit — autonomous CVE-2022-22706 exploit chain
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 r3n3r0/cve-2026-0006-step-2
Research package demonstrating a leak-assisted ROP chain in Android media.swcodec via the CVE-2026-0006 APV decoder heap overflow, with payload…
 constantinefedorov/review.cve-2021-3156
Python proof-of-concept exploit for CVE-2021-3156 (Baron Samedit), a sudoedit heap overflow enabling local privilege escalation to root on vulnerable…
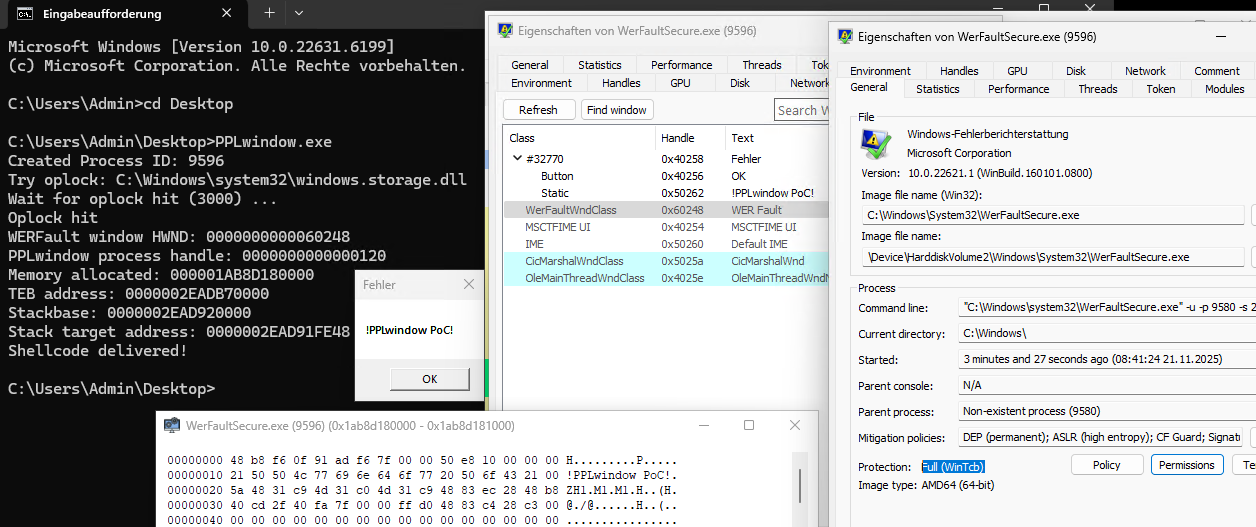 r41n3rzuf477/pplwindow
Proof-of-concept PPL bypass abusing the NtUserGetWindowProcessHandle syscall to obtain a handle to protected Windows processes without admin…
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 wonjj6768/lenovo-tb365fc-ghostlock-cve-2026-43499
GhostLock (CVE-2026-43499) root + KernelSU LKM for the Lenovo TB365FC (ZUXOS / Android 16, kernel 5.15.170)
 aniketlab/poco-m7-plus-jailbreak
Temporary Root Research on Poco M7 Plus (SM6375) via Qualcomm GBL Exploit (CVE-2026-24088) + GhostLock Kernel Analysis (CVE-2026-43499)
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 wangs-official/opace6-cve-2026-64560
Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…
 qingle009/opace6-cve-2026-64560
OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 yutori-natsu/cve-2023-6931-pipa
Kernel LPE exploit for CVE-2023-6931 on Xiaomi Pad 6 (pipa), chaining a perf read_size overflow to root and disabling SELinux via data-only…
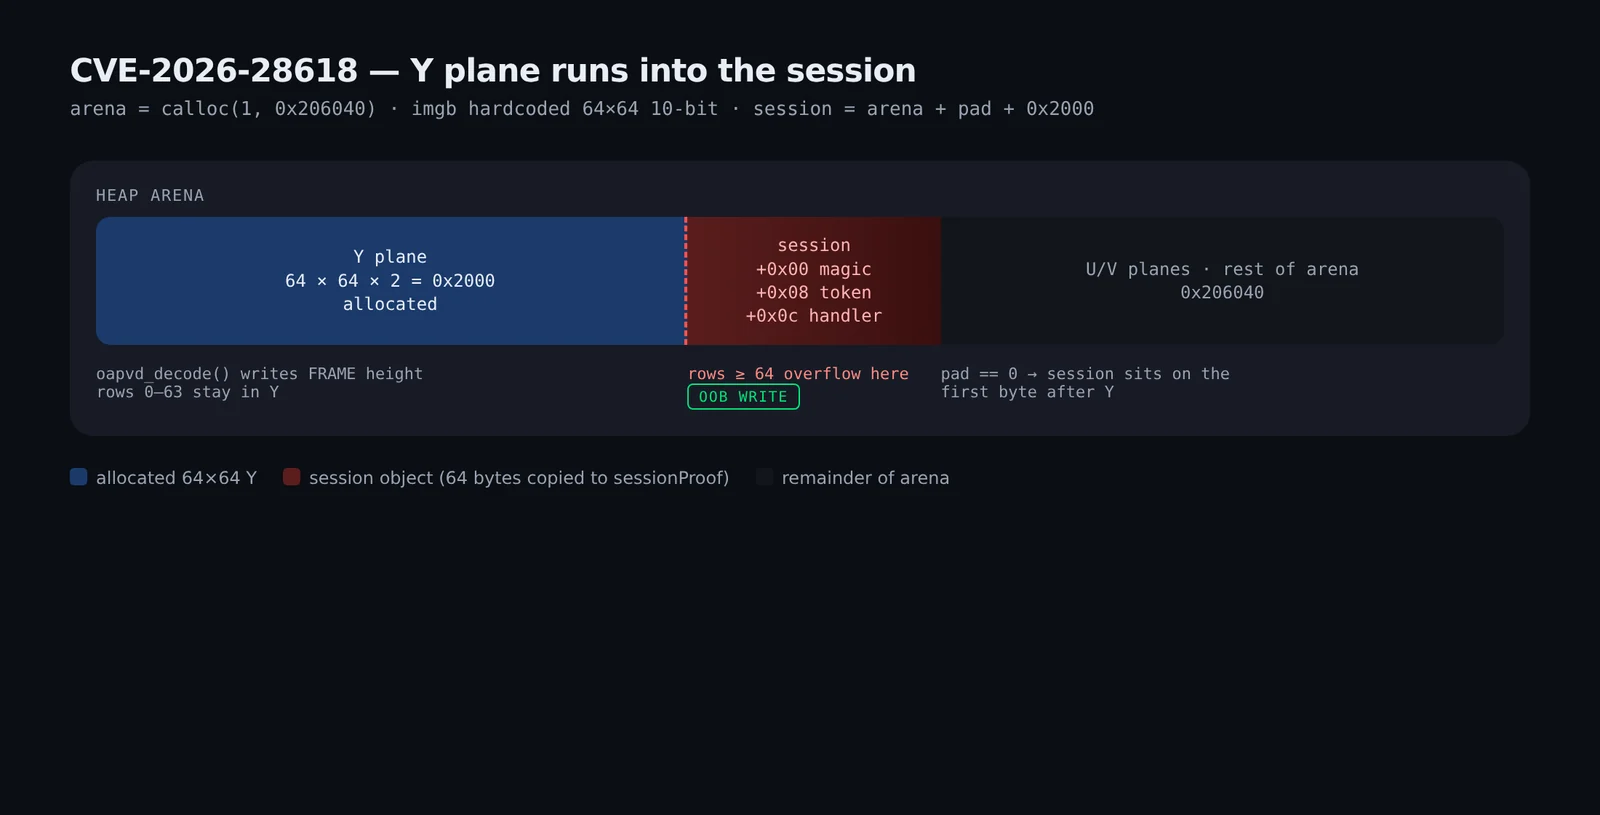 raafatabualazm/streambox-cve-2026-28618
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch
 gmh5225/frida-vmprotect-bypass
Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.