

CVE-2017-4878-Samples
 brianwrf/cve-2017-4878-samples
CVE-2017-4878 Samples - http://blog.talosintelligence.com/2018/02/group-123-goes-wild.html
binary-exploitationexploitationmalware-analysis+3
17
brianwrf/cve-2017-4878-samplesCVE-2017-4878 Samples - http://blog.talosintelligence.com/2018/02/group-123-goes-wild.html
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 jonpichel/cve-2017-7358
Proof-of-concept exploit for CVE-2017-7358, demonstrating a specific vulnerability in a software application. Intended for security research and…
 vinukalana/dirtypipe-cve-2022-0847
This repository is developed to analysis and understand DirtyPipe exploit CVE-2022-0847
 alex-acero-security/cve-2025-20260-poc
Proof-of-concept exploit for CVE-2025-20260, a buffer overflow in ClamAV's PDF scanning. Includes a Python script to generate a malicious PDF and…
 0xkickit/icue_dllhijack_lpe-cve-2024-22002
Proof-of-concept exploit for CVE-2024-22002, demonstrating local privilege escalation via DLL hijacking in CORSAIR iCUE's update service to run code…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 tin-z/cve-2025-27363
Integer overflow in FreeType software, which also affects Chrome
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
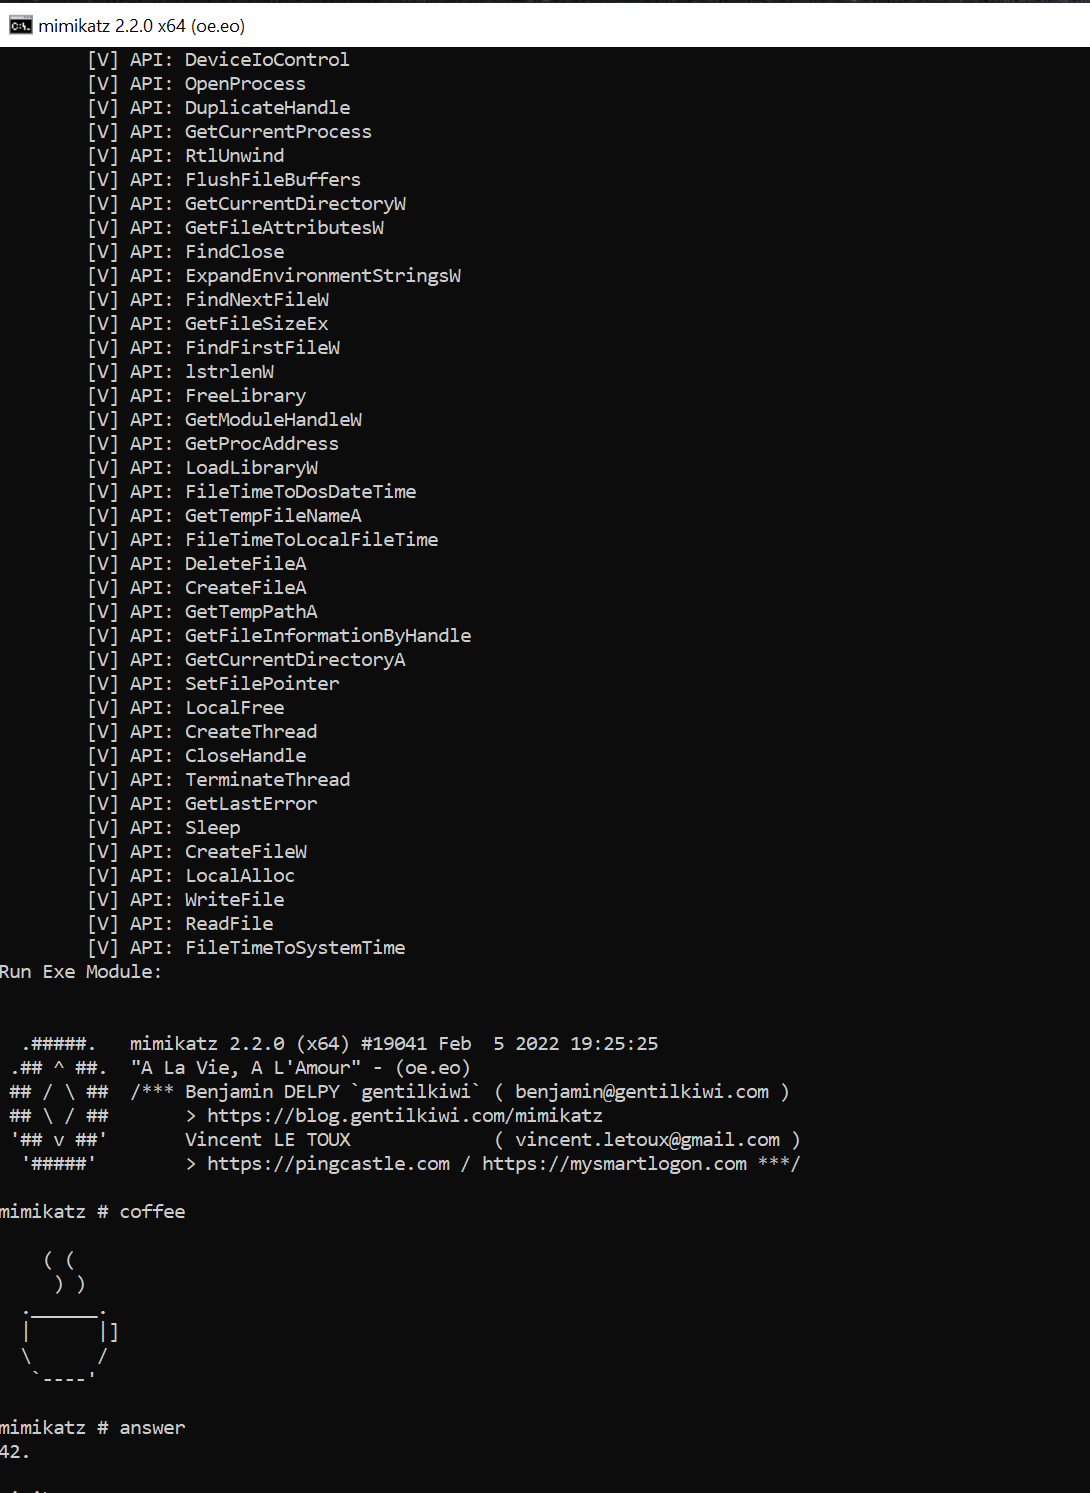 s3cur3th1ssh1t/nim-runpe
A Nim implementation of reflective PE-Loading from memory
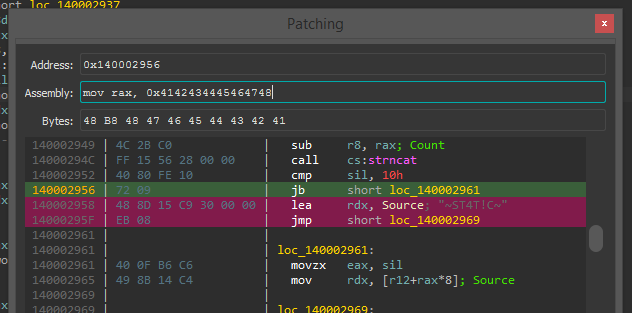 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 zkenjar/v0ltpwn
Tool Suite for V0LTpwn (CVE-2019-11157). Code will be published soon.
 rajauzairabdullah/cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a remote code execution vulnerability in Windows Notepad, demonstrating file-based trigger and execution…
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 ashemery/exploitation-course
Offensive Software Exploitation Course