
LocalStranger
 nbs32k/localstranger
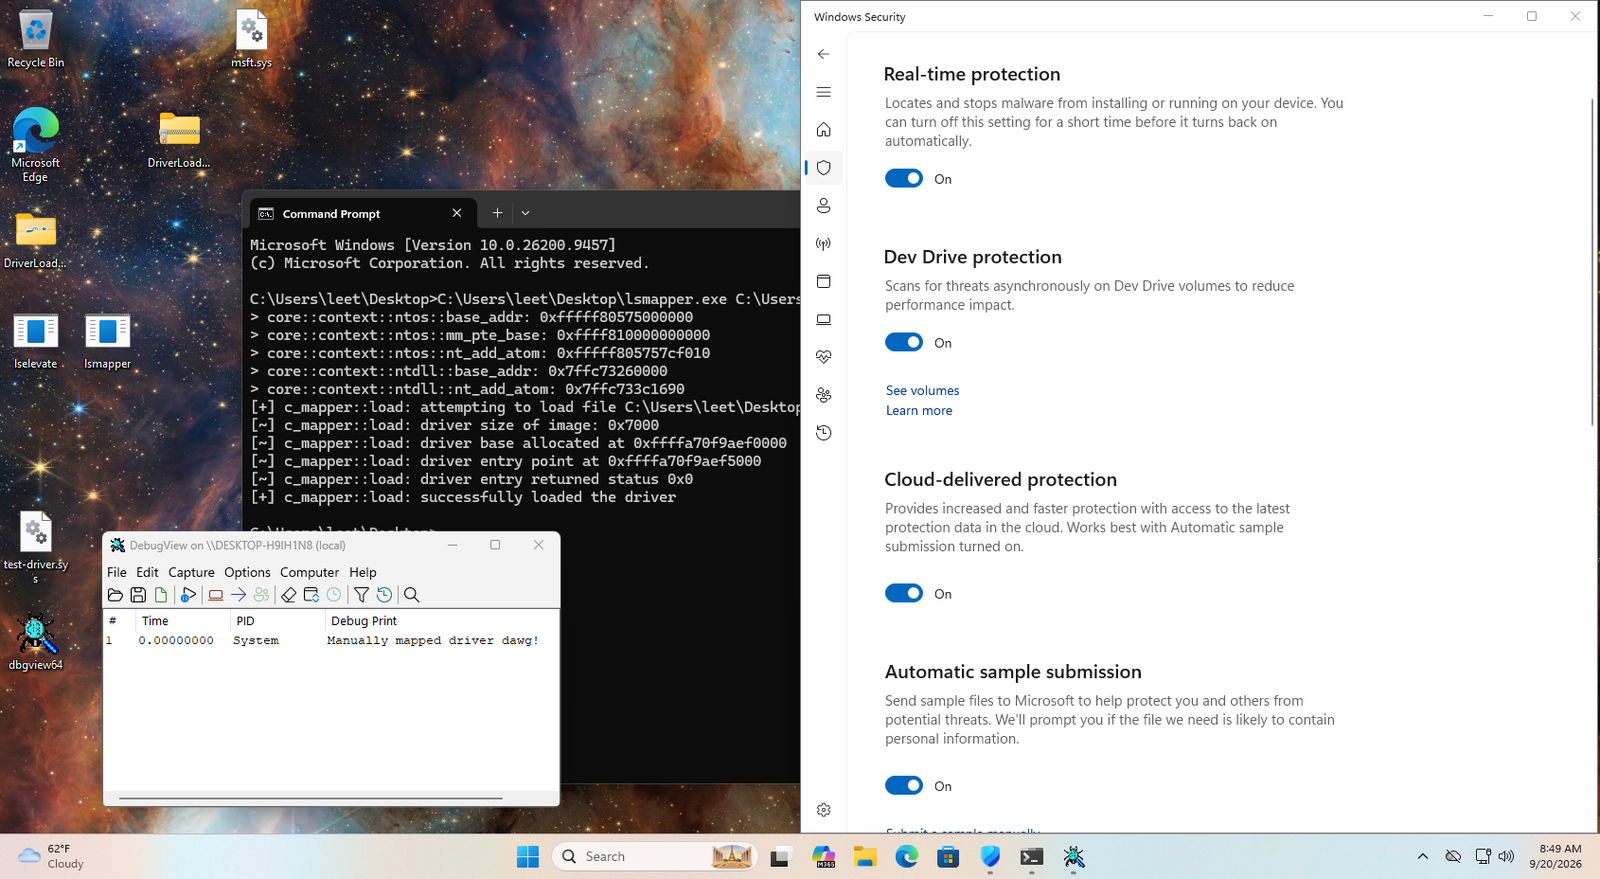
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
binary-exploitationexploit-frameworkspayload-development+3
40
nbs32k/localstrangerPoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 ioallocate/immapper
Demonstration of Abusing the Vulnerable driver AmdTools64.sys for Physical R/W.
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 jigerjain/interview_tips
Summary of Cyber Security interview questions I have been through, hope this helps
 0x4d31/awesome-oscp
A curated list of awesome OSCP resources
 warxim/vucsa
Deliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…
 rohilchaudhry/cve-2024-48208
This repo contains all the work surrounding the development of the PoC for CVE-2024-48208, and how a simple OOB(Out-of-bound) read can result in jail…
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…
 martinclauss/exim-rce-cve-2018-6789
This repository provides a learning environment to understand how an Exim RCE exploit for CVE-2018-6789 works.
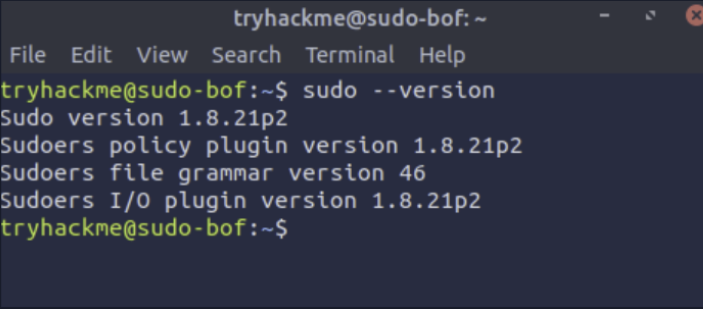 devteam6rabbit/cve-2019-18634-writeup
analysis of the sudo buffer overflow affect sudo version <1.8.26 and how to use GCC to compile publicly availible exploits
 nova-master/cve-2022-21894-payload-new
C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…
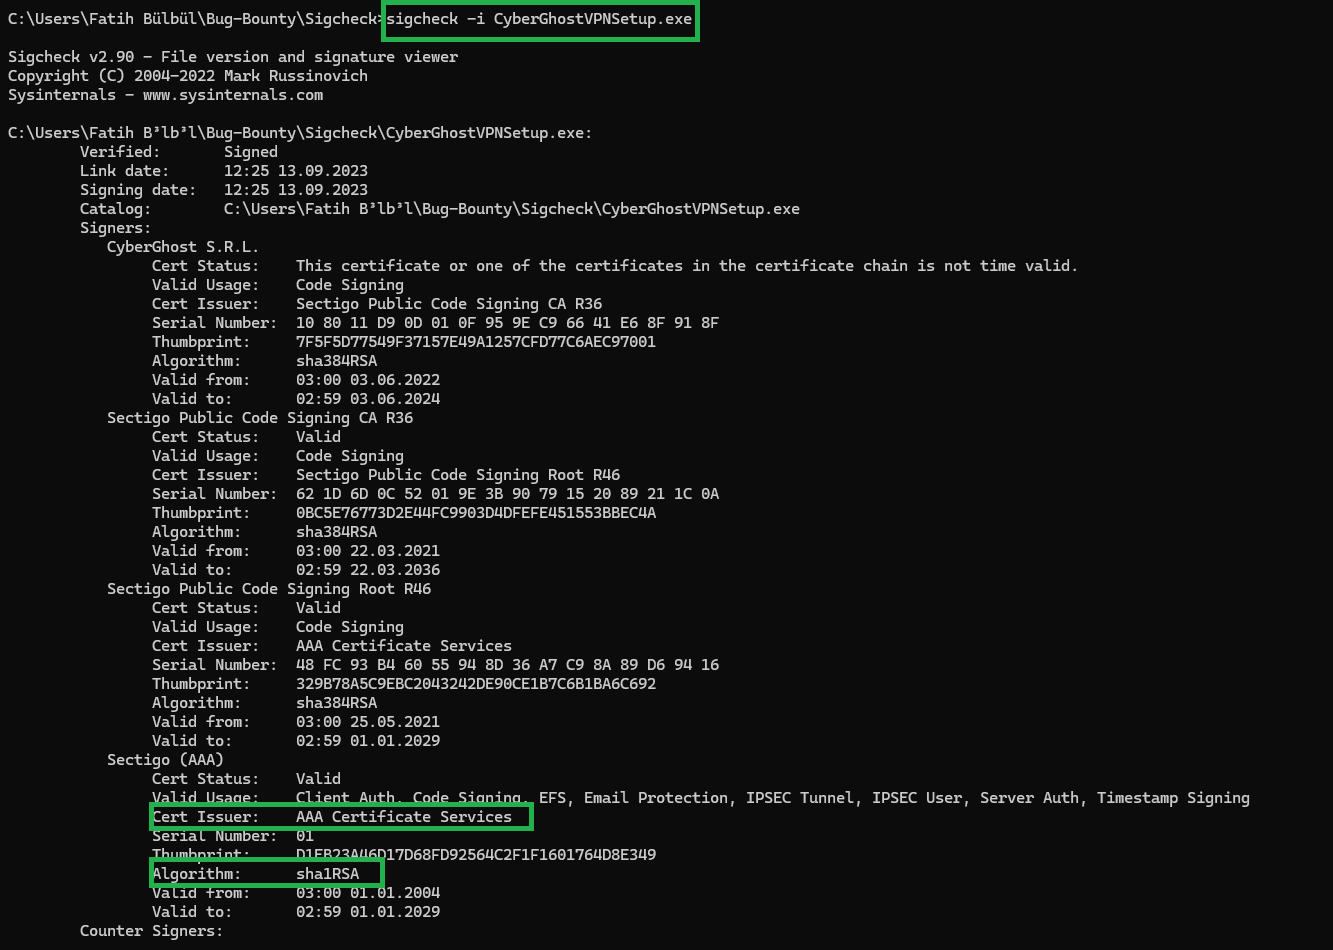 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 spiralbl0ck/linux-kernel-infoleak-6.12.-leveraged-to-do-cross-container-info-leak.-
POC shows how to leak postgresql stuff cause hugefile sub-system. Based on https://x.com/spendergrsec/status/1993794163880718700?s=20
 dinosn/cve-2026-25243
CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
 ahm3dgg/cve-2018-8611
Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.