

EternalBlueC
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
binary-exploitationeducationexploitation+7
613
bhassani/eternalbluecEternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
 rat5ak/cve-2026-50343-installservice-eop
CVE-2026-50343 InstallService StaticPluginMap EoP - standard user to SYSTEM
 riftsandroses/cve-2024-50986
An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
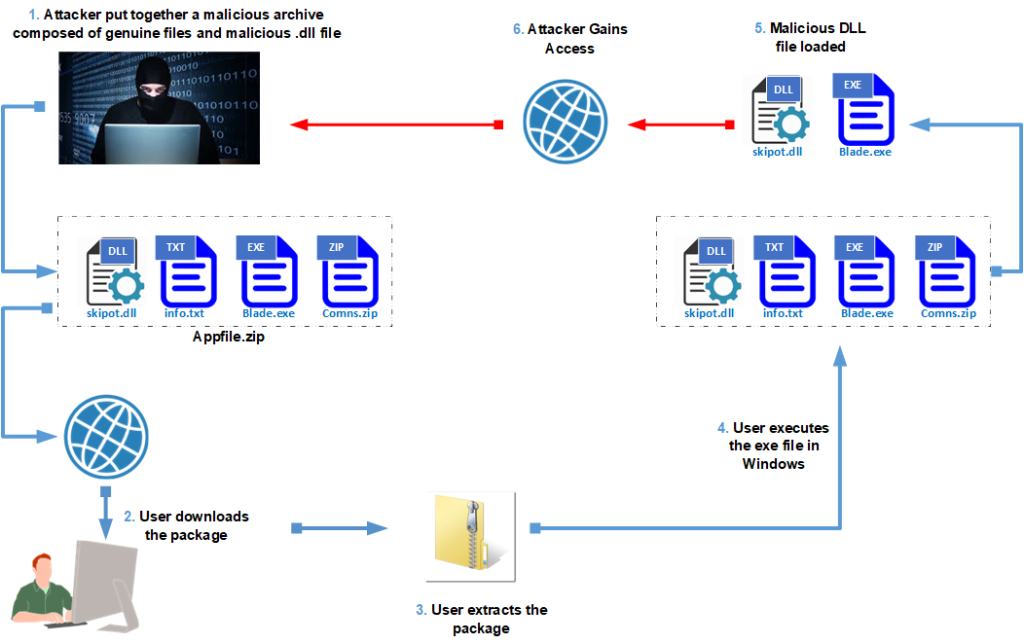 kobukovui/dll_injection_on_vlc
DLL Injection and CVE-2010-3124
 surajhacx/helakuruv.1.1-dllhijack
Helakuru Version 1.1 DLL Hijack - CVE-2024-48605
 sourceincite/cve-2018-8440
CVE-2018-8440 standalone exploit
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
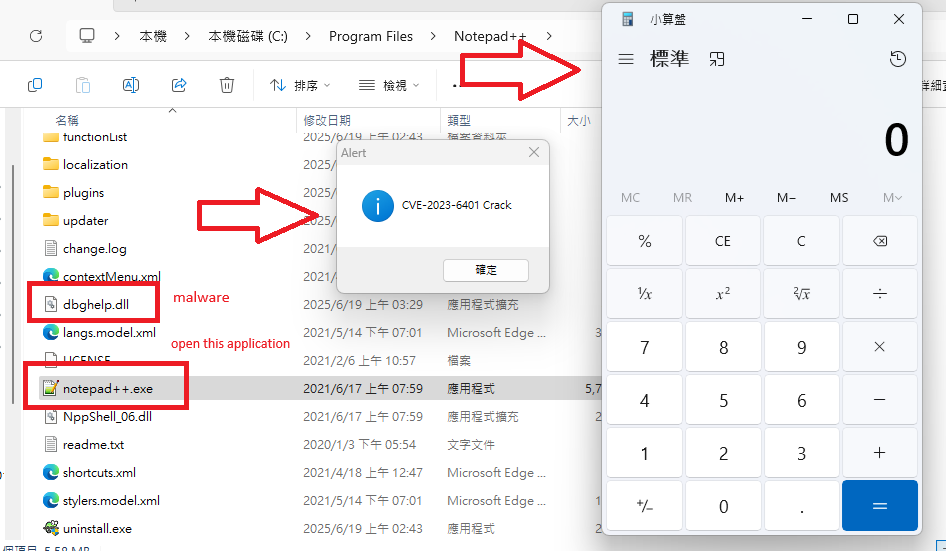 mekitoci/cve-2023-6401
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…
 0xkickit/icue_dllhijack_lpe-cve-2024-22002
Proof-of-concept exploit for CVE-2024-22002, demonstrating local privilege escalation via DLL hijacking in CORSAIR iCUE's update service to run code…
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 tiger3080/cve-2025-9267
Seagate Toolkit for Windows (Installer <2.35.0.6) is vulnerable to insecure DLL loading. The installer loads DLLs from the working directory without…
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 s3c/globalprotect-ca-cert-ipc
Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.
 egebalci/amber
Reflective PE packer.