
DirtyPipe-CVE-2022-0847
 vinukalana/dirtypipe-cve-2022-0847
This repository is developed to analysis and understand DirtyPipe exploit CVE-2022-0847
binary-exploitationeducationexploitation+3
2
vinukalana/dirtypipe-cve-2022-0847This repository is developed to analysis and understand DirtyPipe exploit CVE-2022-0847
 mranonymous234/sandbox-escape-ios-18.0-26.0
This uses CVE-2025-43407 as exploit and still testing working not gauranteed.
 therealdreg/hcon2026hwctf
Hardware Hacking CTF hcon2026hwctf - RISCV Hazard3 (@Wren6991) Exploiting by @b1n4ri0 @antoniovazquezblanco & @therealdreg
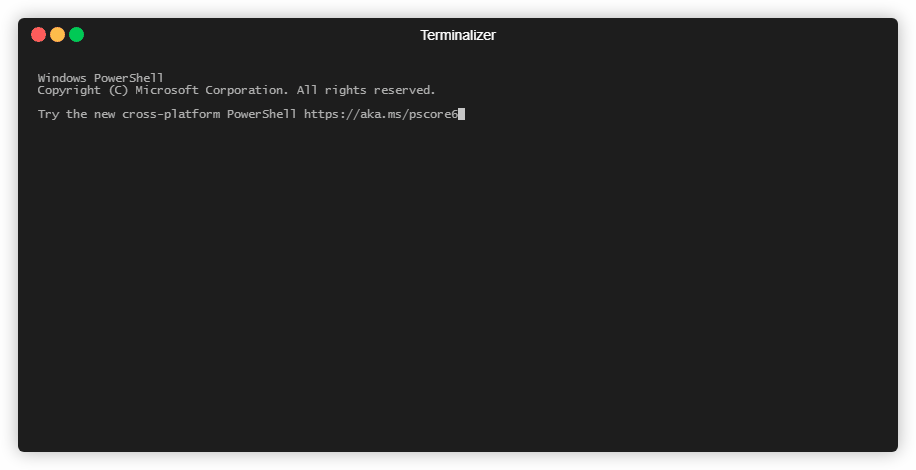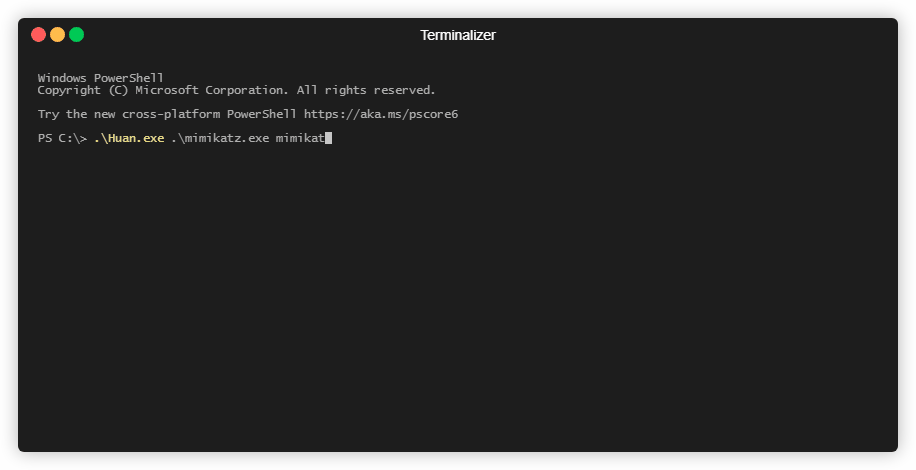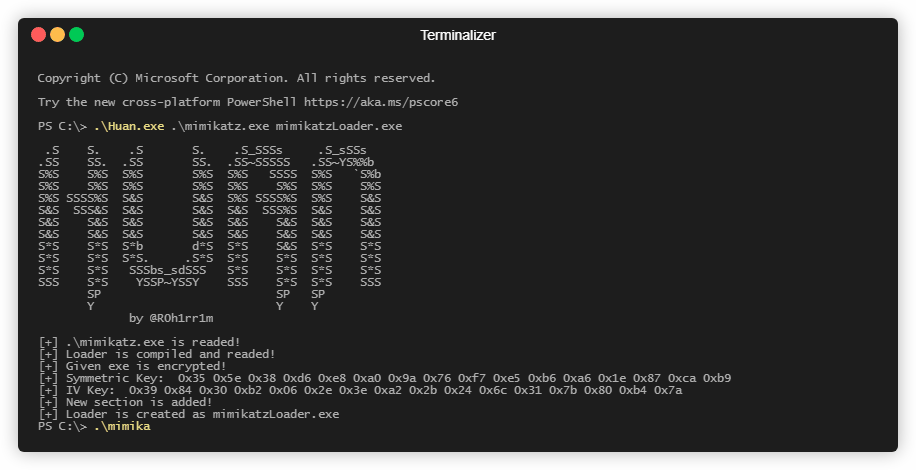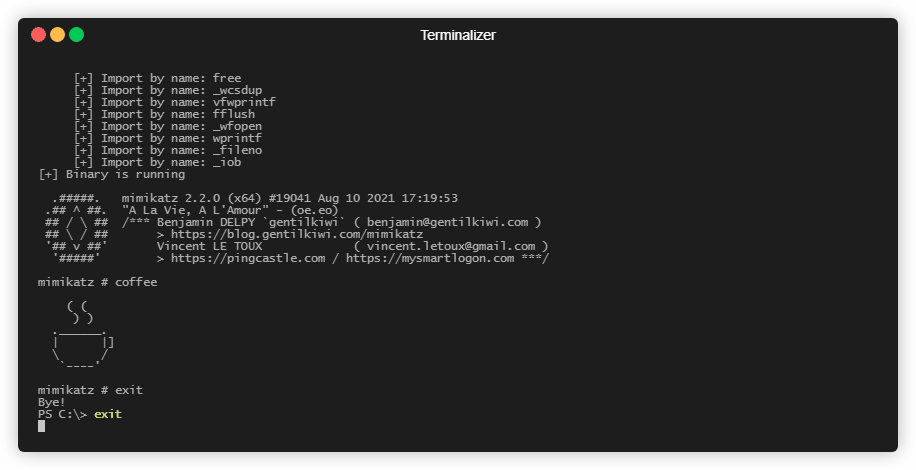 frkngksl/huan
Encrypted PE Loader Generator
 xen0vas/ascii-and-sub-encoder
This is a custom ASCII AND/SUB Encoder developed during my preparation for the legacy OSCE/CTP course
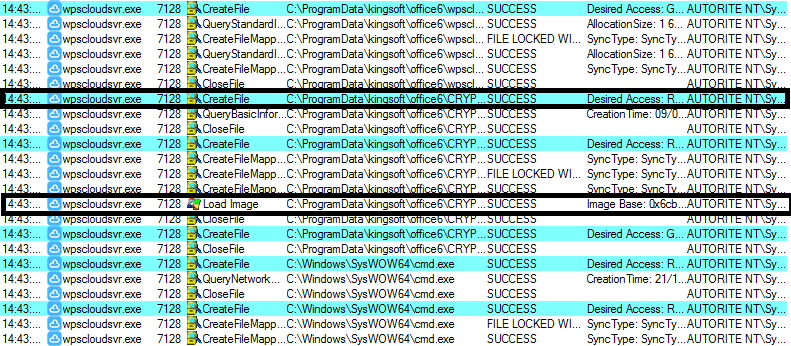 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 kungfulon/nf-tables-lpe
Linux kernel privilege escalation exploits targeting Netfilter's nf_table module, developed by Team Orca for multiple CVEs.
 watchtowrlabs/cve-2024-27130
PoC for CVE-2024-27130
 milo-d/cve-2016-6187_lpe
Kernel Exploit for CVE-2016-6187 (Local Privilege Escalation)
 uname1able/cve-2026-24291
Proof-of-concept exploit for CVE-2026-24291 targeting Windows 10 21H2 (build 19044.6937) AMD64, developed in C# with Visual Studio 2022.
 green-avocado/cve-2023-4911
https://www.qualys.com/2023/10/03/cve-2023-4911/looney-tunables-local-privilege-escalation-glibc-ld-so.txt
 wusijie/cve-2024-21338-1
PoC for the Untrusted Pointer Dereference in the appid.sys driver
 n1et/cve-2019-18634
An Python Exploit for Sudo vulnerability CVE-2019-18634
 mhanief/dirtypipe
Dirty Pipe Vulnerability Detection Script - RHSB-2022-002 Dirty Pipe - kernel arbitrary file manipulation - (CVE-2022-0847)
 bluedragonsecurity/cve-2011-1485-pkexec-exploit
CVE-2011-1485 - Linux pkexec and polkitd 0.96 race condition privilege escalation exploit. Developed in 2011 by Antonius (ev1lut10n / w1sdom)
 h4xl0r/winrar_ace_exploit_cve-2018-20250
This program is an script developed in Python which exploit the ACE vulnerability on WinRar - Vulnerability CVE-2018-20250