WinRAR-Exploit-Tool---Rust-Edition

A high-performance, memory-safe implementation of the WinRAR CVE-2025-8088 exploit tool, rewritten in Rust for better reliability and performance.

A high-performance, memory-safe implementation of the WinRAR CVE-2025-8088 exploit tool, rewritten in Rust for better reliability and performance.

Rust Weaponization for Red Team Engagements.

An experimental webkit-based kernel exploit (Arb. R/W) for the PS5 on <= 4.51FW

Go-based exploit for CVE-2021-3156, a sudo heap overflow vulnerability enabling local privilege escalation on Linux systems.

Labtainers: A Docker-based cyber lab framework

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

CVE-2025-21479 proof-of-concept, I think

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…

Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence

Implementation of CVE-2022-0847 as a shellcode

Disclosure of Accfly camera vulnerabilities: CVE-2020-25782, CVE-2020-25783, CVE-2020-25784, CVE-2020-25785.

Heap-based buffer overflow example based on CVE-2023-4504

Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…

CVE-2021-3156-Exploit-Demo

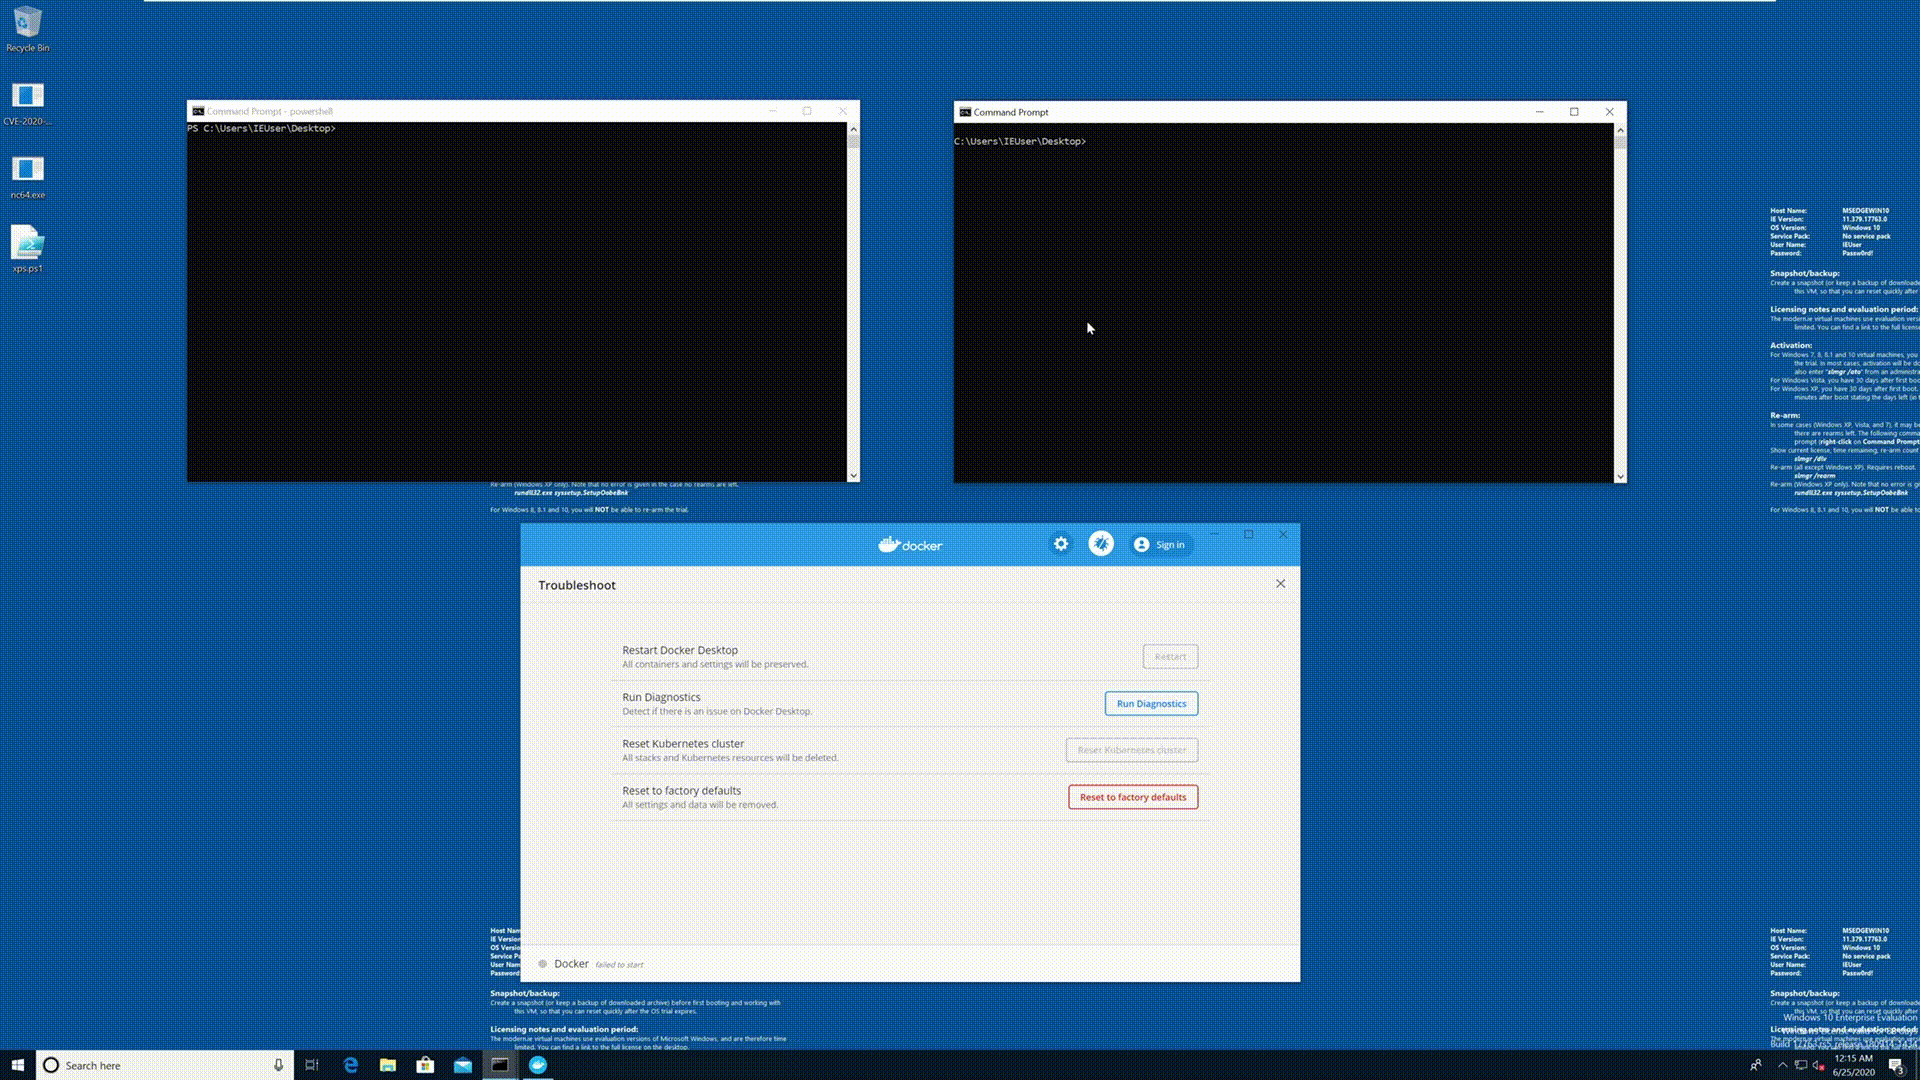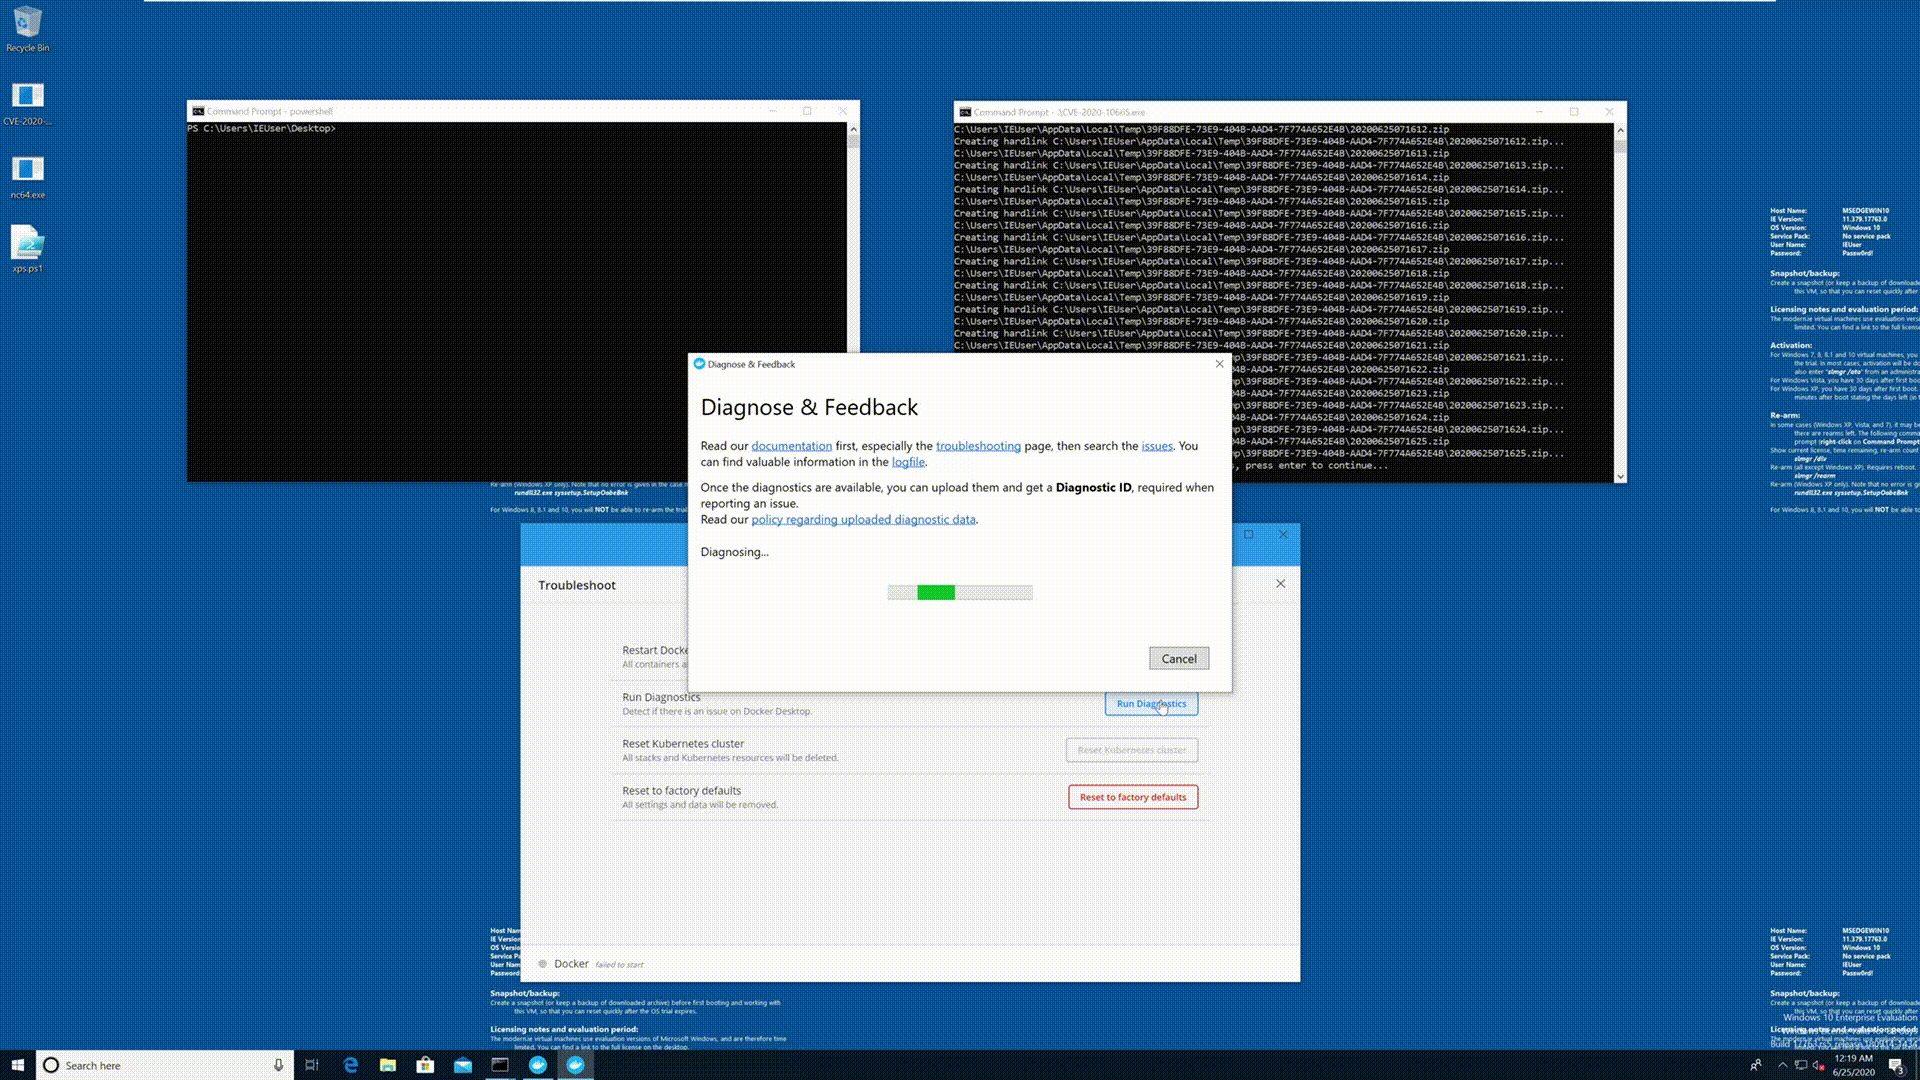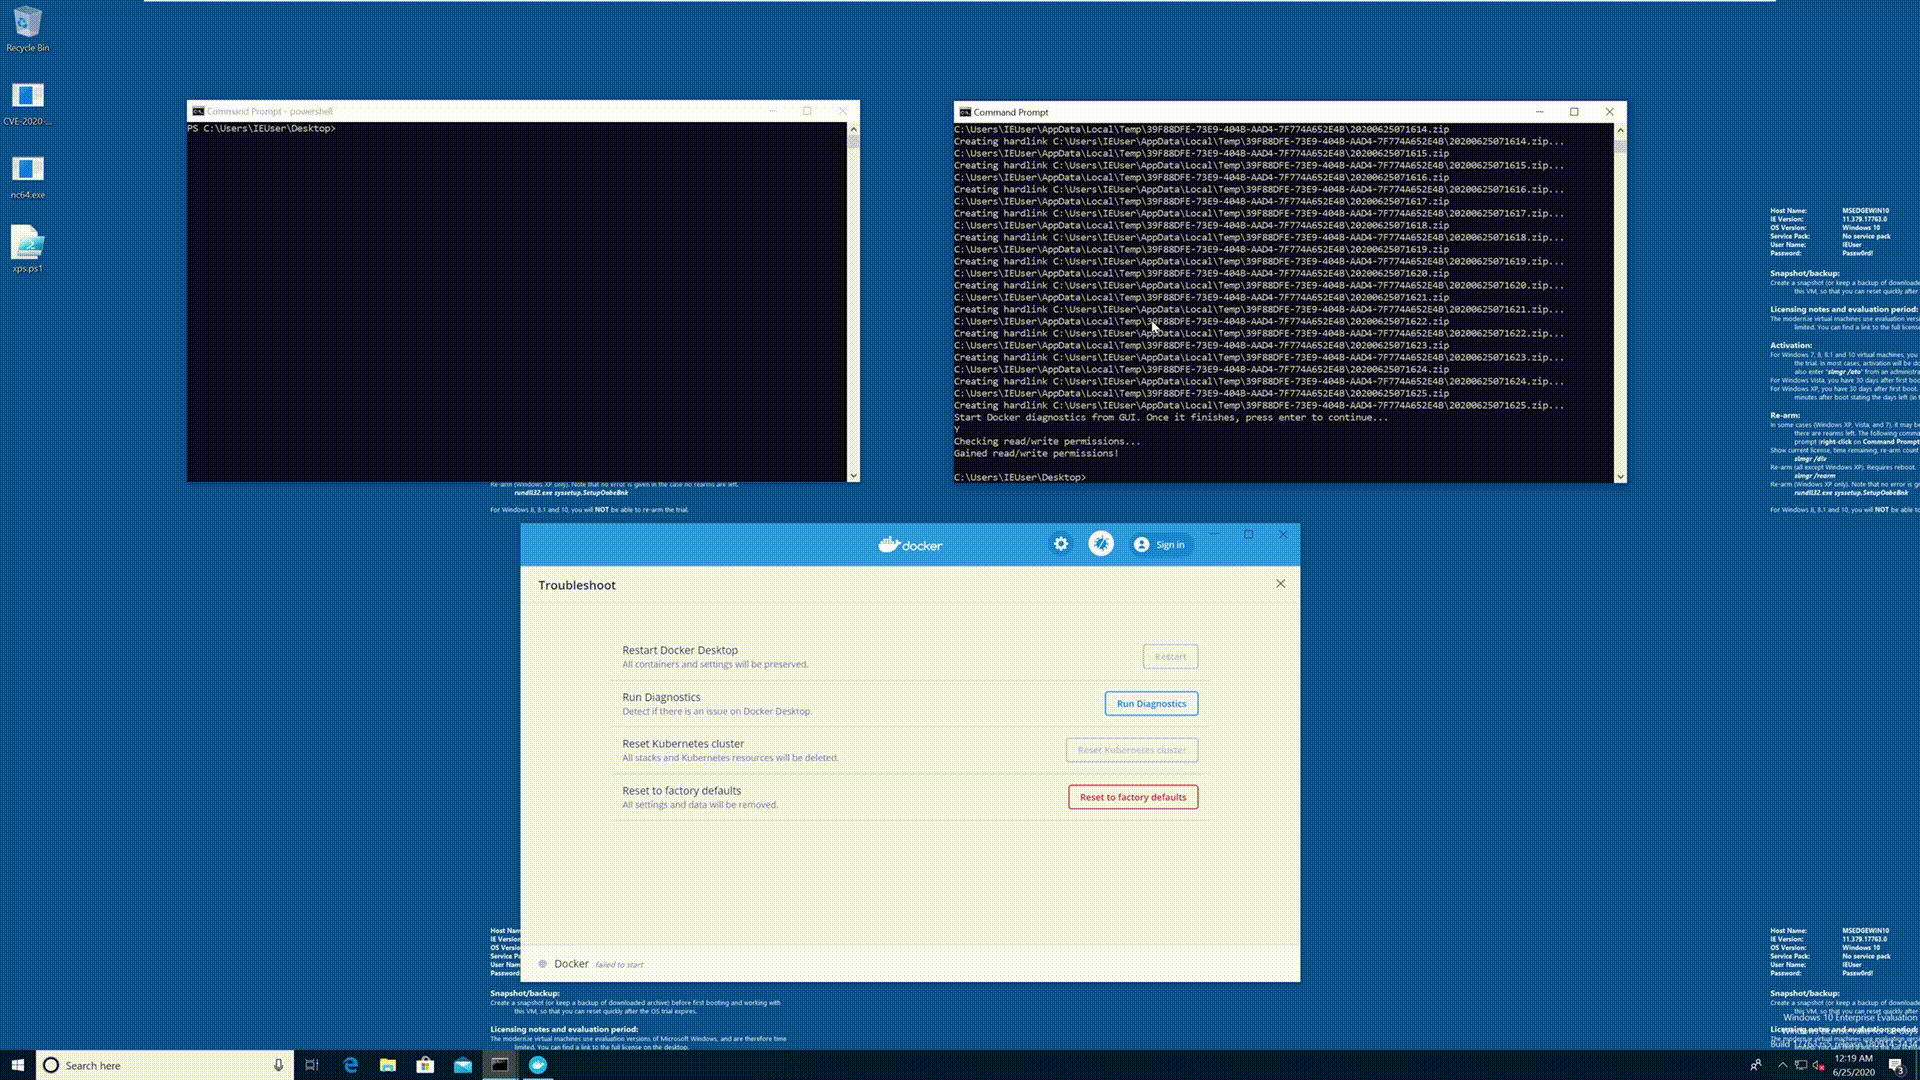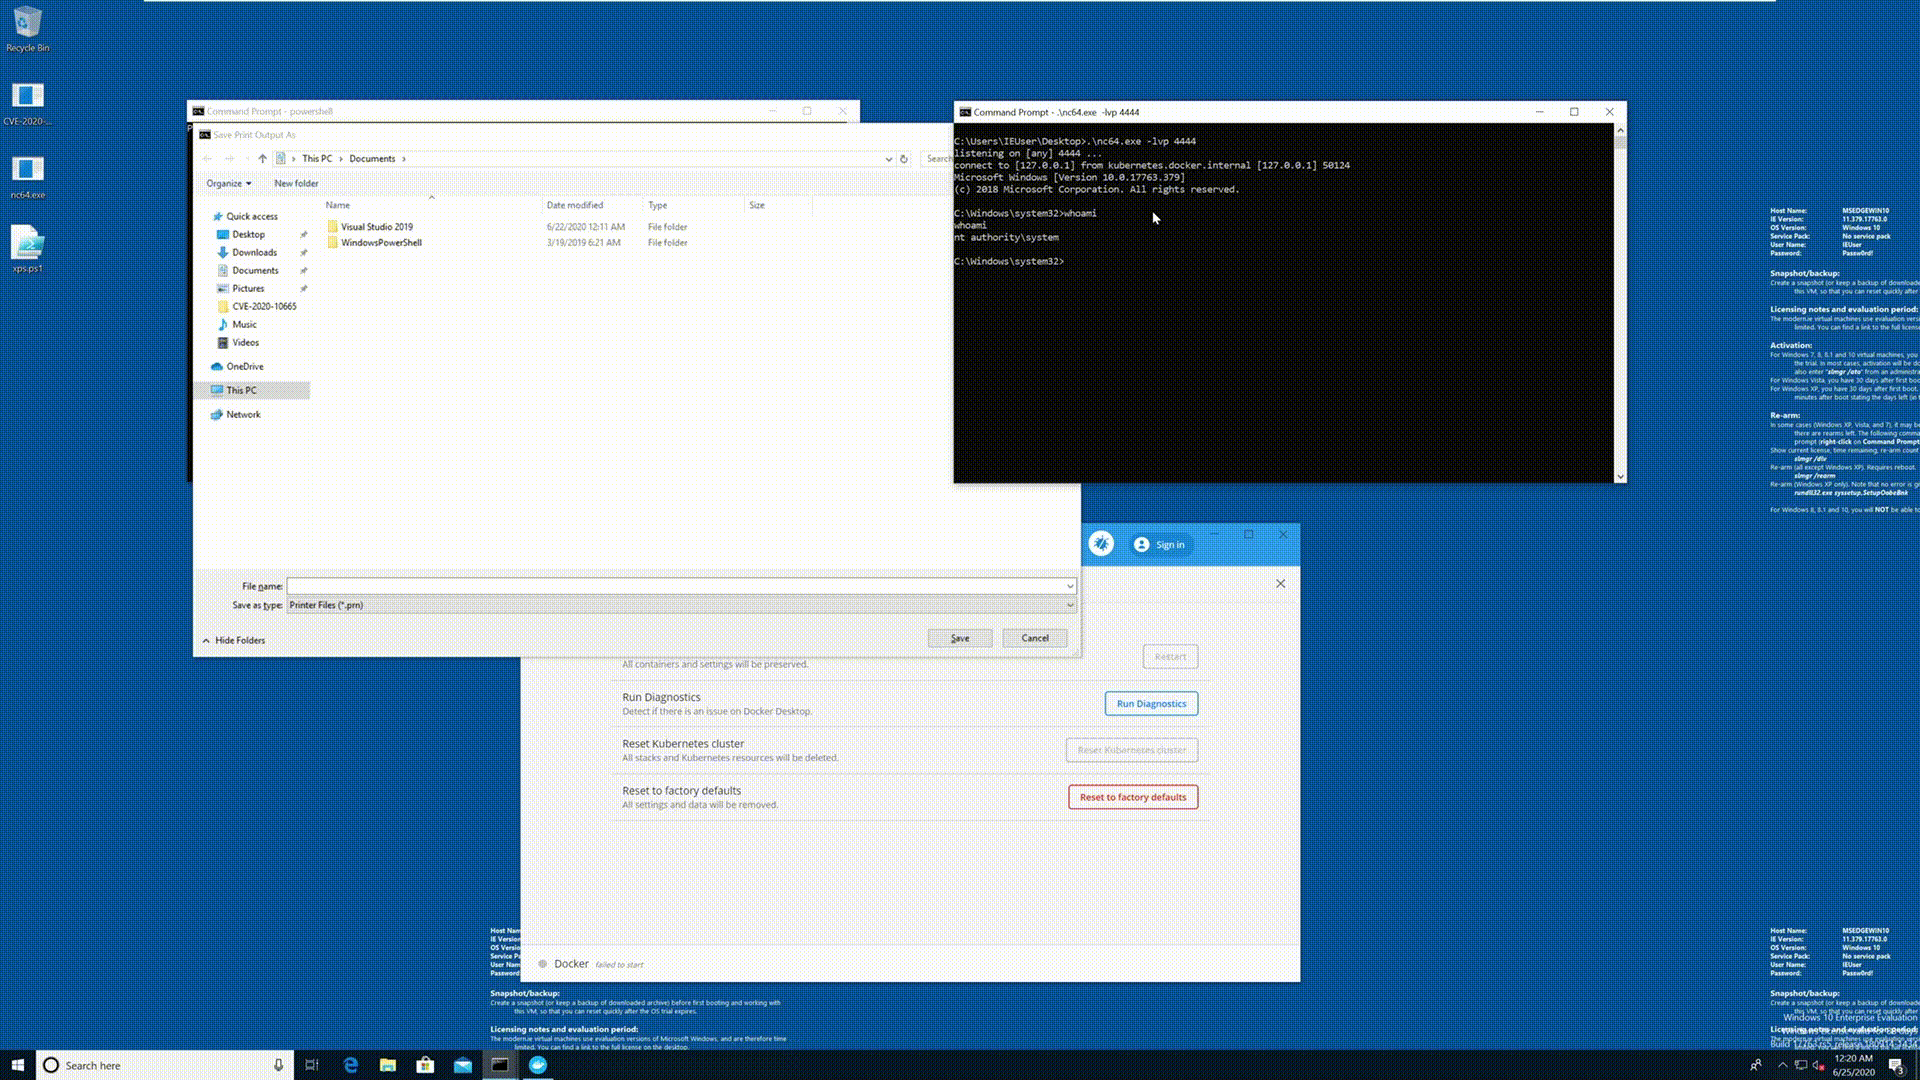
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation

CVE-2026-43499 (GhostLock) rtmutex remove_waiter() UAF local-root PoC adapted for Qualcomm Android 4.19 kernels (Redmi K40 / Snapdragon 870 class),…

GhostLock CVE-2026-43499 port for Galaxy Z Fold 8 (h8q)

Exploit for CVE-2025-0282: A remote unauthenticated stack based buffer overflow affecting Ivanti Connect Secure, Ivanti Policy Secure, and Ivanti…