
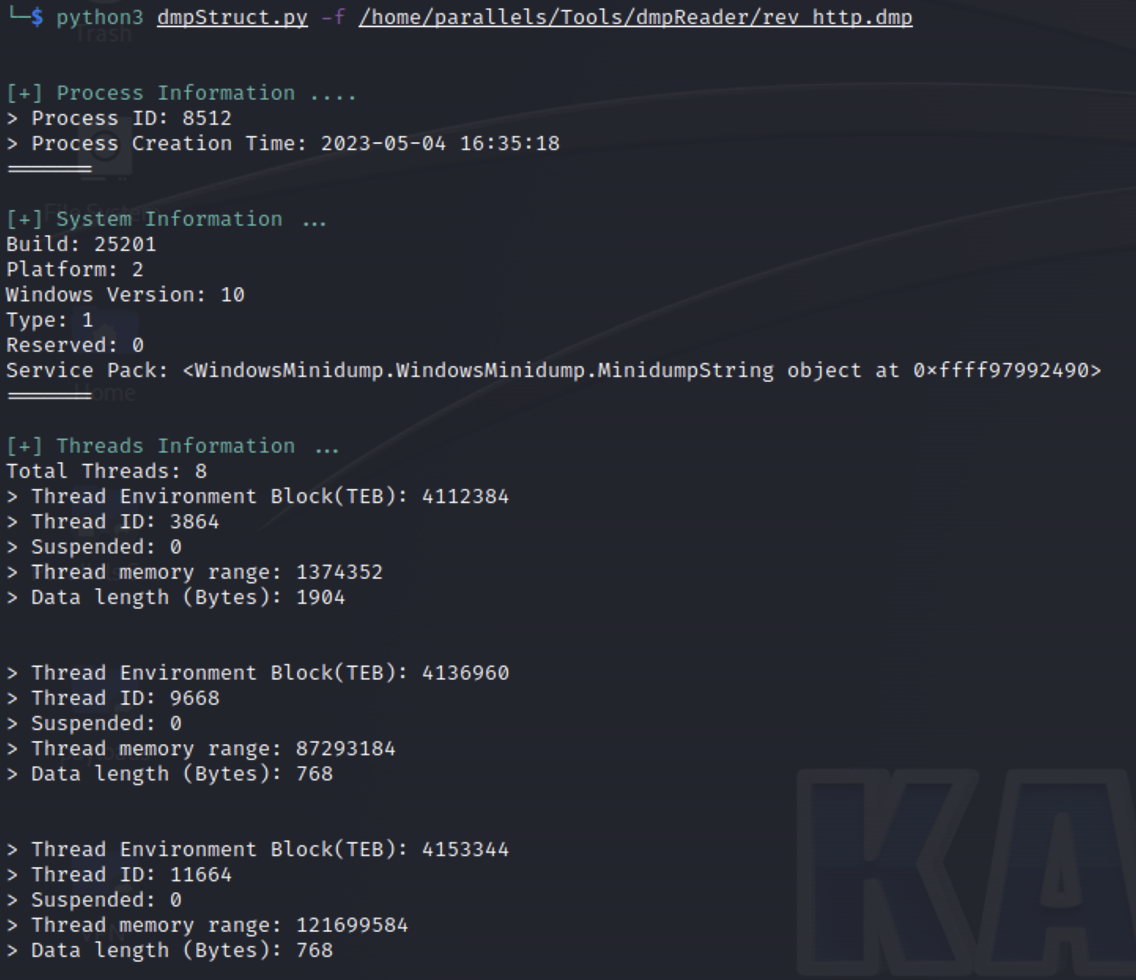
miniDumpReader
 gmh5225/minidumpreader
Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
binary-analysisdigital-forensicsforensics+3
gmh5225/minidumpreaderParses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
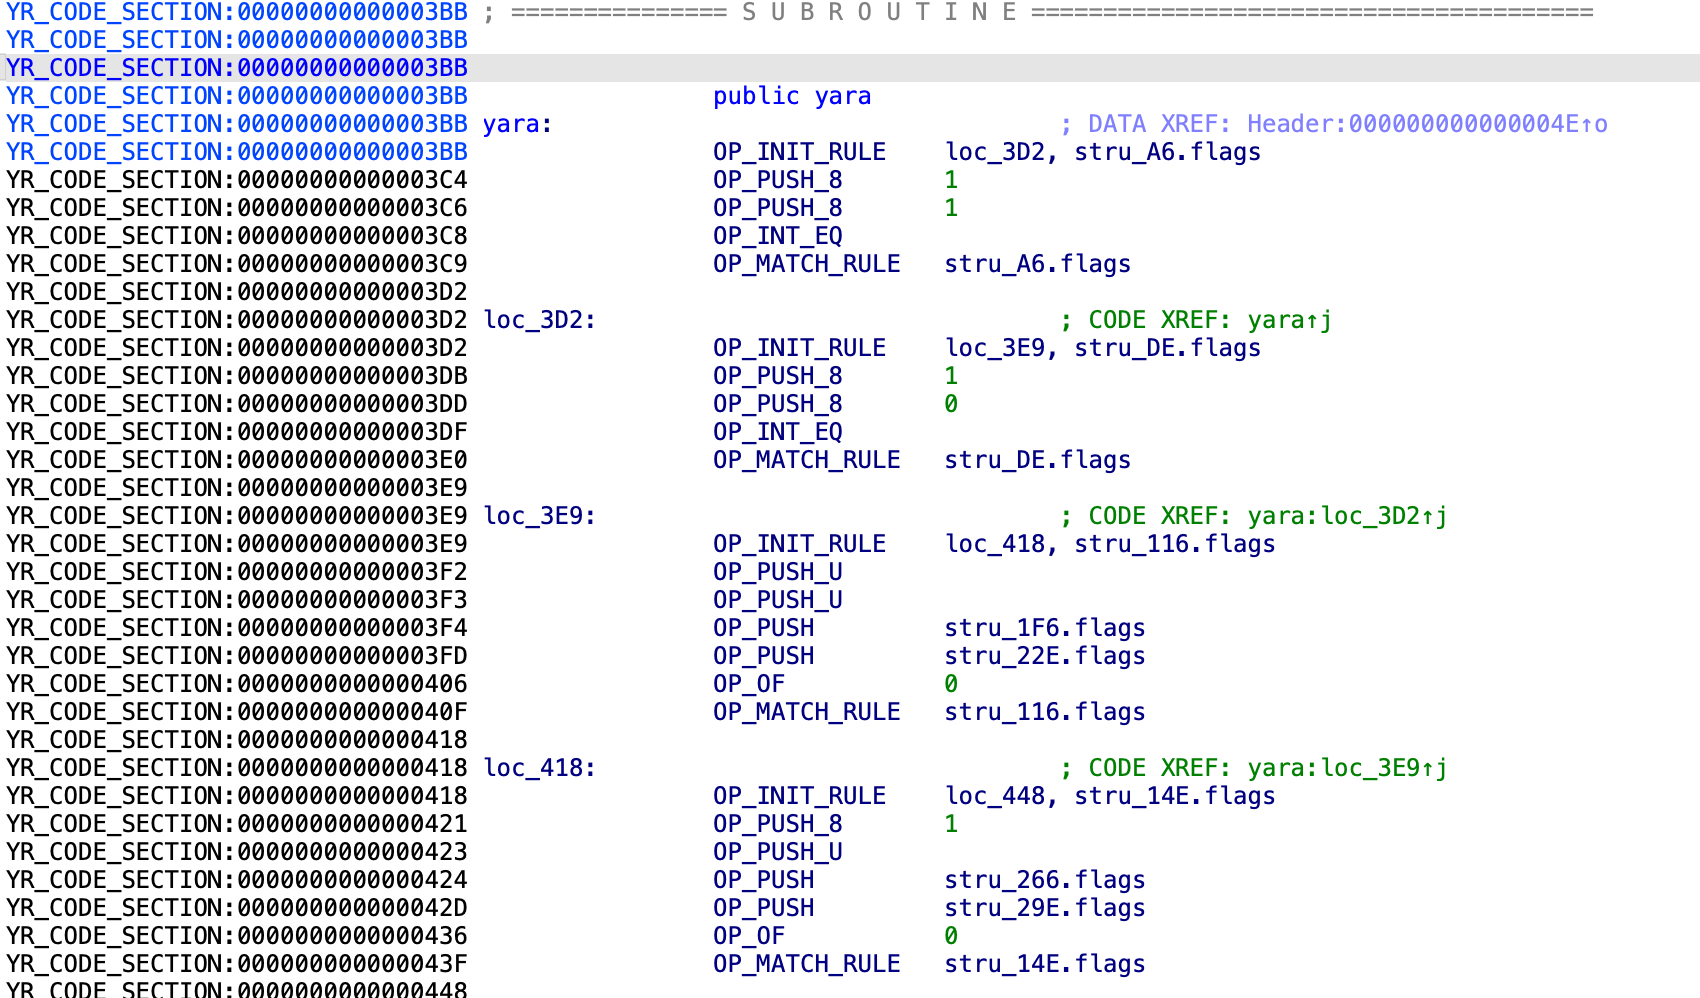 milankovo/yaravm
This repository contains an IDA processor for loading and disassembling compiled yara rules.
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 yo-yo-yo-jbo/macos_xprotect
Educational deep dive into Apple's built-in malware protection: signature databases, YARA rules, Gatekeeper integration, remediation binaries, and…
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 ald3ns/copy-as-yara
This is a little plugin to copy disassembly in a way that is usable in YARA rules!
 oalabs/findyara-ida
IDA python plugin to scan binary with Yara rules
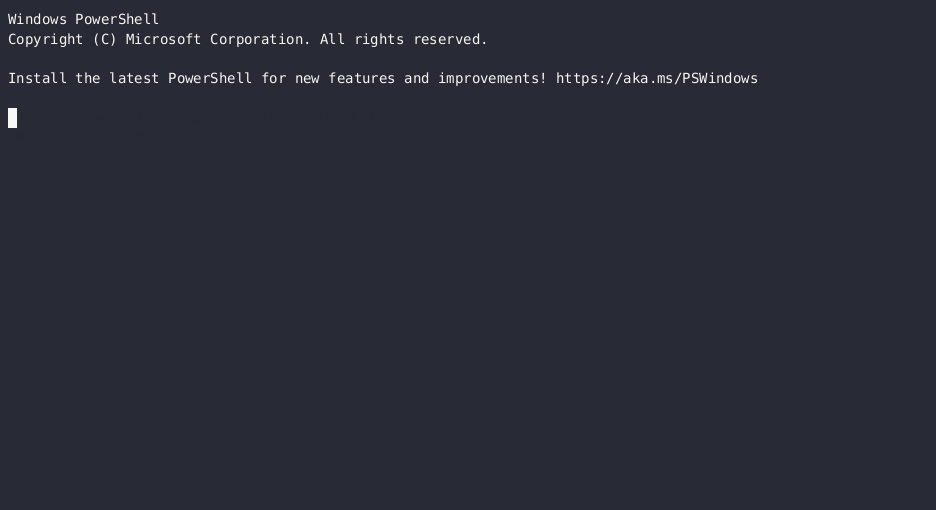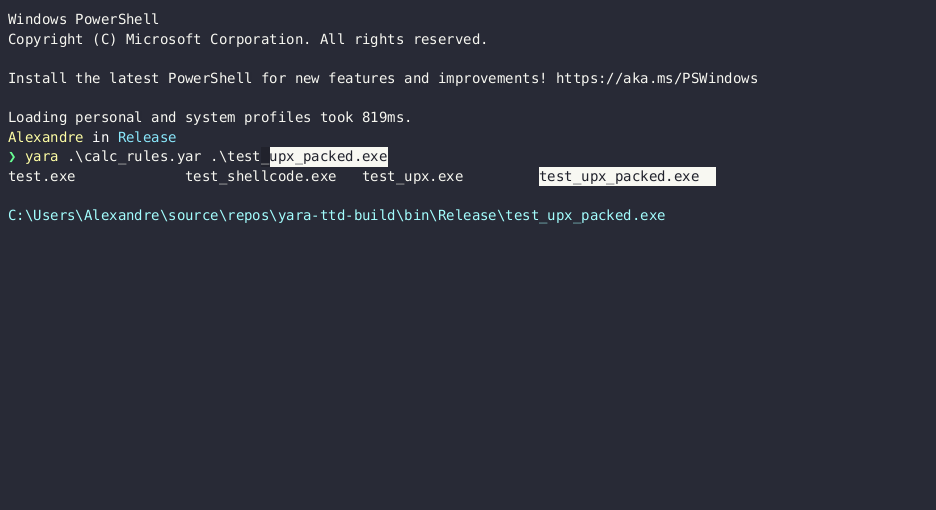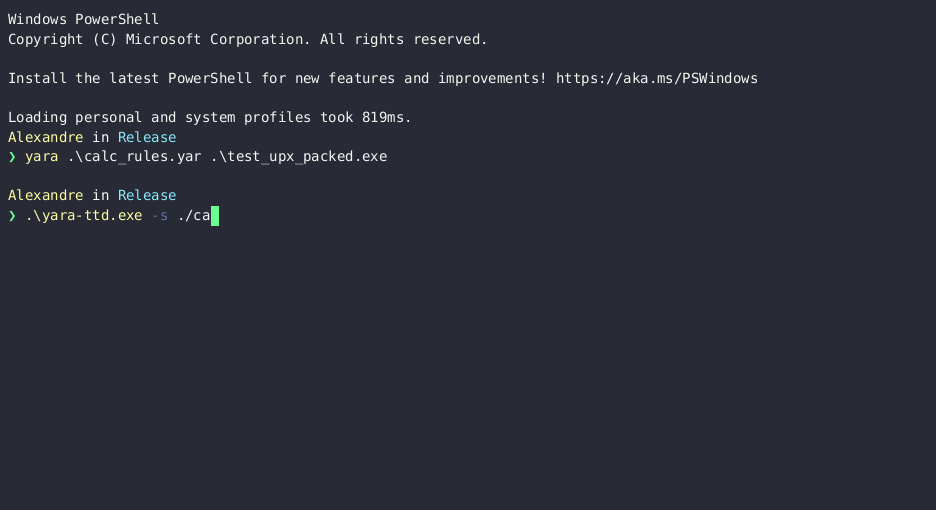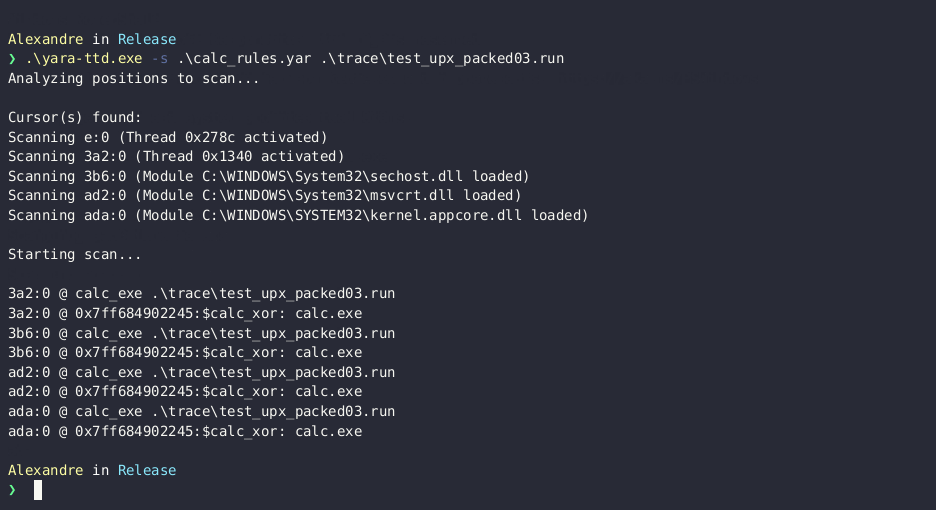 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
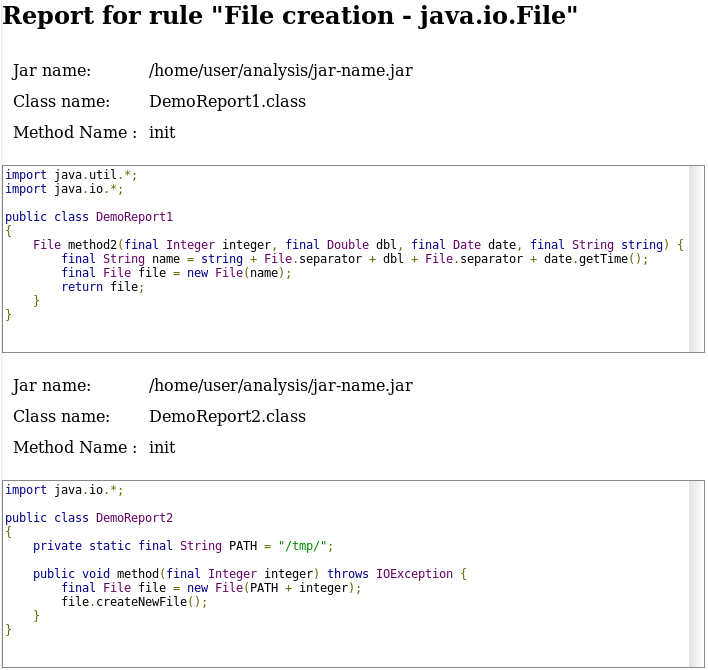 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules