
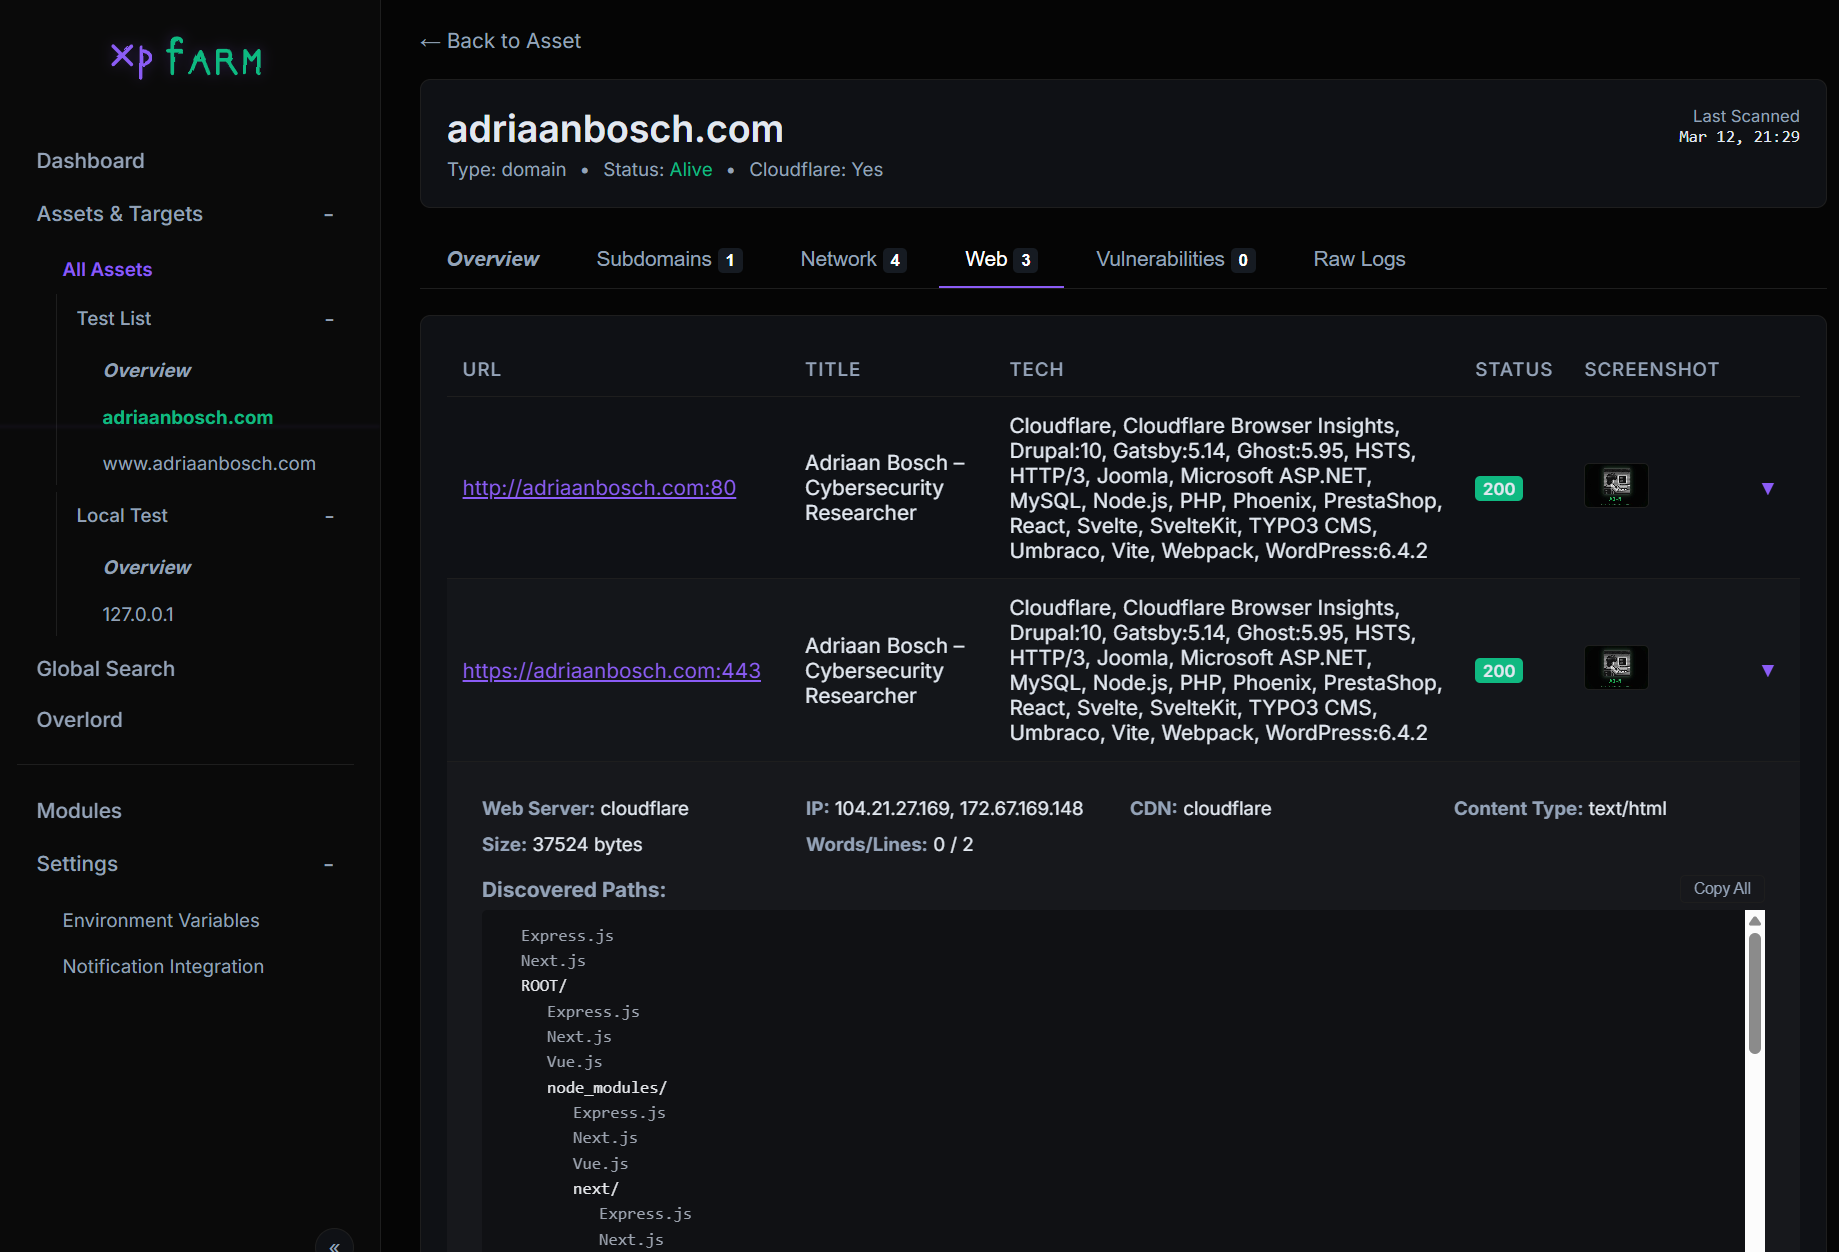
xpfarm
 a3-n/xpfarm
Free XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…
ai-securitybinary-analysiseducation+6
446 months ago
a3-n/xpfarmFree XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 gmh5225/awesome-llvm-security
Curated collection of LLVM security resources covering binary lifting, code obfuscation, static analysis, symbolic execution, sanitizers, and…
 keensecuritylab/binabsinspector
Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…
 sandflysecurity/sandfly-entropyscan
Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
 cq674350529/pocs_slides
my advisory, poc, slides and scripts related to IoT/protocol security
 liamg/extrude
:detective: Analyse binaries for missing security features, information disclosure and more...
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 ridhinva/linux-kernel-algif-aead-checker
Scanner: CVE-2026-31431 Linux kernel algif_aead Copy Fail vulnerability checker — Python PoC for heap overflow path
 fuzzinglabs/octopus
Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)
 abhi-r3v0/adhrit
Android Security Suite for in-depth reconnaissance and static bytecode analysis based on Ghera benchmarks.
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 we5ter/scanners-box
The Ultimate Open-Source Security Arsenal for Hackers, Enterprises, and AI Agents——面向极客、企业与 AI 智能体的全域开源网络安全工具矩阵
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 0sec-labs/0
Open-source AI security harness. Includes a web UI for code analysis, pentesting, vulnerability research, reverse engineering, verification, and…
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…