Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
624 results
SHA-256-Backdoor-Discovery-Engine preview

SHA-256-Backdoor-Discovery-Engine

GitHubpolllogamer/sha-256-backdoor-discovery-engine

Detects potential backdoors in SHA-256 hashes using cryptographic analysis and pattern recognition. Designed for malware analysis and security…

binary-analysiscryptographyeducation+3
6
9 months ago
StegoScan preview

StegoScan

GitHublcbower33/stegoscan

Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…

ai-securitybinary-analysiscrawler+7
1091 year ago
datadome-vm preview

datadome-vm

GitHubxkiian/datadome-vm

Reverse engineering the new Datadome VM 🔥

anti-botbinary-analysiscaptcha-bypass+3
1317 months ago
AFLplusplus preview

AFLplusplus

GitHubaflplusplus/aflplusplus

AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…

binary-analysisdns-fuzzingdynamic-analysis-sandboxing+3
6.8k29 days ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k23 days ago
LibAFL preview

LibAFL

GitHubaflplusplus/libafl

Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...

binary-analysisdynamic-analysis-sandboxingeducation+5
2.6k16 days ago
speakeasy preview

speakeasy

GitHubmandiant/speakeasy

Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…

binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2.1k2 days ago
Firmware_Slap preview

Firmware_Slap

GitHubchristhecoolhut/firmware_slap

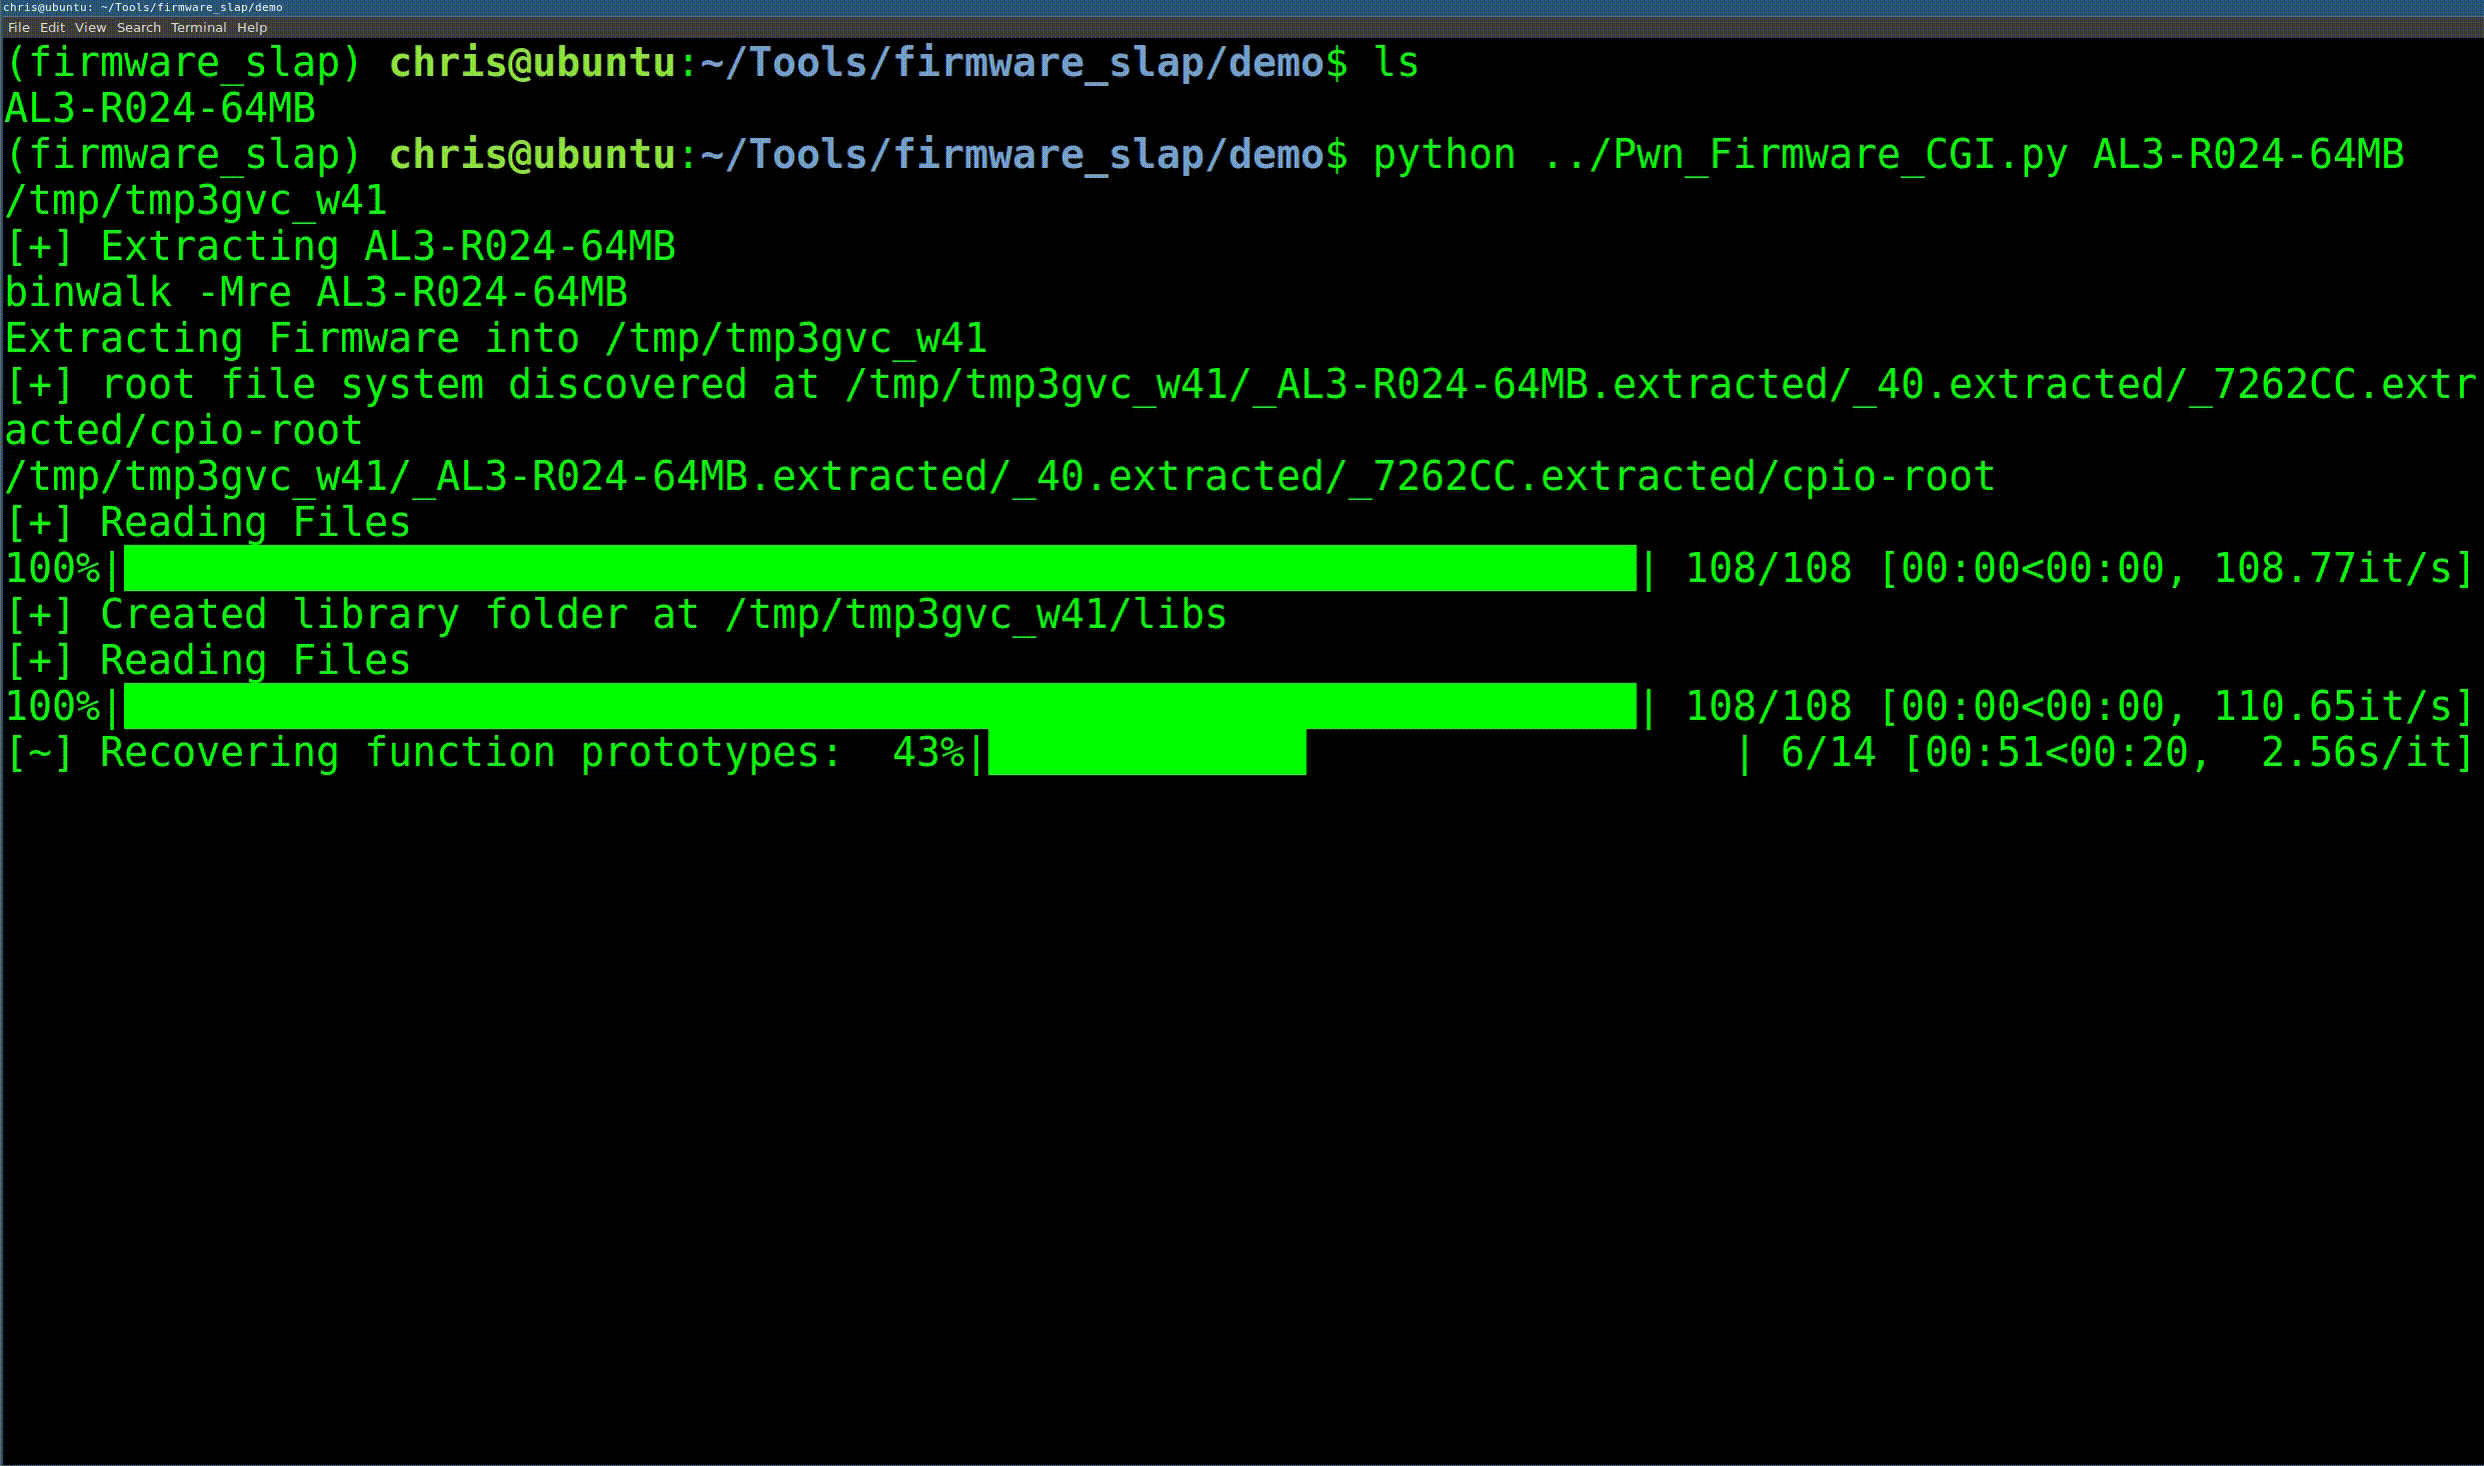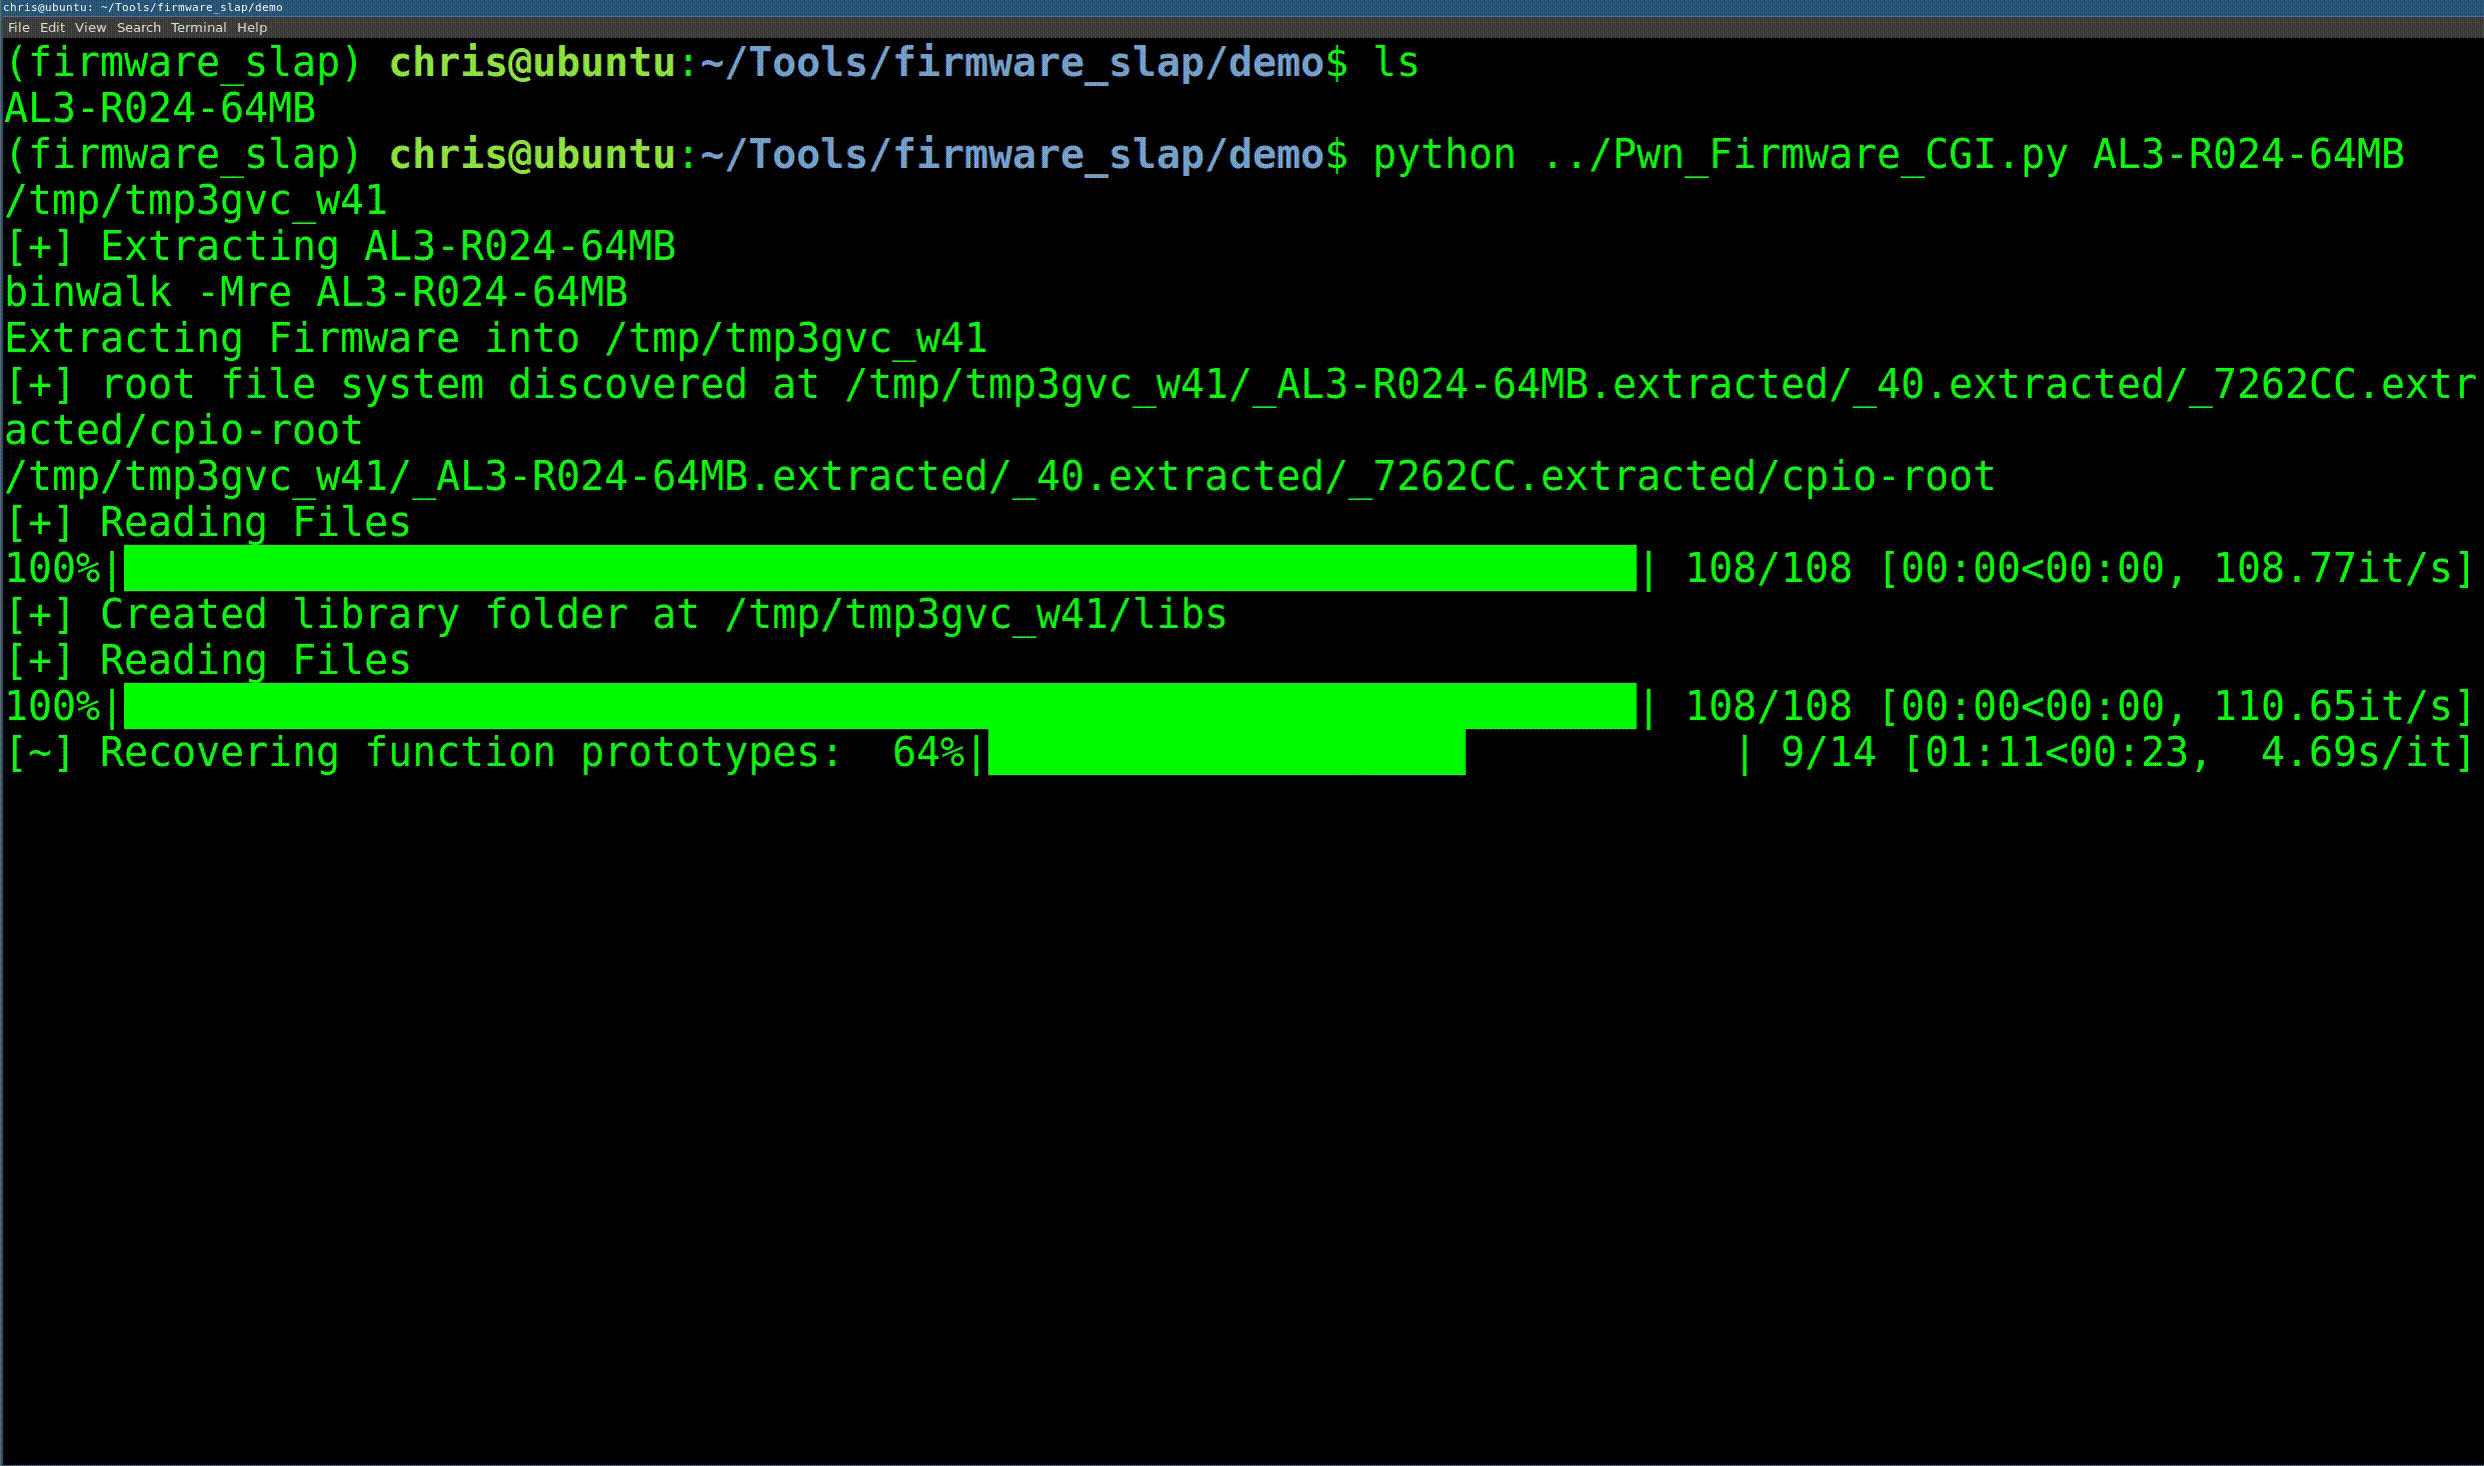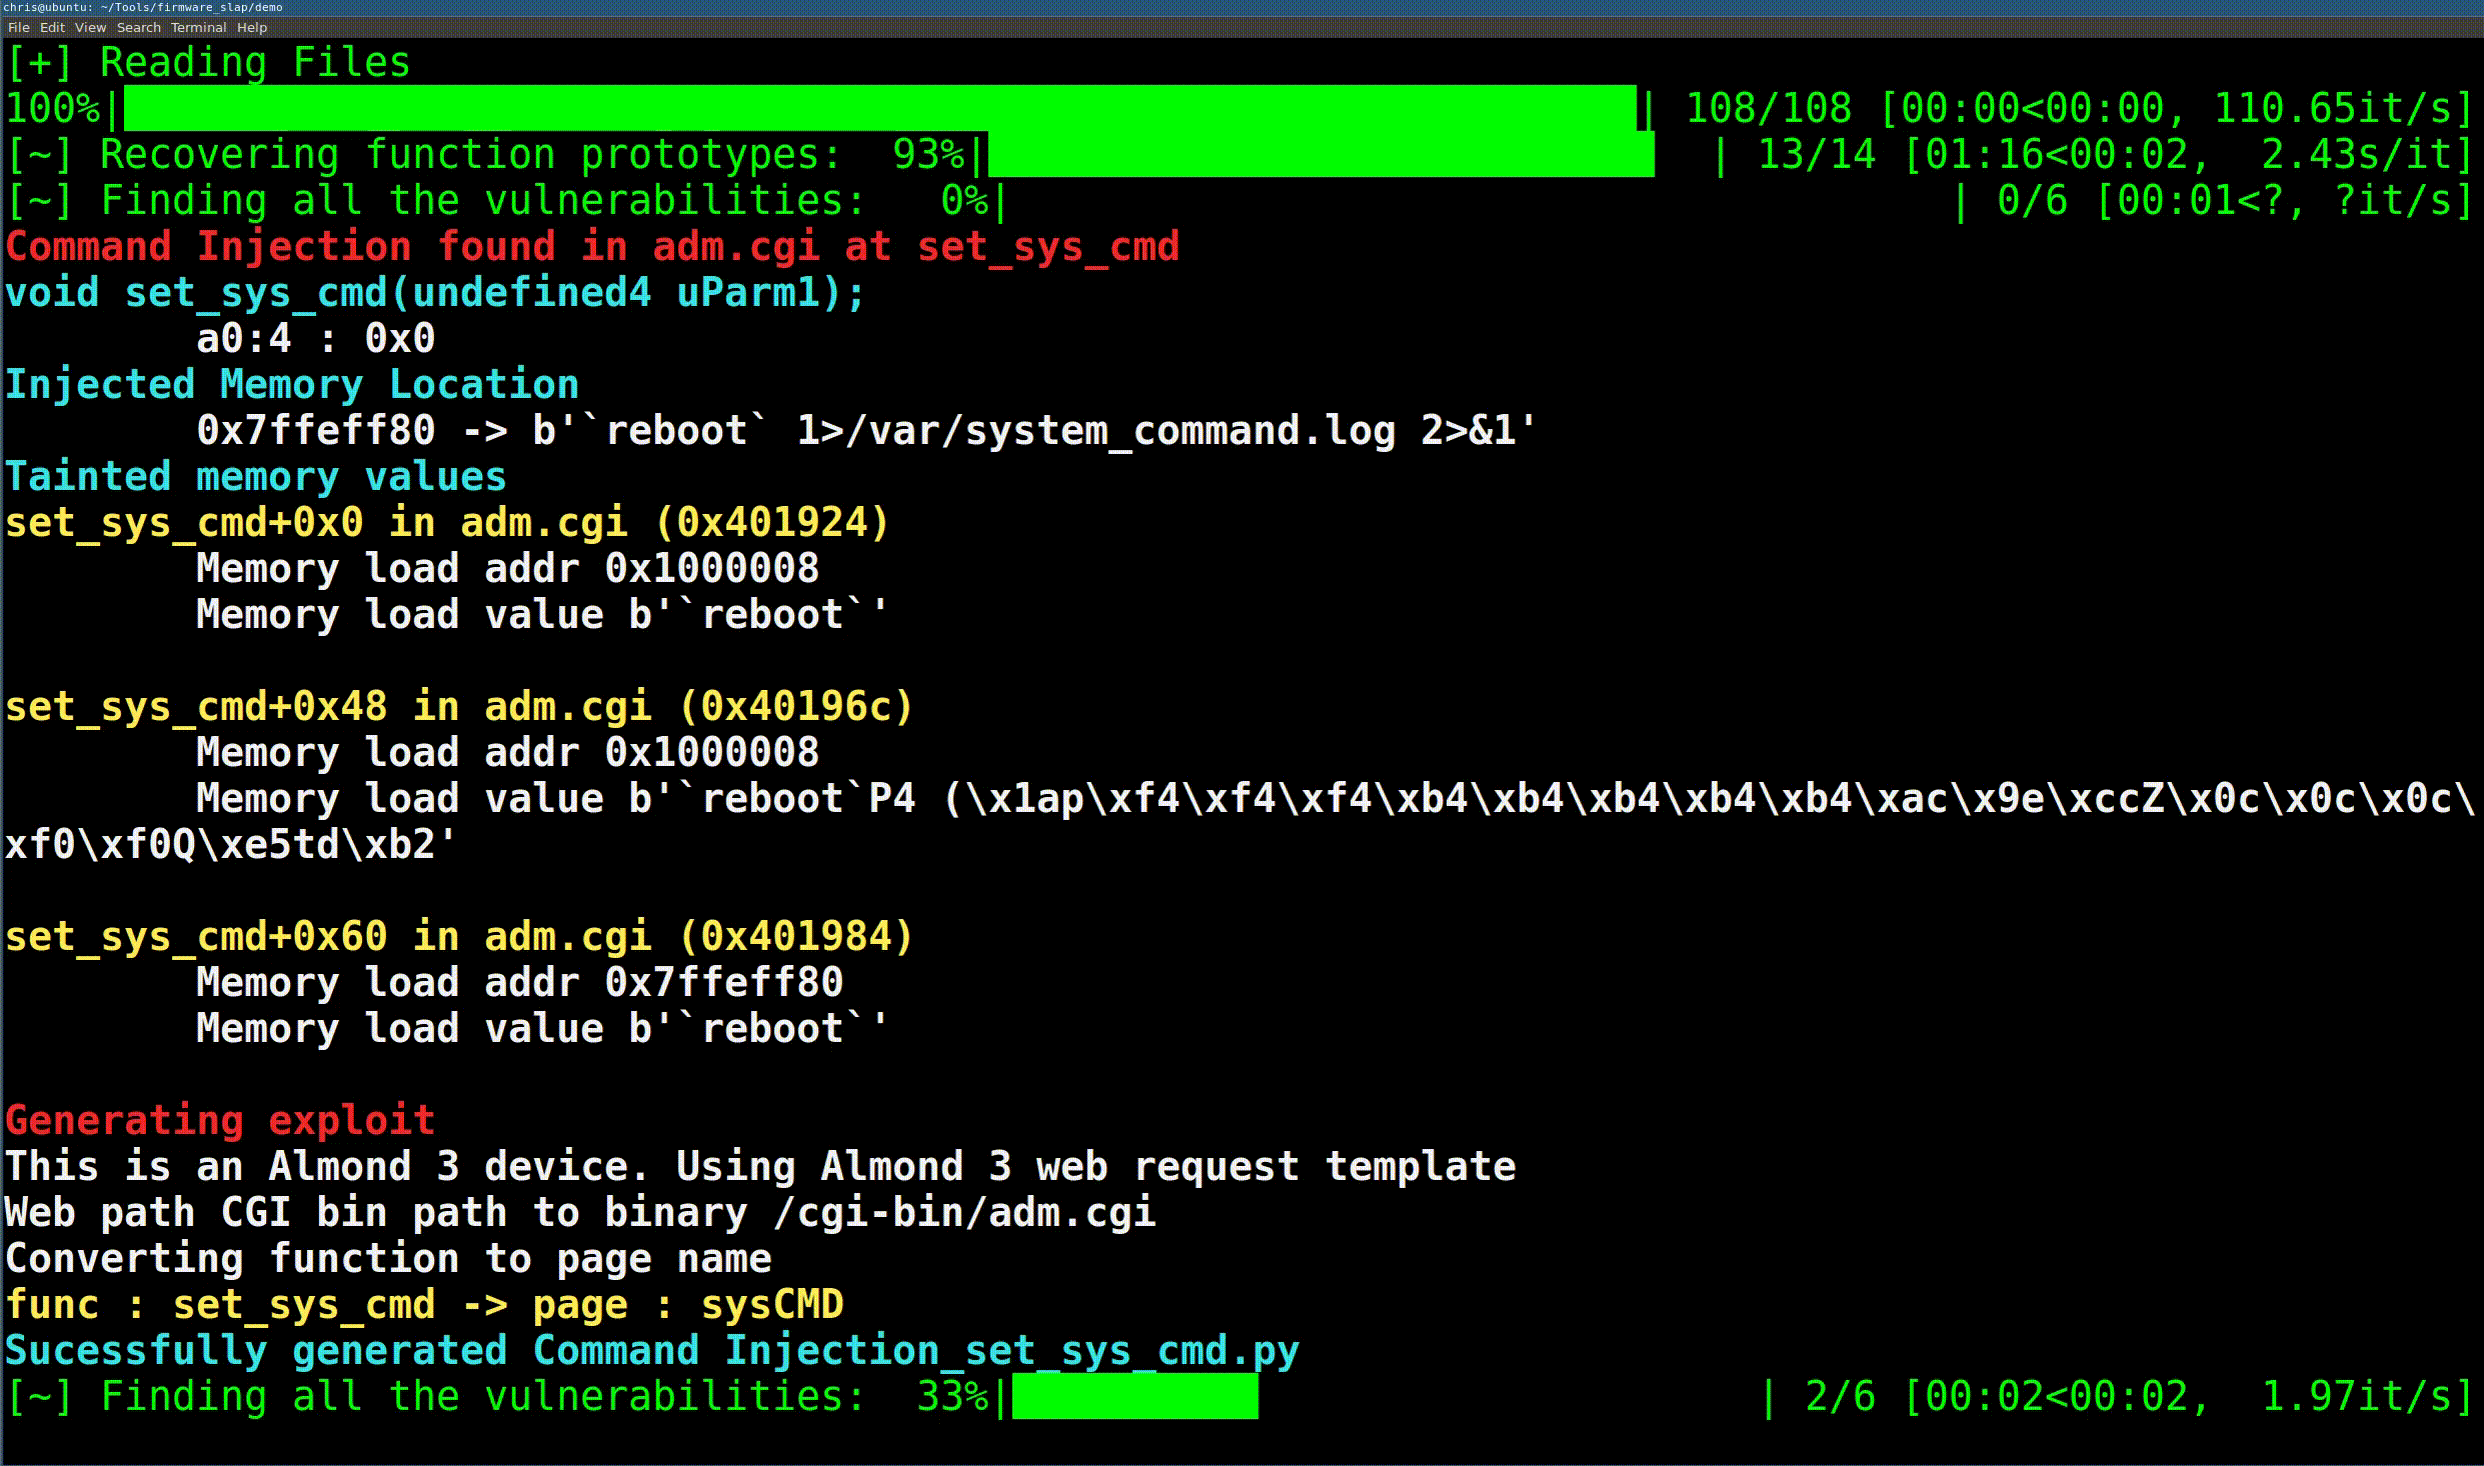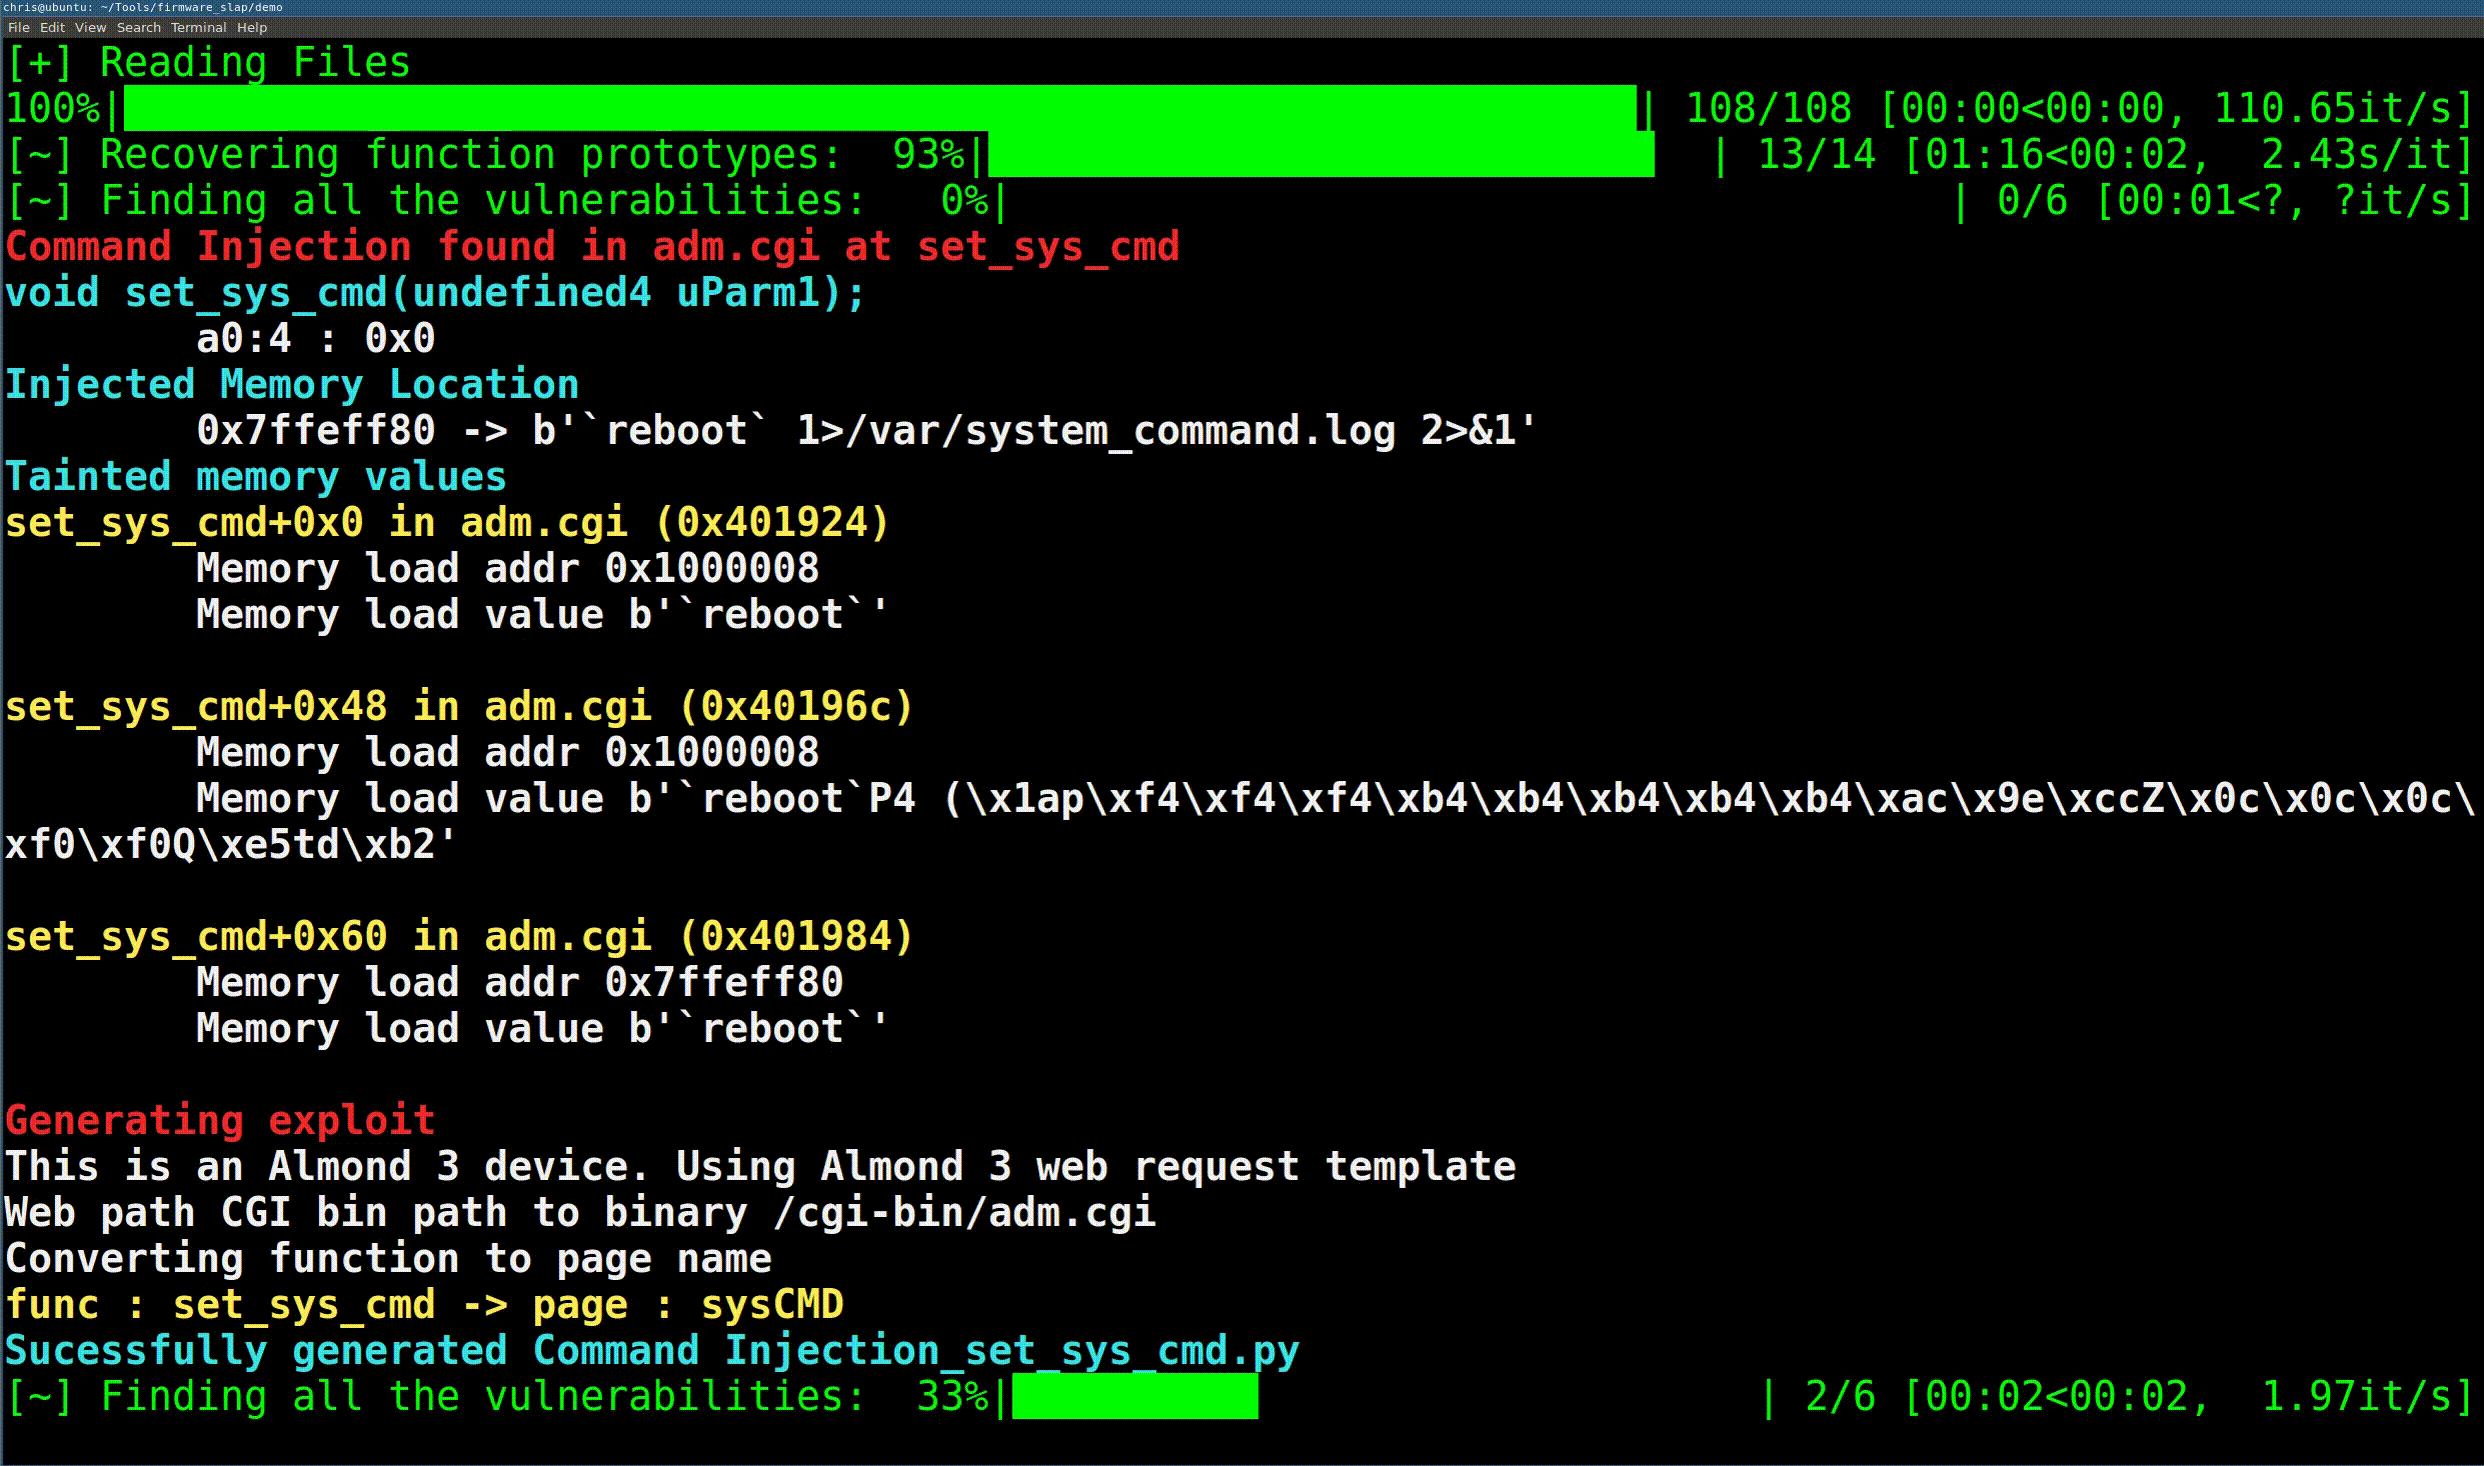
Discovering vulnerabilities in firmware through concolic analysis and function clustering.

binary-analysisexploitationfirmware-analysis+1
4766 years ago
B2R2 preview

B2R2

GitHubb2r2-org/b2r2

B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…

binary-analysisdynamic-analysis-sandboxingeducation+4
55115h 6m ago
ioctlance preview

ioctlance

GitHubzeze-zeze/ioctlance

A tool that is used to hunt vulnerabilities in x64 WDM drivers

binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
4733 months ago
dumpulator preview

dumpulator

GitHubmrexodia/dumpulator

An easy-to-use library for emulating memory dumps. Useful for malware analysis (config extraction, unpacking) and dynamic analysis in general…

binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
8852 years ago
WFH preview

WFH

GitHubconscioushacker/wfh

Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…

binary-analysisdynamic-analysis-sandboxingexploitation+1
4374 years ago
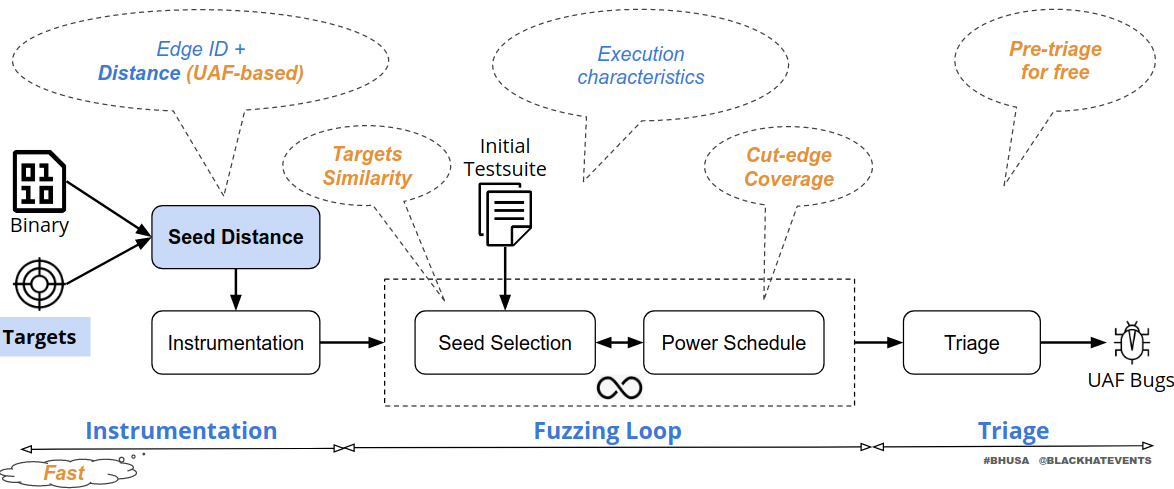
uafuzz preview

uafuzz

GitHubstrongcourage/uafuzz

Binary-level directed fuzzer specialized in detecting Use-After-Free vulnerabilities via ordering-aware input metrics and static analysis, enabling…

binary-analysisexploitationfuzzing+2
3534 years ago
ConcoLLMic preview

ConcoLLMic

GitHubconcollmic/concollmic

LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…

ai-securitybinary-analysiscode-analysis+8
16123 days ago
malduck preview

malduck

GitHubcert-polska/malduck

🦆 Malduck is your ducky companion in malware analysis journeys

binary-analysiscryptographydynamic-analysis-sandboxing+3
3581 year ago
Melkor_ELF_Fuzzer preview

Melkor_ELF_Fuzzer

GitHubioactive/melkor_elf_fuzzer

Melkor is a very intuitive and easy-to-use ELF file format fuzzer to find functional and security bugs in ELF parsers.

binary-analysisfuzzingvulnerability-analysis
1552 years ago
gobee preview

gobee

GitHubboratanrikulu/gobee

Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.

binary-analysiscode-analysisdevsecops+3
3485 months ago
firmware-workshop preview

firmware-workshop

GitHubonekey-sec/firmware-workshop

In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…

binary-analysisdynamic-analysis-sandboxingeducation+5
673 months ago
Previous12…35Next